
fritzos8-mcp



English · Deutsch
Let your AI assistant run your FRITZ!Box – safely. An MCP server for AVM FRITZ!Box routers on FRITZ!OS 8: diagnose slow internet, audit security, clean up the device list, manage guest Wi-Fi, telephony and smart home – read-only by default, and every change is verified.
What you can ask
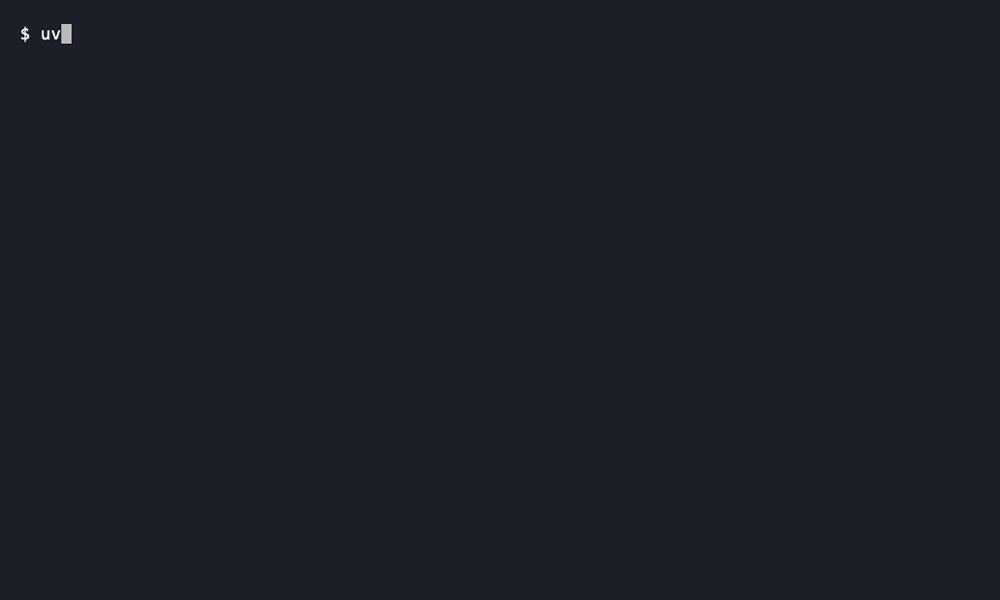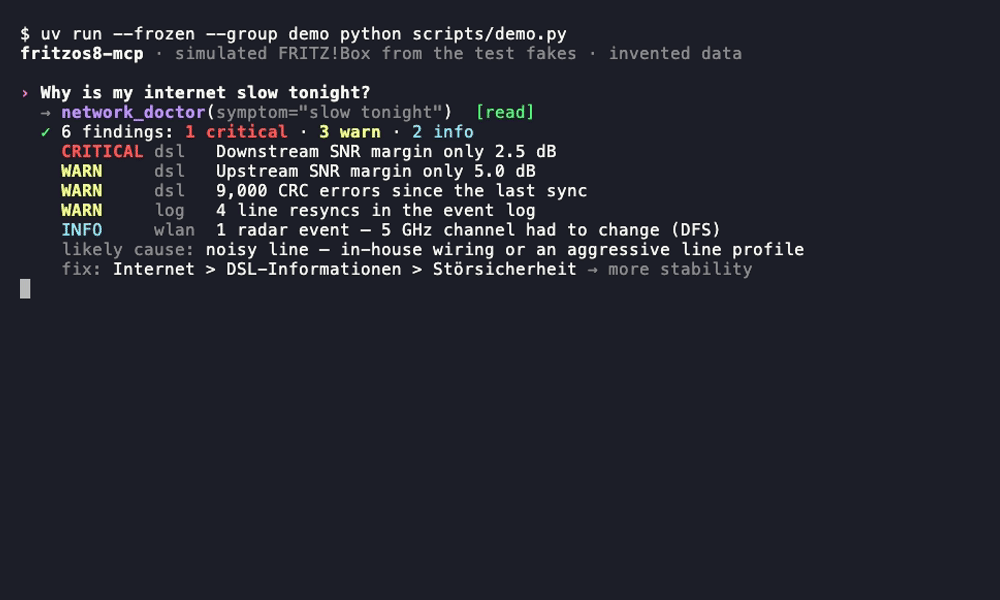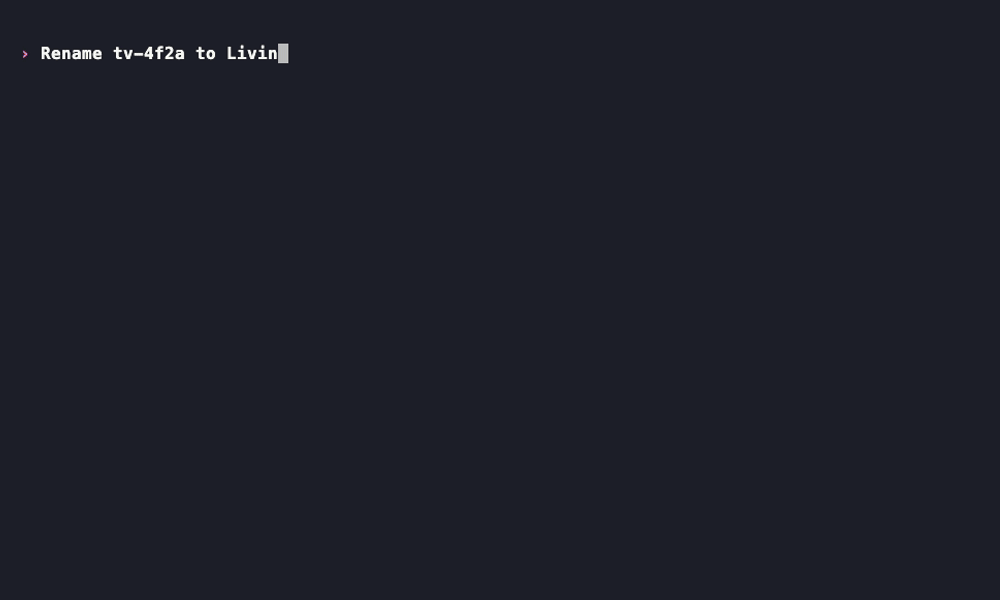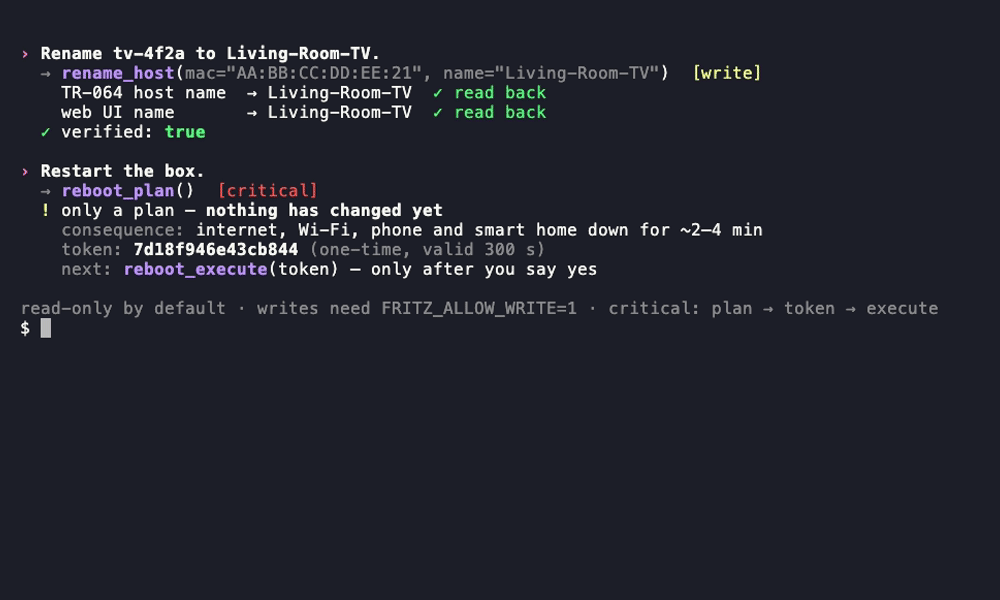
"Why is my internet slow tonight?" Runs the network doctor: line values (SNR margin, errors, resyncs), event log, Wi-Fi and mesh, LAN link flapping, DNS as a single point of failure – and returns findings with severity, likely cause and what to do.
"How secure is my FRITZ!Box?" Security check with a 0–100 score: remote access, MyFRITZ!, port forwards, WPS, Wi-Fi encryption, guest isolation, firmware, DNS over TLS – each finding with the exact menu path to fix it.
"Clean up devices that haven't been online for three months." Finds candidates (long offline, random MACs, duplicates, orphaned static IPs), suggests better names via vendor lookup, shows you the plan and changes nothing until you confirm.
"Turn on guest Wi-Fi for two hours." · "Boost the living room heating for 30 minutes." · "Block this spam number." Write actions – each one is read back from the box and reported as
verified: trueorfalse.
Features
- Diagnostics – network doctor, line diagnostics for DSL, cable, fibre and LTE, per-device connection quality, link-flapping detection, system transparency (TR-069, NTP, IPv6/DS-Lite)
- Security – scored security check, two-factor status, firmware and update overview for all AVM devices
- Devices – both device names (TR-064 and web UI), rename, static IP, clean-up assistant, snapshots with diff, Wake-on-LAN, mesh and LAN ports
- Wi-Fi & family – Wi-Fi channels and settings, guest Wi-Fi with time limit, access profiles, tickets, internet block per device
- Telephony – call list with reverse lookup, answering machines, phone books, call deflection and barring, alarm clocks
- Smart home – thermostats, switches, blinds, energy report, routines, holiday periods (REST API, AHA fallback)
- Monitoring – optional collector for a local measurement series, ISP fault reports, anomaly detection, alerts via webhook, ntfy or Telegram
- Multi-box – manage several boxes from one server, with a family-admin report across all of them
About 160 tools in total – see the generated tool reference.
Quick start
1. Prepare the box. Enable Home Network › Network › Network Settings › Allow access for applications and create a dedicated user under System › FRITZ!Box Users.
2. Store the password in your OS keychain (or use FRITZ_PASSWORD_FILE with mode 600):
uvx --from 'fritzos8-mcp[keyring]' keyring set fritzos8-mcp <user>
3. Add the server to your client – Claude Code shown. Other clients and Windows/Linux: docs/clients.md. Claude Desktop: install the one-click bundle fritzos8-mcp-<version>.mcpb from the latest release instead – it asks for host, user and password and needs neither step 2 nor a terminal.
claude mcp add fritzos8 -s user -e FRITZ_HOST=fritz.box -e FRITZ_USER=<user> -- \
  uvx --from 'fritzos8-mcp[keyring]' fritzos8-mcp
4. Ask your assistant to run setup_check. It verifies TR-064, the user's rights and two-factor settings, and tells you which tools a missing right would disable.
The server starts read-only. Enable changes with FRITZ_ALLOW_WRITE=1, critical actions additionally with FRITZ_ALLOW_CRITICAL=1.
Safety model
| Tier | Enabled by | What it allows |
|---|---|---|
read |
always | read-only tools |
write |
FRITZ_ALLOW_WRITE=1 |
changes – each one is read back and reports verified |
critical |
+ FRITZ_ALLOW_CRITICAL=1 |
reboot, port forwards, firmware update, … only via plan → one-time token → execute, plus a yes/no prompt in clients that support it |
- Never claims success it didn't see. If the result can't be read back, you get
verified: false. - Never bypasses two-factor confirmation. If the box asks for it, the tool reports
confirmation_requiredand explains how to confirm. - Never shows secrets. Passwords, Wi-Fi keys, PINs, session IDs and VPN keys are redacted from every output, error and log line.
- Protects the box. Throttling, caching and a circuit breaker per box;
server_statusshows the health of each interface (last success/error, re-logins) even when the client still shows the server as connected.
Details: SECURITY.md.
Works with
- Boxes: FRITZ!OS 8 – tested on FRITZ!Box 7583 (DSL) and 6660 Cable. Reports for other models are welcome: compatibility.
- Clients: any MCP client – Claude Code, Claude Desktop, Cursor, VS Code, …
- Interfaces: TR-064 (via fritzconnection), the AHA and Smart Home REST APIs, and the web UI's
/api/v0– the latter only where TR-064 can't help. - Language: tool descriptions and messages are in German; assistants handle them fine in any conversation language.
Not a Home Assistant replacement. For HA entities use the official AVM FRITZ!Box Tools, FRITZ!SmartHome and Call Monitor integrations. This server is for AI assistants – diagnostics, audits and guarded changes. Alerts can be sent to a Home Assistant webhook.
Documentation
| Configuration | permissions, all environment variables, multiple boxes, client setup |
| Tool reference | every tool with tier, required right and parameters |
| Remote access | Streamable HTTP with bearer token, e.g. on a Raspberry Pi |
| Interface coverage | what is covered against the official AVM documentation |
| Compatibility · Fixtures | tested models, contributing anonymized box answers |
Contributing
Bug reports, compatibility reports and pull requests are welcome – see CONTRIBUTING.md. make setup installs everything including the git hooks; tests run against mocks only, no box required.
License
MIT. Parts are adapted from MIT-licensed projects, see NOTICE.
Independent project, not affiliated with AVM / FRITZ! GmbH. FRITZ!Box and FRITZ!OS are trademarks of FRITZ! GmbH. The /api/v0 endpoints are undocumented and may change with firmware updates; affected tools then report unsupported_firmware.
1 maintainer

Metadata
1 maintainer
Release files for fritzos8-mcp 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| fritzos8_mcp-0.2.0.tar.gz | 277.3 kB | With provenance | Details for fritzos8_mcp-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| fritzos8_mcp-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for fritzos8_mcp-0.2.0-py3-none-any.whl |
Total release size: 592.4 kB
Release files / fritzos8_mcp-0.2.0.tar.gz
| Download URL | fritzos8_mcp-0.2.0.tar.gz |
|---|---|
| Size | 277.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
018ffa33508cc50100123c85f7eaaf63b90ed08daf5b6e857f937200f7d47673
|
|
BLAKE2b-256 checksum How to use checksums |
fcbaf4e2ae6ded9e0d7401ba6e94c0a6f5f145d02b4a90ca333ff5581415eb8e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logRelease files / fritzos8_mcp-0.2.0-py3-none-any.whl
| Download URL | fritzos8_mcp-0.2.0-py3-none-any.whl |
|---|---|
| Size | 315.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
34e15ff708c73f2dd60a2ecc7e067666e771a83723f4a69b4f89dbf5043fae38
|
|
BLAKE2b-256 checksum How to use checksums |
b258937609702730769782f8c83f0e82648e59b754ed60bf102b2fbc8b7b73ce
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logSecurity for fritzos8-mcp 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for fritzos8_mcp-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














