
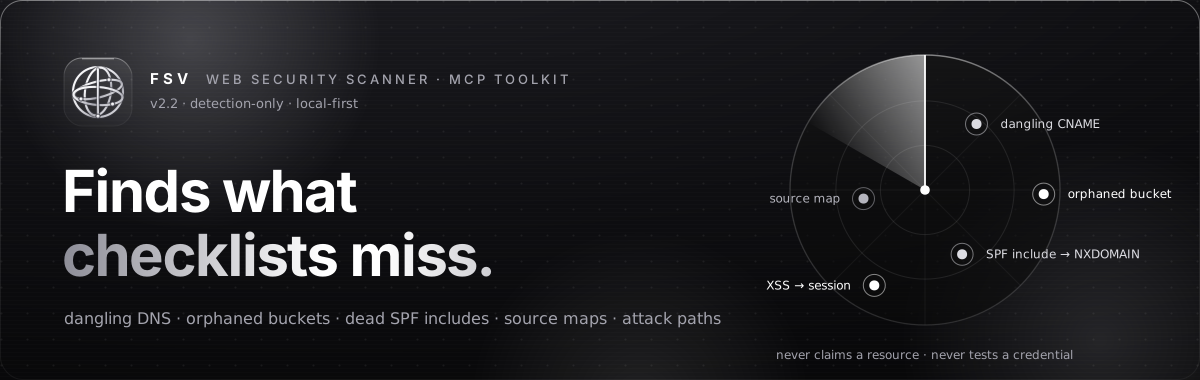
FSV — web security scanner & MCP server
For the problems nobody is watching: dangling DNS and subdomain takeover, orphaned cloud buckets, scripts from compromised or expired CDN domains, SPF includes that no longer exist, debug mode left on in production, secrets in your JavaScript, end-of-life software — and the attack paths that turn small findings into a real compromise, each with the cheapest fix that breaks it.
Runs as a CLI, a dashboard, an MCP server for AI assistants (Claude, Cursor, VS Code), and a CI step. Detection only: it never exploits, never claims a resource, never tests a credential.
Authorized use only. Scan only systems you own or are explicitly authorized in writing to test.
Install
pip install fsv            # Python 3.11+
fsv doctor                 # checks dependencies, DNS, database
Scan
fsv scan example.com --authorize                     # full scan of a site you own
fsv scan example.com --authorize --profile passive   # read-only: no payloads sent
fsv fixes <scan_id> nginx                            # paste-ready config for what was found
fsv web                                              # dashboard → http://127.0.0.1:7474
Connect your AI assistant
fsv mcp-config --client claude-code      # prints:  claude mcp add fsv -- /path/to/fsv-mcp
fsv mcp-config --client claude-desktop   # or: cursor · vscode
Then ask: “Use the security_review prompt on https://my-site.example — I own it.” The assistant confirms authorization, runs a passive check and a full scan, leads with attack paths and hands you the fixes.
What it finds
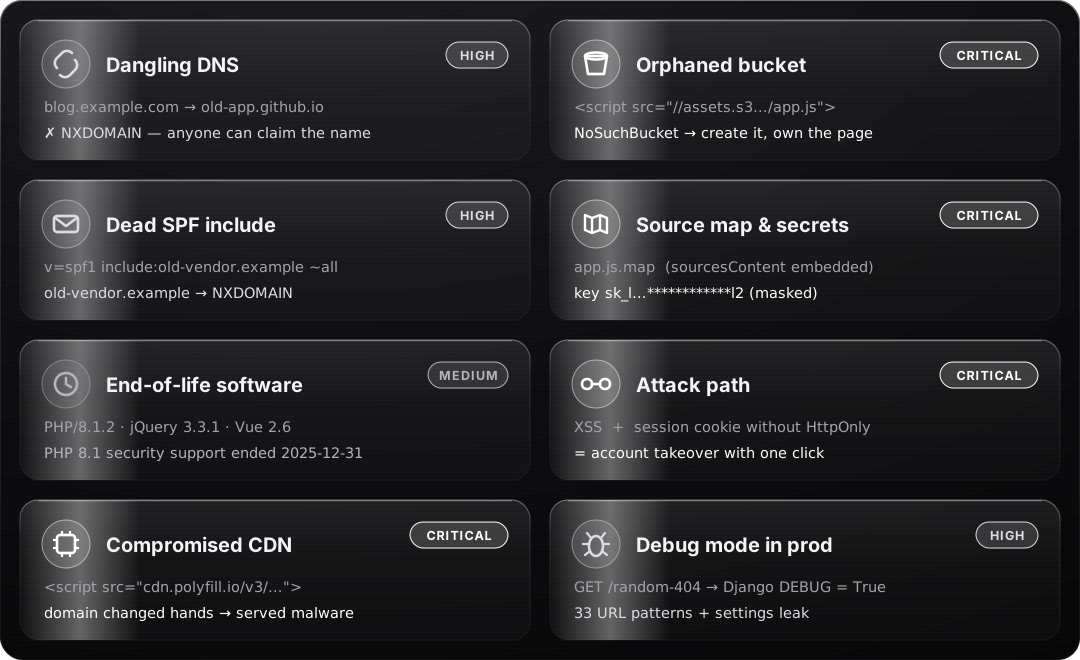
38 modules — DNS takeover, cloud storage, script supply chain, SPF/DMARC/DKIM, TLS (certificate trust, key strength, legacy protocols),
JavaScript secrets and source maps, DOM-XSS static analysis, OIDC/JWKS/OpenAPI exposure, vulnerable and end-of-life libraries,
~100 content-validated exposure checks (~190 with --profile deep), framework debug pages, headers/CSP/cookies, and benign
context-aware active checks for common reflected issues. Findings carry severity,
confidence, CWE, OWASP Top 10 category and remediation; reports in Markdown, JSON, HTML, SARIF and CSV.
Links
- Source, full documentation and screenshots: https://github.com/twayst0/fsv
- Changelog: https://github.com/twayst0/fsv/blob/main/CHANGELOG.md
- Security policy: https://github.com/twayst0/fsv/blob/main/SECURITY.md
- Contact: statways1707@gmail.com · Discord .tways
License: MIT — free for everyone, including commercial use.
1 maintainer

Metadata
1 maintainer
Release files for fsv 2.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| fsv-2.3.0.tar.gz | 278.4 kB | With provenance | Details for fsv-2.3.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| fsv-2.3.0-py3-none-any.whl | Python 3 | none | any | Details for fsv-2.3.0-py3-none-any.whl |
Total release size: 530.6 kB
Release files / fsv-2.3.0.tar.gz
| Download URL | fsv-2.3.0.tar.gz |
|---|---|
| Size | 278.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2e1f5d9fdd1bcd90b7c7b40a7a8eb75d68c7709896a69c97883045e165078aee
|
|
BLAKE2b-256 checksum How to use checksums |
6ce4b620ff52d2265cbfcf772cdf996ee170bac39b5637f4718e1ddaef309956
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logRelease files / fsv-2.3.0-py3-none-any.whl
| Download URL | fsv-2.3.0-py3-none-any.whl |
|---|---|
| Size | 252.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
70560efa9ff427b7a045d84f0965085ddbc53f481c96f3f66836b115aeb4c587
|
|
BLAKE2b-256 checksum How to use checksums |
30dbb42c7ccdaec9b29838f05020d68fe5daa599fabb95e8c2e1ac1899d63cad
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logSecurity for fsv 2.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for fsv-2.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














