
geometry-validated-layout
Deterministic geometry validation for coordinate-based spatial layouts.
This project is an early extraction from a private kitchen-planning workflow. The core idea is simple: define a room, objects, parent-child relationships, clearances, operation envelopes, and module runs as structured data; validate the geometry; render only after validation passes.
It is not a construction-approval tool. It is a small geometry back end for auditable layout proposals and agent-generated designs.
Developer preview: version 0.1.0 is pre-1.0. The data model and Python API may change incompatibly while downstream use cases establish the right public abstractions.
Why This Exists
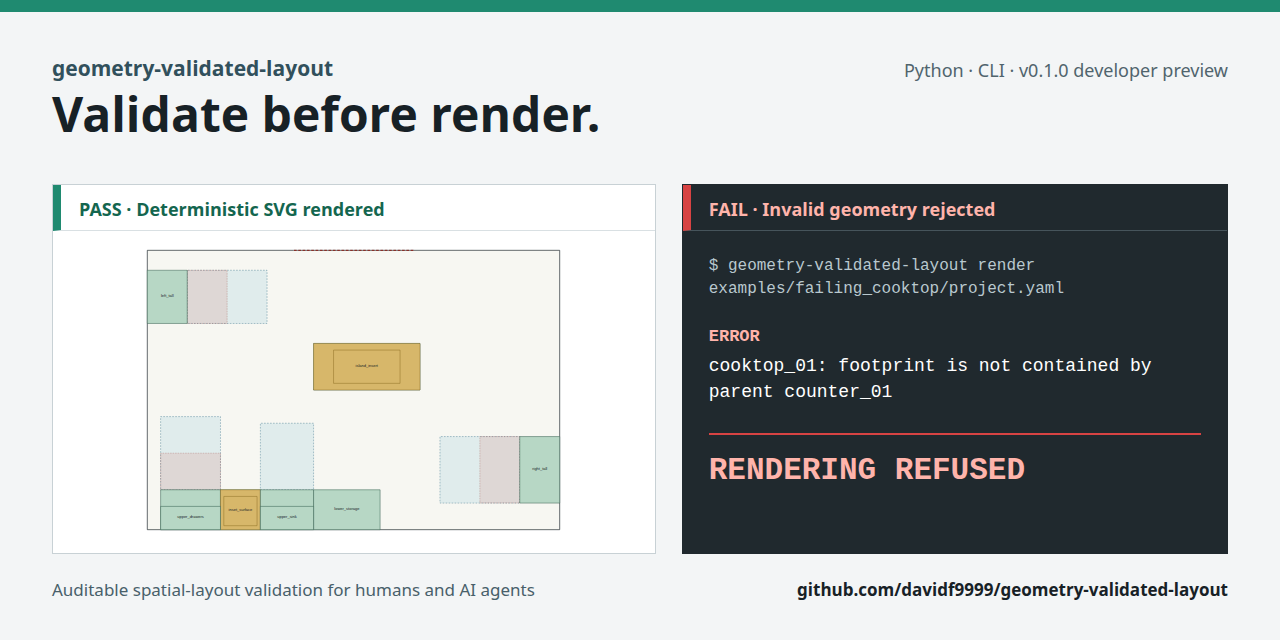
This is not a visual planner, CAD package, or construction approval system. It is a validation-first geometry backend for layout proposals made by humans or coding agents. The intended workflow is to reject invalid geometry before a plausible drawing can make it look acceptable.
A private downstream project provided an early practical test: an operation envelope intersected an upper cabinet in plan, but the two occupied different vertical intervals. The initial generic validator incorrectly reported a blockage. The downstream adapter exposed the defect, and the core now makes operation-blocker checks height-aware. This feedback loop is why the package is kept separate from domain policy while still being exercised by a real project.
Failure Is a First-Class Output
The validator does not produce a design drawing after a hard failure:
$ geometry-validated-layout render examples/failing_cooktop/project.yaml \
    --output /tmp/failing.svg
Errors:
- cooktop_01: footprint is not contained by parent counter_01
Rendering refused because validation failed.
This refusal is part of the public contract: rendering and validation use the same structured coordinates, so a plausible image cannot hide rejected geometry.
Install
pip install geometry-validated-layout
Run the Included Examples
git clone https://github.com/davidf9999/geometry-validated-layout.git
cd geometry-validated-layout
python3 -m venv .venv
. .venv/bin/activate
pip install -e ".[dev]"

geometry-validated-layout validate examples/irregular_kitchen/project.yaml
geometry-validated-layout render examples/irregular_kitchen/project.yaml --output /tmp/irregular_kitchen.svg
pytest
Try the deliberate failure:
geometry-validated-layout render examples/failing_cooktop/project.yaml \
  --output /tmp/failing.svg
Expected result: validation identifies the containment error and rendering is refused.
Generate the demo SVG:
geometry-validated-layout render examples/irregular_kitchen/project.yaml --output docs/demo/irregular_kitchen.svg
Open docs/demo/irregular_kitchen.svg to inspect the shell, closed footprints,
keep-clear boundary, and operation envelopes.
For a more complete downstream example, see
examples/complete_kitchen/README.md. It includes a substantial synthetic
project, checked-in machine validation report, and deterministic SVG drawing.
Integrating With an Application
Use the CLI when integrating from another language or when a stable process
boundary is preferable. Python applications can construct LayoutProject
directly. Existing CAD, configurator, or domain applications should normally
keep their own data model and add a small adapter into the generic schema.
existing app/domain model -> adapter -> LayoutProject -> validate_project()
                                                     -> report
                                                     -> render only after pass
See the integration guide for pinned installation, CLI exit/report behavior, Python, adapter, HTTP-service, and coding-agent examples.
Scope
The generic core understands:
- shell polygons and wall/open-boundary segments
- wall-anchored rectangles and explicit polygons
- parent-child containment
- vertical interval overlap
- object overlap
- keep-clear boundary segments
- operational use/opening envelopes
- clearance checks
- exact module-run sums
- machine-readable and human-readable validation reports
- deterministic SVG rendering from the same coordinates
Kitchen-specific rules such as refrigerators, sinks, appliance counts, metrage,
and supplier workbooks belong in a separate domain package or private project.
See docs/ARCHITECTURE.md for the dependency boundary and the criteria for
splitting out a reusable domain package.
Compatibility
Python 3.10 through 3.14 are exercised in CI. The CLI is the recommended initial integration surface. Direct Python imports are available but do not have stable pre-1.0 compatibility guarantees yet.
Agent Guidance
Reusable agent workflow rules live in
.agents/skills/geometry-validated-layout/SKILL.md. They intentionally describe
the domain-neutral validation contract rather than kitchen-specific planning
rules. Current capabilities, limitations, and deferred work are recorded in
STATUS.md so development can continue without external chat context.
Data Shape
See examples/irregular_kitchen/project.yaml for a synthetic example. The
example is intentionally fictional and does not contain private room geometry,
addresses, Drive links, or supplier data.
Tagline
Validate before render.
1 maintainer

Metadata
1 maintainer
Release files for geometry-validated-layout 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| geometry_validated_layout-0.1.1.tar.gz | 111.5 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| geometry_validated_layout-0.1.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 125.6 kB
Release files / geometry_validated_layout-0.1.1.tar.gz
| Download URL | geometry_validated_layout-0.1.1.tar.gz |
|---|---|
| Size | 111.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f1cc1652f67459b881551e9d90d559db5b4d397e55acabdaf210094a58e0c475
|
|
BLAKE2b-256 checksum How to use checksums |
596a2baa31f618a989cbb12683584d82c4b03e9b5244021016dcf57806078526
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logRelease files / geometry_validated_layout-0.1.1-py3-none-any.whl
| Download URL | geometry_validated_layout-0.1.1-py3-none-any.whl |
|---|---|
| Size | 14.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
0512aacc2ea7822ca1219ebca9db0cabbce3b24ebbf6b055532fb09c743ff31f
|
|
BLAKE2b-256 checksum How to use checksums |
a84b6cc0742d5e941e0e1ab35530ce6ae280eaba22ad9293b921ed839b3e52f3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logSecurity for geometry-validated-layout 0.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for geometry_validated_layout-0.1.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













