


✨ Giphon is the contraction of 🦊 Gitlab and 🫗 siphon. This CLI tools allows users to recursively clone all projects in a given Gitlab group or instance.
Motivation
This project aims to provide a tool capable of replicating a Gitlab group's structure into a directory structure.
Locally cloned projects enable users to use familiar CLI tools such as grep
and sed directly into the projects' tree structure.
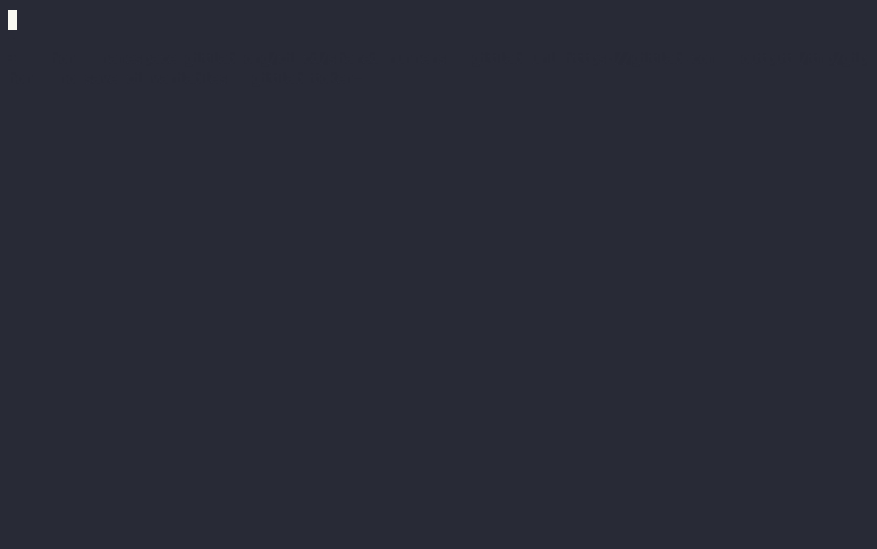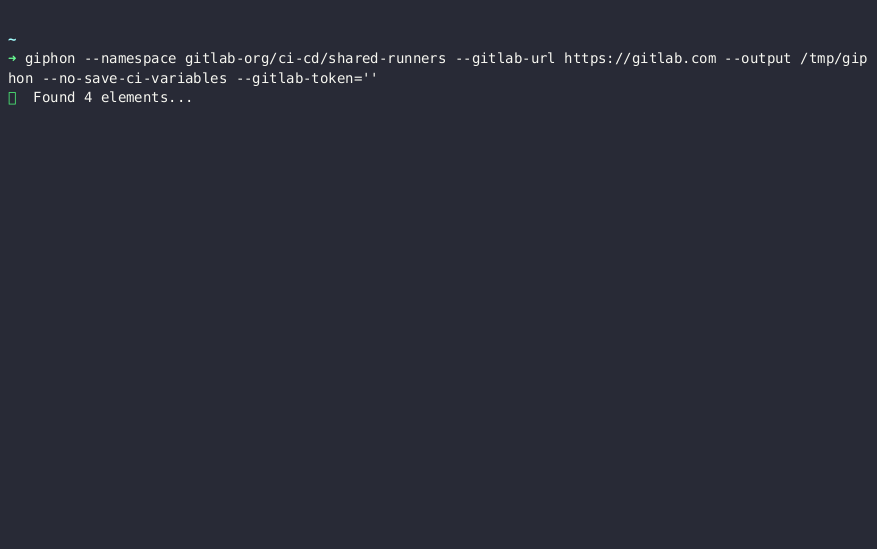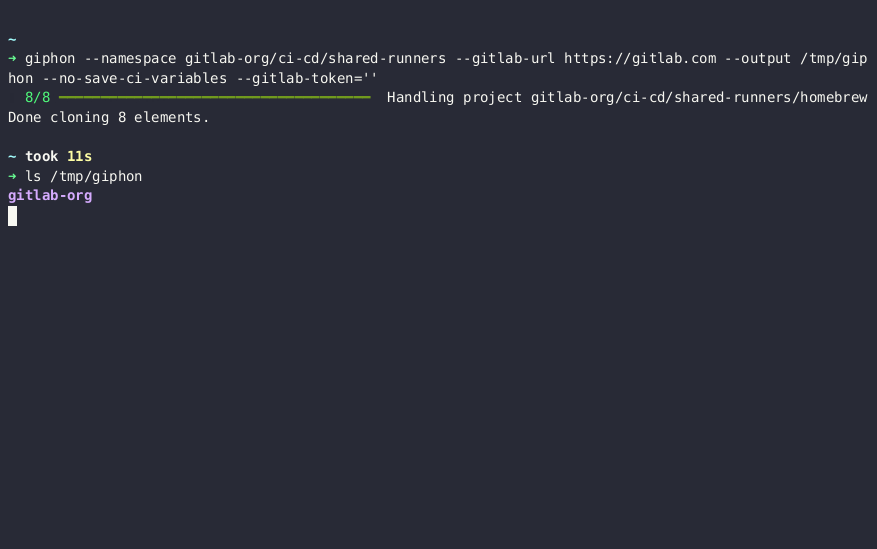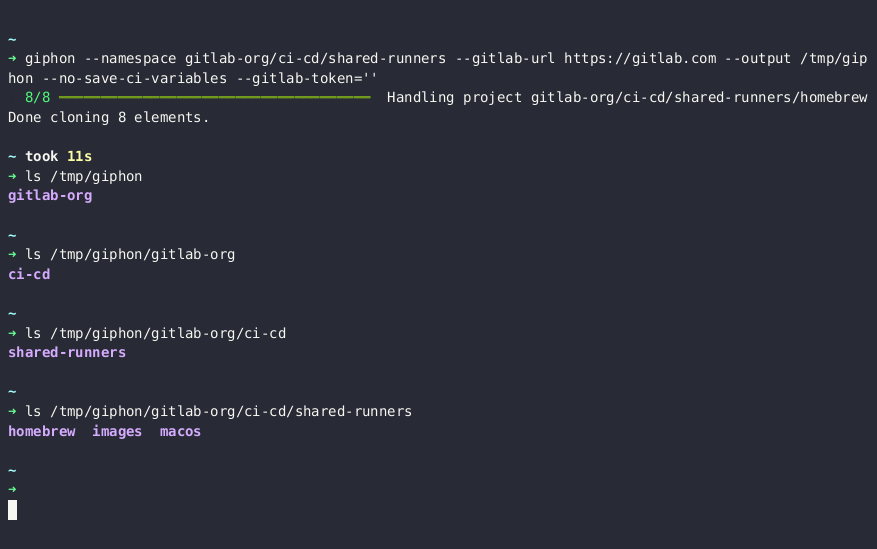
Demo
Installation
To install giphon, simply run:
pip install --user giphon
And if you wish to use giphon by simply calling giphon, you can set-up an
alias in your .bashrc (or other, if you have another shell):
echo 'alias giphon="/usr/bin/env python3 -m giphon"' >> ~/.bashrc
Parameters
The giphon tool allows for the following parameters:
- namespace (CLI:
--namespace): The Gitlab namespace to be cloned./defaults to the whole instance. - output (CLI:
--output): The target path to clone the repositories to. - gitlab_token: (CLI:
--gitlab-token, env:GITLAB_TOKEN): The Personal Access Token authenticating the user. - gitlab_url: (CLI:
--gitlab-url, env:GITLAB_URL): The URL of the Gitlab instance to clone the repositories from. Defaults to"https://gitlab.com" - fetch_repositories: (CLI:
--fetch-repositories/--no-fetch-repositories): Whether to fetch remotes on repositories that already exist. - save_ci_variables: (CLI:
--save-ci-variables/--no-save-ci-variables): Whether to download CI/CD variables to a .env directory. - clone_archived (CLI:
--clone-archived/--no-clone-archived): Whether to also clone archived repository. - clone_through_ssh: (CLI:
--clone-through-ssh/--no-clone-through-ssh): Whether to use the SSH protocol or the HTTPS protocol to clone the git repositories - gitlab_username (CLI:
--gitlab-username, env:GITLAB_USERNAME): The username to use, when cloning through HTTPS. - verbose: (CLI:
--verbose/-v): The level of verbosity
Running programmatically
You can import the main function from giphon as such:
from pathlib import Path

from giphon.siphon import siphon

siphon(
    namespace=Path("my-namespace"),
    output=Path("~/Projects"),
    gitlab_token="",
    gitlab_url="https://gitlab.com",
    fetch_repositories=True,
    save_ci_variables=False,
    clone_archived=False,
    verbose=False,
)
The function takes as inputs the same parameters from the CLI tool.
Logo is © from Midjourney
1 maintainer

Metadata
1 maintainer
Release files for giphon 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| giphon-0.2.0.tar.gz | 16.5 kB | Without provenance | Details for giphon-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| giphon-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for giphon-0.2.0-py3-none-any.whl |
Total release size: 29.9 kB
Release files / giphon-0.2.0.tar.gz
| Download URL | giphon-0.2.0.tar.gz |
|---|---|
| Size | 16.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
31ece60f89734d5aef0e557d707d65030d08e56dedc705196a01e91cb095424b
|
|
BLAKE2b-256 checksum How to use checksums |
2b7fc1bf5ce5beafdb254330f7b8802feb2606dfd84542125bc6068322fd874d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
python-httpx/0.27.0
|
Release files / giphon-0.2.0-py3-none-any.whl
| Download URL | giphon-0.2.0-py3-none-any.whl |
|---|---|
| Size | 13.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f968ed4ada2c883ad9ac007c83dab6b66c96aae85ed90bc2881d0db8e5568a73
|
|
BLAKE2b-256 checksum How to use checksums |
99a08f766a3c8181a07db31ba82a7f4d93c2681538f06d56cbaad430be4b1adc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
python-httpx/0.27.0
|
Security for giphon 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














