
GIPPA
GIPPA (genome integrated prokaryotic proteomics analysis) takes one assembled bacterial genome plus proteomics evidence and asks: what does genome context explain about which proteins are detected, and how abundant they are? It places peptides and proteins on the genome with its own error control, builds one gene table keyed by Bakta locus tags, tests genome context (regions, autocorrelation, abundance islands, operons, function, sequence determinants), calls REF/ALT residues and novel ORFs, and writes standard tables, plots and an HTML report.

Documentation: khoa-yelo.github.io/gippa (from the first
release; until then the same pages are under docs/). Changes between releases
are listed in CHANGELOG.md. The
process-level diagram shows every Nextflow process with its inputs
and outputs.
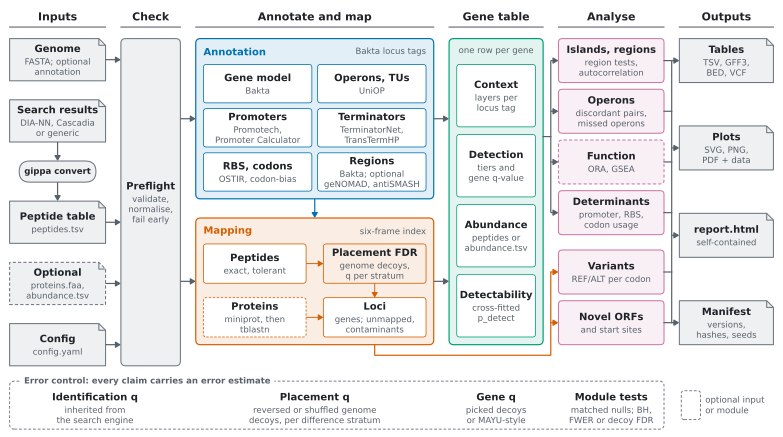
GIPPA at a glance: from one genome and a peptide table to a gene table, genome-context tests and an HTML report, each claim with its own error control.
Status
1.0.0 is the first release. The full pipeline is tested on Linux x86-64 with Slurm and
Apptainer, on the synthetic demo below and on
the E. coli Nissle 1917 pilot (PXD078459; validation/pilot/README.md).
Pending:
- the hosted docs and Bioconda;
- the final pilot report.
Genetic codes 11 (default), 4 (Mycoplasma and Spiroplasma) and 25 (SR1 and Gracilibacteria) are
supported through annotation.translation_table
(Inputs › Genetic code).
gippa preflight, convert, compare and report need only the Python package. gippa run
also needs Nextflow, Java 17 or newer, Docker or Apptainer, the tool images and the databases
(Install, Platforms).
Install
With pip (Bioconda is pending):
pip install gippa                                     # Python package and the `gippa` command
micromamba install -c conda-forge -c bioconda gippa   # from Bioconda, once the recipe is merged
From a checkout (Python >= 3.11):
git clone https://github.com/khoa-yelo/gippa.git && cd gippa
python3 -m venv .venv && . .venv/bin/activate && pip install .
gippa run also needs Nextflow (with Java 17+) and Docker or Apptainer; see
Install for the prerequisites, the execution profiles and running
on a Slurm cluster.
Quickstart
pip install gippa                         # or: conda install -c bioconda gippa
gippa demo                                # about 2 minutes; prints the report path
gippa setup                               # databases and images for the detected runtime
gippa run --genome g.fna --peptides p.tsv --outdir out
gippa demo runs a small bundled synthetic genome with no Nextflow, containers, databases or
network. gippa setup and gippa run detect the Nextflow profile (pass --profile to choose).
The guided walk-through, with example inputs and outputs, is
Quick start
(source). With raw spectra and no peptide table yet, see
From raw spectra to a GIPPA run; for converting search-engine
output, gippa convert.
Citing GIPPA
If you use GIPPA, please cite it as described in CITATION.cff (GitHub's
"Cite this repository" button reads the same file).
Developers
The build specification is GIPPA_SPEC.md; progress is tracked in
PROGRESS.md. Every PR that changes src/ or workflow/ adds a fragment under
changelog.d/ (checked in CI by scripts/ci/check_changelog.py).
From a checkout, with uv:
uv sync --frozen --all-extras
uv run pytest -m "not slow and not calibration_full and not e2e" -n auto
See AGENTS.md for test layers and conventions.
Development on FarmShare
The maintainers' own cluster setup (scripts/farmshare_env.sh) is in the
developer guide; users do not need it.
Licence
MIT. Third-party tools keep their own licences and run only as separate programs; see
NOTICE.md.
geNOMAD (module mobile) is for non-commercial use only (gippa setup --no-genomad,
--modules core,bgc,function); KEGG is free for academic use only (gippa setup --no-kegg); see
Licences.
1 maintainer

Metadata
1 maintainer
Release files for gippa 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| gippa-1.0.0.tar.gz | 1.3 MB | With provenance | Details for gippa-1.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| gippa-1.0.0-py3-none-any.whl | Python 3 | none | any | Details for gippa-1.0.0-py3-none-any.whl |
Total release size: 2.9 MB
Release files / gippa-1.0.0.tar.gz
| Download URL | gippa-1.0.0.tar.gz |
|---|---|
| Size | 1.3 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fff51ebc23e77f0e44b8bf77721a7dbe544061d1fdb15b02130492157e17a85b
|
|
BLAKE2b-256 checksum How to use checksums |
4e9f6b00d153cb98ca11db9d9a397ba0d4d14c323c39c8ce778511dd37ccf71f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logRelease files / gippa-1.0.0-py3-none-any.whl
| Download URL | gippa-1.0.0-py3-none-any.whl |
|---|---|
| Size | 1.6 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
9ffc0099d33a7906b62614a20a4d7896a548d606782f79cb2b8b50649c99c105
|
|
BLAKE2b-256 checksum How to use checksums |
020cb6a5bda61beb64bd49d9e140d4bb95168888ce4fa57176e560b852910314
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logSecurity for gippa 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for gippa-1.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













