
github_monitor




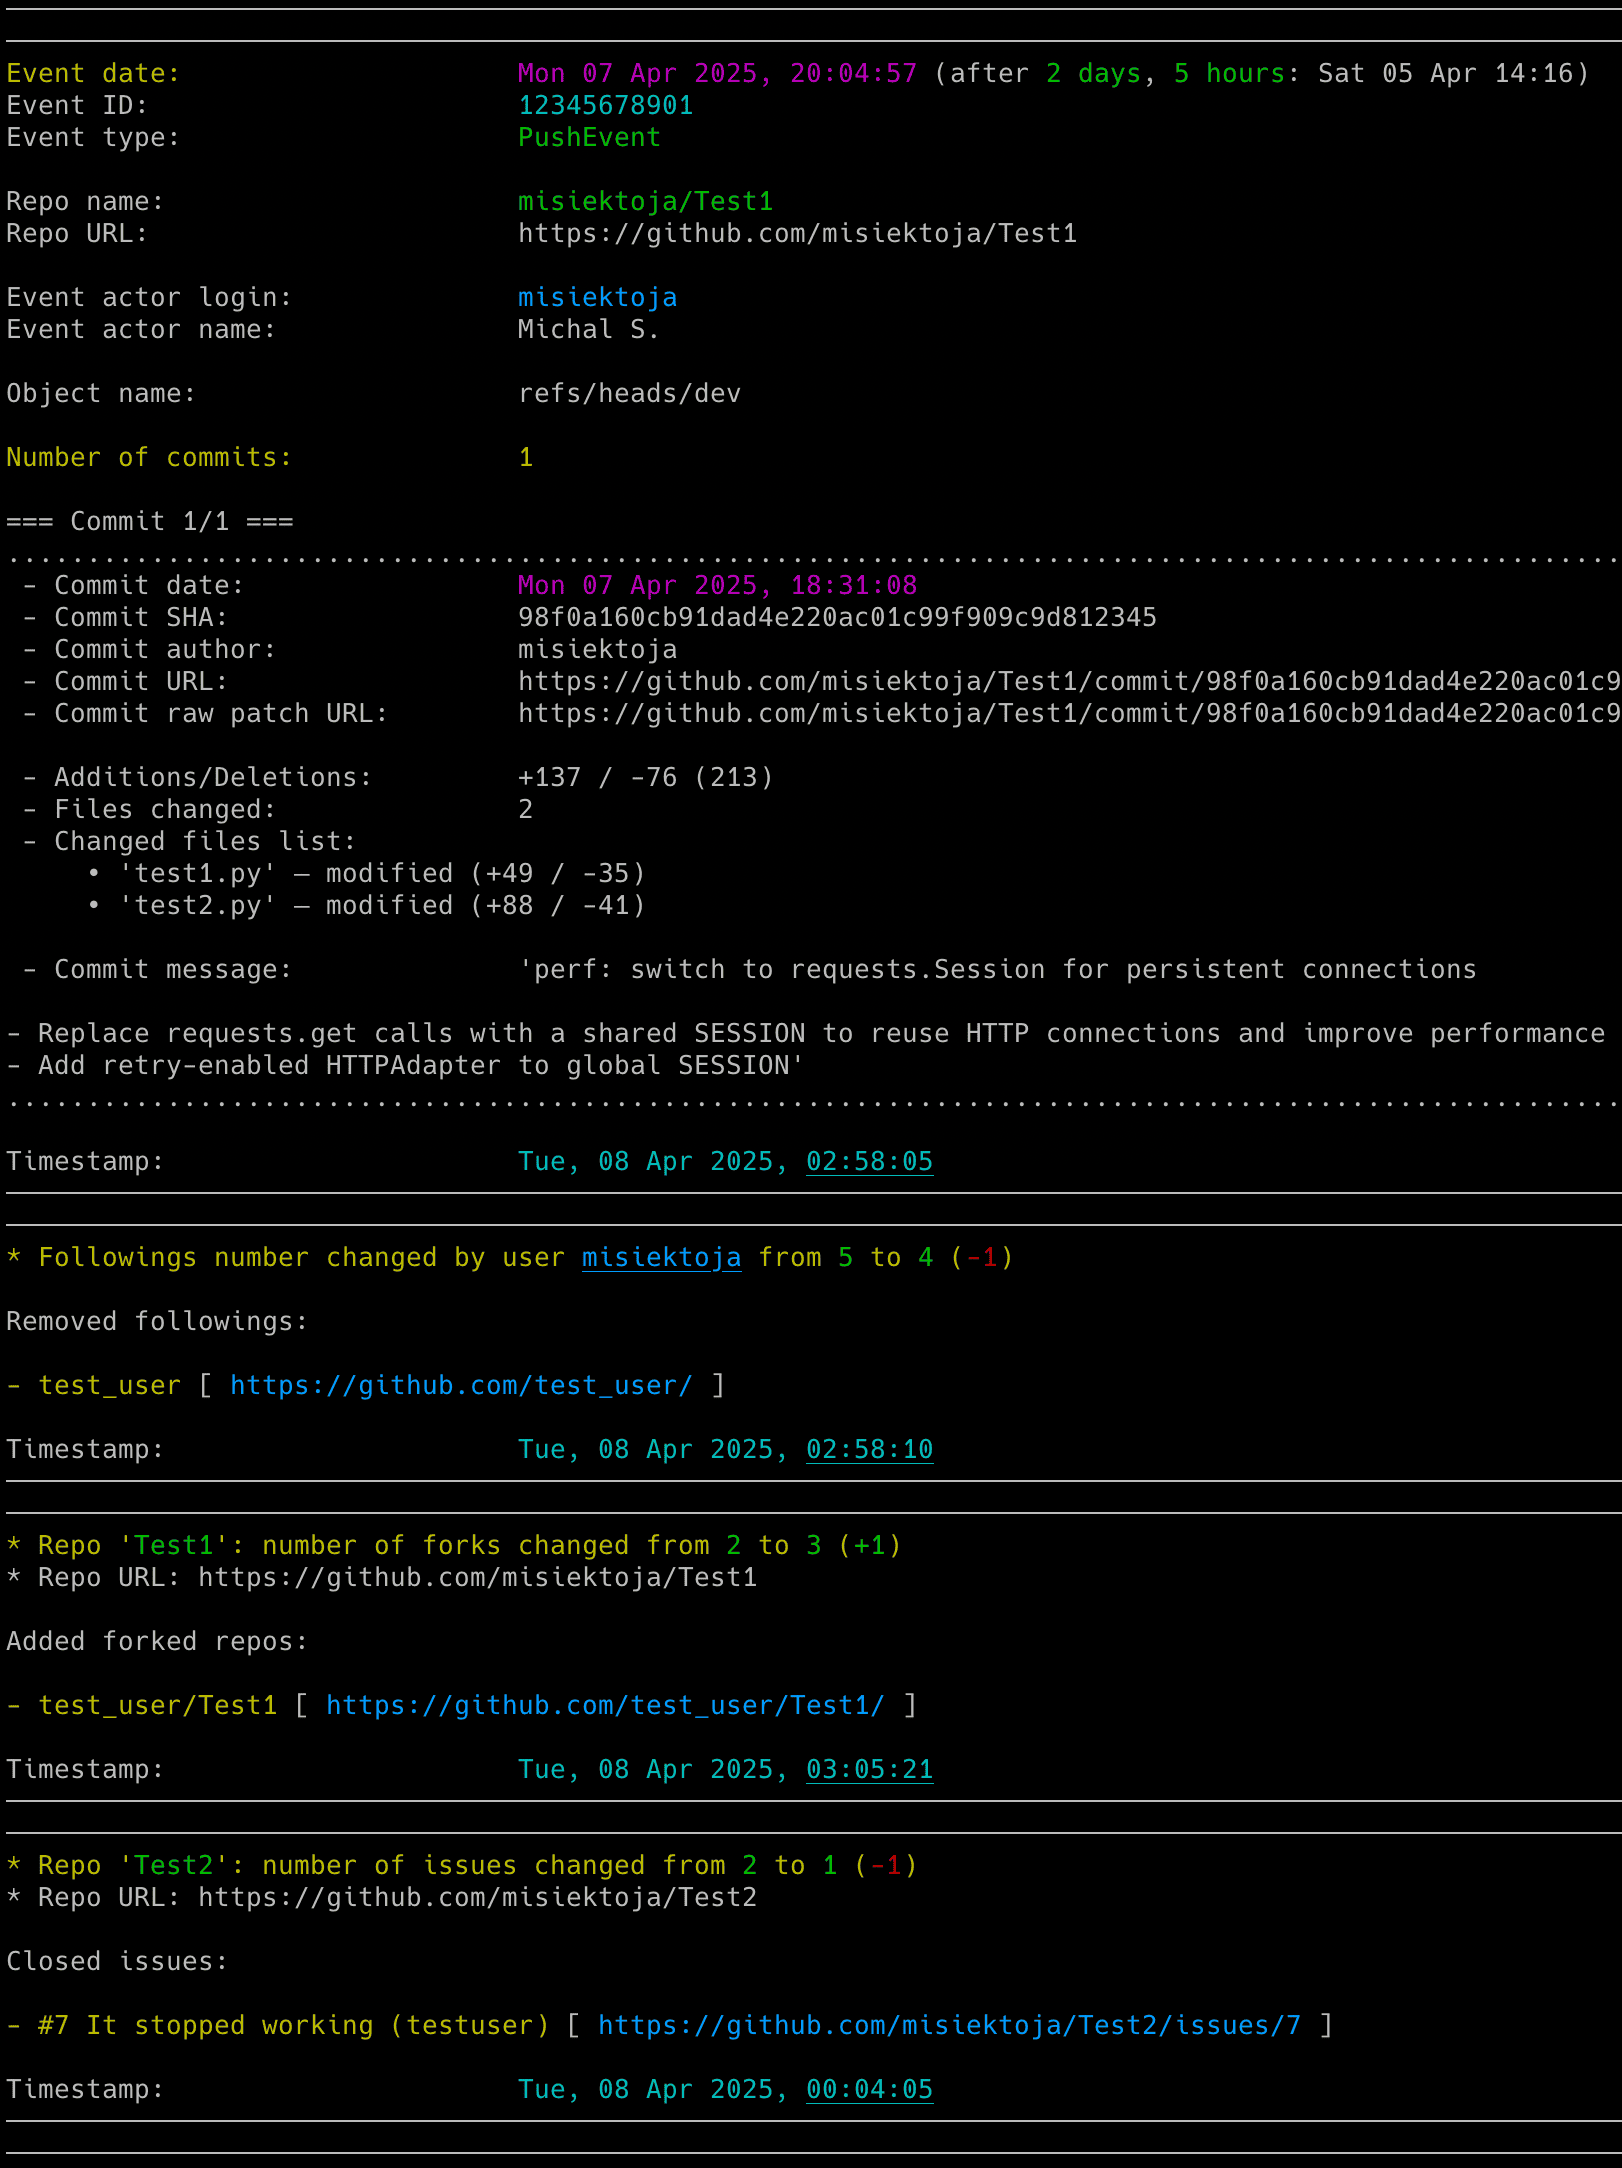
Powerful real-time GitHub OSINT tool that tracks everything from profile updates and contribution streaks to repository engagement and follower changes - even detecting when you've been blocked, all with instant email and webhook notifications.
🚀 Quick Install & Run
New to Python or unsure what is installed? Follow the Python install walkthrough first.
Install from PyPI:
pip install github_monitor
Run the setup wizard:
github_monitor --setup
The wizard asks for the target, the GitHub token and optional notifications. Review the settings before saving them. See Setup & First Run for how to create the GitHub personal access token.
For the manual single-file method, dependencies and upgrade commands, see Installation.
Features
🔍 Activity and Profile Tracking
- GitHub events: Track pushes, pull requests, issues, forks, releases and reviews.
- Profile changes: Detect changes to names, email, location, company, bio, blog URL, visibility and account metadata.
- Connections and contributions: Track followers, followed accounts, daily contributions and blocking or unblocking.
📊 Repository Insights
- Repository lists: Track added or removed public and starred repositories.
- Repository changes: Monitor stars, watchers, forks, issues, pull requests, discussions, descriptions and update dates.
- Removal context: Flag deleted accounts or repositories when reporting removals.
- GitHub links: Open repositories, commits, issues and other activity from console and email links.
🔔 Notifications and History
- Event alerts: Send email, Discord and ntfy notifications with event-specific controls.
- CSV history: Save detected activity and profile changes with timestamps.
- Terminal colours: Customize the theme, with colours disabled when output is redirected.
⚙️ Setup and Configuration
- Guided setup: Configure a target, credentials and alerts with
--setup, then check them with--doctor. - Flexible settings: Use configuration files, dotenv files, environment variables and command-line options.
- Runtime controls: Adjust the running monitor through supported signals.
- GitHub deployments: Connect to public GitHub or GitHub Enterprise.
Common Commands
Use Quick Install & Run above for first-time setup. The table uses PyPI commands. For the manual script equivalents, see Run Individual Commands.
Replace the target placeholders with a GitHub username or complete profile URL. Monitoring requires the GitHub personal access token described in the setup guide.
| I want to... | Run this |
|---|---|
| Configure the target, credentials and alerts | github_monitor --setup |
| Start monitoring with existing authentication | github_monitor <github_target> |
| Check authentication, connectivity and one target | github_monitor --doctor <github_target> |
| Enter or replace securely the GitHub personal access token | github_monitor --set-github-token |
| Configure and test webhook alerts | Use the setup wizard or follow Webhook Settings |
| Save an SMTP password for email alerts | github_monitor --set-smtp-password |
| Send a test email | github_monitor --send-test-email |
| Save a new webhook URL | github_monitor --set-webhook-url |
| Send a test webhook | github_monitor --send-test-webhook |
| List public repositories | github_monitor <github_target> -r |
| List starred repositories | github_monitor <github_target> -g |
| List followers and followings | github_monitor <github_target> -f |
| List the ten most recent events | github_monitor <github_target> -l -n 10 |
| Write every change to a CSV file | github_monitor <github_target> -b changes.csv |
| Use a specific configuration and secrets file | github_monitor --config-file github_monitor.conf --env-file .env <github_target> |
| List every supported command-line flag | github_monitor --help |
Running the tool with no arguments offers the wizard if you have not saved a target. If a target is already saved, it starts monitoring that target.
The tool runs until interrupted (Ctrl+C). Use tmux or screen for persistence and run multiple copies to monitor several targets.
For the personal access token, saved targets and notification setup, see the full Setup & First Run guide.
For the events and repositories to monitor, TLS verification, email and webhook setup, see Configuration. For notification choices, listing commands and output files, see Usage.
If a run fails, start with Doctor Preflight.
Documentation
Full documentation is available at misiektoja.github.io/github_monitor:
| Page | What it covers |
|---|---|
| Installation | Python walkthrough, PyPI or manual installation, upgrades |
| Setup & First Run | Setup wizard, the personal access token, the first monitoring run |
| Configuration | Config file, events and repositories to monitor, SMTP, webhooks, TLS verification, storing secrets, check intervals |
| Usage | Monitoring mode, listing mode, notifications, CSV export, signals, terminal output |
| Troubleshooting | --doctor preflight checks, what to do when something fails, --verbose and --debug output |
| Testing | Running the offline suite, the linter and the docs build |
| About | Change log, contributing, security, license, support |
Change Log
See RELEASE_NOTES.md.
Contributing
Bug reports, documentation fixes and code contributions are welcome. See CONTRIBUTING.md for the development setup, the checks CI enforces and what a change needs before it is merged. Participation is covered by the Code of Conduct.
Security
Report a suspected vulnerability privately through GitHub security advisories, never as a public issue. SECURITY.md covers the reporting process, the supported versions and the security posture of stored credentials and configuration loading.
Maintainers
- misiektoja (@misiektoja)
License
Licensed under GPLv3. See LICENSE. Dependency licenses are listed in THIRD_PARTY_NOTICES.md.
Support
Questions, bug reports and vulnerability reports each have a place, listed in SUPPORT.md.
If the project is useful to you, you can support its development through GitHub Sponsors or Buy Me a Coffee.
1 maintainer

Metadata
1 maintainer
Release files for github-monitor 2.8
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| github_monitor-2.8.tar.gz | 313.9 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| github_monitor-2.8-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 471.0 kB
Release files / github_monitor-2.8.tar.gz
| Download URL | github_monitor-2.8.tar.gz |
|---|---|
| Size | 313.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
39d05d31283230ec4aa3d2ff5b6729bdeee014ca7e09a8fdbf4c0c7e5ac4b1d5
|
|
BLAKE2b-256 checksum How to use checksums |
ea60fa797d19337b43d37be279866c2cd99f93a92006e72a162e42d1b769c5ca
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 22, 2026.
Transparency logRelease files / github_monitor-2.8-py3-none-any.whl
| Download URL | github_monitor-2.8-py3-none-any.whl |
|---|---|
| Size | 157.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
0f9b9888471c232db36ce07a9e89f606305892c577bc8e991f95af40d7fe23eb
|
|
BLAKE2b-256 checksum How to use checksums |
ae7897639a2edfeb23a7a0ee0fc0a8bec4d9213efc38ba26ddc678ee2c46eb45
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 22, 2026.
Transparency log













