
GitPulse
A local Python CLI for GitHub repository traffic and release asset download stats. GitPulse can build a dashboard for a whole organization, and it keeps SQLite snapshots so you have history beyond GitHub's short traffic window.
What GitHub can tell you: aggregate daily views and clones, unique counts, popular paths, referrers, and release-asset download totals. It does not identify individual visitors or people who cloned a repository. GitHub's traffic data is generally available for the most recent 14 days. Release asset downloads are not Homebrew formula install counts.
Requirements
-
Python 3.10+
-
A GitHub token with access to the repositories you want to inspect. Classic tokens need the
reposcope for private repositories. For fine-grained tokens, grant these repository permissions:Permission Needed for Metadata: read All commands (always included) Contents: read downloads, and release downloads inorgAdministration: read traffic,snapshot, and traffic inorgA fine-grained token only covers repositories owned by its resource owner, so org-owned repositories need a token whose resource owner is that org. Without a required permission, GitHub returns
Resource not accessible by personal access token.
Traffic endpoints only work for repositories you have push access to. Public visibility alone does not grant access to traffic analytics.
Install
Homebrew (macOS and Linux):
brew install fullstackspectrum/gitpulse/gitpulse
pipx or pip. The package is called gitpulse-analytics on PyPI; the command it installs is gitpulse:
pipx install gitpulse-analytics
# or
python -m pip install gitpulse-analytics
Docker. Images for linux/amd64 and linux/arm64 are on Docker Hub. Mount a directory at /data to keep the HTML dashboard and snapshot history:
docker run --rm -e GITHUB_TOKEN -v "$PWD:/data" fullstackspectrum/gitpulse org ORG
The container runs as UID 1000. On Linux, if your user can't write the mounted directory as that UID, add --user "$(id -u):$(id -g)".
From source, for development:
python3 -m venv .venv
source .venv/bin/activate
python -m pip install --upgrade pip
python -m pip install -e '.[dev]'
Check the install with gitpulse --version.
Set a token in your shell. GITHUB_TOKEN and GH_TOKEN are both supported. GitPulse never saves the token:
export GITHUB_TOKEN="github_pat_..."
If you use the GitHub CLI and are signed in with gh auth login, you can reuse its token instead:
export GITHUB_TOKEN="$(gh auth token)"
Organization dashboard
gitpulse org ORG                                   # terminal summary + gitpulse-ORG.html
gitpulse org ORG --open                            # also open the dashboard in your browser
gitpulse org ORG --save                            # also save views/clones snapshots for `history`
gitpulse org ORG --all --output reports/org.html   # include forks and archived repos, custom path
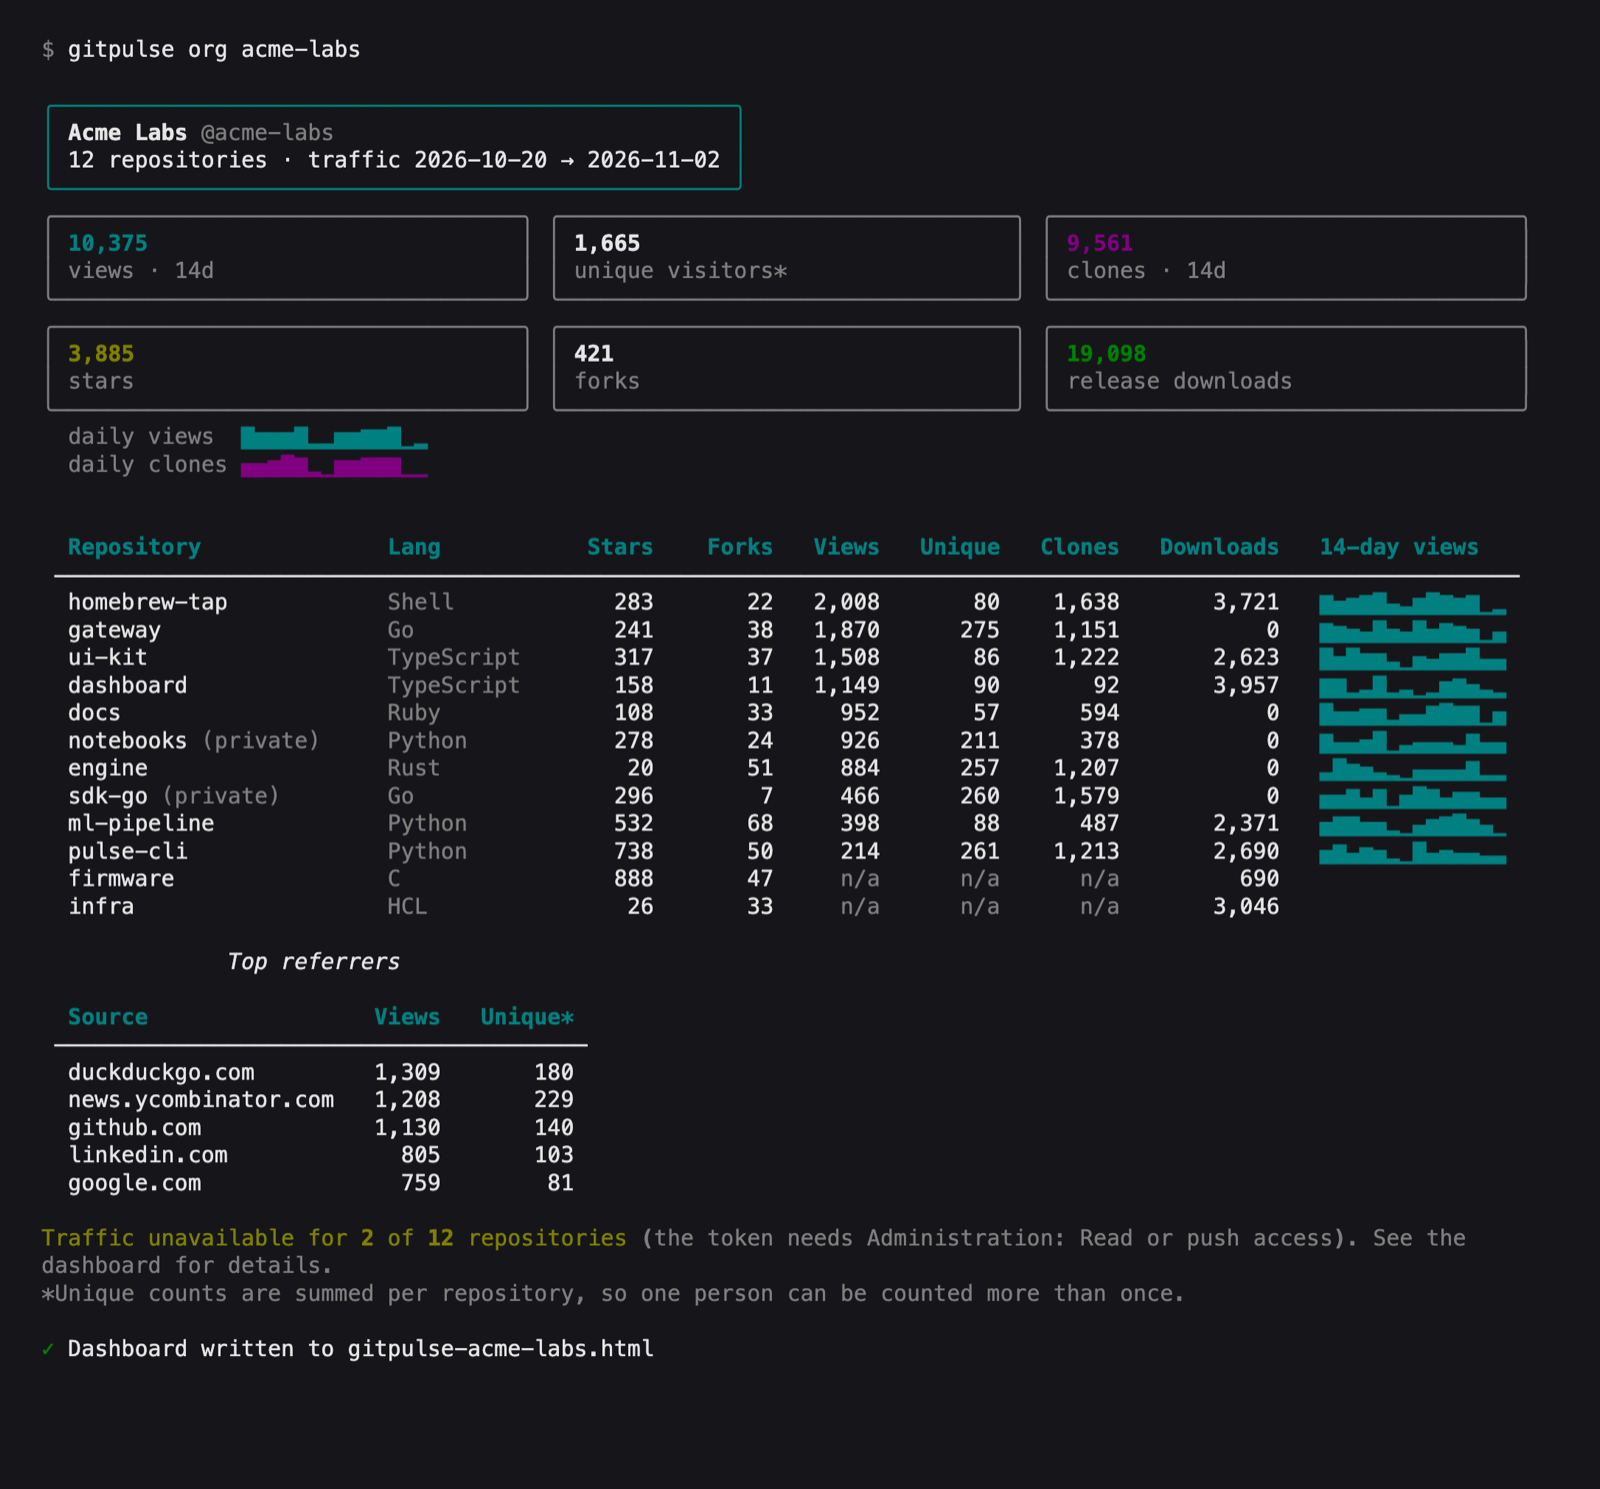
org works for an organization or a user account. It fetches every repository in parallel (--workers, default 8), then prints a summary in the terminal: totals, daily sparklines, a table of every repository, and the top referrers.
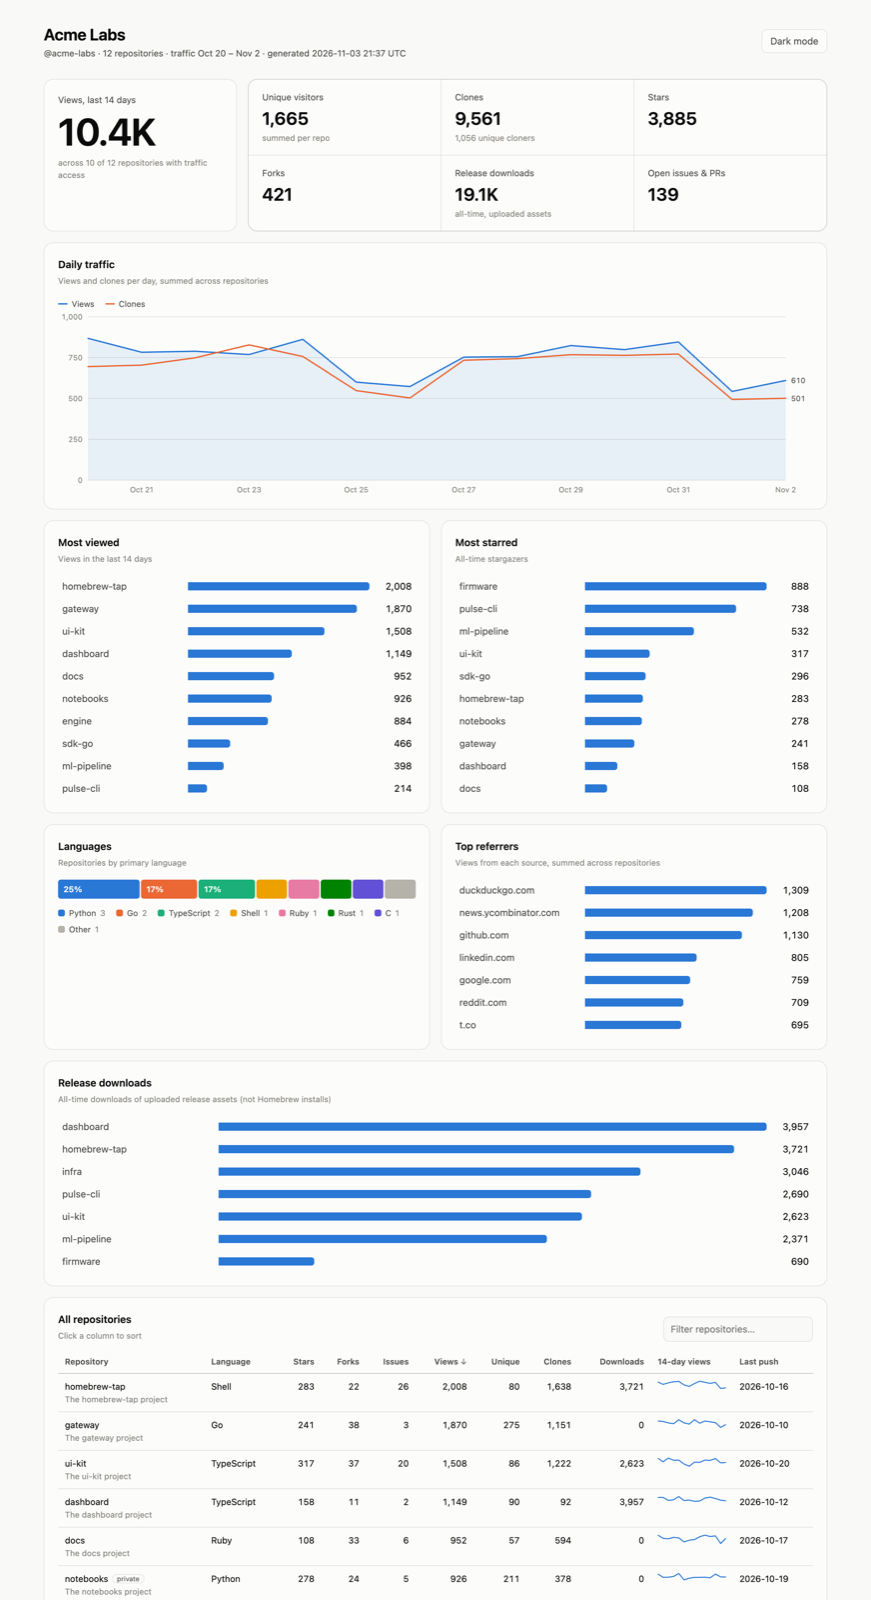
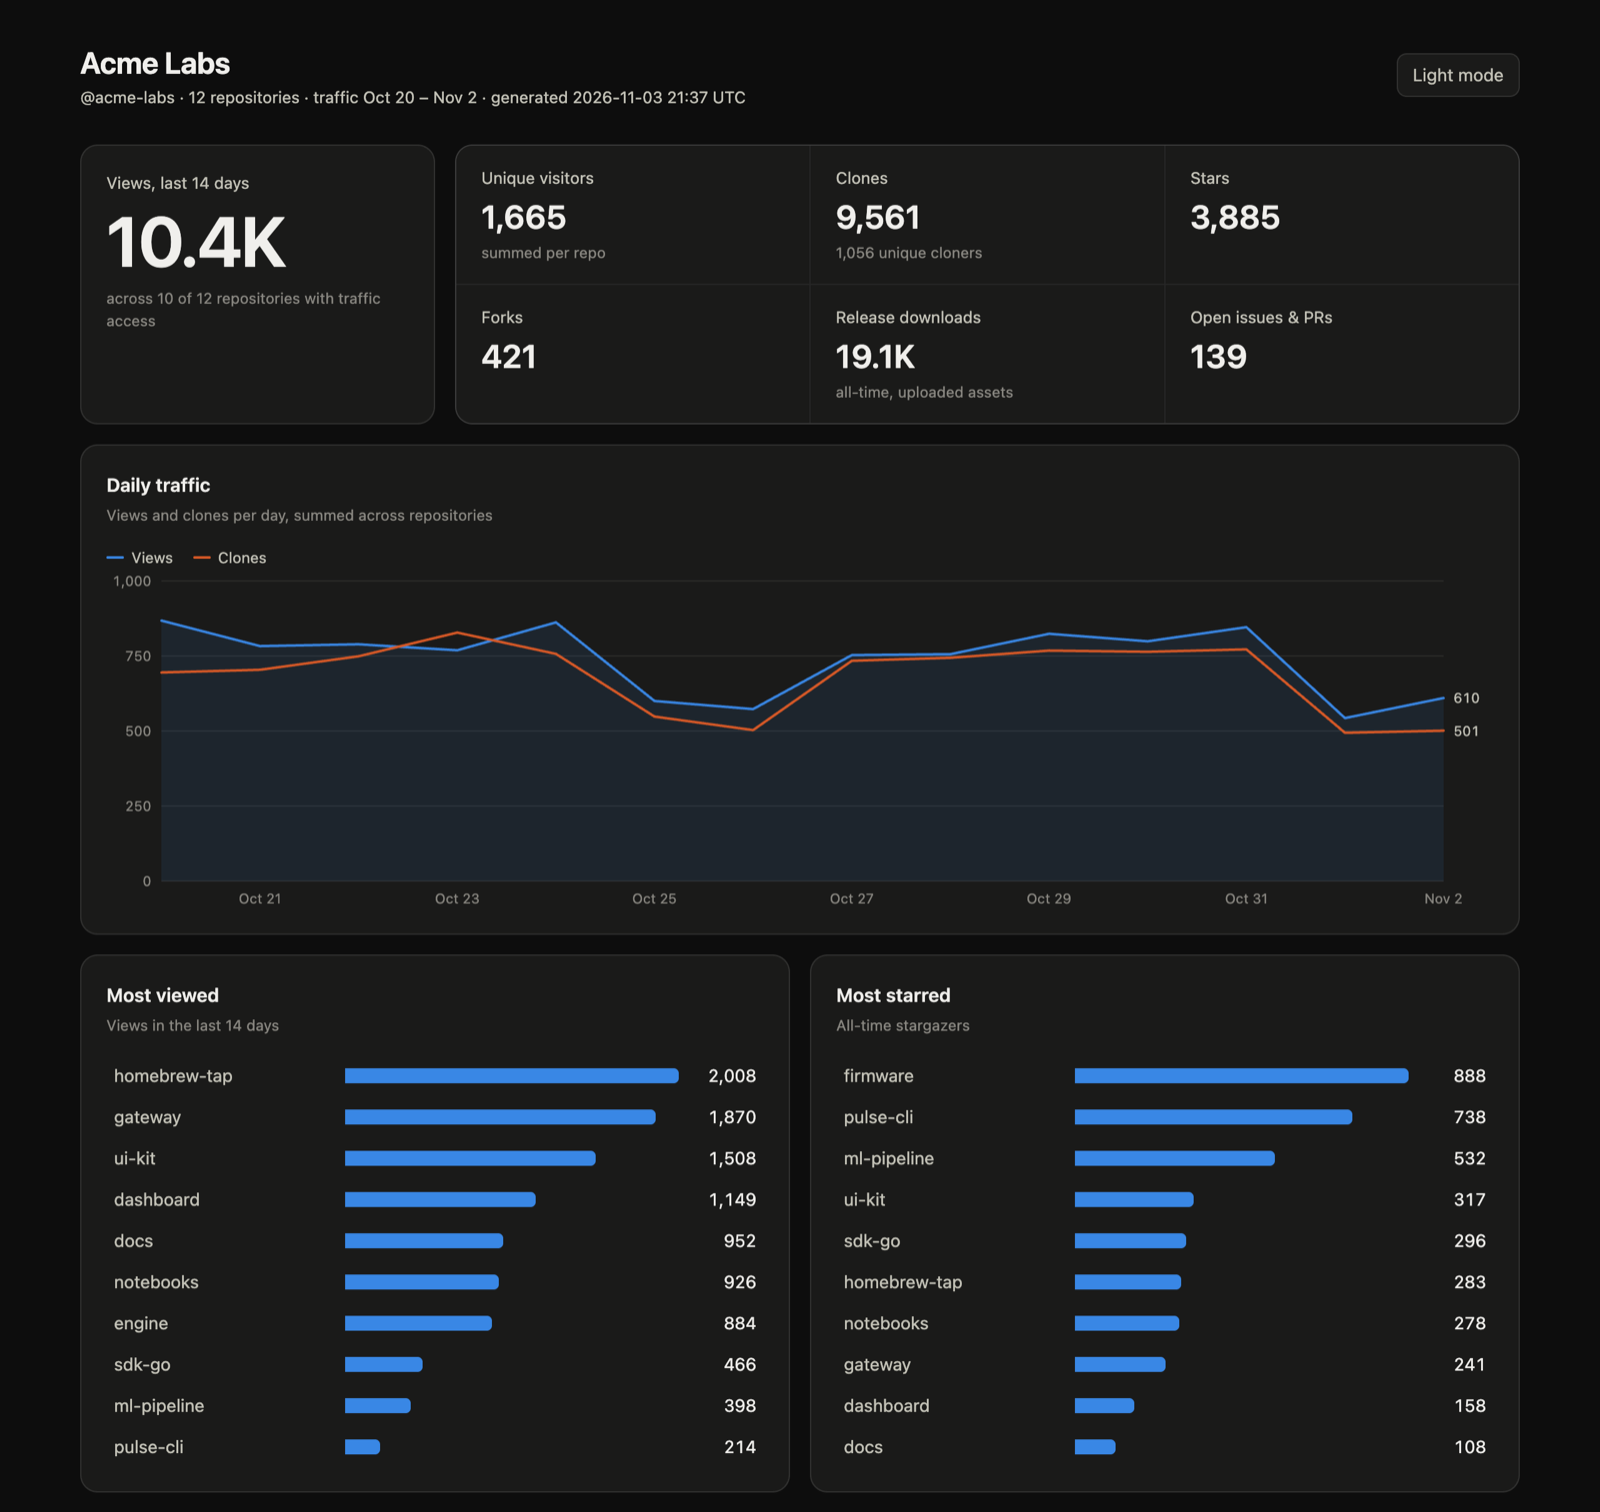
It also writes a self-contained HTML dashboard to gitpulse-ORG.html in the current directory, or to the path you pass with --output. The dashboard shows:
- Totals for views, unique visitors, clones, stars, forks, release downloads, and open issues and PRs
- Daily views and clones summed across repositories, with a hover readout for each day
- The most viewed and most starred repositories, a language breakdown, top referrers, and release downloads by repository
- A sortable, filterable table of every repository with a 14-day views sparkline
Styles, charts, and scripts are all inline, so it works offline (only the owner's avatar loads from GitHub). It follows your system's light or dark theme, and has a toggle to switch.
By default, forks and archived repositories are skipped; --all includes them. When your token can't read traffic for a repository, its stars, forks, and downloads still appear, and the dashboard lists which repositories are missing traffic and why. Unique visitor and cloner counts are summed per repository, so one person who visits two repositories is counted twice.
Screenshots show sample data.
Repository commands
gitpulse --help
gitpulse repos
gitpulse repos --all
gitpulse traffic OWNER/REPO
gitpulse traffic OWNER/REPO --metric clones
gitpulse traffic OWNER/REPO --metric referrers
gitpulse traffic OWNER/REPO --metric popular/paths
gitpulse traffic OWNER/REPO --metric views --save
gitpulse snapshot OWNER/REPO
gitpulse history OWNER/REPO --metric views
gitpulse history OWNER/REPO --metric clones
gitpulse downloads OWNER/REPO
repos lists repositories accessible to the authenticated account and filters forks and archived repositories by default. --all includes them.
traffic displays GitHub's recent traffic response. snapshot fetches views and clones and saves both responses locally. Run it on a schedule (for example, daily) to build a history beyond GitHub's 14-day window. history displays saved snapshots; it does not backfill earlier data.
downloads lists release asset download counts. It does not measure Homebrew formula installation.
Local data and privacy
Snapshots are stored at ~/.local/share/gitpulse/gitpulse.sqlite3. The database contains repository names and traffic responses, but no GitHub token. To use another location, set GITPULSE_DB to a SQLite file path.
Generated dashboards contain repository names, descriptions, and traffic numbers, including for private repositories. Treat them like any other internal report before sharing. gitpulse-*.html files are ignored by git.
Homebrew tap usage
For tap repositories, clone traffic and unique cloners can be useful directional signals, but they are not install totals. A tap clone, formula installation, and binary download are distinct events. GitHub does not expose an install-by-user report for formulae through these traffic endpoints.
Development
Run tests with pytest and lint with ruff check ..
Releasing
- Bump
__version__insrc/gitpulse/__init__.pyand merge tomain. - Publish a GitHub release with the tag
vX.Y.Zmatching that version.
The Release workflow checks that the tag matches the version, then publishes to PyPI. After that it pushes the multi-arch Docker image and updates the formula in homebrew-gitpulse. A release marked as a pre-release goes to PyPI and to Docker Hub under its exact version tag only, without moving latest or the Homebrew formula. The formula template lives in packaging/homebrew/; edit it there, not in the tap.
1 maintainer

Metadata
1 maintainer
Release files for gitpulse-analytics 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| gitpulse_analytics-0.2.0.tar.gz | 23.8 kB | With provenance | Details for gitpulse_analytics-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| gitpulse_analytics-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for gitpulse_analytics-0.2.0-py3-none-any.whl |
Total release size: 48.7 kB
Release files / gitpulse_analytics-0.2.0.tar.gz
| Download URL | gitpulse_analytics-0.2.0.tar.gz |
|---|---|
| Size | 23.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
1dcb44914b2ceda576d6c3a8f44f105fc2deae2d938236abaf77e495f7f80428
|
|
BLAKE2b-256 checksum How to use checksums |
ee5ce1c2ff886df84faa20d0630330c85d7dfd037b6809bf7b70f618f8a289a1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logRelease files / gitpulse_analytics-0.2.0-py3-none-any.whl
| Download URL | gitpulse_analytics-0.2.0-py3-none-any.whl |
|---|---|
| Size | 25.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
14b0d2937d70b439cbd3bbf7f690aa15671b9296a02dd5394f66f8916e449ae9
|
|
BLAKE2b-256 checksum How to use checksums |
a0a1de4d1cc4d21f86da2dd525cf6ca51d328857f3a75c3f0a9e72c94bcc674e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logSecurity for gitpulse-analytics 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for gitpulse_analytics-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














