
glassport
See what an MCP server actually does, not just what it declares.
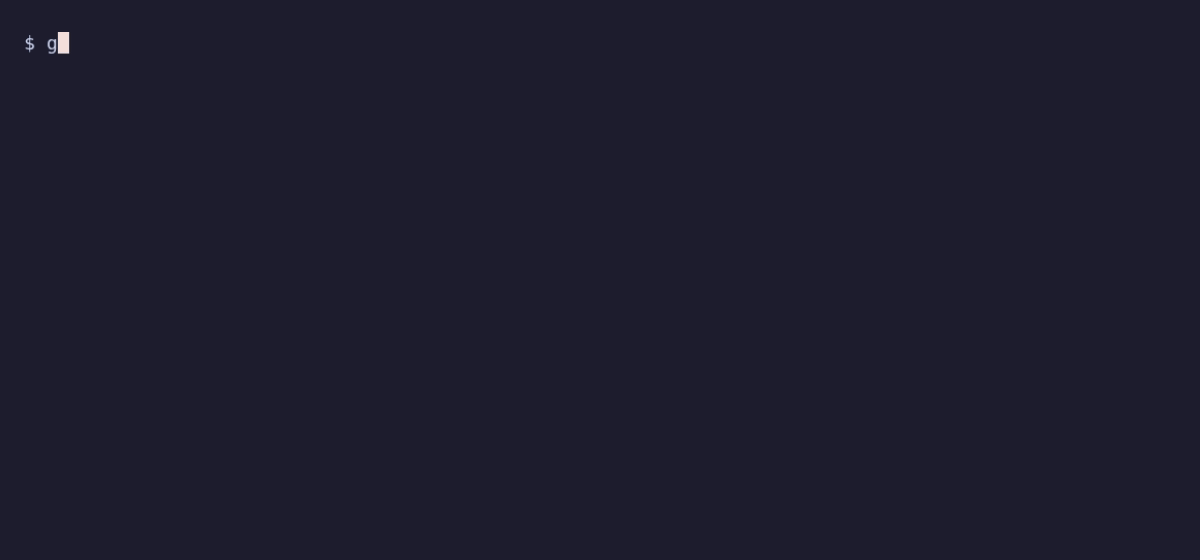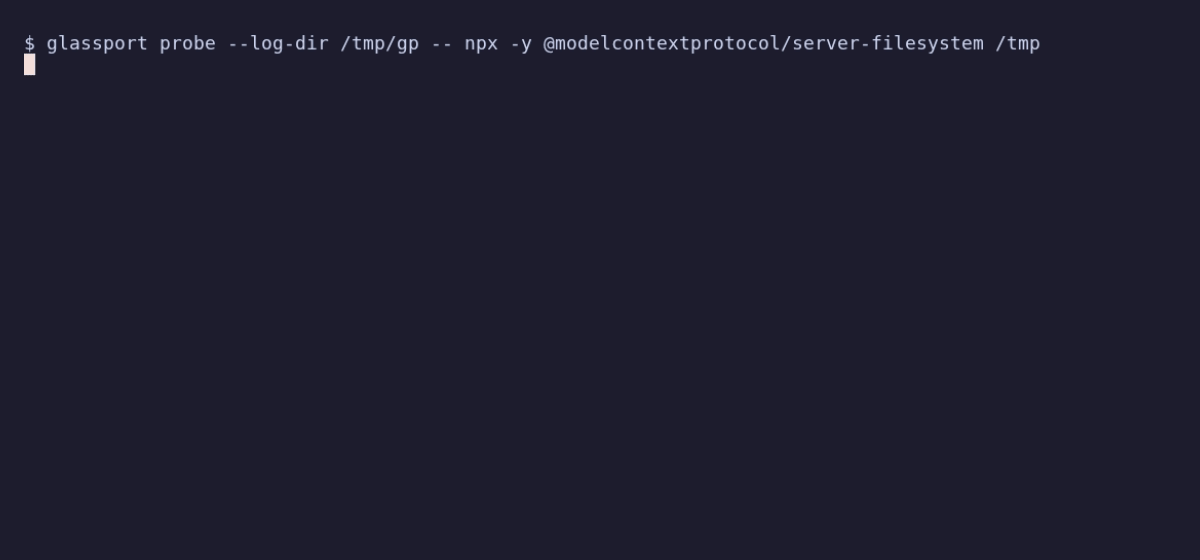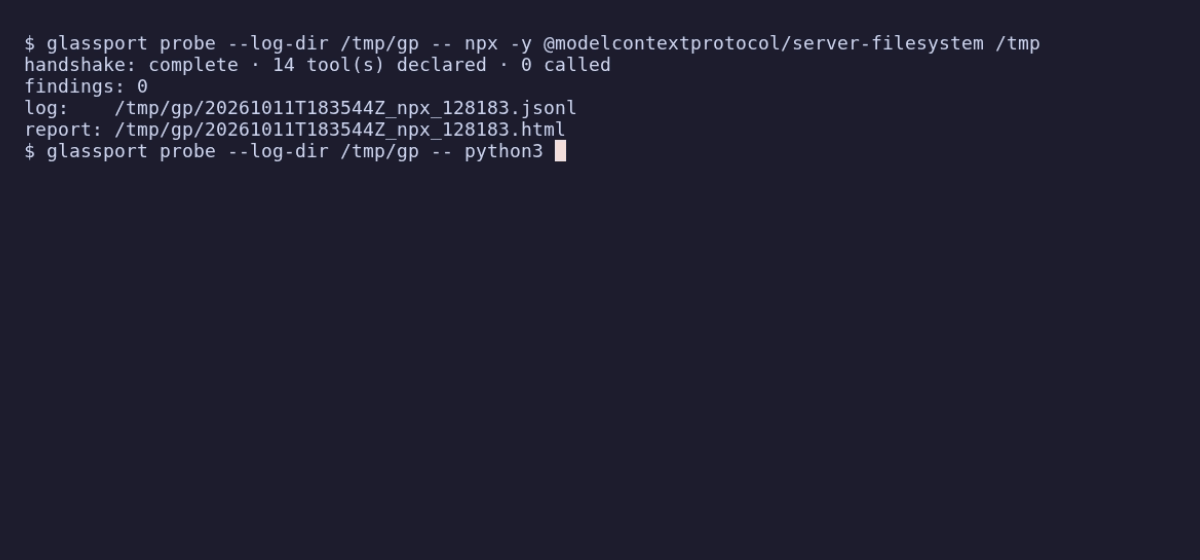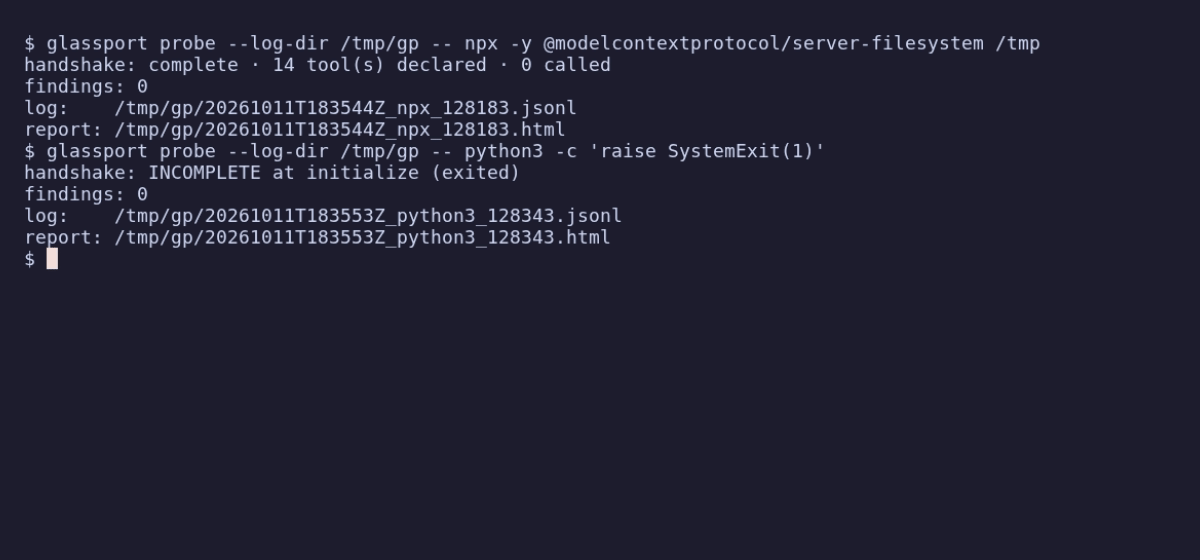
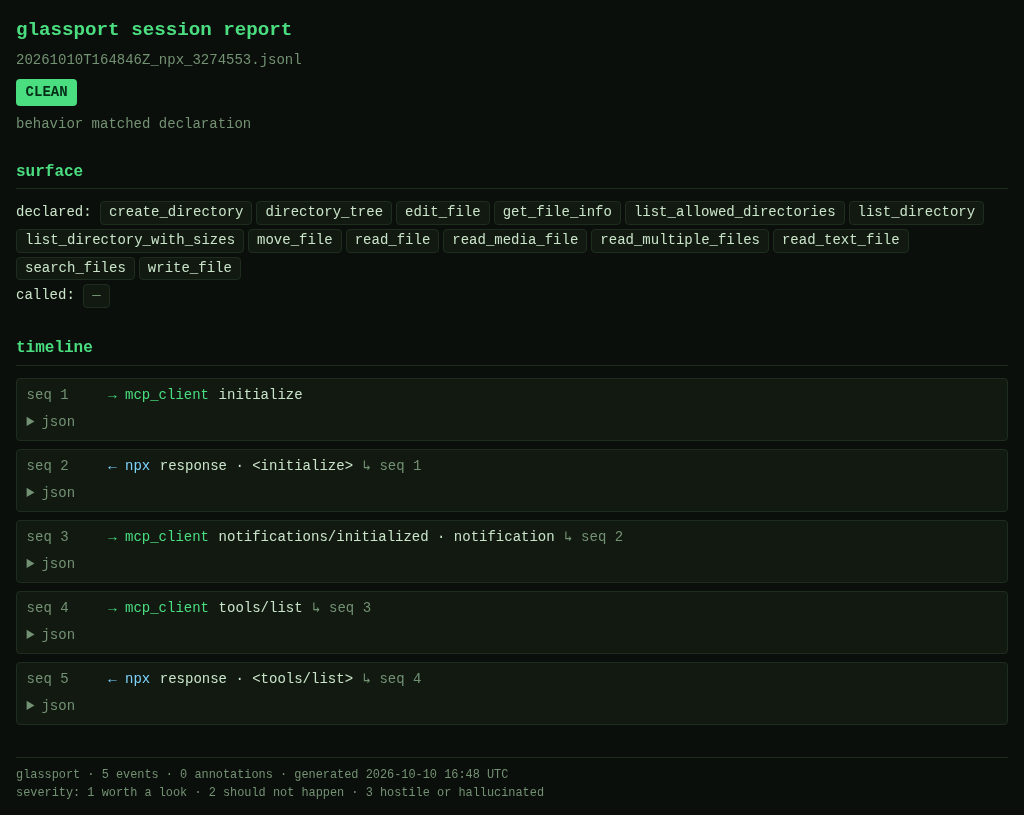
An MCP server tells your agent what it offers in its tools/list handshake. Everything after that is behavior. Glassport sits on the wire between the two and reports the gap: calls outside the declared surface, secrets leaving in arguments, a tool list that quietly changes mid-session. Point it at a server and it plays the client, or put it in front of a real agent session and it records passively. No cloud, no sandbox, zero dependencies.
pip install glassport
glassport probe -- npx -y @modelcontextprotocol/server-filesystem /tmp
# -> handshake, tools/list, detectors; prints the path to an HTML report
- Real sessions:
glassport wrap -- <server command>in your MCP client config, thenglassport report <session.jsonl>. - CI:
glassport audit <path> --sarifreads server source without running it and uploads to the GitHub Security tab.
Deeper docs → · MIT · Python 3.10+ · runs in Termux
1 maintainer

Metadata
1 maintainer
Release files for glassport 0.7.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| glassport-0.7.0.tar.gz | 370.8 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| glassport-0.7.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 572.3 kB
Release files / glassport-0.7.0.tar.gz
| Download URL | glassport-0.7.0.tar.gz |
|---|---|
| Size | 370.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a307e4bceba5b938ced994125466746a31b13a3be16f83b739110cde92176f0d
|
|
BLAKE2b-256 checksum How to use checksums |
e924255ed97ee9a6cffb9f5866471ba23a118db1a86a31de8ff798306d3593e8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency logRelease files / glassport-0.7.0-py3-none-any.whl
| Download URL | glassport-0.7.0-py3-none-any.whl |
|---|---|
| Size | 201.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
b80ede298f36f85fd29b7d1e72d8af478ae0327d5f2ae0e3747b907bef913135
|
|
BLAKE2b-256 checksum How to use checksums |
c102d0f8704a5bac2c623586b3042cc0e5f32f1aec3dda865edfe82b3bdd2f97
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency log













