
gmic-sphinx
A Sphinx extension for displaying G'MIC command results as images using the gmic-py Python binding.
Usage
This Sphinx extension adds a new directive name gmicpic that takes any gmic expression as input and outputs an image and the gmic command below as caption (other could come later). It has been tested with Sphinx's html builder only for now.
It works only with the reStructuredText (aka ReST) documentation format, not Markdown or others.
In any of your .rst file, add the following:
.. gmicpic:: your gmic command
For example:
.. gmicpic:: sp earth blur 4 output earthy.png
will yield a picture file-named earthy.png followed by the command as caption:
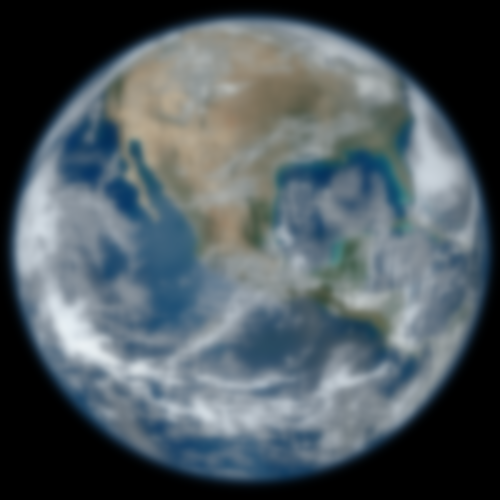
sp earth blur 4 output earthy.png
G'MIC command pre-processing
- that the
outputparameter is optional. - In order to prevent proxy-blocking issues at docs build-time, G'MIC's samples are stored in this extension:
.. gmicpic:: sp leno blur 4
will yield a picture file-named with a unique id cce2fce2-e6fc-11ea-9e0e-8cec4b8c0881.png followed by the command as caption:

sp leno blur 4
...implies that leno.png exists in the gmic_samples directory (we have done it for you for <=2020 image samples already).
The resulting implicit output image will be pre-stored in gmic-images/ with a unique-id generated .png filename.
Installing & set-up
Install this Python module from pypi.org (in the same virtual environment as Sphinx):
pip install gmic-sphinx
Edit your Sphinx documentation project's conf.py file and ensure you have line like:
extensions = ['gmic-sphinx']
You might need to add gmic-sphinx to your Python path.
Projects using this
This extension is used in the following projects:
- gmic-py // readthedocs.io documentation
- PR to add your project here :)
Tests
Automated pytest test cases are run in the Github Actions tab. You can run them yourself as well in a Python >= 3.7 environment.
Install the test requirements:
pip install dev-requirements.txt
Install the package locally:
pip install .
Run the pytest test suite:
py.test tests/
Releasing
If you are maintainer and would like to trigger a new release for this project, you do not need any credential since they are stored as Github Secret for this project. You just have:
- Change the version number in
gmic_sphinx/gmicpic.py'ssetup()function andgmic_sphinx/gmicpic.py'ssetup()function. - to Git-push a new tag, as described in this Github Action Worfklow file.
License
This project is under the CeCILL License.
1 maintainer

Metadata
1 maintainer
Release files for gmic-sphinx 0.0.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| gmic-sphinx-0.0.4.tar.gz | 32.4 MB | Without provenance | Details for gmic-sphinx-0.0.4.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| gmic_sphinx-0.0.4-py3-none-any.whl | Python 3 | none | any | Details for gmic_sphinx-0.0.4-py3-none-any.whl |
Total release size: 64.7 MB
Release files / gmic-sphinx-0.0.4.tar.gz
| Download URL | gmic-sphinx-0.0.4.tar.gz |
|---|---|
| Size | 32.4 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
30e05a7fd69ce5d3917a5ec3b915fa0c9ebc083684c048796486eee3f40469f5
|
|
BLAKE2b-256 checksum How to use checksums |
ff4a90517e50655ad4abbc6a778eca6068152bd4bb1d15a7a02e42b96bc326e3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.2.0 pkginfo/1.5.0.1 requests/2.24.0 setuptools/47.1.0 requests-toolbelt/0.9.1 tqdm/4.48.2 CPython/3.7.9
|
Release files / gmic_sphinx-0.0.4-py3-none-any.whl
| Download URL | gmic_sphinx-0.0.4-py3-none-any.whl |
|---|---|
| Size | 32.4 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
e81236fc0443277820f0402fc221c56f778cb751fe304c24f8be682693a9890d
|
|
BLAKE2b-256 checksum How to use checksums |
3bfb11d040d0155e6cdf6c0df15affe7b129a6d7aef553bf59893a8ee28def69
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.2.0 pkginfo/1.5.0.1 requests/2.24.0 setuptools/47.1.0 requests-toolbelt/0.9.1 tqdm/4.48.2 CPython/3.7.9
|
Security for gmic-sphinx 0.0.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














