
 Guardmarly — Static analysis for authorization gaps and risky code paths
Focused on missing object-level authorization checks (IDOR / broken access control) and related security findings across supported languages.
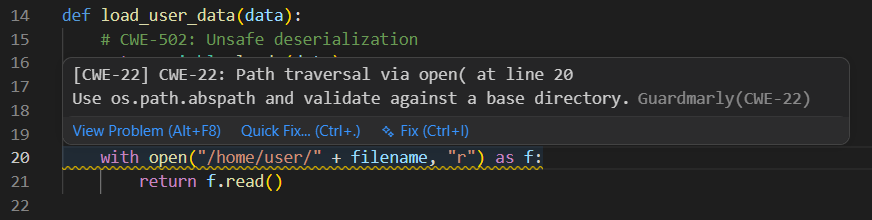



pip install guardmarly && guardmarly src/
The problem
Authorization bugs — IDOR, missing access controls, privilege escalation — caused some of the largest data breaches in history. Most SAST tools can't find these bugs because they require tracing data from HTTP routes through auth guards into database queries.
What Guardmarly does differently
@app.route("/invoice/<id>")
def get_invoice(id):
    return Invoice.query.get(id)
    # ↑ CWE-639 IDOR: any user can view any invoice
    #   Bandit: silent. Semgrep OSS: silent. CodeQL: silent.
    #   Guardmarly: 🚨 CRITICAL — route flows to DB without auth check
Guardmarly maps every HTTP route, checks for auth guards, traces data flow to sinks, and flags the gap.
Quick start
pip install guardmarly
guardmarly src/                          # text output
guardmarly src/ --format json -o r.json  # JSON report
guardmarly src/ --format sarif           # SARIF for GitHub
guardmarly --show-stats                  # lifetime + today counts
guardmarly --list-rules                  # full rule catalog
Supported languages & CWEs
5 full-AST languages: Python, JavaScript/TypeScript, Go, Java, C#
35+ pattern-aware languages: PHP, Ruby, Kotlin, Swift, Dart, Rust, Scala, Elixir, C/C++, Lua, and 25+ more
35+ CWE types: IDOR (CWE-639), Missing Auth (CWE-862/306), SQLi (CWE-89), Command Injection (CWE-78), XSS (CWE-79), Path Traversal (CWE-22), SSRF (CWE-918), Deserialization (CWE-502), Hardcoded Secrets (CWE-798), Open Redirect (CWE-601), CSRF (CWE-352), XXE (CWE-611), and 25+ more.
Evidence: See CLAIMS_AND_EVIDENCE.md for benchmark methodology, corpus details, and measured results. Detection rates vary by language and CWE category.
Contributing
git clone https://github.com/mattybellx/Guardmarly.git
cd Guardmarly && pip install -e ".[dev]"
pytest tests/ -q                       # 1,183+ tests in ~12s
License
See LICENSE for terms. Guardmarly is source-available software.
1 maintainer

Metadata
1 maintainer
Release files for guardmarly 6.6.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| guardmarly-6.6.0.tar.gz | 930.8 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| guardmarly-6.6.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.9 MB
Release files / guardmarly-6.6.0.tar.gz
| Download URL | guardmarly-6.6.0.tar.gz |
|---|---|
| Size | 930.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
717a1fcf20331f6491ea725ce623ad9e03865737b5f26bb9ac44dffbb227dd70
|
|
BLAKE2b-256 checksum How to use checksums |
8ee8d2417ea7baa9fa71e588e9c3180ebcb6896f0d313545fece5c3b01ef7b85
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 19, 2026.
Transparency logRelease files / guardmarly-6.6.0-py3-none-any.whl
| Download URL | guardmarly-6.6.0-py3-none-any.whl |
|---|---|
| Size | 936.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d63116a7f1b48380c66ef979cc0df7107107d9edafa452abc7680af8d68ec3fa
|
|
BLAKE2b-256 checksum How to use checksums |
e6b5e1f3b1414ef490c2ada168b05929ab8d69fab02d5fd0945473121a7d56a0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 19, 2026.
Transparency logSecurity for guardmarly 6.6.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for guardmarly-6.6.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 19, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














