
Happy Jar CLI
An easy to use CLI for storing good memories and gratitiude.
# basic logging
$ happy log "Happy text here! :D"

# view logs with
$ happy get all

# or,
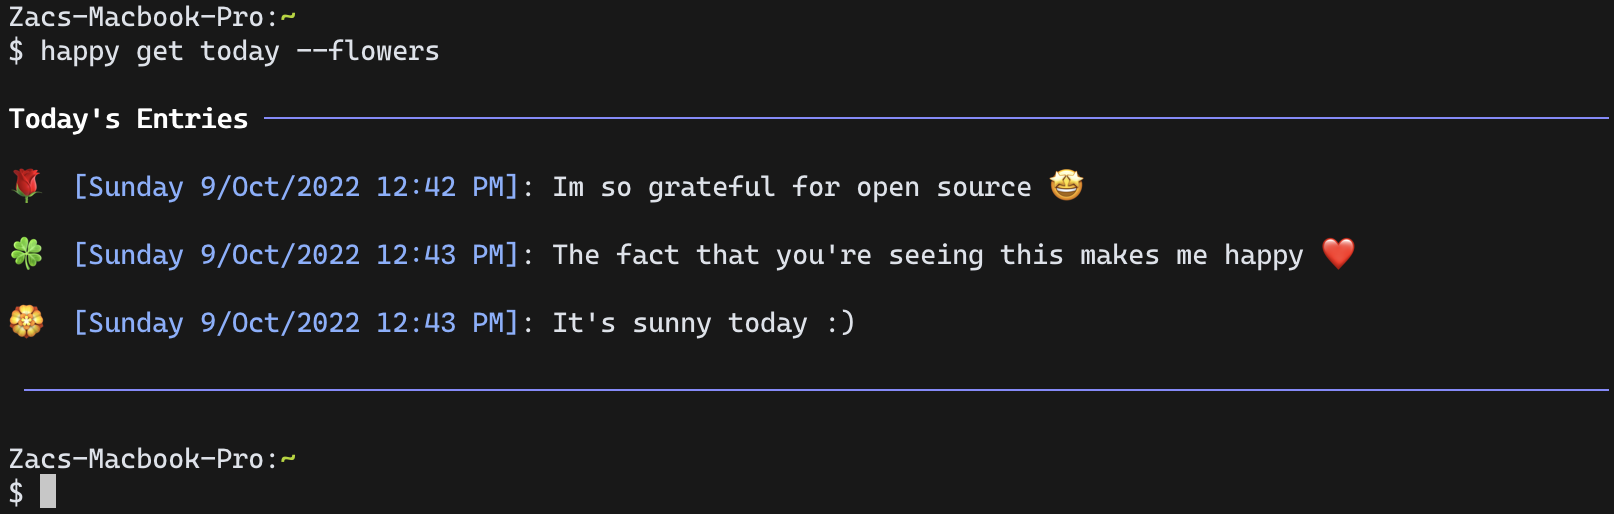
$ happy get today
Installation
pip install happyjar
Binaries:
Download the binary for your platform from the Artifacts section of the latest GitHub Actions run.
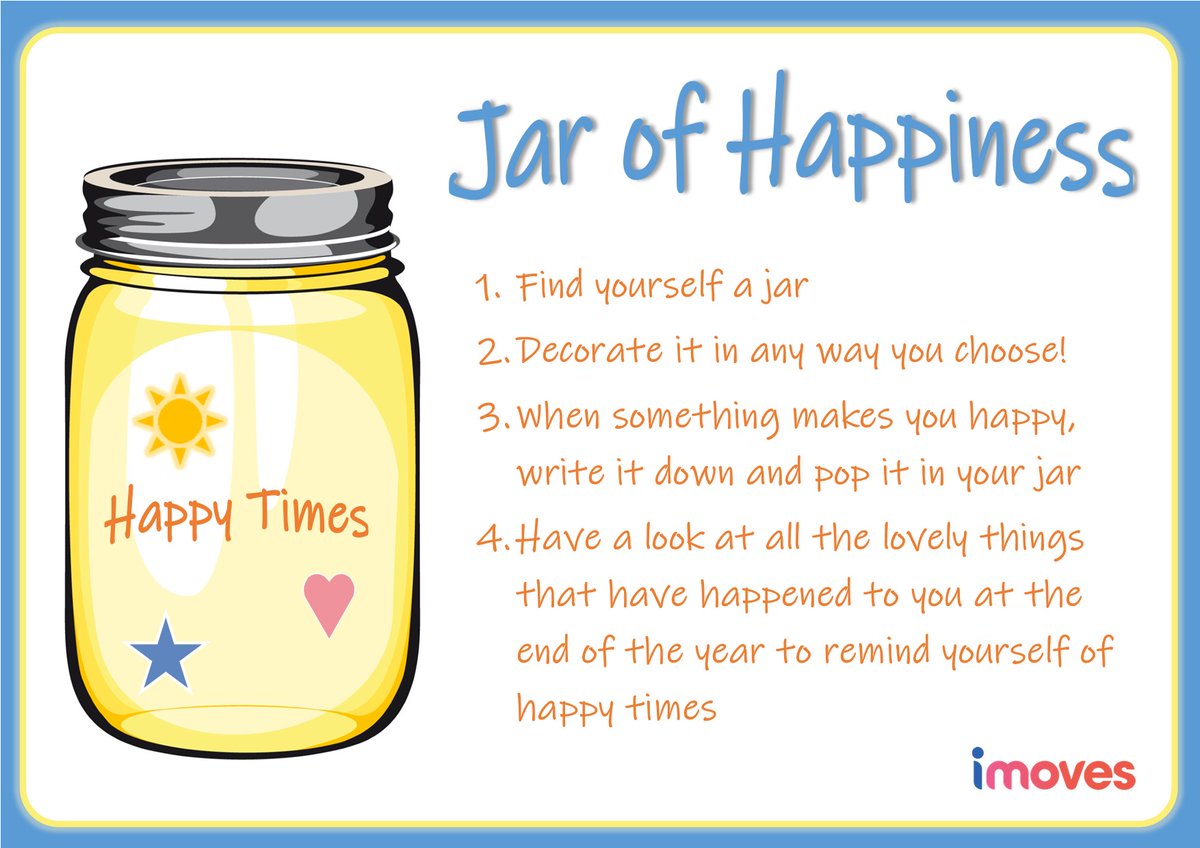
What is it?
Usage
$ happy --help
usage: happy [-h] {log,get} ...

Log your good memories and gratitiude.

positional arguments:
  {log,get}
    log       logs an entry
    get       gets entries

optional arguments:
  -h, --help  show this help message and exit

examples:
happy log "i am so happy because you starred this project's repo on github xDD"
happy get all
Example
Inspired by michelle/happy
Todo
- Add support for markdown emojis with the
:emoji:format. Use Textualize/rich for this.
Check Issues for more.
Contributors
- HitBlast the Mighty
- Diwash Dahal the Conqueror
- Franklin Ikeh the Neat
- Micah Wood the Strong
🎉 Commit labels
If you're interested in the commit labels used in this repo, check out my git commit emoji project
1 maintainer

Metadata
1 maintainer
Release files for happyjar 4.0.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| happyjar-4.0.1-py3-none-any.whl | Python 3 | none | any | Details for happyjar-4.0.1-py3-none-any.whl |
Release files / happyjar-4.0.1-py3-none-any.whl
| Download URL | happyjar-4.0.1-py3-none-any.whl |
|---|---|
| Size | 18.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
377c6ffb0313bc49c904e06e757910c42b30007b10c1cee323c6044a3cb69b8c
|
|
BLAKE2b-256 checksum How to use checksums |
0a5fce34828d19f2ae0f0c8602f645df08720704433065b7744f6a42ab308a13
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.1 CPython/3.9.0
|
Security for happyjar 4.0.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














