
Hidori


Hidori is a modern, agentless, zero-dependency1 variation on updating system state. General rule of thumb is that changes to the system are only done if the requested state is different from the actual state. Hidori modules are idempotent if the system is already in the desired state. Every change in the destination system is reported through the modules log as "affected".
Hidori communicates with destination machines through appropriate protocol that is designated by the chosen driver.
Install
Depending on your environment you might wish to install Hidori globally or locally using chosen Python dependency manager such as poetry or pip. Ultimately, the choice is yours. Either way, Hidori is safe for your Python environment - it does not pull any dependencies from PyPI.
Example using pip:
pip install hidori
Hello World
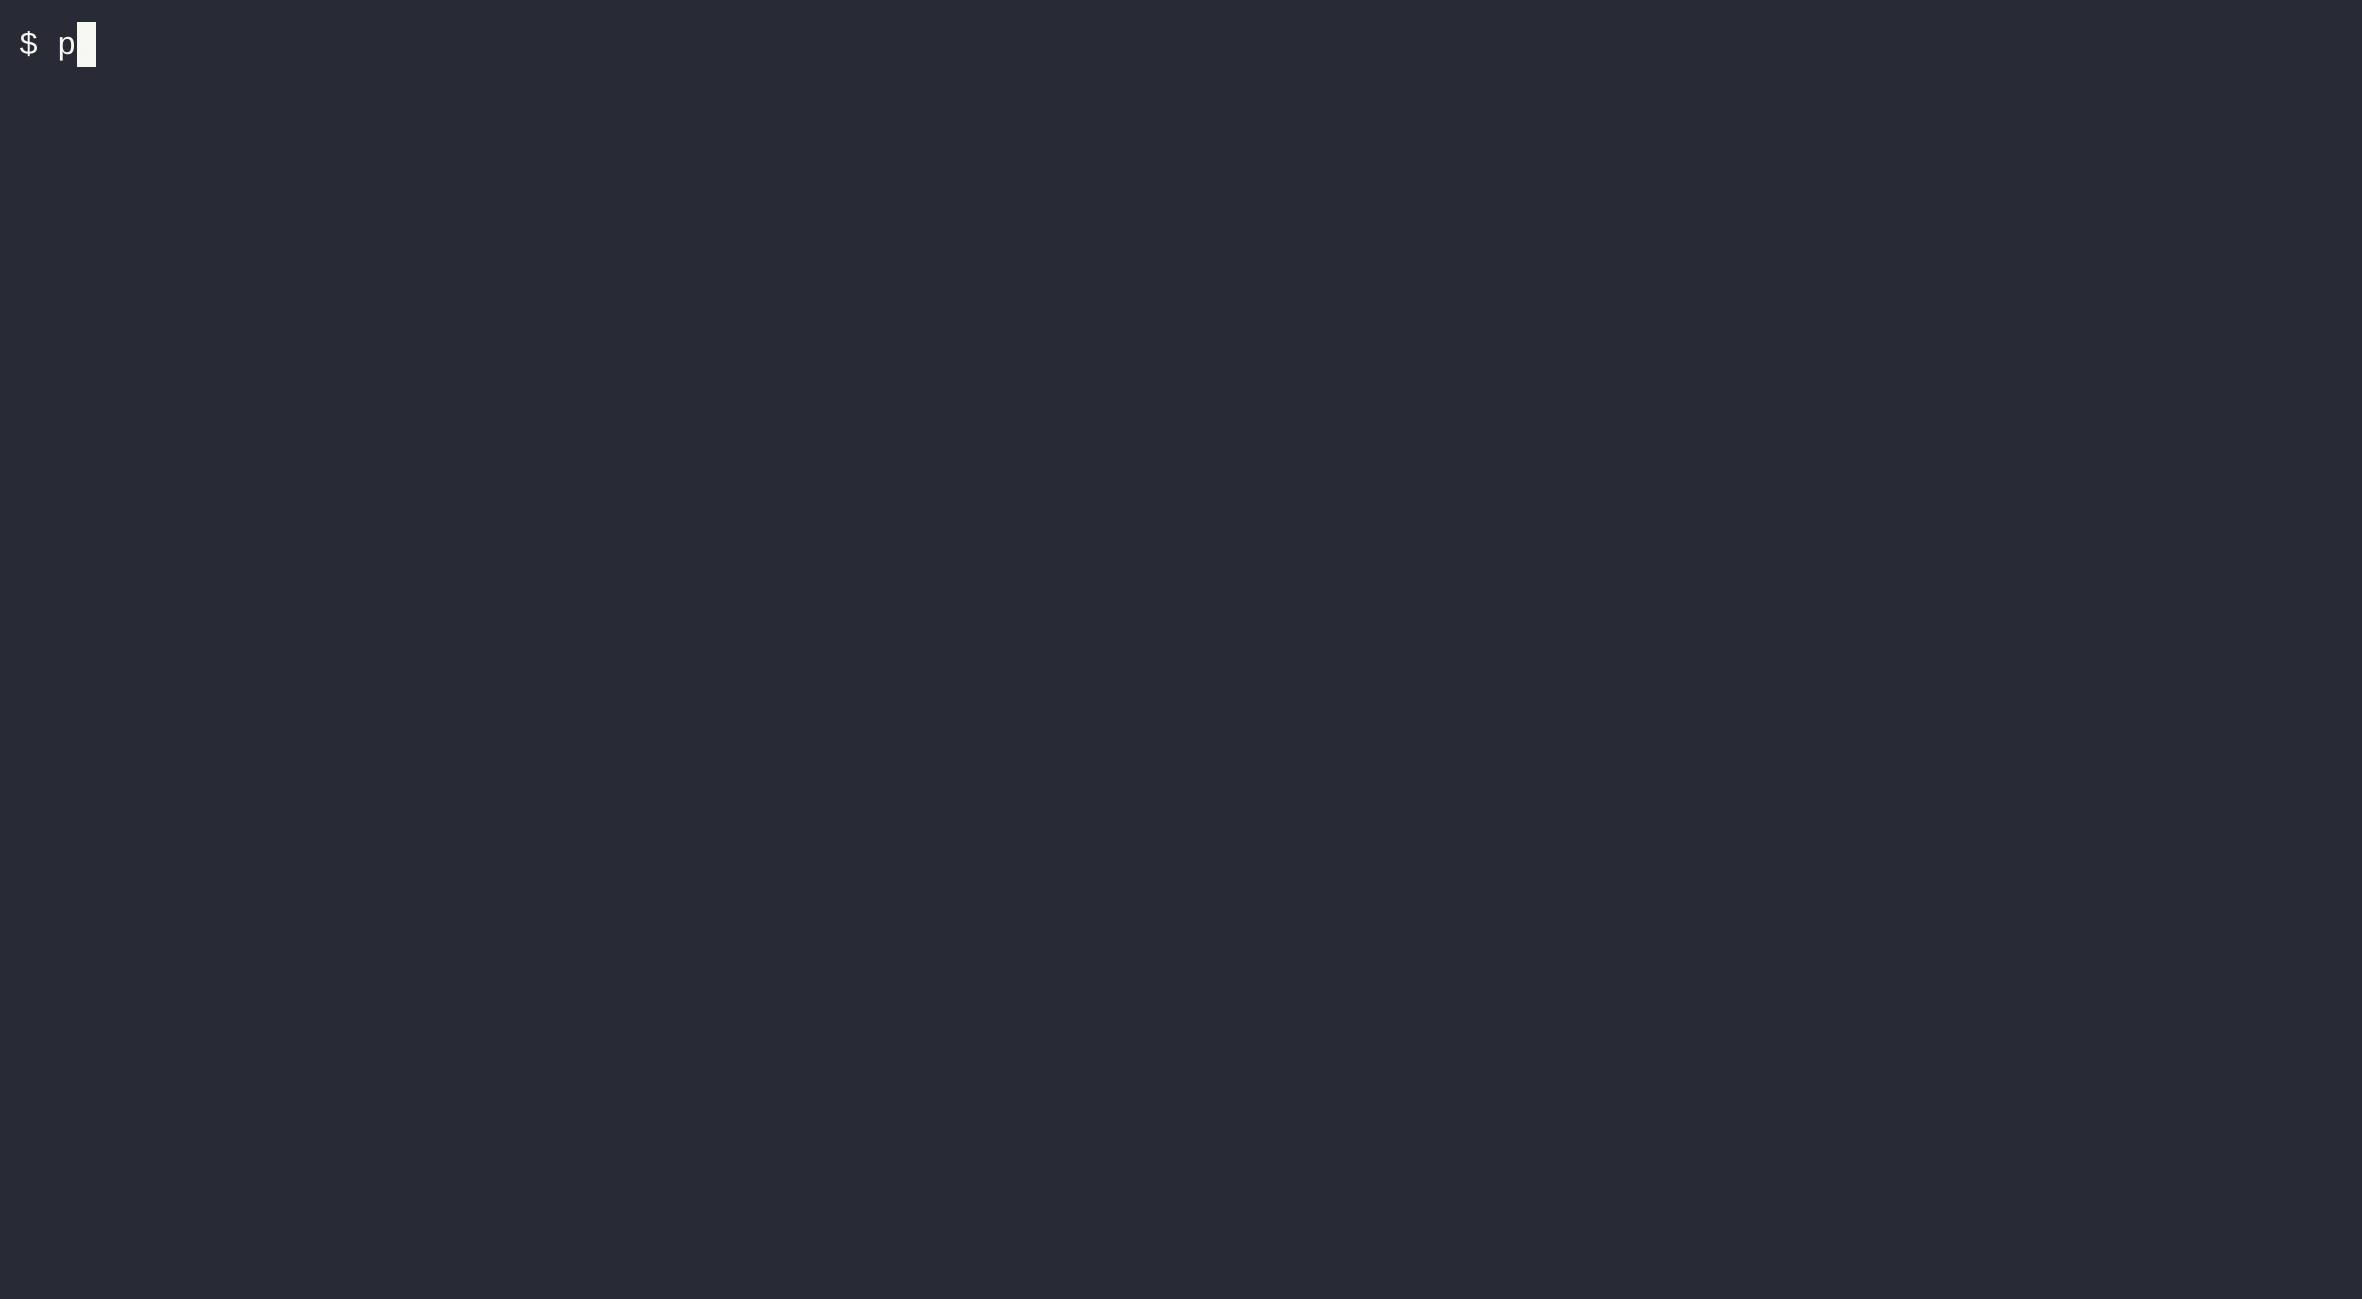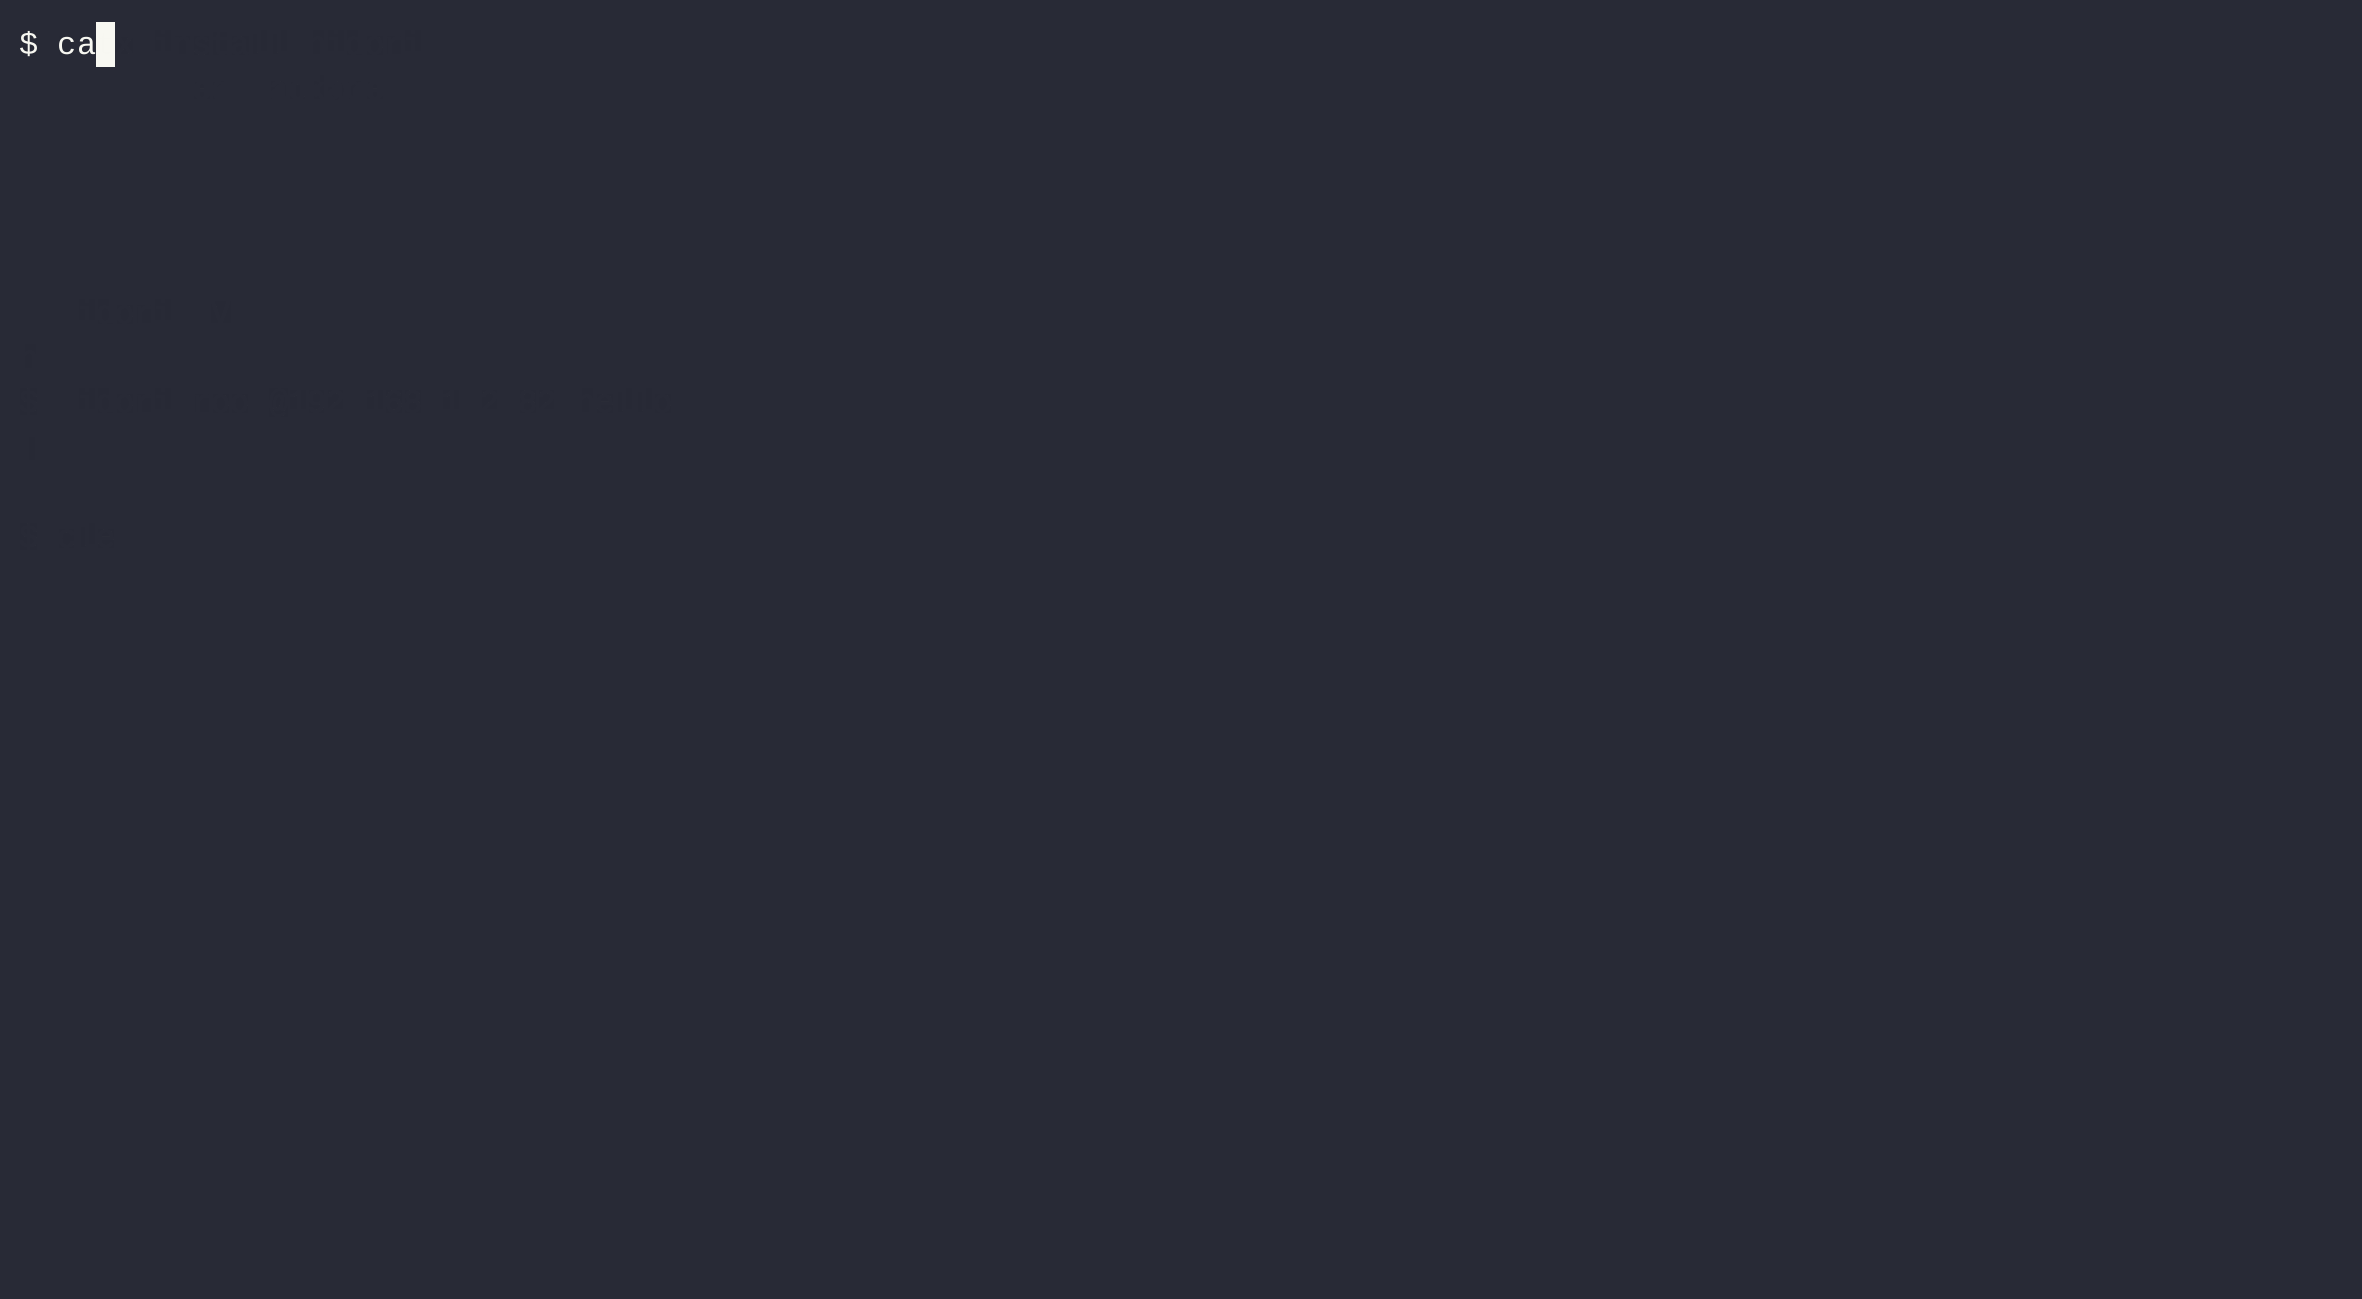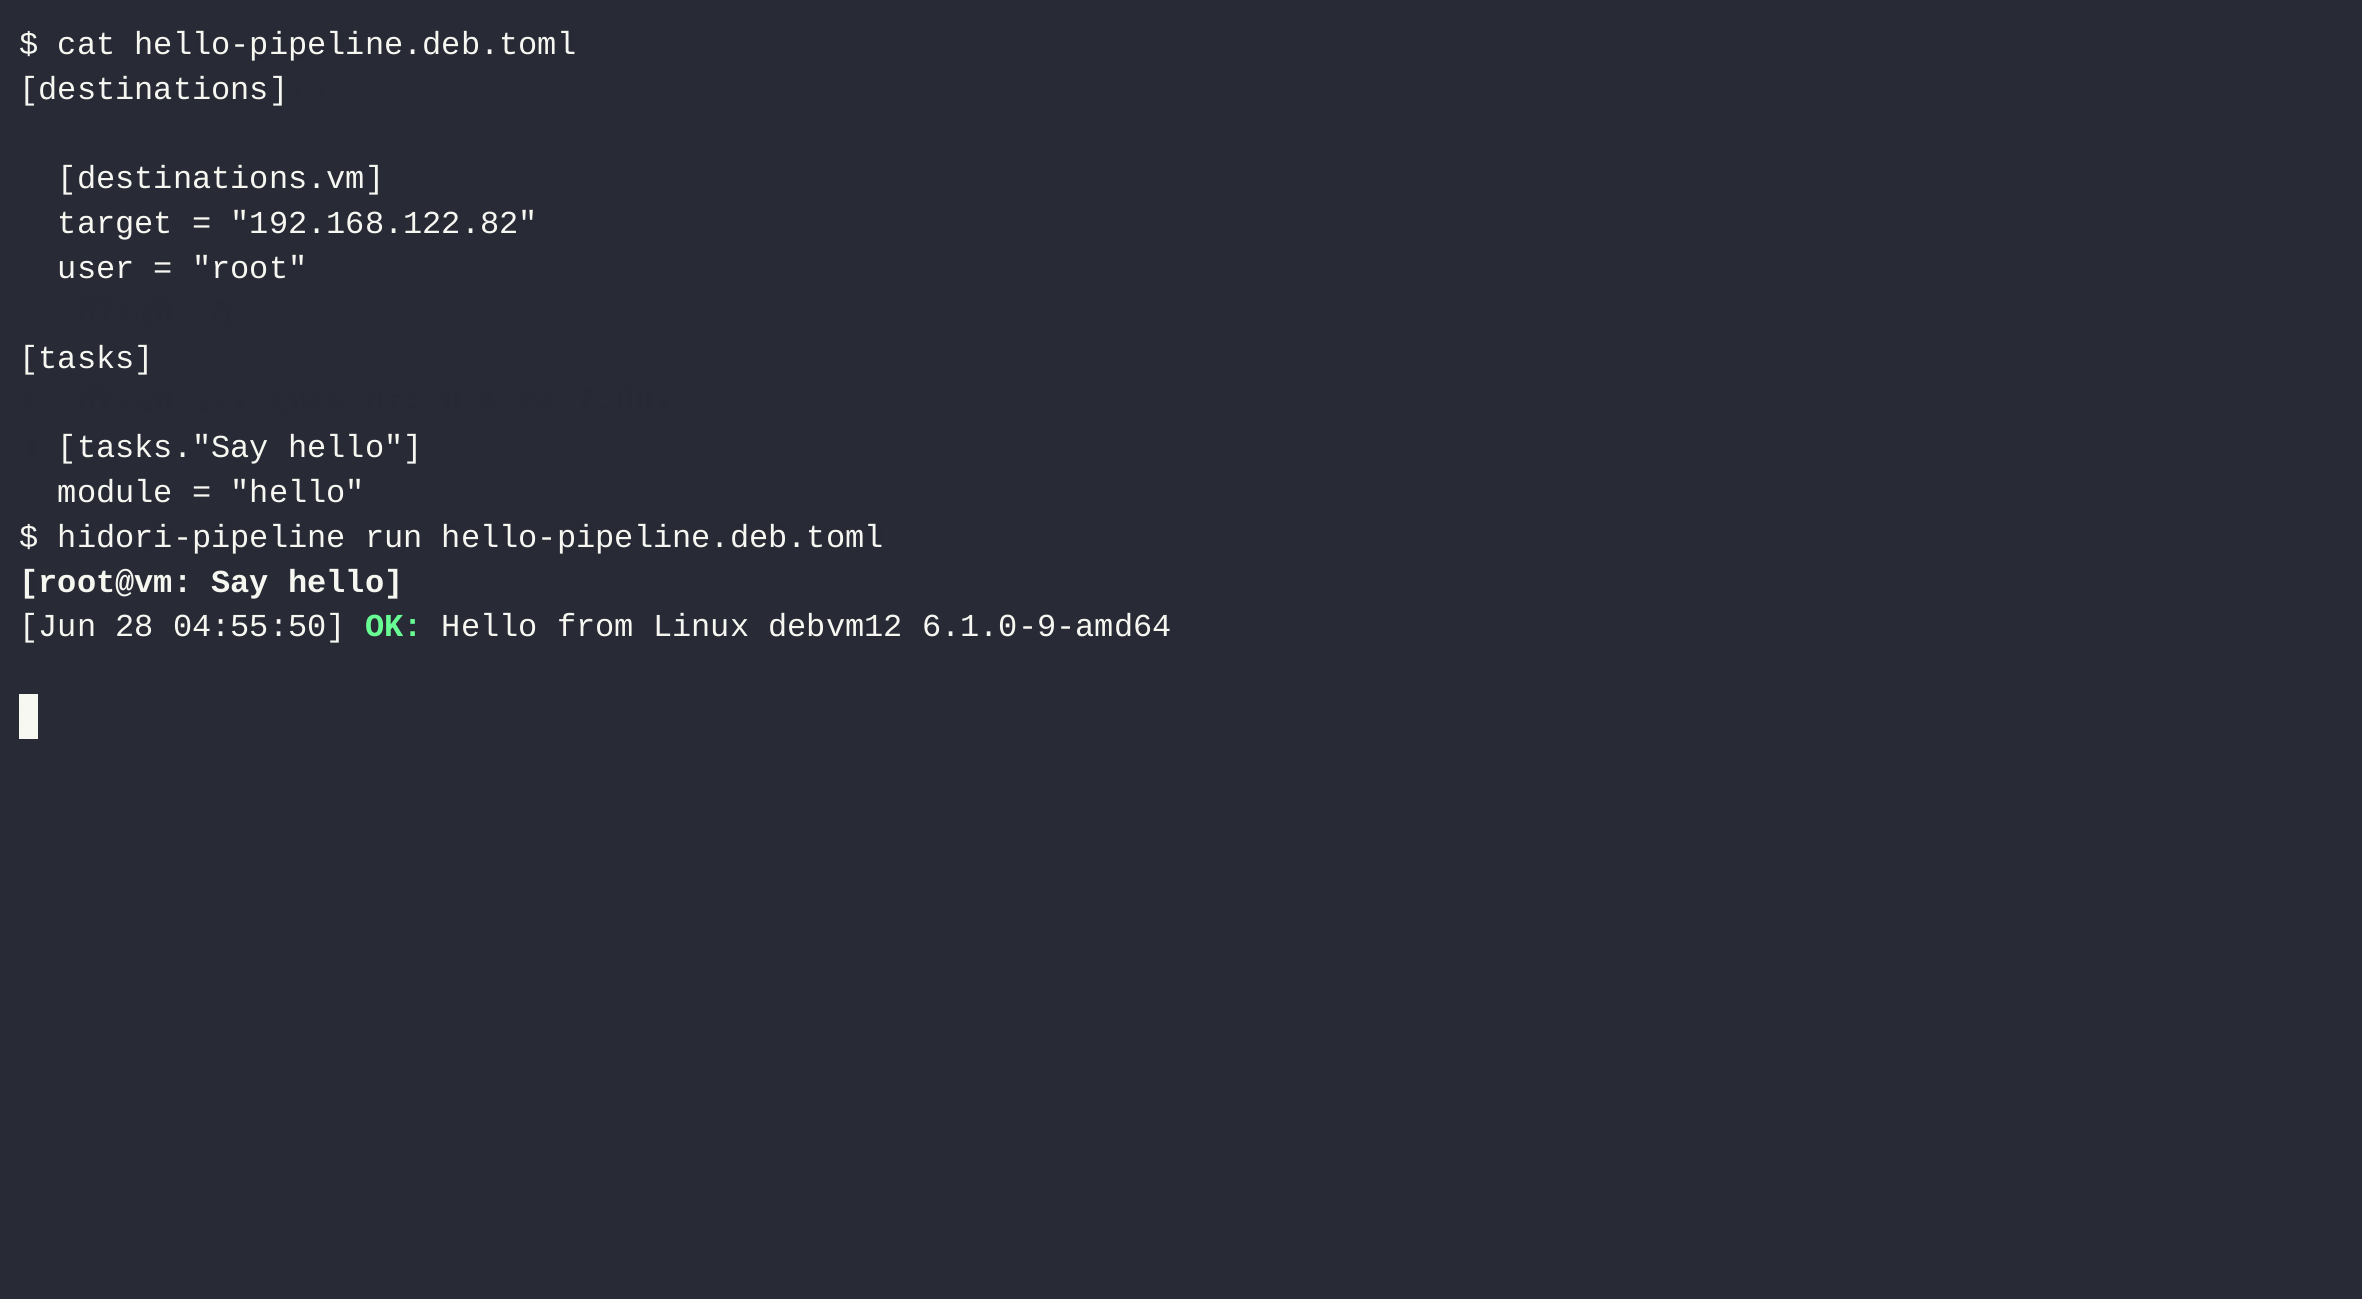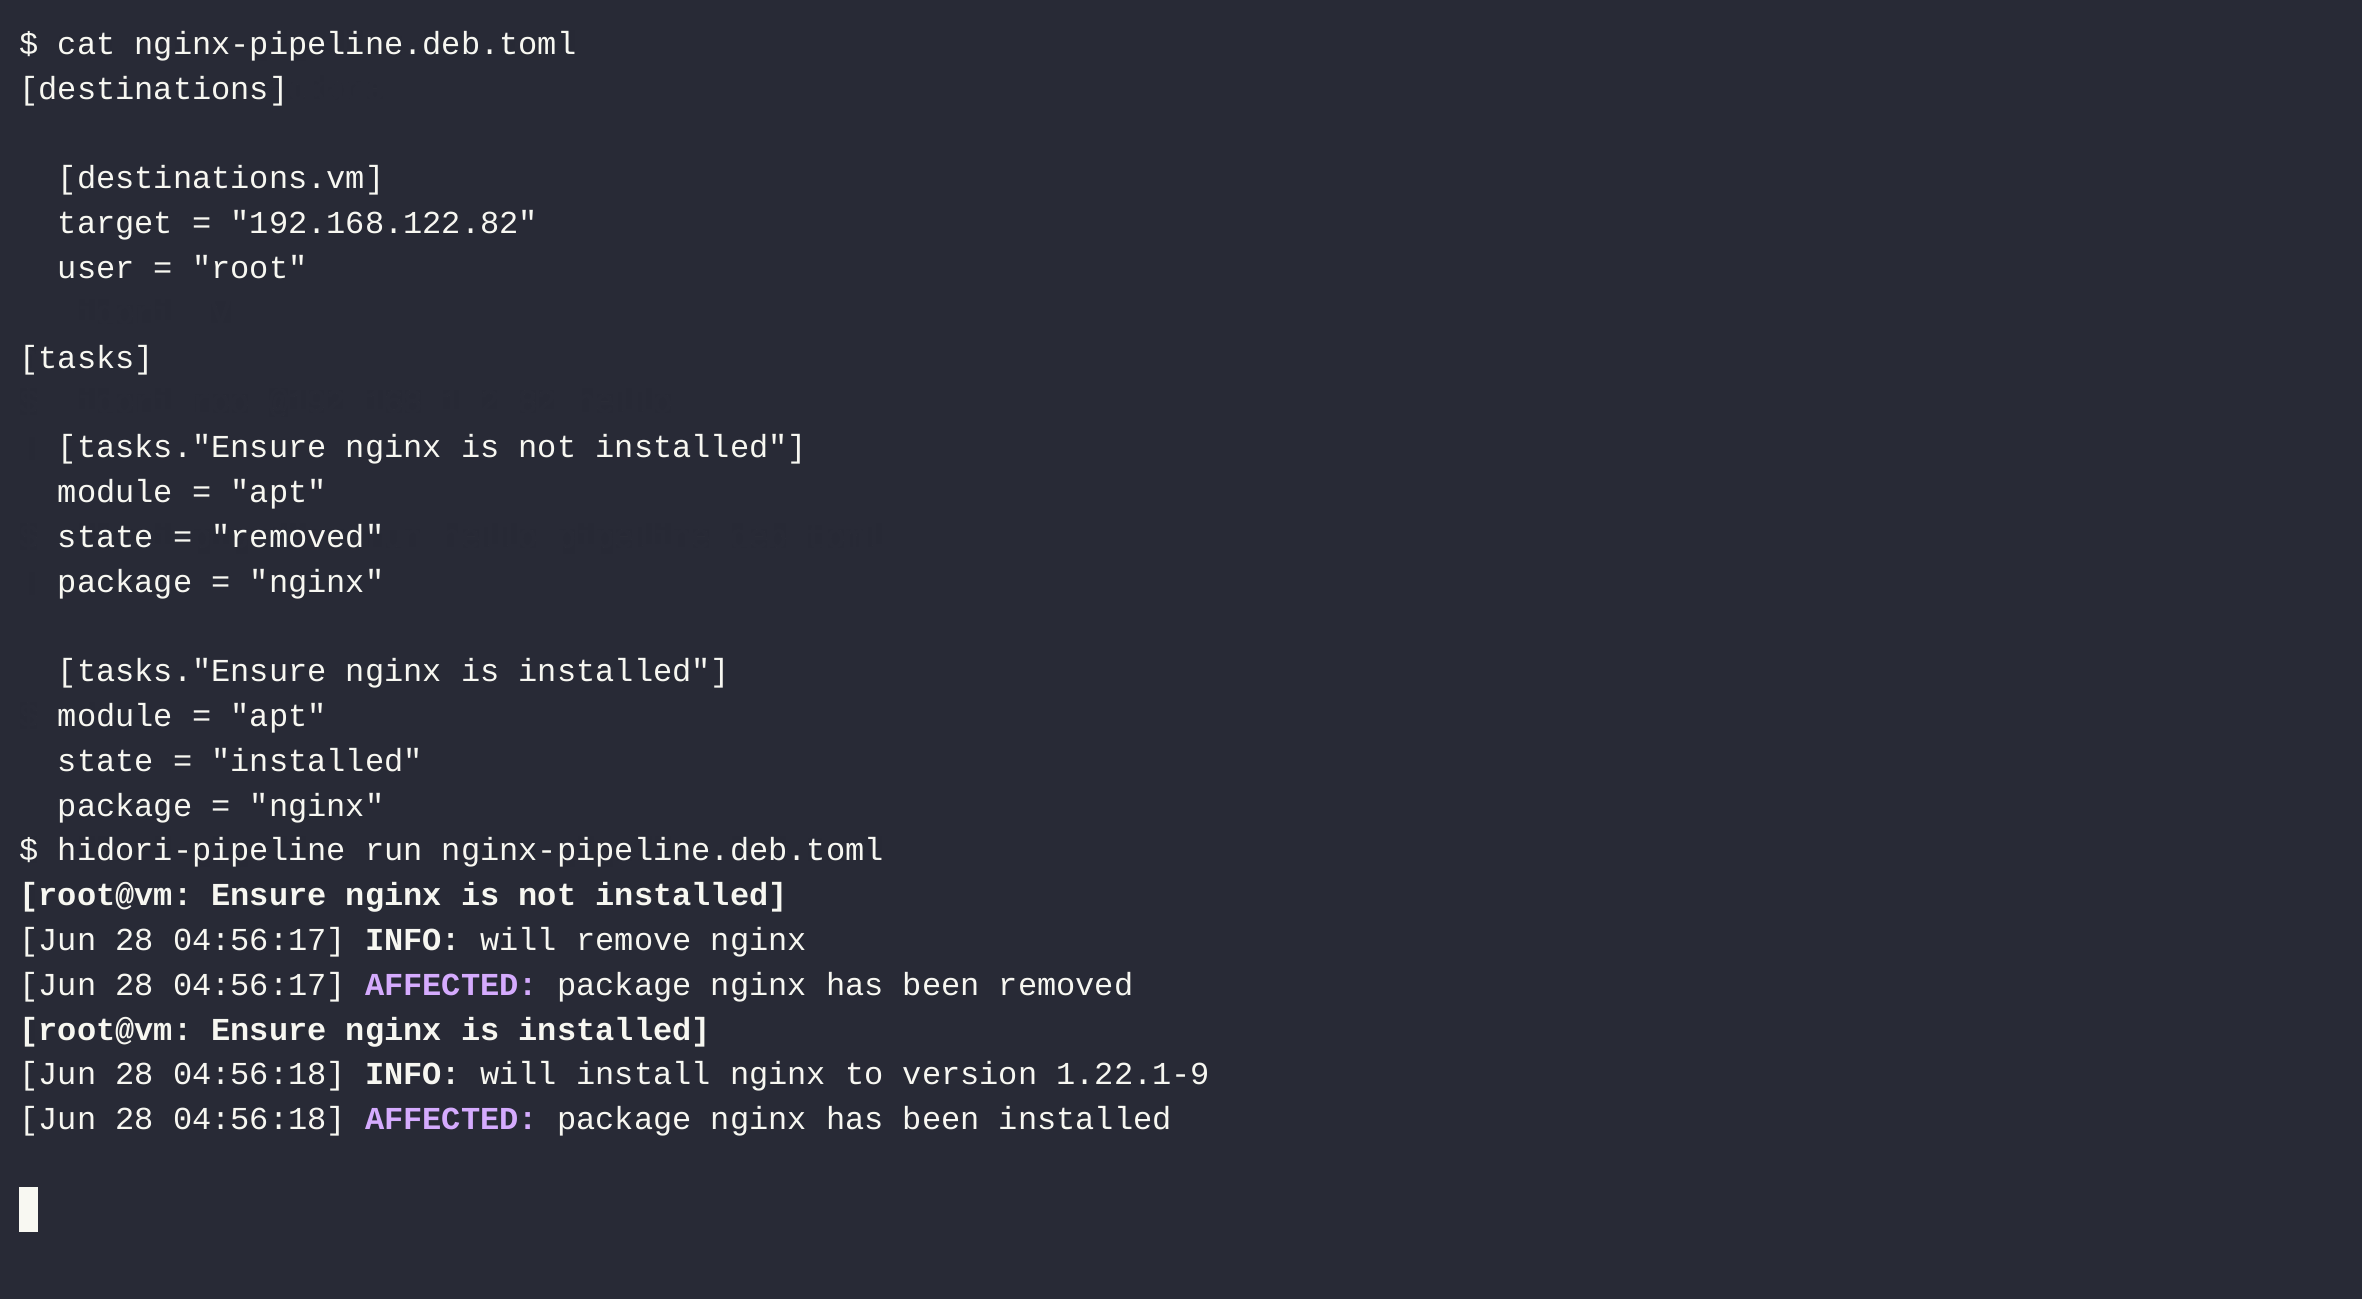
With Hidori installed you need a single TOML file that provides where and what should be done. A simple 'hello world' example assuming that some machine is available at the given target:
[destinations]

  [destinations.vm]
  target = "192.168.122.31"
  user = "root"

[tasks]

  [tasks."Say hello"]
  module = "hello"
Now you just need to run it (example assumes the file is named pipeline.toml):
hidori-pipeline run pipeline.toml
The result on my machine is:
[root@vm: Say hello]
[16:03:19] OK: Hello from Linux debian 4.19.0-21-amd64
Support
In general, Hidori is based on Python 3.11, but hidori_core runs with any version of Python that is still supported.
Reason for that is vast majority of destination systems don't have the latest Python runtime installed, so therefore hidori_core
which includes all the code that runs on a destination system can be expected to be supported according to the following table:
| Python Version | EOL Date |
|---|---|
| 3.8 | November 2024 |
| 3.9 | November 2025 |
| 3.10 | November 2026 |
| 3.11 | November 2027(?) |
Development
The dev environment can be setup with poetry:
poetry install
License
Hidori is licensed under both the MIT and the EUPL-1.2 licenses.
-
Except for the necessary runtime - python, and system libraries that are used by modules ↩
1 maintainer

Metadata
1 maintainer
Release files for hidori 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| hidori-0.3.0.tar.gz | 24.4 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| hidori-0.3.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 54.7 kB
Release files / hidori-0.3.0.tar.gz
| Download URL | hidori-0.3.0.tar.gz |
|---|---|
| Size | 24.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e2d1e93f338a1f43a5eadfd30a075a0019f03cc015fe3a64b4f93ad4a89ba19c
|
|
BLAKE2b-256 checksum How to use checksums |
120ece66c0ecda7c2f30270a1256a4fbe06a0bf2285d5ac99446f2c5b8f27b33
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.11.4
|
Release files / hidori-0.3.0-py3-none-any.whl
| Download URL | hidori-0.3.0-py3-none-any.whl |
|---|---|
| Size | 30.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ed48bed94635d70219ef1db0a70fd88cdc1c5895365d80d0d71394efde83f6ac
|
|
BLAKE2b-256 checksum How to use checksums |
63f1867a39a5ffcce53f2cd7a148bfe27e99ae48bb9397259d90e87113ee532c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.11.4
|
Security for hidori 0.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














