
Monkey patch for HuggingFace Hub to download Git-LFS blobs from Storj
This patch aims to demonstrate the transfer speed that can be achieved with huggingface_hub Python library when utilizing the power of the Storj Decentralized Cloud Storage.
HuggingFace Hub stores all large files in Git-LFS.
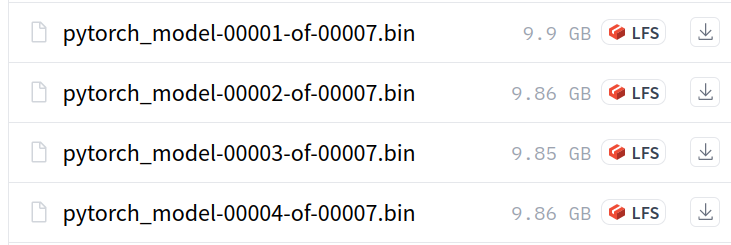
When the huggingface_hub Python library requests to download such a file, the download request is redirected to the Git-LFS CDN hosted at cdn-lfs.huggingface.co.
This monkey patch modifies the huggingface_hub library to redirect Git-LFS downloads to the Storj Linksharing service hosted at link.storjshare.io.
Prerequisites
The Git-LFS blobs for the respective AI model must be replicated to a Storj bucket and shared it with the Storj Linksharing Service.
We have already replicated the Git-FLS blobs of the StarCoder model to a Storj bucket and shared it: https://link.storjshare.io/raw/juzlwaj7ovnst5gtkv2km3rkriha/lfs-huggingface
If you want to use another AI model, you need to use your own Storj bucket and then configure the patch to use it. See Configuration for more details.
Installation
First, install the patch module:
pip install huggingface-hub-storj-patch
Then add the following import statement at the top, before any other import, of your Python script:
import huggingface_hub_storj_patch
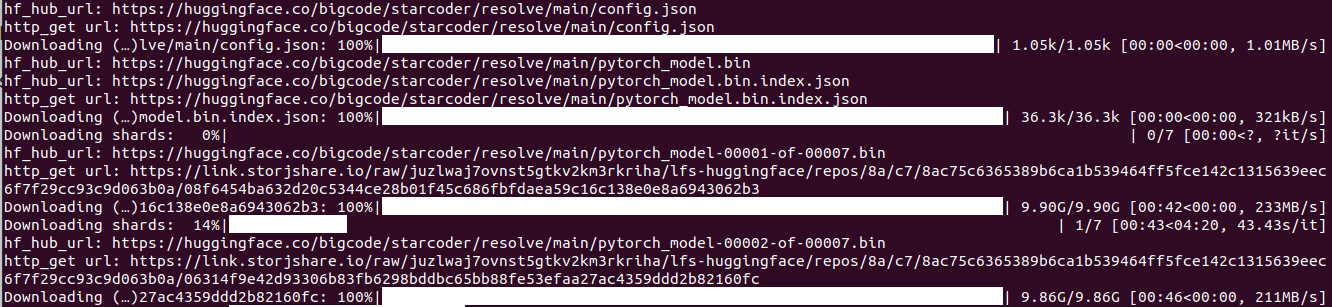
Now you can run your script. If the patch is applied successfully, you will see it printing the URLs from which the huggingface_hub library is downloading.
Configuration
These environment variables can configure the behavior of the patch.
HF_HUB_NO_STORJ
If set to true, downloads won't be redirected to the Storj Linksharing Service as if the patch is not applied.
HF_HUB_STORJ_PARALLELISM
Configures how many parallel download connections are open to the Storj Linksharing Service. The default value is 16.
HF_HUB_STORJ_URL_PREFIX
Configures the URL to the shared Storj bucket that replicates the Git-LFS blobs of the AI model. The default value is the bucket that replicates the StarCoder model: https://link.storjshare.io/raw/juzlwaj7ovnst5gtkv2km3rkriha/lfs-huggingface
1 maintainer

Metadata
1 maintainer
Release files for huggingface-hub-storj-patch 0.0.6
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| huggingface_hub_storj_patch-0.0.6.tar.gz | 8.3 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| huggingface_hub_storj_patch-0.0.6-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 17.0 kB
Release files / huggingface_hub_storj_patch-0.0.6.tar.gz
| Download URL | huggingface_hub_storj_patch-0.0.6.tar.gz |
|---|---|
| Size | 8.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5da5c0ffe5bffe9d9745a7534da493a7d6a6033e2ca849d83c32b1b795b09cf7
|
|
BLAKE2b-256 checksum How to use checksums |
94739fc2b2ae0298aa8ba0ef396416dc525df74b2f1696b410b66d0183e678da
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.10.6
|
Release files / huggingface_hub_storj_patch-0.0.6-py3-none-any.whl
| Download URL | huggingface_hub_storj_patch-0.0.6-py3-none-any.whl |
|---|---|
| Size | 8.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
657c5a450673d6c04ec58d028901024323fbddb8dfd797cb00076841581ef125
|
|
BLAKE2b-256 checksum How to use checksums |
a195bd9663e71e10f26f8d588a05177efb0d2236a3f3030c123b2717ccdb3496
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.10.6
|
Security for huggingface-hub-storj-patch 0.0.6
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













