
ilmers_corner

A CLI for browsing and generating hashpins for GitHub Actions.
Install
pip install ilmers_corner
Usage
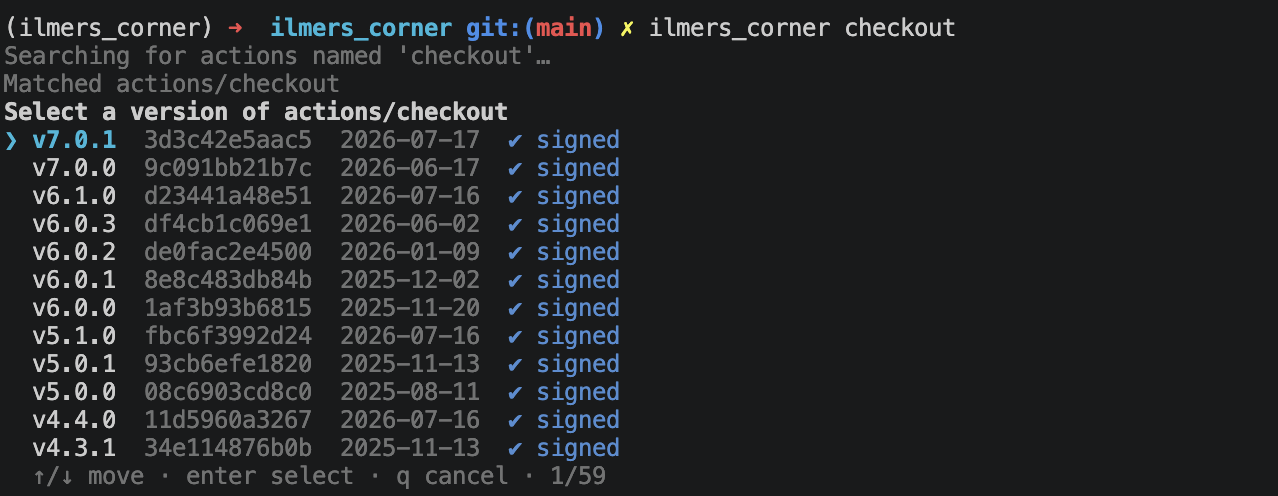
ilmers_corner checkout                # search by name
ilmers_corner actions/checkout        # exact repository, opens the picker
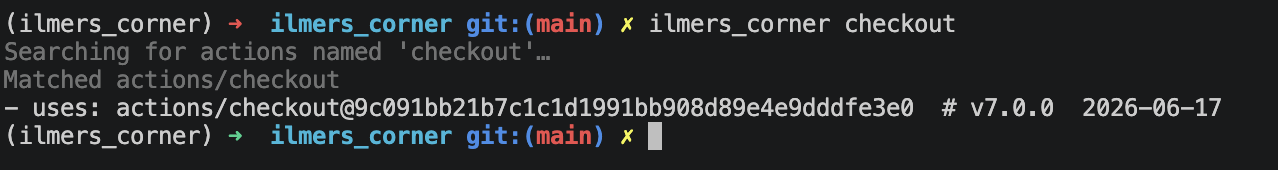
ilmers_corner actions/checkout@v4     # pin the latest v4.x.y, no prompt
ilmers_corner actions/checkout@v4.2.2 # pin that exact version
Browsing:
Result:
Options
| Flag | Effect |
|---|---|
--pre |
include prereleases (rc, beta, alpha) |
--major-tags |
include floating tags like v4, marked moving tag |
--limit N |
maximum tags to fetch (default 100) |
--token |
GitHub token (defaults to $GITHUB_TOKEN) |
--no-advisories |
skip the security advisory lookup (saves one request) |
--clear-cache |
delete cached API responses |
Rate limits
Unauthenticated GitHub allows 60 requests/hour, and only 10/hour for search. Two things keep that workable:
- Passing an exact
owner/nameskips search entirely, so the scarce search quota is only spent on genuine name lookups. - Responses are cached on disk. Repeat lookups cost zero requests.
For heavier use, set a token to raise the limit to 5000/hour:
export GITHUB_TOKEN=ghp_...
Notes on correctness
Dates come from the commit, not the release. GitHub's published_at records
when the release entry was written, which can be rewritten in bulk — as of this
writing actions/checkout reports v7.0.1 and v3.7.0 as published six minutes
apart. The commit date is the one that reflects reality.
SHAs come from the /tags endpoint, which returns the dereferenced commit even
for annotated tags. Reading git/ref/tags/... instead would return the tag
object's own SHA, which GitHub Actions cannot resolve when pinned.
Why does this exist?
Great tools like pinact exist that automates the process of hashpinning Actions in workflow files. This tool offers something in cases where:
- The hashpin is needed outside of workflow files.
- The developer wants to browse versions and release dates.
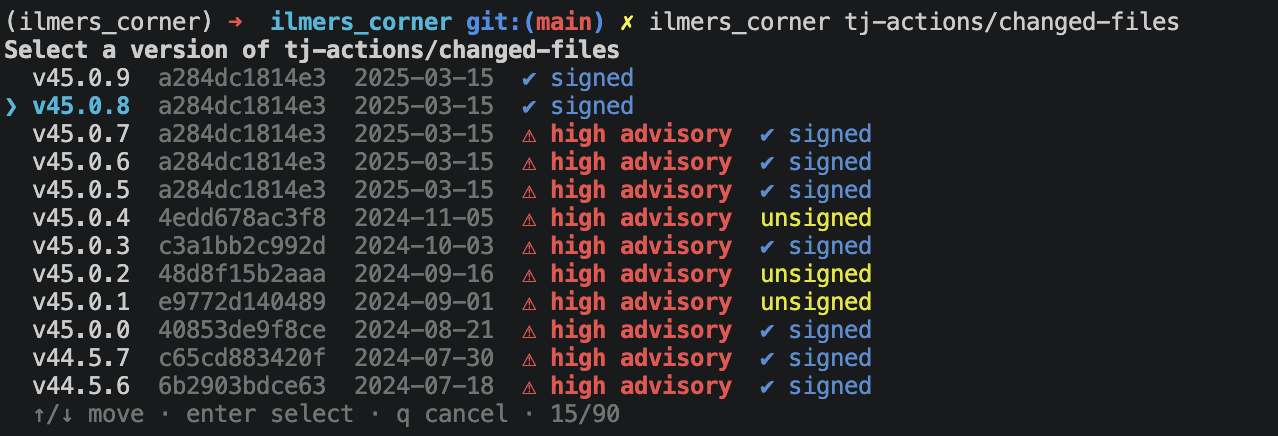
- The developer wants to check out security signals (verified signatures, advisories from GitHub Advisory Database).
Example of the last use case with the famous supply chain compromised tj-actions/changed-files in March 2025:
1 maintainer

Metadata
1 maintainer
Release files for ilmers-corner 0.1.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| ilmers_corner-0.1.2.tar.gz | 376.5 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| ilmers_corner-0.1.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 394.9 kB
Release files / ilmers_corner-0.1.2.tar.gz
| Download URL | ilmers_corner-0.1.2.tar.gz |
|---|---|
| Size | 376.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
be94e81e82c9594944049924cdbcde43d999cf924487647ed8256222f7fb5622
|
|
BLAKE2b-256 checksum How to use checksums |
9e02133bbf3a2b37495bbd832b7199cde91a6af1ee80cfe599b6be49f02c4a3e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 8, 2026.
Transparency logRelease files / ilmers_corner-0.1.2-py3-none-any.whl
| Download URL | ilmers_corner-0.1.2-py3-none-any.whl |
|---|---|
| Size | 18.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f11e0aece83eef204ab84e20caf7709ac92f12a954db7233a2e03e6d337354e9
|
|
BLAKE2b-256 checksum How to use checksums |
15d2a17167d93c3436215b1fefee82b14d3f3a0ee852f007fb47dc77d5829e9f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 8, 2026.
Transparency logSecurity for ilmers-corner 0.1.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for ilmers_corner-0.1.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 8, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














