




A high-performance a Polars plugin written in Rust with python bindings for fast and memory efficient reading of Avro files into DataFrames.
Jetliner is designed for data pipelines where Avro files live on S3 or local disk and need to land in Polars fast. It streams data block-by-block rather than loading entire files into memory, uses zero-copy techniques, and has (almost) complete support for the Avro spec (see Known Limitations).
Features
- High-performance streaming — Supports block-by-block processing with minimal memory footprint, ideal for large files
- Idiomatic polars integration — Feels like a Polars native API
- Query optimization — Projection pushdown (select columns) and predicate pushdown (filter rows) at the source via Polars LazyFrames
- S3 and local file support — Read Avro files from Amazon S3 or local disk with the same API, including glob patterns
- All standard codecs — null, snappy, deflate, zstd, bzip2, and xz compression out of the box
- (Almost) complete avro schema support — reads almost any valid avro (see limitations)
- Flexible error handling — Optionally skip bad blocks for resilience to data corruption
- Ridiculously fast reads — Check the benchmarks!
This library was created to serve performance critical scenarios around processing large avro files from python. It's fast but limited to read use cases. If you also need to write avro files from Polars then you should check polars-avro.
Performance benchmarks
Jetliner is built for speed, and significantly outperforms the alternatives. Yes, that's a log scale.
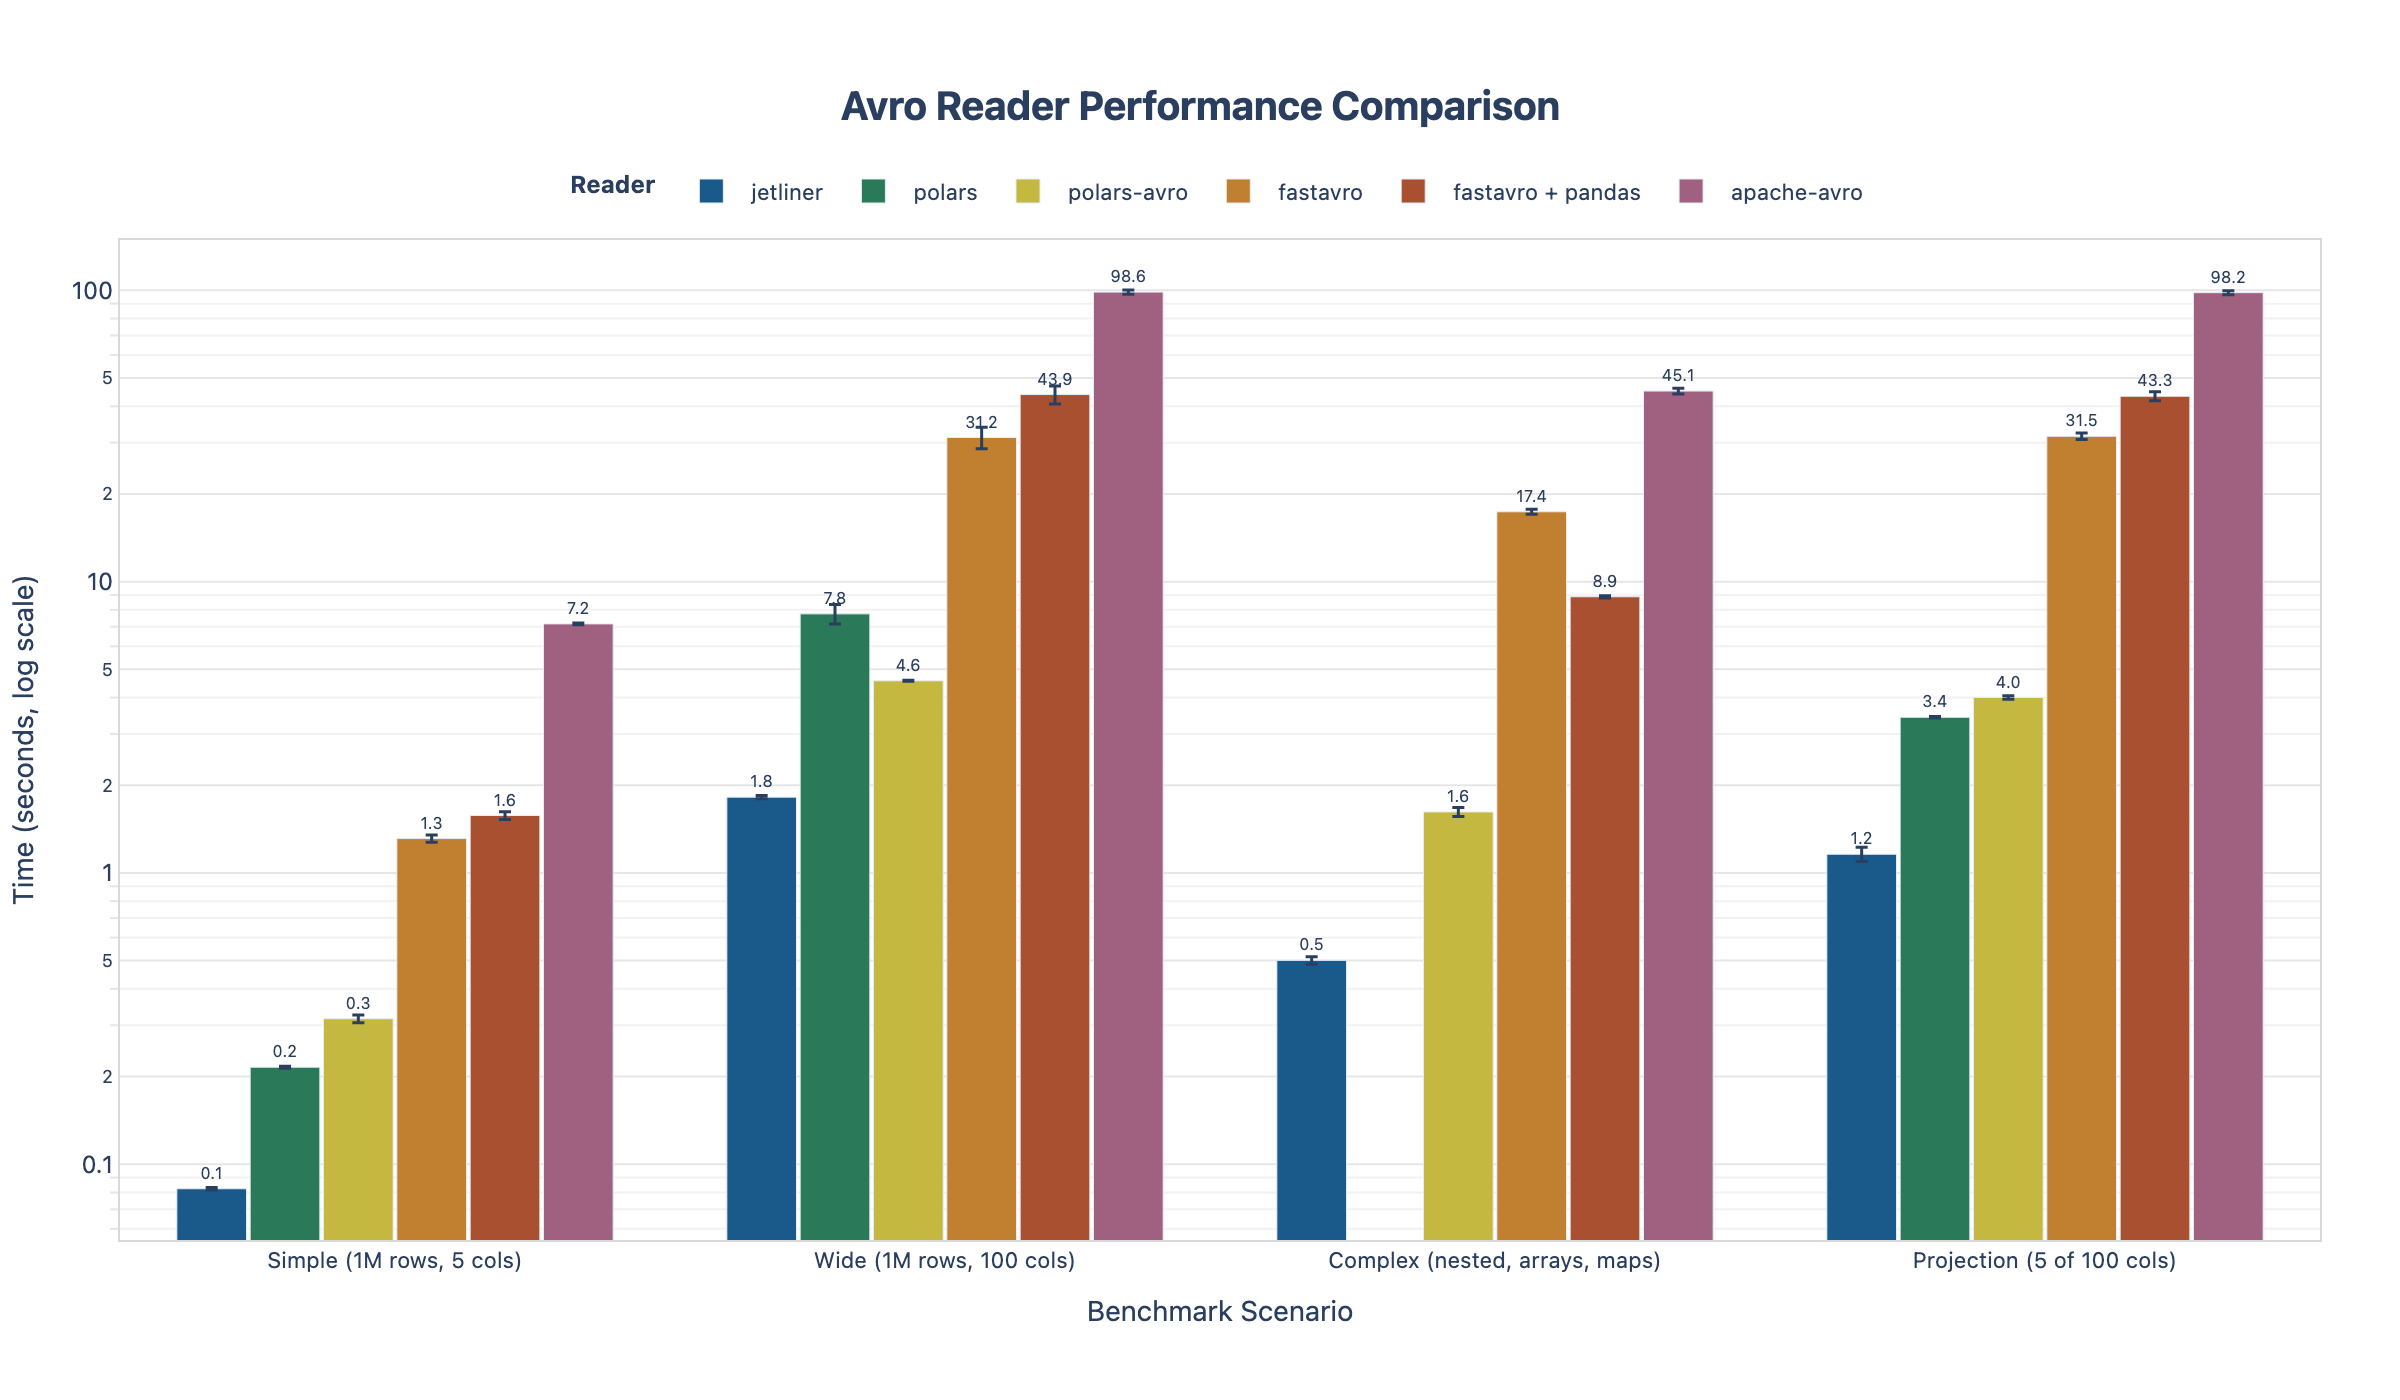
The chart compares read times across four scenarios using 1M-row Avro files. Note that Polars' built-in Avro reader is missing from the "Complex" all the complex field types.
Installation
Install from PyPI using pip or your favorite python dependency manager:
pip install jetliner
Quick Start
Lazy Reading with Query Optimization
Use scan_avro() for the best performance — Polars pushes projections and predicates down to the reader:
import jetliner
import polars as pl

df = (
    jetliner.scan_avro("s3://bucket/events/*.avro")
    .select("user_id", "event_type", "timestamp") # Only these columns are loaded
    .filter(pl.col("event_type") == "purchase")   # Filter rows as they're loaded
    .head(10_000)                                 # Stops reading after 10k matches
    .collect()
)
Eager Reading with Column Selection
Use read_avro() when you want a DataFrame immediately:
df = jetliner.read_avro("data.avro", columns=["id", "name"], n_rows=1000)
Streaming Iteration
Use AvroReader or MultiAvroReader for batch-by-batch control — useful for progress tracking, memory management, or custom pipelines:
for batch in jetliner.AvroReader("huge_file.avro", batch_size=50_000):
    process(batch)  # each batch is a DataFrame

# MultiAvroReader handles multiple files with continuous row indexing
reader = jetliner.MultiAvroReader(
    ["file1.avro", "file2.avro"],
    row_index_name="idx",           # Continuous index across files
    include_file_paths="source",    # Track which file each row came from
)
for batch in reader:
    process(batch)
Schema Inspection
Inspect the schema without reading data:
schema = jetliner.read_avro_schema("data.avro")
print(schema)  # Polars Schema showing column names and types
Reading from S3 and Local Files
All APIs work with local paths, S3 URIs, and glob patterns:
# Local files
df = jetliner.read_avro("./data/events.avro")
df = jetliner.read_avro("./data/**/*.avro")  # Recursive glob

# S3 (credentials from environment or explicit)
df = jetliner.read_avro("s3://bucket/path/to/file.avro")
df = jetliner.read_avro(
    "s3://bucket/data/*.avro",
    storage_options={
        "endpoint": "http://localhost:9000",  # MinIO, LocalStack, R2
        "aws_access_key_id": "...",
        "aws_secret_access_key": "...",
    }
)
Error Recovery
Skip corrupted blocks instead of failing — errors are collected for inspection:
reader = jetliner.AvroReader("suspect_file.avro", ignore_errors=True)
for batch in reader:
    process(batch)

if reader.error_count > 0:
    print(f"Skipped {reader.error_count} bad blocks")
    for err in reader.errors:
        print(f"  Block {err.block_index}: {err.message}")
Performance Tuning
Fine-tune for your workload:
df = jetliner.scan_avro(
    "s3://bucket/data/*.avro",
    batch_size=100_000,        # Rows per batch (default: 100k)
    buffer_blocks=8,           # Prefetch buffer depth (default: 4)
    buffer_bytes=128*1024*1024,# Prefetch buffer size (default: 64MB)
    read_chunk_size=8*1024*1024,# S3 read chunks (default: 4MB for S3)
).collect()
Development
The project uses spec driven development via kiro. See ./.kiro for the specs and related documentation.
Project tasks
This project uses poethepoet for task management.
# Install poe globally with homebrew
brew tap nat-n/poethepoet
brew install nat-n/poethepoet/poethepoet
# Or with uv/pip/pipx
uv tool install poethepoet
# run poe without arguments to list available tasks, defined in pyproject.toml
poe
There are tasks available for formatting, linting, building, and testing. The check task orchestrated all tasks that must complete successfully for a change to be accepted.
Running tests
poe test-rust # run rust unit tests
poe test-python # run python e2e tests
Known Limitations
Read-Only
Jetliner is a read-only library. It does not support writing Avro files.
Avro object container files only
Jetliner reads Avro Object Container Files (.avro) — self-contained files where the schema is embedded in the file header. It does not support:
- Single-object encoding — Used with schema registries (e.g., Confluent Schema Registry, Kafka). These encode objects with a schema fingerprint that requires external lookup.
- Bare Avro encoding — Raw Avro binary without any schema information.
- Standalone schema files (
.avsc) — Schema JSON files are not read directly; schemas are extracted from.avrofile headers.
Recursive types
Avro supports recursive types (e.g., linked lists, trees) where a record can contain references to itself. Since Arrow and Polars don't natively support recursive data structures, Jetliner serializes recursive fields to JSON strings. This preserves data integrity while maintaining compatibility with the Polars DataFrame model.
Example: A binary tree node with left and right children will have those fields serialized as JSON strings that can be parsed if needed after reading.
Complex top-level schemas
Avro is usually used as a table format, with a Record as the top level type. However it may also be used with any other type at the top level.
Jetliner support primitive top level schemas (int, long, string, bytes) which are treated in the resulting polars Dataframe as a Record with a single 'value' key. However complex types have the following limitations:
- Arrays as top-level schema: Not yet supported (Polars list builder constraints)
- Maps as top-level schema: Not yet supported (struct handling in list builder)
Empty schemas
An avro schema may consist of a Record with zero fields. Since Polars cannot represent a DataFrame with zero columns, such avro files are no compatible with Jetliner.
Trivia
- The Avro Canada C102 Jetliner was the worlds second purpose built jet powered airliner.
Contributing
If you encounter an issue or have an idea for how to make jetliner more awesome, do come say hi in the issues 👋
If you discover an avro file that other libraries can read but jetliner fails (for reasons other than Known Limitation) then please share it.
License
Licensed under the Apache License, Version 2.0. See LICENSE for details.
1 maintainer

Metadata
1 maintainer
Release files for jetliner 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| jetliner-0.2.0.tar.gz | 1.7 MB | With provenance | Details |
Built distributions (wheels)
Total release size: 661.9 MB
Release files / jetliner-0.2.0.tar.gz
| Download URL | jetliner-0.2.0.tar.gz |
|---|---|
| Size | 1.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
4dda63e83adc1fe7884ce6a3394509d7c78deedded74c97c7fb66329e00d0ca1
|
|
BLAKE2b-256 checksum How to use checksums |
e1eb09b73bb4d5760ea7e44c9248a0cb7aad150c49067cf0280f4851bf6dbdf4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-pp311-pypy311_pp73-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-pp311-pypy311_pp73-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | Linux musl 1.2+ x86-64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
e6f3b56b5e5c67078c9b529ec805119b4335e1e00864b2f220f87c4b5938e27b
|
|
BLAKE2b-256 checksum How to use checksums |
651180e407b549d7bc2402b3487606e51e8223cf2a237a61dbdf4a5900adbcd9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-pp311-pypy311_pp73-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-pp311-pypy311_pp73-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | Linux musl 1.2+ ARM64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
c99c3bc992176bc3e798a1d68c5b430282ddc3268287e29e2ef75b3b13c22688
|
|
BLAKE2b-256 checksum How to use checksums |
91db64f38f52ffc9556a512f215cc8f478fd6eabdc30036483e445b73d96f029
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-pp311-pypy311_pp73-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | jetliner-0.2.0-pp311-pypy311_pp73-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | Linux glibc 2.17+ x86-64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
9a087b511f874a341649e52995df1820d77a512b2371fff4e453a8a2f45fe2a6
|
|
BLAKE2b-256 checksum How to use checksums |
d4b745d1c5896ca08e8ab312819c9840cd755ddb9d1e0b99377baa793a506e94
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-pp311-pypy311_pp73-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | jetliner-0.2.0-pp311-pypy311_pp73-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 15.0 MB |
| Tags | Linux glibc 2.17+ ARM64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
7276e67a65ae03b9a0258ea754c6e9600ffda50fecfa7a3e6419a63289330270
|
|
BLAKE2b-256 checksum How to use checksums |
0ffb84e3d11a36d3158a66a4498be6e00dde4a284b07714593c00955631d0cda
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-pp310-pypy310_pp73-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-pp310-pypy310_pp73-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | Linux musl 1.2+ x86-64 PyPy 3.10 PyPy 3.10 7.3 |
|
SHA-256 checksum How to use checksums |
7cdbaf12aedb9c1ae86fc4e9e1da326957d20c642f9cb225803aa6727e54c5d3
|
|
BLAKE2b-256 checksum How to use checksums |
4ea8f603c014a8f845f97cbe95e7797f74d1b5db89a9033acb138ac762f0b55a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-pp310-pypy310_pp73-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-pp310-pypy310_pp73-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | Linux musl 1.2+ ARM64 PyPy 3.10 PyPy 3.10 7.3 |
|
SHA-256 checksum How to use checksums |
3f7e9f95d9d59677bbeb76dc7bc486a675d59aafd6f985e4c74ca51ef34e512a
|
|
BLAKE2b-256 checksum How to use checksums |
1a0f4367fff67816ce36acdc9d83ad97f112fff7f0d1987e178275537c9ddb06
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314t-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-cp314-cp314t-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | CPython 3.14 CPython 3.14 free-threading Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
329804184e1e7ecb324bd7f19abfce3121e6aec7c16c2808556c0ab21a8b7824
|
|
BLAKE2b-256 checksum How to use checksums |
8a41e7dbca38e5ce3c95ea38517413738d18949897faa80759ac58e7925ad74b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314t-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-cp314-cp314t-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.14 CPython 3.14 free-threading Linux musl 1.2+ ARM64 |
|
SHA-256 checksum How to use checksums |
32427b0739946bb333f1389af1680663393c36db55c33d2aa2a429ded75b7849
|
|
BLAKE2b-256 checksum How to use checksums |
eee3c12b36a757369792819fd57d283c75dd9dc167d1fb55096ba019a4898af0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314-win_amd64.whl
| Download URL | jetliner-0.2.0-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 12.8 MB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
84756cc95c326e1dfcee008fc02f7464e1cac2f2a3b40bc12e2fe15d5c3db241
|
|
BLAKE2b-256 checksum How to use checksums |
e338f683e8c138d5ef4322f7e7dbcc5645920d4ed4e41281bbc13d123b45544b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-cp314-cp314-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | CPython 3.14 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
c341ff266db26364468621cab63e18e91c2c731f0680bbd8e1fb7dbcee215fc8
|
|
BLAKE2b-256 checksum How to use checksums |
3c1b24a80d583720f6783f06d7348ab736be2183b7e606aa10cb3001b80a4f7b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-cp314-cp314-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.14 Linux musl 1.2+ ARM64 |
|
SHA-256 checksum How to use checksums |
6248449b1b953fda8e63b55c29bc0e110e9733d9d8aef20b3a801ae211efe2f3
|
|
BLAKE2b-256 checksum How to use checksums |
5597e07eea95a4de8b3479b8c3fa10e5ec41c37ac7bbfadcf79197008b1e2bb0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | jetliner-0.2.0-cp314-cp314-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.14 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
eceff36452c4dc87d44c5e66225d800e36d3ef93bd951dfde2e9295f4561e533
|
|
BLAKE2b-256 checksum How to use checksums |
439b35122559302b08031f5611d013cd3b91246198afc3b98c433b185a6402be
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | jetliner-0.2.0-cp314-cp314-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 15.0 MB |
| Tags | CPython 3.14 Linux glibc 2.17+ ARM64 |
|
SHA-256 checksum How to use checksums |
264855489eeba1e4968f75d14eeb0d903522151ebced7d895fa4d7da07d40ee1
|
|
BLAKE2b-256 checksum How to use checksums |
b9d2cd9942e9d97d3b1c33c9425efa3f15991c217d7ec462f8e82c213396e086
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314-macosx_11_0_arm64.whl
| Download URL | jetliner-0.2.0-cp314-cp314-macosx_11_0_arm64.whl |
|---|---|
| Size | 13.1 MB |
| Tags | CPython 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
c3fbff1f80843132f5ed7f04163202343085e8f56b70ce6b5f6903a4cd98af7a
|
|
BLAKE2b-256 checksum How to use checksums |
69a71888934eb2cc6614d0e376e98ec4e50fbd00713f465e639ddfc5292d39a3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp314-cp314-macosx_10_12_x86_64.whl
| Download URL | jetliner-0.2.0-cp314-cp314-macosx_10_12_x86_64.whl |
|---|---|
| Size | 14.3 MB |
| Tags | CPython 3.14 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
982327f88645b9e54660869e0864869c01ff2bdafc377abd83ac1b61af362869
|
|
BLAKE2b-256 checksum How to use checksums |
138ad4cf4302e083abe615c0463961501190457786c1f61409349d7a81dd7edb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313t-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-cp313-cp313t-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | CPython 3.13 CPython 3.13 free-threading Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
91e0ca0f6d9158a377b47c71e0457a130090057f39d45c14518993fe1fc489c0
|
|
BLAKE2b-256 checksum How to use checksums |
541621851d4930ed5aa2c749aa96a92d0252d89f0b823b641c061105dd6affa2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313t-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-cp313-cp313t-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.13 CPython 3.13 free-threading Linux musl 1.2+ ARM64 |
|
SHA-256 checksum How to use checksums |
097ac5ef832a98dfff9770845d644ebe46ccc094c9c745339621c7a69cee5a45
|
|
BLAKE2b-256 checksum How to use checksums |
ae8b432c909c8d01811e596a2bd553044c87d6bd618c85442f4aea788101e91d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313-win_amd64.whl
| Download URL | jetliner-0.2.0-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 12.8 MB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
e40d35f27ff3e84a97497de8ee78131389f7944ee0c1399516671a4555fb636f
|
|
BLAKE2b-256 checksum How to use checksums |
2a82ad3419c4fa407a2e6d0efd757032a2a31eebd1eeed144ee0fe41742071ea
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-cp313-cp313-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | CPython 3.13 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
b4c08b007b9b8684f598650a0456ae336e50f372165fbb2ebcb6386228646f4c
|
|
BLAKE2b-256 checksum How to use checksums |
a523f05fca7da32e35e2a3b7bfc5c59823429ed6aa1e07ba96be70309f9e39e7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-cp313-cp313-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.13 Linux musl 1.2+ ARM64 |
|
SHA-256 checksum How to use checksums |
397ea85b7f5a9e18a733971c36583a5410e3f32b5c462d09cc2b691c086e710d
|
|
BLAKE2b-256 checksum How to use checksums |
f296cb4e6857f105855226dcb0f5ed15b8a933502f01578e36c9ecf0ccddff5c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | jetliner-0.2.0-cp313-cp313-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.13 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
25e92fa69c28f5b2b012e96de2858f84ef1d006f2c2f6290f7641fab96813f58
|
|
BLAKE2b-256 checksum How to use checksums |
bcb3ad5e09cf71697b998e8b6119dcbb2a1e2d5e720dec6be72d2abcfa6b1576
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | jetliner-0.2.0-cp313-cp313-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 15.0 MB |
| Tags | CPython 3.13 Linux glibc 2.17+ ARM64 |
|
SHA-256 checksum How to use checksums |
53b5c34e535f728a3b1a5d85e1922707f3cb0b77b381918c453c3ee006d5dcad
|
|
BLAKE2b-256 checksum How to use checksums |
810a635257b2e685900bba4080b7359d46694ce7dda7315bf3282d643324acd1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | jetliner-0.2.0-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 13.1 MB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
04cfc2b8b56f8a07f8a64d34ce7e9dde94b5edad0568b50e08a61c6c3cd1460a
|
|
BLAKE2b-256 checksum How to use checksums |
c316882b5edebf04511f8557606f298daaeff35408a8db343b0c5de28a4569e8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp313-cp313-macosx_10_12_x86_64.whl
| Download URL | jetliner-0.2.0-cp313-cp313-macosx_10_12_x86_64.whl |
|---|---|
| Size | 14.3 MB |
| Tags | CPython 3.13 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
2d294439f19dbec9faebbce5cb0ce7660df9c113936454191ba9df1a2a18b6b2
|
|
BLAKE2b-256 checksum How to use checksums |
2701bb58bbdc3a6c46d14c100f3ffd6deb1f148eb5eb2128db7bfb88367679dc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp312-cp312-win_amd64.whl
| Download URL | jetliner-0.2.0-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 12.8 MB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
69ecf00e3f411e656978ad1b9b0a30f940cbc270a1495f987770eeff5030e5ab
|
|
BLAKE2b-256 checksum How to use checksums |
401b66451b7a79351da0b76919c7315b5b36bd93c27c3ba1877f39faa54e7ca9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp312-cp312-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-cp312-cp312-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | CPython 3.12 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
b3b9ba232508b5000a7eb1b0ab76fd6a8da574dfff688189a3efddef55cce017
|
|
BLAKE2b-256 checksum How to use checksums |
193e5fef1ca8a5b0acb03a824491349cbe4f8070587edd22575452809ef1c037
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp312-cp312-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-cp312-cp312-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.12 Linux musl 1.2+ ARM64 |
|
SHA-256 checksum How to use checksums |
7c689cdfb0504e96662b4ca20ee267b3ae275a945552eda9aa5480d0e9402394
|
|
BLAKE2b-256 checksum How to use checksums |
ed9808ce2a6bafd2faaccd88ecffe38fa31e2eb609fe3306bc01509b5d3bc7cd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp312-cp312-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | jetliner-0.2.0-cp312-cp312-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
ff4cdb7475f125123489209ae427f4b7063f7726a691fb8781c382f2f5b6d1d4
|
|
BLAKE2b-256 checksum How to use checksums |
beb34242957326320a04fc63872507b99d3bb01ef3de1db4bb526dd30839e50a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp312-cp312-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | jetliner-0.2.0-cp312-cp312-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 15.0 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ ARM64 |
|
SHA-256 checksum How to use checksums |
b500210faf1e99db4c3225bb550f4bbd9aa5d3def961fa2797ff221ebcf5dee1
|
|
BLAKE2b-256 checksum How to use checksums |
4f9f7fa23d3eeb4ea9fc56fd2c0b5dff69c848e912c5edd82dbfa6eb59dd3ab1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | jetliner-0.2.0-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 13.1 MB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
9b3300f9518e950d2aa2385f8885a94606fae833ade52efdd501afc52ca76a3f
|
|
BLAKE2b-256 checksum How to use checksums |
d1c51e194775f3dde58fff033991bf2e74e5a526f8d1e254fd182cae43d05e5f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp312-cp312-macosx_10_12_x86_64.whl
| Download URL | jetliner-0.2.0-cp312-cp312-macosx_10_12_x86_64.whl |
|---|---|
| Size | 14.3 MB |
| Tags | CPython 3.12 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
f3889659eef36894fe9391f1f0f845d757cfd1b76a4eb965cf89674e2cbbe922
|
|
BLAKE2b-256 checksum How to use checksums |
878005014d1a53705f279e6debe9b1a00bbc7ae422054e67d6c85a3d3e7bd4b0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp311-cp311-win_amd64.whl
| Download URL | jetliner-0.2.0-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 12.9 MB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
650907455a2fd619dc535081b7874a699f503cdac2b9f8dfcd1b5e778d9a8f00
|
|
BLAKE2b-256 checksum How to use checksums |
7e6d89647234e004b82d263b7421e6dd57d783a47ae6465adcd44d7088aa9923
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp311-cp311-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-cp311-cp311-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | CPython 3.11 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
e4c08ee4ec1c3fc4bb9183cffcc5a13e3441c319093108259ec87c108b445041
|
|
BLAKE2b-256 checksum How to use checksums |
2f8443905cdb69f452d499b3d21c343daa161b331eef3007d841bed048f0487c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp311-cp311-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-cp311-cp311-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.11 Linux musl 1.2+ ARM64 |
|
SHA-256 checksum How to use checksums |
19d5e3a1bdb880bd86a64ffb89f51f46df1a3e734ac7d8a2f8a3fa1b42f8363b
|
|
BLAKE2b-256 checksum How to use checksums |
8a206c4c83b8ec3e6d1908dab5f7606b943b9be8deb17aabbfeec908b36abcc8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp311-cp311-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | jetliner-0.2.0-cp311-cp311-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
afeef8918fc873e7b11e2ad10cc4dd3cf60c1252590196640d33572d430e9174
|
|
BLAKE2b-256 checksum How to use checksums |
a8e132810edfc336816b9c09f904ad485c1ef3d36193153962f42281e34430e1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp311-cp311-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | jetliner-0.2.0-cp311-cp311-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 15.0 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ ARM64 |
|
SHA-256 checksum How to use checksums |
8b59c5a4883ca295f35961804431f08be7a810110e7bb5edb3a507545d7d7fad
|
|
BLAKE2b-256 checksum How to use checksums |
15d311d00d806f337c4fbbccd559fbf0d10909a4eab6f208926221e9f20a462a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | jetliner-0.2.0-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 13.1 MB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
7c4f26ff7d8b1ec67149a41c871b8b4c2a2b10ceb5be6725a4247b89f6d75fb0
|
|
BLAKE2b-256 checksum How to use checksums |
9e0f8988121682cb395045220ef6f0fdcaed063d584398c144e573456e35e961
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp311-cp311-macosx_10_12_x86_64.whl
| Download URL | jetliner-0.2.0-cp311-cp311-macosx_10_12_x86_64.whl |
|---|---|
| Size | 14.2 MB |
| Tags | CPython 3.11 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
92e6f85fbed8c02b9884d7df87516b40a552b3f7534de6a00cc440533473adfc
|
|
BLAKE2b-256 checksum How to use checksums |
41adaa5ef4bb3c6865d2591c85a97d0aa32bec6ddc0fcae5a8f0e25532a5b915
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp310-cp310-win_amd64.whl
| Download URL | jetliner-0.2.0-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 12.8 MB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
82b8e7df96b5aa277ae069c50f88f47a7ed62be343414ca140848851581bd5b5
|
|
BLAKE2b-256 checksum How to use checksums |
f2b6bb65e9459dcfbc984cfdc45037155012f0e01e434eeab6b5d616879b6335
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp310-cp310-musllinux_1_2_x86_64.whl
| Download URL | jetliner-0.2.0-cp310-cp310-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 15.7 MB |
| Tags | CPython 3.10 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
a54badc1b5b08f40509ed6601ebb5b243b1645b8bd930bdfe65cc9f7a3e4ebce
|
|
BLAKE2b-256 checksum How to use checksums |
8bfee91c8ba45905e6924cd16b65e0313f30b23ee734b5fdc59ba1814ff38760
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp310-cp310-musllinux_1_2_aarch64.whl
| Download URL | jetliner-0.2.0-cp310-cp310-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.10 Linux musl 1.2+ ARM64 |
|
SHA-256 checksum How to use checksums |
e417bed1039149f876e7fcca34469b8313cc98982cd2358102da7fb267b5cf51
|
|
BLAKE2b-256 checksum How to use checksums |
714b0607a818d5c769167e0541d2e899bc91de88e269b424067517e9c8a7acbf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp310-cp310-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | jetliner-0.2.0-cp310-cp310-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
76ea2d1b34004a69e19131a5a768575a85a42145b40b57f2d5f7ef571c833228
|
|
BLAKE2b-256 checksum How to use checksums |
0227830b20085317edf29d027a9a1920ac92be5b5a3493a5d977faead762953e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp310-cp310-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | jetliner-0.2.0-cp310-cp310-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 15.0 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ ARM64 |
|
SHA-256 checksum How to use checksums |
329f6152cfe1489e57140a06beec1d7f656aa84c524be633449e3f0e2e6f3efc
|
|
BLAKE2b-256 checksum How to use checksums |
522b2820c0b6fed86cc58738fc6abeda88c5312ca7dbb1c6eee80e37f99cddc8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp310-cp310-macosx_11_0_arm64.whl
| Download URL | jetliner-0.2.0-cp310-cp310-macosx_11_0_arm64.whl |
|---|---|
| Size | 13.1 MB |
| Tags | CPython 3.10 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b1e4b8d89cb030f3bfa995f02e5d0b331b086c193dcf55ca5a0d4d9f7d5034f1
|
|
BLAKE2b-256 checksum How to use checksums |
2dd64dfffba724bd884a29410d1e7dc2c05be1ce6129e74d9bd84b7c7ed3a47f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logRelease files / jetliner-0.2.0-cp310-cp310-macosx_10_12_x86_64.whl
| Download URL | jetliner-0.2.0-cp310-cp310-macosx_10_12_x86_64.whl |
|---|---|
| Size | 14.2 MB |
| Tags | CPython 3.10 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
75c1a7c69f958c1d353f051988e7dfba2d101201328c32ae6bc627028739e759
|
|
BLAKE2b-256 checksum How to use checksums |
a205e804f507a3a963e5d957f780c9627c0bc2a0f2231e66addb602ce0428095
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logSecurity for jetliner 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 46 files in this release have been uploaded with provenance metadata.
Attestation for jetliner-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 17, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














