
jevq

jq | jevq | jq. jq handles structure; jevq reads one JSON value per line from stdin, asks
Jev (a TypeSafe System One model) a yes/no question about each, and passes through the yeses.
QUESTION is a yes/no claim about the current value, not a search query.
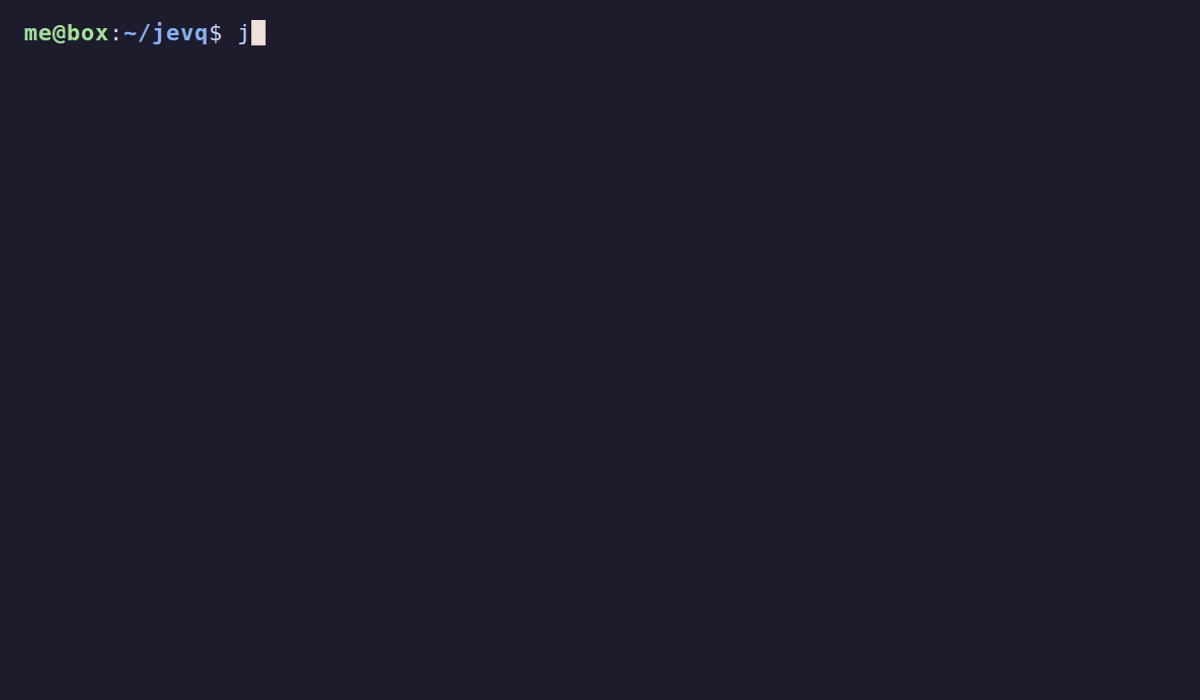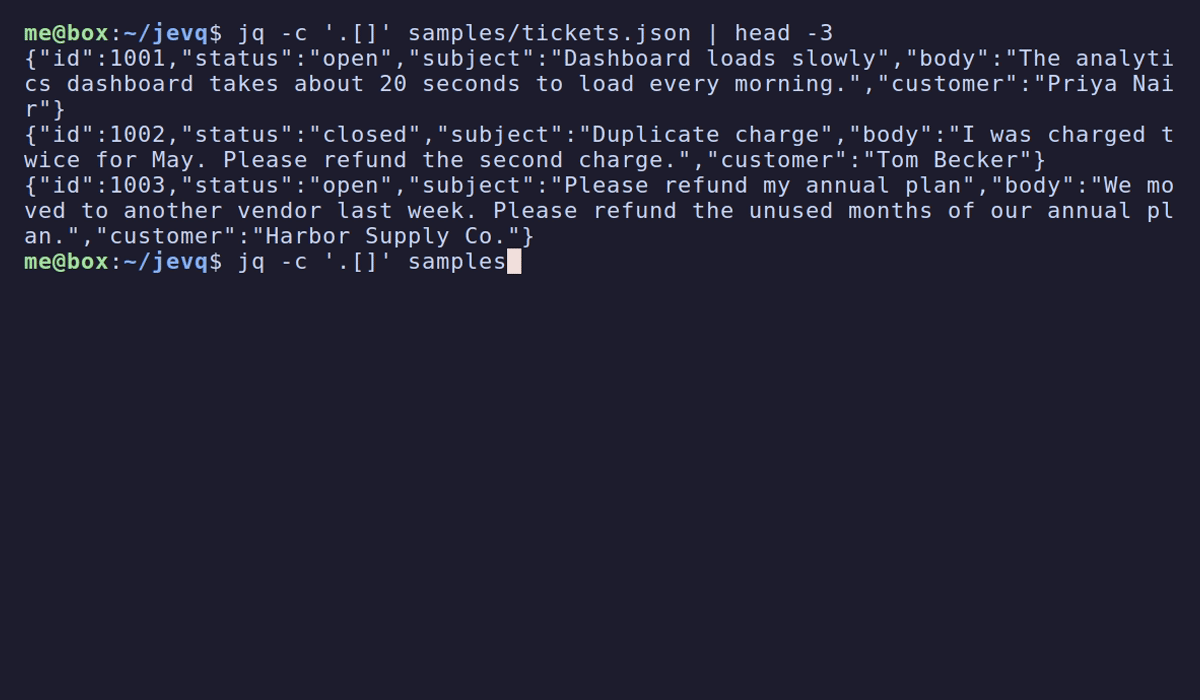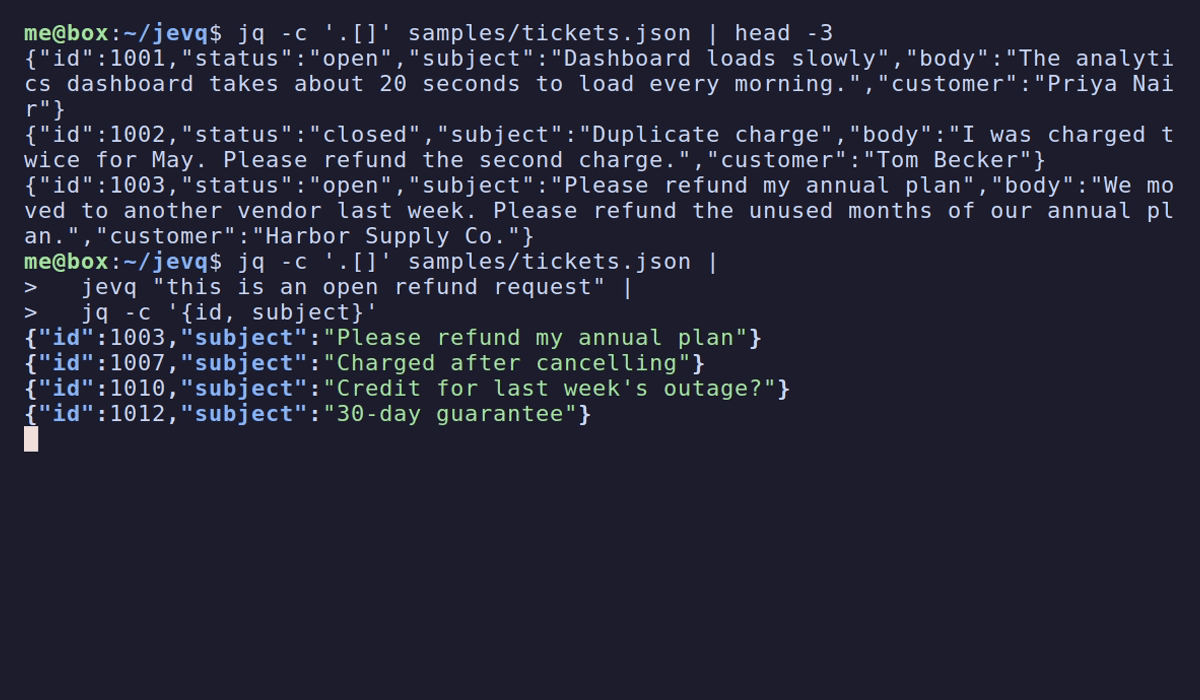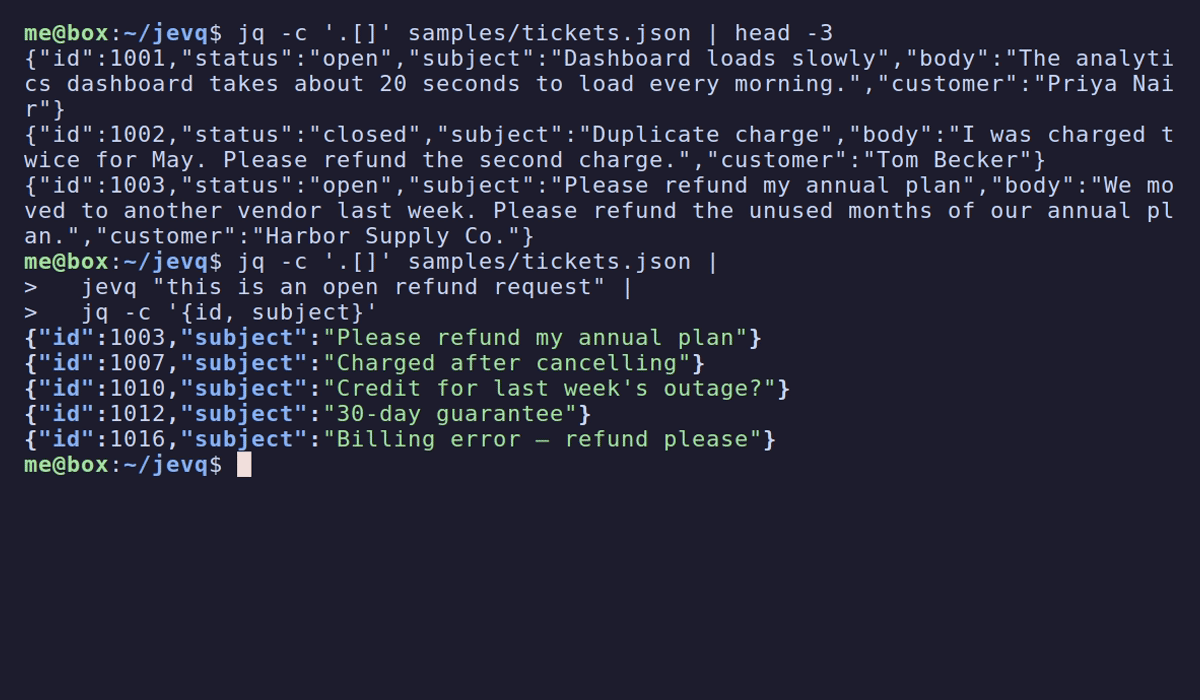
Video: docs/assets/jevq-demo.mp4
Install
uv tool install jevq            # from PyPI (or: pipx install jevq)
uv tool install --editable .    # from a source checkout
export TYPESAFE_API_KEY=...
scripts/reinstall-cli.sh forces a rebuild (--dry-run, --no-editable, --skip-smoke).
Options
jevq [options] QUESTION reads JSONL on stdin. QUESTION is required unless --pass.
| Flag | Default | Description |
|---|---|---|
QUESTION |
none | Yes/no claim about each value |
-t N, --threshold N |
0.5 ($JEV_THRESHOLD) |
Keep values scoring at least N |
-f a,b, --fields a,b |
whole value | Send only these keys; output stays the full value |
--score |
off | Emit every value as {"score":<noul>,"value":<original>} |
--pass |
off | Emit every value unchanged; no API call, no key |
--model NAME |
jev-1.13.0 ($JEV_MODEL) |
Model to ask |
-v, --verbose |
off | Print counts and the answering model to stderr |
-h, --help |
Show help and exit |
--score and --pass are mutually exclusive. A flag beats its env var.
Environment
| Variable | Default | Description |
|---|---|---|
TYPESAFE_API_KEY |
none | API key; required except with --pass |
JEV_MODEL |
jev-1.13.0 |
Default model |
JEV_BASE_URL |
https://api.typesafe.ai/v1/systemone |
API base URL |
JEV_THRESHOLD |
0.5 |
Default threshold |
Use cases
jq -c '.[] | select(.status == "open")' samples/tickets.json |
  jevq "the customer is asking for a refund" |
  jq -c '{id, subject}'
Open tickets asking for money back, printed as {id, subject}.
jq -c 'select(.level == "error")' samples/app.ndjson |
  jevq "this error is caused by a network timeout, not a bug in our code"
Error log lines that look like a timeout rather than a code bug.
gh api 'repos/itchyny/gojq/issues?state=open&per_page=100' |
  jq -c '.[] | select(.pull_request | not) | {number, title, body}' |
  jevq --score "reports a crash or wrong output, not a feature request" |
  jq -rs 'sort_by(-.score) | .[:5][] | .value | "\(.number)\t\(.title)"'
The five most bug-like open issues, as number<TAB>title.
More examples: docs/examples.md
Full contract (output rules, exit codes, HTTP, retries): docs/jevq.md
Testing
uv run pytest -q
bash tests/samples/run.sh
JEVQ_LIVE=1 TYPESAFE_API_KEY=... bash tests/samples/run.sh runs the sample pipes live.
Not supported in v1: --path, a jev() builtin, concurrency, caching.
1 maintainer

Release files for jevq 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| jevq-0.1.0.tar.gz | 12.4 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| jevq-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 21.2 kB
Release files / jevq-0.1.0.tar.gz
| Download URL | jevq-0.1.0.tar.gz |
|---|---|
| Size | 12.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
517c7d51411659334b0ce536464dc4ae43aba7bdb093e7d598bfde7799ba0107
|
|
BLAKE2b-256 checksum How to use checksums |
87f0c8f6be684b80ce9ff7c01ba4c82a315fc135820ef2c2001898a44e27fd2f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / jevq-0.1.0-py3-none-any.whl
| Download URL | jevq-0.1.0-py3-none-any.whl |
|---|---|
| Size | 8.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
adf6c379cfdf3d495c44848c4db047e69d2cb743ed07c71b69019094f1b10bb5
|
|
BLAKE2b-256 checksum How to use checksums |
1c907ea5a33b3748636f83a8d80a7b2d880762995e0f4dbd25a77d20fc15cfee
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency log












