
keyfence


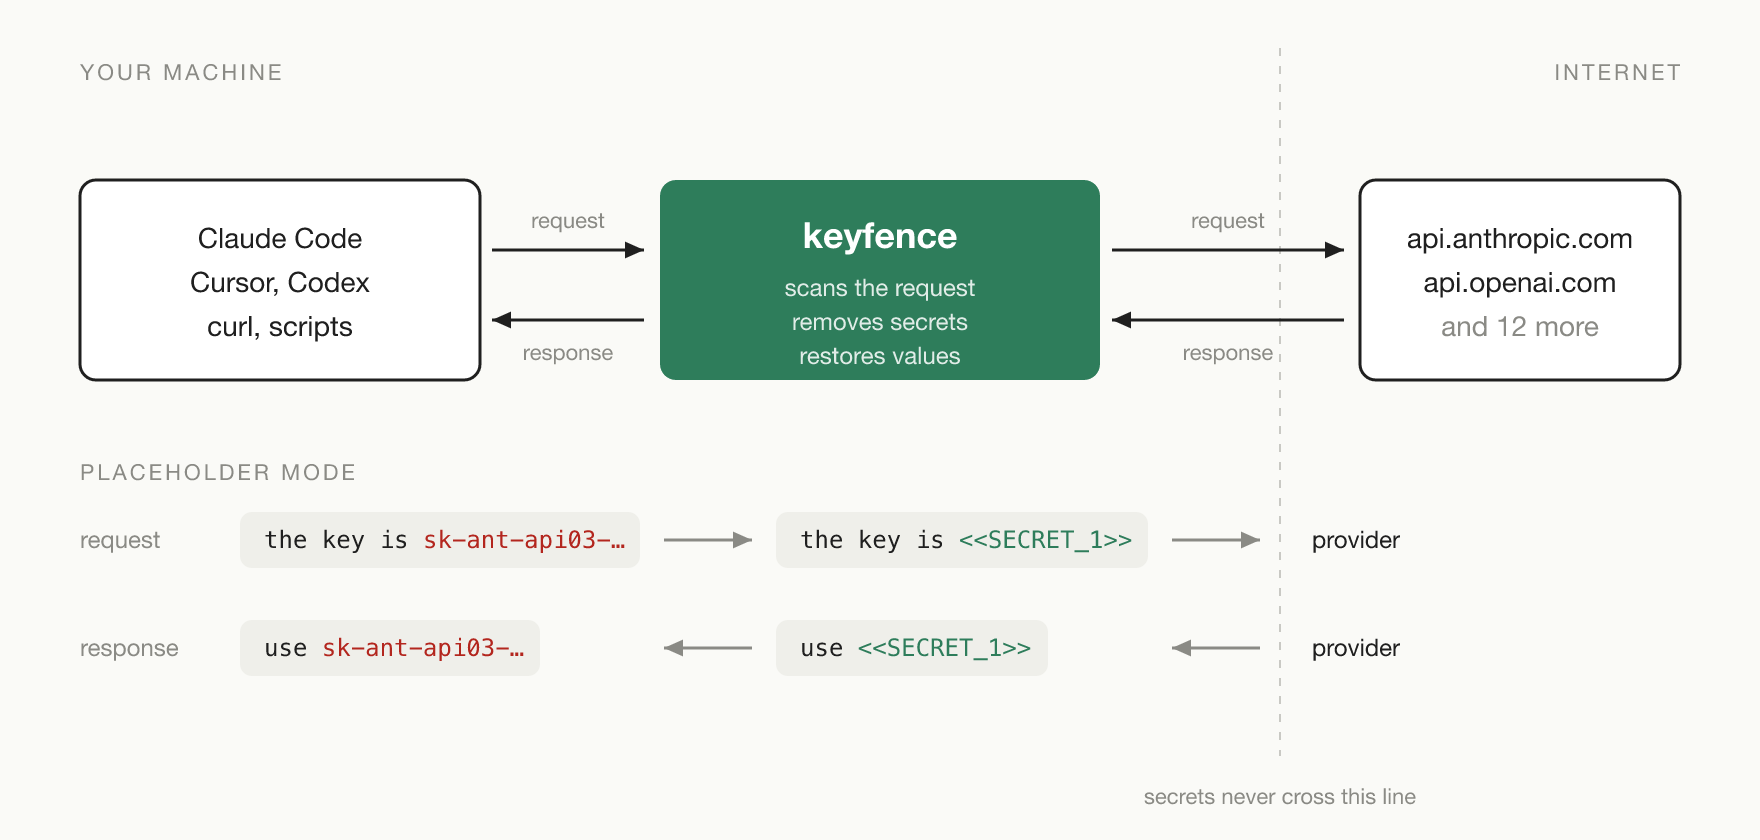
A local proxy that stops secrets from reaching LLM APIs. It checks every
request to an AI provider before it leaves your machine and blocks, redacts
or placeholder-swaps API keys, passwords and other secrets. Coding agents
read .env files and credential stores and send what they find to the
model; keyfence makes sure the values never arrive.
Try it in one minute
uv tool install keyfence     # or: pipx install keyfence, or pip install keyfence
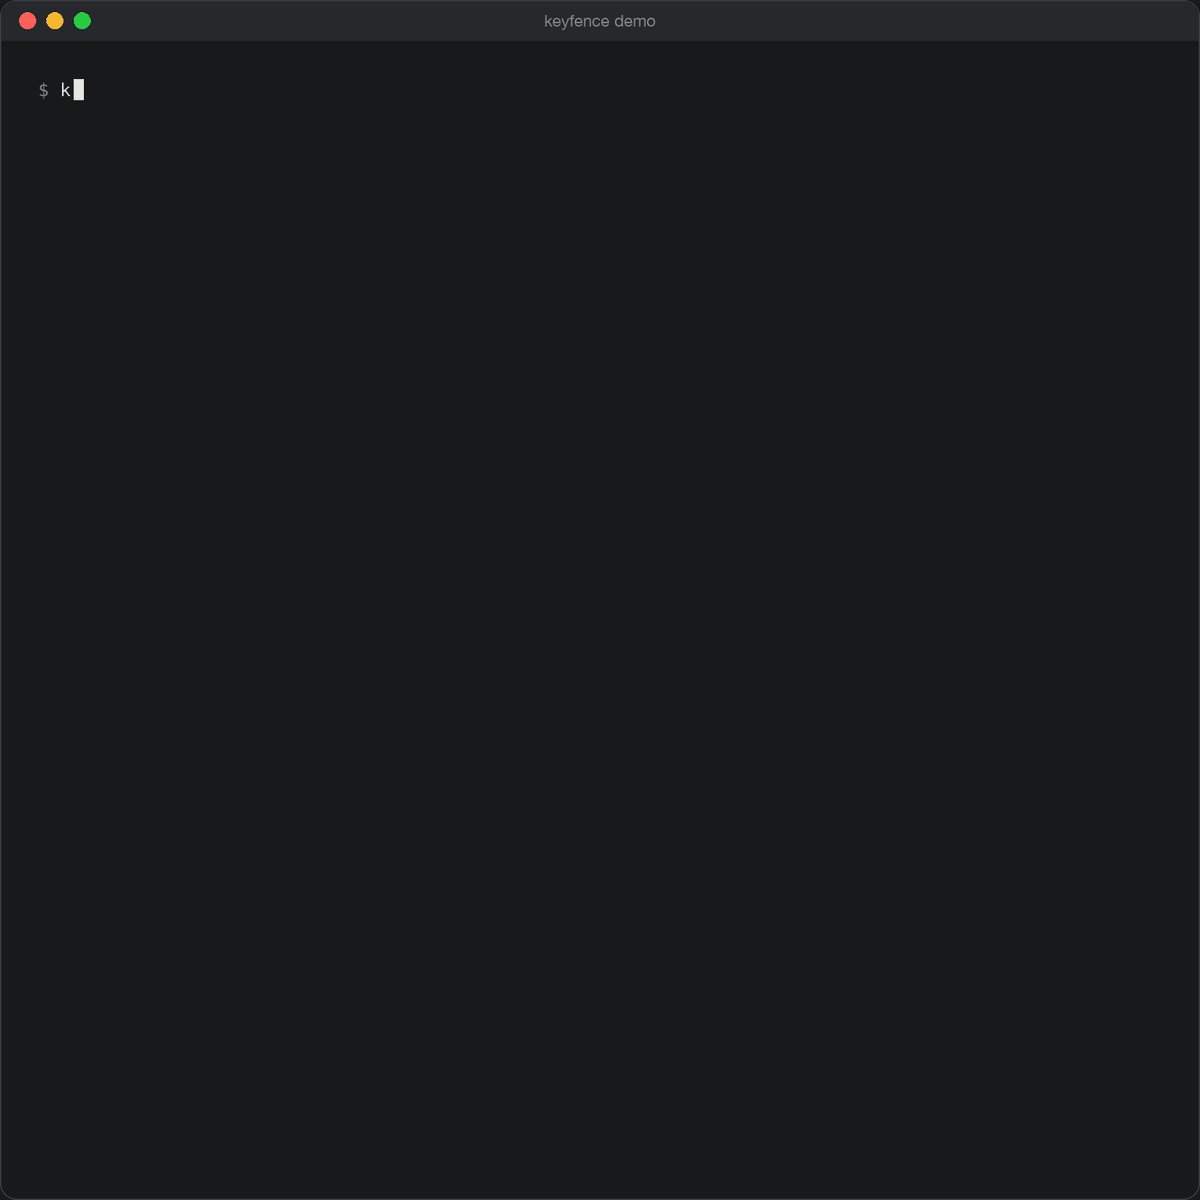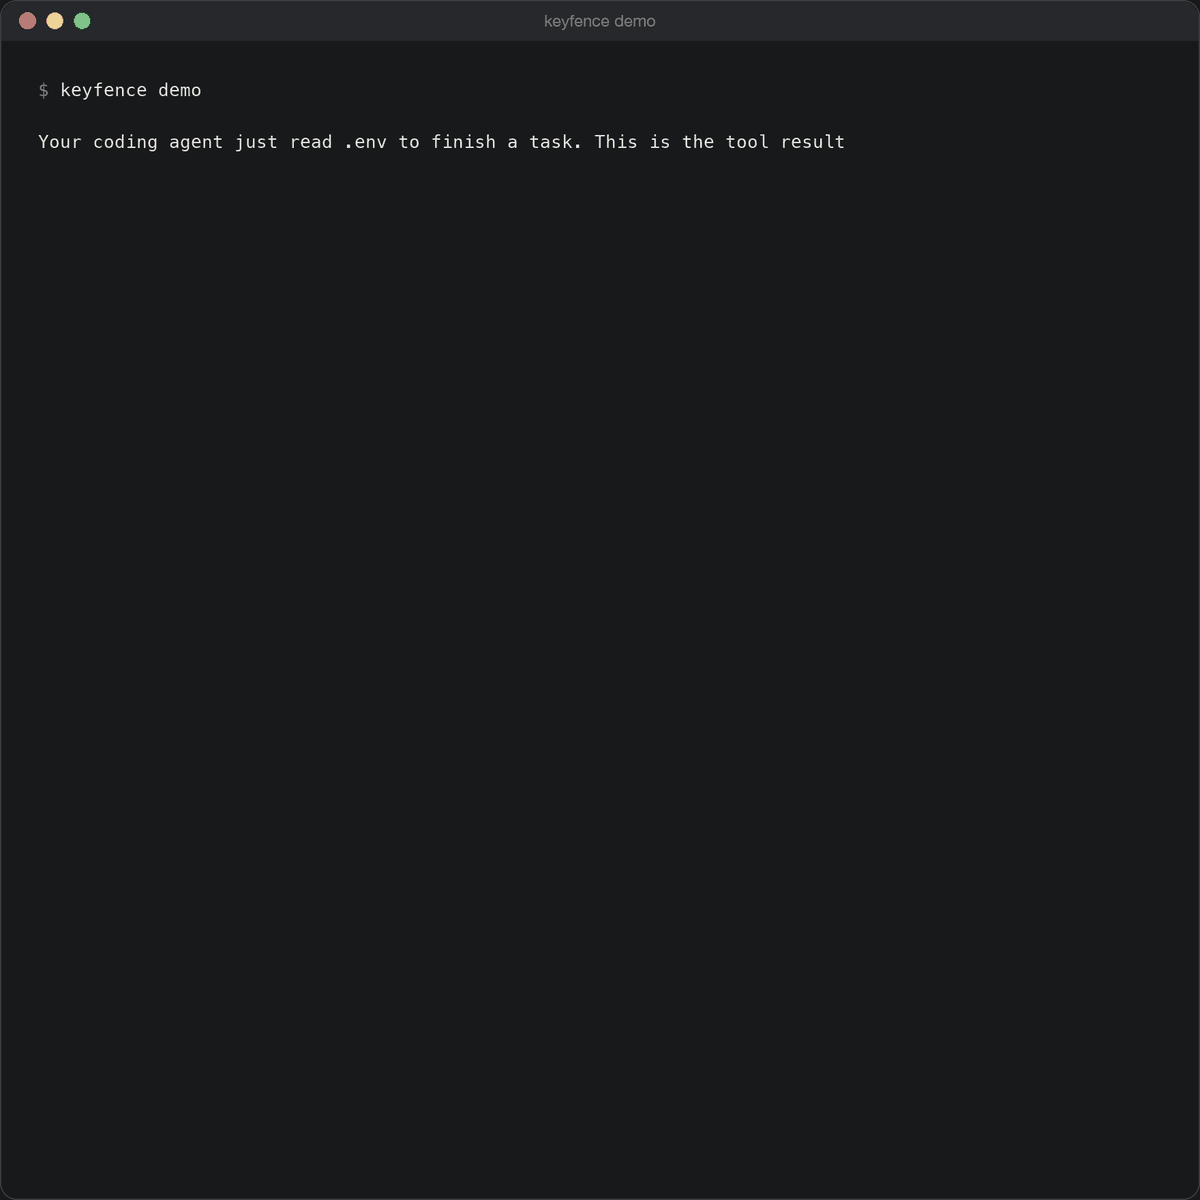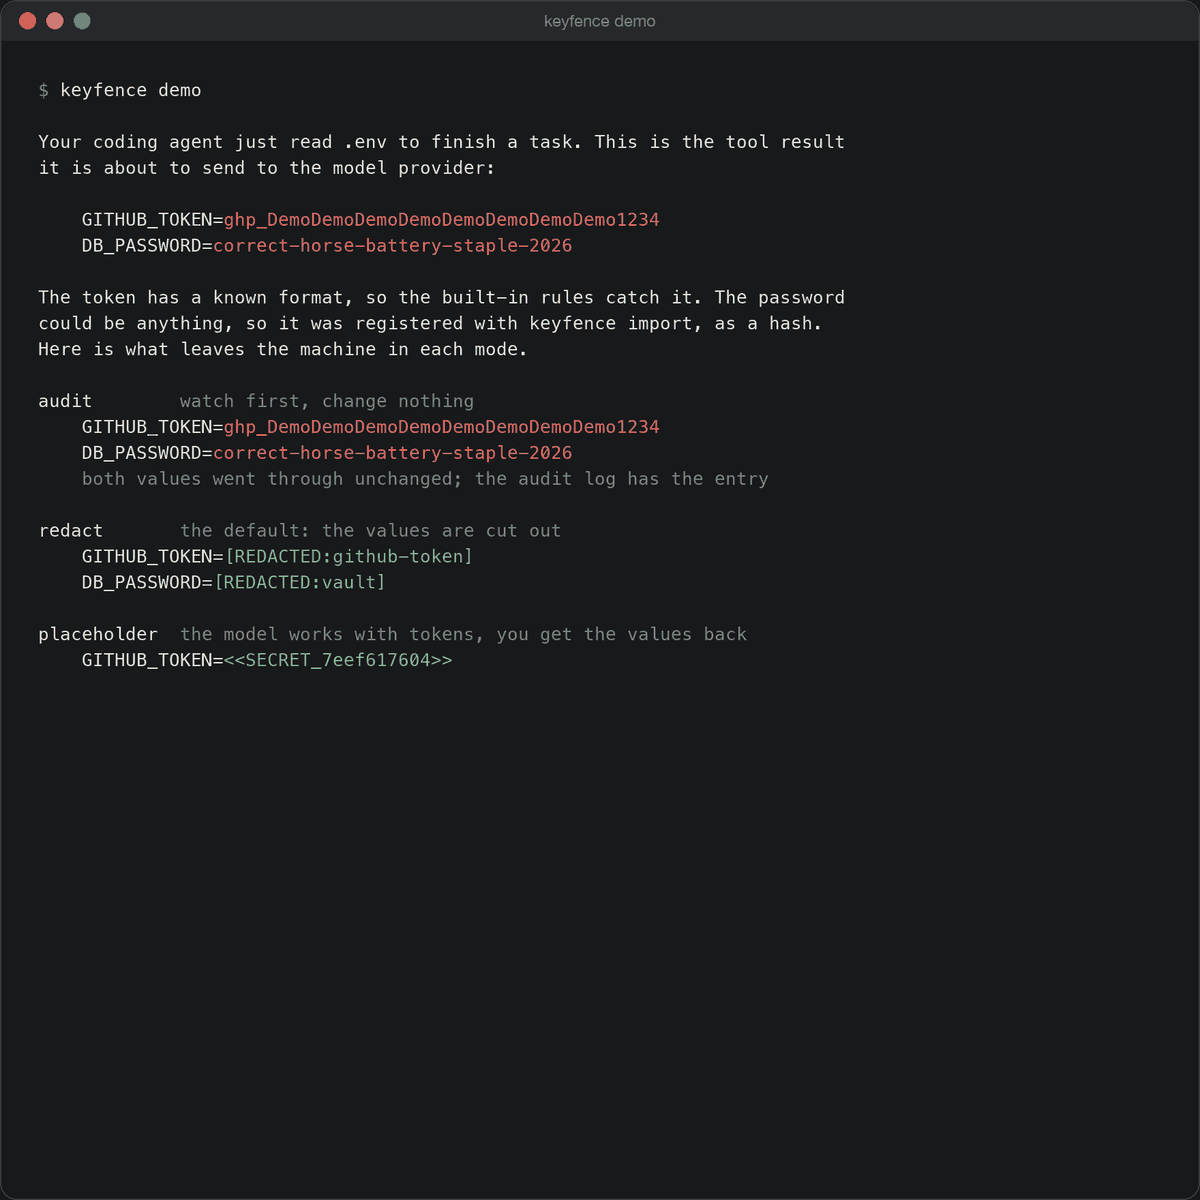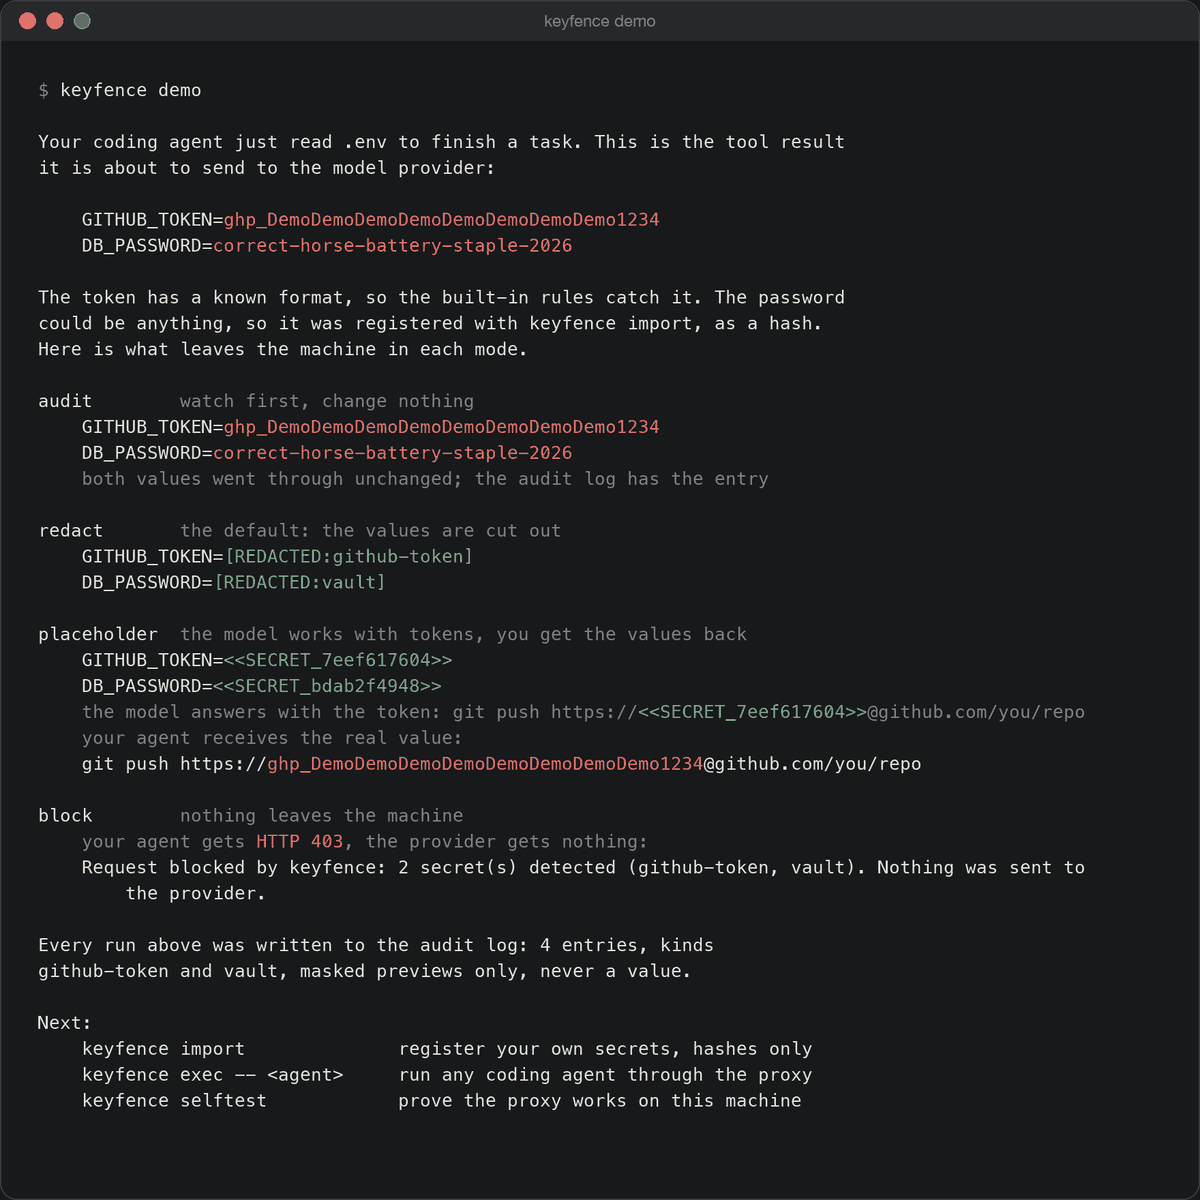
keyfence demo                # shows what each mode does to a fake request, no network
Use it
keyfence import              # register your own secrets: .env files and credential stores, hashes only
keyfence exec -- claude      # run Claude Code through the proxy
That is the whole setup for Claude Code, Codex, Aider, curl and anything
built on the Python or Node SDKs: keyfence exec starts the proxy, points
the command at it and hands it the CA certificate, then stops the proxy when
the command exits. No sudo, nothing changes on your system.
Not sure it is working? keyfence doctor checks every piece and says what
to fix. keyfence status shows what has been caught.
Two more layers, both optional:
keyfence install-hooks claude-code   # Claude Code refuses to read secret files at all
keyfence canary .env                 # plant a fake secret; if a tool ever sends it, you will know
Modes
Set mode in ~/.keyfence/config.yaml.
| mode | behaviour |
|---|---|
audit |
log what would have been caught, change nothing; start here to see what your tools send |
redact (default) |
secret becomes [REDACTED:<kind>] |
placeholder |
secret becomes <<SECRET_id>> and the real value is restored in the response, streaming included |
block |
request gets a 403 and is not sent |
What it catches
Your own secrets, whatever their format, once registered with
keyfence import (from .env files, ~/.aws/credentials, ~/.netrc,
~/.npmrc, ~/.docker/config.json, or --from op|vault|doppler|aws);
240 known formats through built-in rules and the bundled gitleaks ruleset;
and high-entropy strings that look like secrets. Only salted hashes are
stored. Details and numbers in the benchmark.
Verified with
Claude Code (through exec, --local and the hook), the Anthropic and
OpenAI HTTP APIs, curl, Python and Node clients. GitHub Copilot, Vertex AI
and Azure AI hosts are on the default list but have not been tested end to
end. Cursor and Windsurf route through their own backends and are not on
the list; add their hosts with extra_hosts if you want to try, and an
issue with the result helps either way.
Documentation
- Setup: install options, GUI apps and system-wide trust, capturing tools that ignore proxies, Docker, all commands.
- Detection: the vault, pattern rules, entropy check, what is excluded, the audit log.
- Configuration: every option, environment variables, the system prompt notice.
- Benchmark:
recall by secret format and false positive rate by content type, against
gitleaks, reproducible with
python bench/run.py. - Limitations: what keyfence does not cover and what to combine it with.
- Claude Code plugin:
the hook and two skills, installable with
/plugin marketplace add aminueza/keyfence. - Security: what the proxy sees, what it stores, how releases are built.
- Development and Changelog.
License
MIT. Bundled detection rules come from gitleaks, also MIT.
1 maintainer

Release files for keyfence 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| keyfence-0.4.0.tar.gz | 83.3 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| keyfence-0.4.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 144.6 kB
Release files / keyfence-0.4.0.tar.gz
| Download URL | keyfence-0.4.0.tar.gz |
|---|---|
| Size | 83.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
eecfb13ae17bdf098a97fc6cb1d09419660f6498d781046ddd6c725e11881d2e
|
|
BLAKE2b-256 checksum How to use checksums |
0c666ee3b15a8a278d5cfa272a6dec6ef3c256a1f1febc9dde41eda34c30b3de
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 11, 2026.
Transparency logRelease files / keyfence-0.4.0-py3-none-any.whl
| Download URL | keyfence-0.4.0-py3-none-any.whl |
|---|---|
| Size | 61.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
500a85e1dcc9632c07bdda1302ca3f6227fc3c23d7167ee696a9a6f507eaf018
|
|
BLAKE2b-256 checksum How to use checksums |
48eb0957340806673a5409c45d111fc6dc96d6b1007d87dd2d1daea2b1e522db
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 11, 2026.
Transparency log













