
KICK - Coding Agent
Kick is an simple coding agent that uses pydantic ai. It can read, write, and edit code.
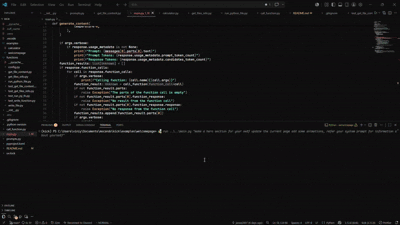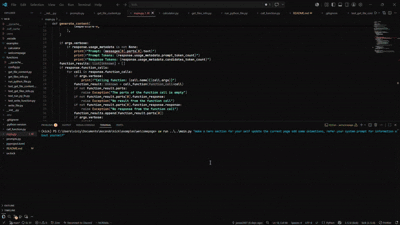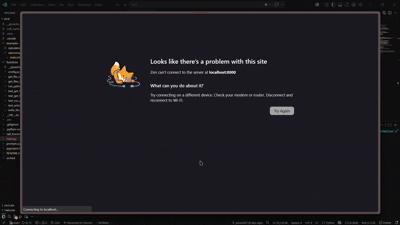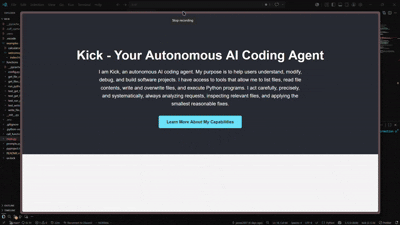
Features
- File Operations: Read, write, edit and list files in the workspace
- supports multiple providers
Installation
- Clone the repository
- Install dependencies:
uv sync - Set your api key:
example:
GEMINI_API_KEY=your_api_key_here
-
setup a model:
example:
MODEL=groq:openai/gpt-oss-120b
Usage
Run the agent with a prompt:
uv run main.py "Your prompt here"
Run the agent in multiturn conversation:
uv run main.py
How It Works
The agent uses ai models to call several functions which will help the llm to interact with the file system.
read: Read file contentsls: List files and directorieswrite: Create or modify filesedit: edit a file
Note: This is a learning project with a simple implementation, Not recommended to use for serious stuff.
1 maintainer

Metadata
1 maintainer
Release files for kick-agent 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| kick_agent-0.1.0.tar.gz | 12.1 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| kick_agent-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 28.8 kB
Release files / kick_agent-0.1.0.tar.gz
| Download URL | kick_agent-0.1.0.tar.gz |
|---|---|
| Size | 12.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a61e341f0e14da8ccb6dd0201fd867e90970e6d40cd233616ee8052dc60f6183
|
|
BLAKE2b-256 checksum How to use checksums |
dd7afbe7e8e3ebfd160c6cdacaa58832e04f169ccb6ed1efd54923ab40b184ef
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.7.2
|
Release files / kick_agent-0.1.0-py3-none-any.whl
| Download URL | kick_agent-0.1.0-py3-none-any.whl |
|---|---|
| Size | 16.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ac8e73ca322ff6ecc301432e0543ec6600d86bf78bcf04918e8c093e22a8cca2
|
|
BLAKE2b-256 checksum How to use checksums |
01d0badc2714a1a6d9d5ea9eca5adc10eff67f8e2a30e1410c4c2e2d5af30637
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.7.2
|
Security for kick-agent 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.













