



Your AI agents write Markdown faster than anyone can keep it true.
Libraryan makes one agent the only writer of your project's docs. Every other agent, and every person, files a request.
Quick start · How it works · Demo · Safety · Guide
The problem
Give a repo a few coding agents and a few months, and the Markdown rots:
a README that documents flags the code dropped, three setup guides that disagree, NOTES.md, TODO_old.md, an empty ideas.md, and agent instruction files nobody has read since they were written.
Every agent writes docs. No one owns them.
The fix: one owner
Libraryan installs an agent that owns every Markdown file in your project: knowledge base, docs and agent instruction files. It is vendor-neutral where it matters: your docs stay plain Markdown in git, the rules live in AGENTS.md (read by Codex, Cursor, Gemini, Copilot, Claude and others), and the lock is a git hook that stops every tool alike.
- 🔒 Single writer, enforced. A git pre-commit hook blocks every other edit, from any agent or editor. This is a hook, not a polite prompt.
- 📨 Everyone else files a request. Other agents and people drop a note in
.libraryan/requests/. Libraryan writes the change. - 🧭 Docs checked against the code. When docs contradict the code, it fixes the docs and reports suspected code bugs. It never edits code.
- 🧹 Junk removed, facts kept. Outdated Markdown is deleted only after a deletion ledger proves where each fact went.
- 🧑⚖️ A second agent reviews every commit. A separate, read-only process with a fresh context. Anything but an exact
APPROVEblocks the commit. - 💸 Cost caps built in. Per-call and daily budgets, and a model-free audit that makes quiet nights cost $0.
Quick start
pipx install libraryan     # once per machine
cd your-project            # any git repo, on its default branch
libraryan init             # once per project: installs, builds the KB, commits
That's it. From now on Libraryan updates the docs after your commits and checks them once a day. It commits locally and never pushes. Remove it at any time with libraryan uninstall; the docs stay.
Or install as a Claude Code plugin
/plugin marketplace add narek-mn/libraryan
/plugin install libraryan@libraryan
/libraryan:init
/libraryan:init installs the CLI with pipx and runs libraryan init. /libraryan:status shows health and cost, and /libraryan:request files a doc change.
Requirements
Linux or macOS with:
| Need | Check | Install |
|---|---|---|
| Python 3.10+ | python3 --version |
your package manager |
| pipx | pipx --version |
Debian/Ubuntu: sudo apt install pipx && pipx ensurepath; macOS: brew install pipx && pipx ensurepath |
| git 2.34+ | git --version |
your package manager |
| Claude Code 2.1+, logged in | claude --version |
Claude Code setup |
| cron | crontab -l |
usually preinstalled |
| gitleaks (optional) | gitleaks version |
secret scanning |
How it works
flowchart LR
A["🤖 Other agents<br/>👩💻 People"] -- "edit README.md" --> L{{"🔒 Lock<br/>git pre-commit hook<br/>any agent, any editor"}}
L -- blocked --> A
A -- "request file" --> Q[".libraryan/requests/"]
T["⏱ Triggers<br/>commit · daily · manual"] --> R
Q --> R["📚 Libraryan run<br/>audit → write → checks"]
R --> G["🧾 Deletion ledger<br/>facts accounted for"]
G --> V{"🧑⚖️ Independent<br/>reviewer"}
V -- APPROVE --> C["✅ docs(libraryan): commit"]
V -- anything else --> X["↩ restore + report"]
- Commit as usual. After a quiet period (10 minutes by default), Libraryan wakes up. A daily run catches anything else.
- Audit first, for free. A deterministic check finds broken links, paths that no longer exist and notes older than their sources. If there is nothing to do, it stops there without calling a model.
- Write. Libraryan updates the knowledge base (
docs/kb/, with anindex.mdand alog.md), fixes stale docs, merges duplicates and deletes junk. - Gate. Lint, secret scan, deletion ledger, then an independent reviewer. Only fully approved runs are committed, and only Libraryan's own files.
- Report. Each run leaves a report (
.libraryan/state/reports/latest.md) and a trace line with its cost.libraryan statsshows the totals.
See it on a real repo
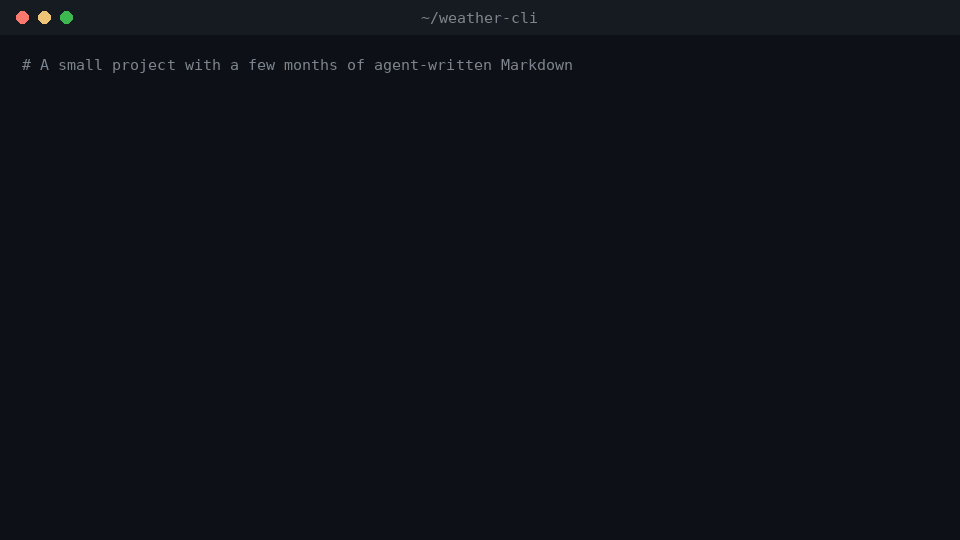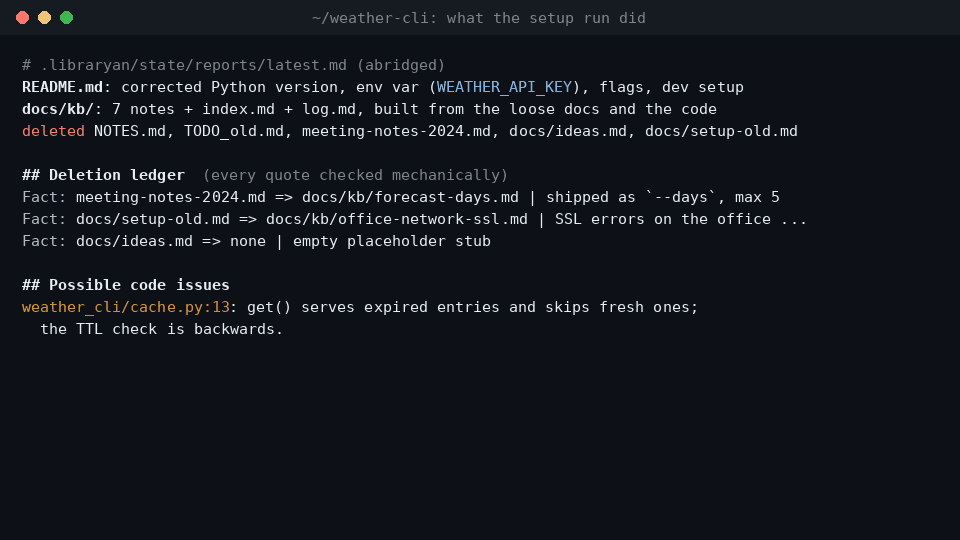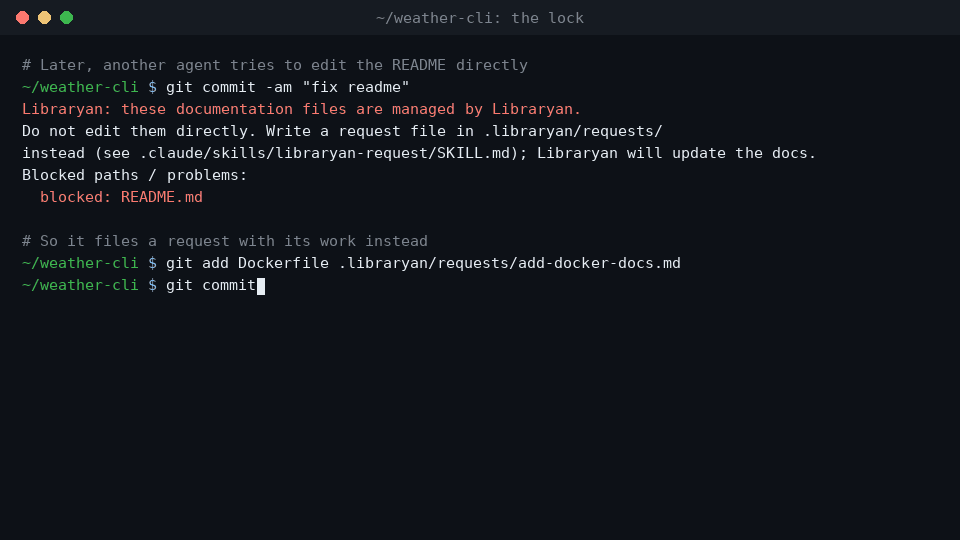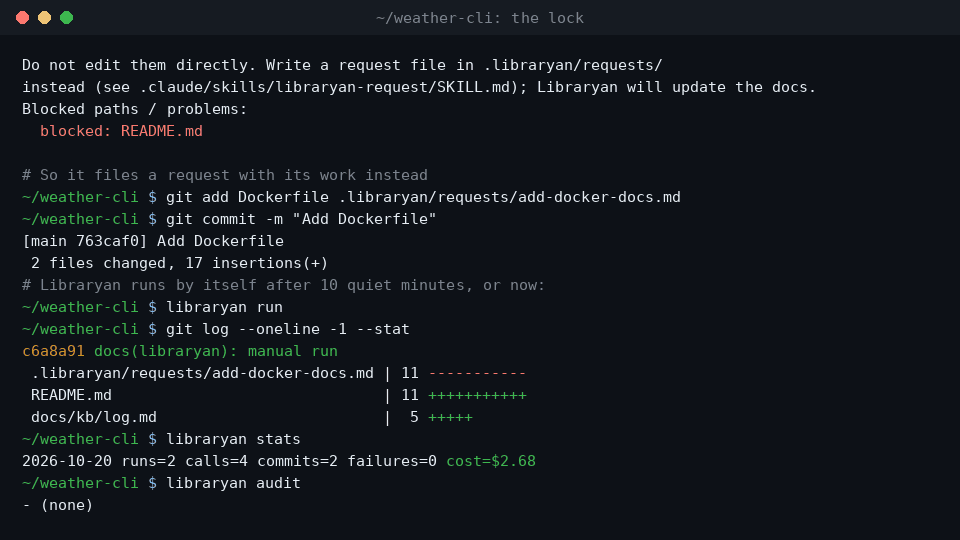
We built a small weather CLI the way agent-heavy repos really look: a README that documents flags and an env var the code dropped, a second setup guide that disagrees with it, scratch notes, meeting notes, an old to-do list, an empty stub, and one quiet bug in the code. Then we ran libraryan init once. These are the real results:
| Before: 8 loose files | After one setup run (5.6 min, $2.29) |
|---|---|
|
|
- 5 junk files deleted, no fact lost. The ledger mapped all 10 facts they held to their new homes, with quotes checked mechanically, and named the 2 files that held nothing worth keeping.
- The README was fixed against the code: Python version, the
WEATHER_API_KEYenv var, the--units/--days/--jsonflags, and dev setup. - It caught the code bug we planted and reported it without touching the code: "
weather_cli/cache.py:13:get()returns the cached entry only when it is older than the TTL… The check is backwards." - It flagged a conflict for a human: an old
AGENTS.mdrule told agents to edit the README directly. - A later request ("document the new Dockerfile") was applied in 53 s for $0.39. Total for the day: $2.68, 2 commits, 0 failures, and an audit with no findings.
Rebuild the demo yourself: examples/demo.
Why trust it with your docs
| Risk | What Libraryan does |
|---|---|
| It deletes something important | A deleted doc must be a pure move, or the run must quote where each fact went. Quotes are checked mechanically, otherwise the deletion is restored. Git keeps everything. |
| It hallucinates | Every commit passes a second agent that sees the diff, not the author's reasoning, and fails closed. |
| It touches my code | It writes only paths it owns. Anything else is restored, and code issues go into the report. |
| It leaks a secret into docs | It is told never to copy secrets, and an optional gitleaks scan runs on every run. |
| It burns money | --max-budget-usd on every call, plus daily caps on runs, commits and failure streaks. Quiet nights skip the model entirely. |
| Other agents treat a request as a command | Request files are data, never instructions. |
| I want it gone | libraryan uninstall removes hooks, cron and the agent in one commit. Your docs stay. |
Honest limits: Libraryan's own writer and reviewer run through Claude Code today; more runtimes (Codex CLI, Gemini CLI) are planned. Linux and macOS only. The lock is a guardrail, not a security boundary (git commit --no-verify skips it). See Known limits.
Commands
| Command | Does |
|---|---|
libraryan init |
Install into this repo and build the knowledge base |
libraryan run |
Run now |
libraryan audit |
Docs-vs-code audit, no model call |
libraryan stats |
Runs, commits, failures and cost per day |
libraryan check |
Lint docs and scan for secrets |
libraryan upgrade |
Refresh the project after pipx upgrade libraryan |
libraryan uninstall |
Remove it. The knowledge base stays |
Configuration, reports, upgrade notes and every option are in the guide.
FAQ
Why not just put "keep the docs updated" in CLAUDE.md?
Because every agent then writes docs in its own style, at its own time, without checking them against the code. That instruction is how Markdown rot starts. Libraryan makes one writer responsible and enforces it with hooks, so the rule can't be skipped by accident.
What does it cost?
You pay for your own model usage. A run happens only after commits, on request, or when the daily audit finds something. Quiet days are free. Hard caps apply per call (default $5 for a run, $25 for the first setup) and per day. libraryan stats shows the real spend.
Does it work with Cursor, Copilot, Gemini or Codex agents?
Yes. The git pre-commit hook rejects any tool's commits to owned docs, the request rules are written into AGENTS.md, which those agents read, and the knowledge base is plain Markdown any model can use. Libraryan's own writer runs through Claude Code today; other runtimes are planned.
Will it push or open PRs?
No. It commits locally, on your default branch only, under its own docs(libraryan): prefix. You decide when to push.
Can my teammates still change docs?
Yes, by filing a request: a short Markdown file under .libraryan/requests/. Their agents learn how from the libraryan-request skill and AGENTS.md. You can also exempt paths in the config.
Contributing
Issues and PRs are welcome. Start with CONTRIBUTING.md. Report security issues privately (SECURITY.md).
If Libraryan keeps your docs honest, a ⭐ helps others find it.
MIT © narek-mn · Changelog
1 maintainer

Metadata
1 maintainer
Release files for libraryan 0.2.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| libraryan-0.2.2.tar.gz | 69.1 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| libraryan-0.2.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 120.4 kB
Release files / libraryan-0.2.2.tar.gz
| Download URL | libraryan-0.2.2.tar.gz |
|---|---|
| Size | 69.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
0d75010e1bd150ab2d301e4bc64b70f7bc40530cb30ef78497896d2c2e8e9e9c
|
|
BLAKE2b-256 checksum How to use checksums |
419f0dd0720b3b8eb639dd2a25e515a8ef8fb27434a56bcaf2872d482b0ee0b8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logRelease files / libraryan-0.2.2-py3-none-any.whl
| Download URL | libraryan-0.2.2-py3-none-any.whl |
|---|---|
| Size | 51.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
bc7f36f8b59ab9a3bdc24da9c7c1022af9dc1798eb7df6bbf6a9f93a9bb136c8
|
|
BLAKE2b-256 checksum How to use checksums |
024ea0f50a0c48aa7f579a19f4bca82752fdccfe5ab1370be7fb9973f38eae42
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logSecurity for libraryan 0.2.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for libraryan-0.2.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














