
Evidence-backed Linux permission graphs and attack-path investigation.
Trace how accounts reach privileged resources, inspect the supporting evidence and compare permission paths before and after hardening changes.



Documentation · Quick start · Docker · GNN · Releases · Issues
Live collection: Linux only. macOS, BSD and Windows are not collection targets. Saved HTML reports open in a modern desktop browser. The demo can run elsewhere with Python; it does not audit that operating system.
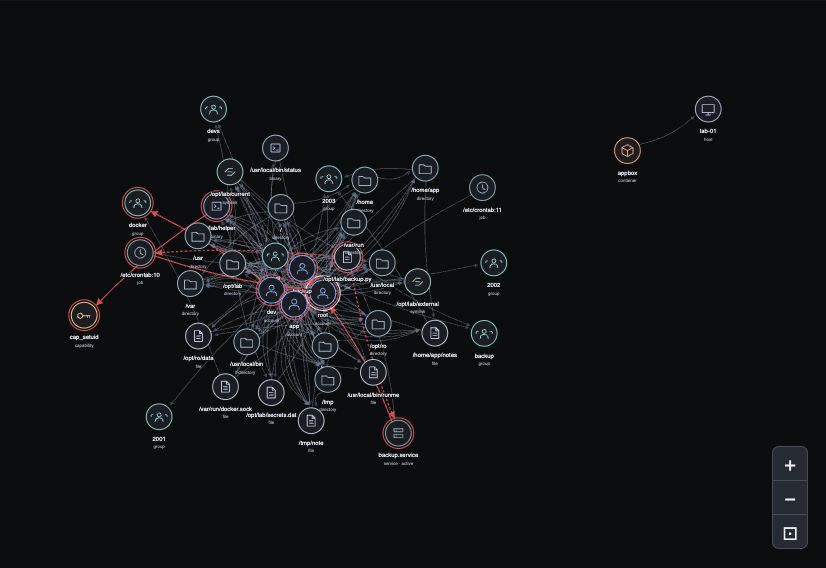
The graph above comes from the LinuxHound demo. Red relationships mark modeled trust boundaries, while dashed relationships retain unresolved prerequisites. Following a connection helps explain access, but does not establish that an exploit works.
Quick start: Linux
To begin on a Linux host with Git and Python 3.9 or newer, clone the repository and enter its directory. Then create a virtual environment, install LinuxHound and run your first collection:
git clone https://github.com/daniyyell-dev/LinuxHound.git
cd LinuxHound
python3 -m venv .venv
. .venv/bin/activate
python -m pip install .
linuxhound scan --root /etc --root /opt --serve --open
When collection finishes, LinuxHound feeds the results directly into the UI.
Each run saves snapshot.json,
report.json and index.html under linuxhound-results/. --serve --open opens
a localhost viewer. On a headless host, omit those flags and copy the HTML to a
trusted desktop. For installation from the Python Package Index, use
python -m pip install linuxhound, or python -m pip install 'linuxhound[gnn]'
to include the optional neural dependencies.
If you want to explore the interface first, open the demo without collecting information from a host:
linuxhound demo --open
Once you are familiar with the graph, you can install the optional Graph Neural Network (GNN) dependencies and explore neural review ordering:
python -m pip install '.[gnn]'
linuxhound demo --gnn --open
The bundled model is an uncalibrated synthetic demonstration. Its scores help order reviews; they do not prove vulnerabilities or safety. Missing collection coverage is not a clean result.
Compare Linux tools
LinuxHound is a better fit when you need to follow permissions across accounts, inspect a path's evidence in a browser and review what changed after hardening. The tools below serve different workflows, so the comparison includes strengths that LinuxHound does not provide.
| Feature | LinuxHound | LinPEAS | RootHound | privmap | Lynis |
|---|---|---|---|---|---|
| Native Linux collection | ✅ | ✅ | ✅ | ✅ | ✅ |
| Privilege graph across collected accounts | ✅ | ❌ | ❌ | ✅ | ❌ |
| Interactive, standalone HTML graph | ✅ | ❌ | ✅ | ❌ | ❌ |
| Before/after path comparison that accounts for missing coverage | ✅ | ❌ | ❌ | ❌ | ❌ |
| General hardening and compliance audit | ❌ | ❌ | ❌ | ❌ | ✅ |
Documentation
Continue with the user guide for investigating results, graph examples and model training. It also covers comparison details, collection scope and limitations, and development.
References and acknowledgements
BloodHound inspired the relationship graph and attack-path investigation approach. LinuxHound also provides an export for BloodHound's OpenGraph framework.
GTFOBins provides the Unix executable reference used by LinuxHound's optional technique matching. Catalog matches provide context for reviewing permissions; they do not establish that a path is exploitable.
LinuxHound is licensed under Apache-2.0. Attribution information is available in NOTICE.
1 maintainer

Metadata
1 maintainer
Release files for linuxhound 0.3.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| linuxhound-0.3.1.tar.gz | 473.1 kB | With provenance | Details for linuxhound-0.3.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| linuxhound-0.3.1-py3-none-any.whl | Python 3 | none | any | Details for linuxhound-0.3.1-py3-none-any.whl |
Total release size: 641.1 kB
Release files / linuxhound-0.3.1.tar.gz
| Download URL | linuxhound-0.3.1.tar.gz |
|---|---|
| Size | 473.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
56a67a992935fae05bd493eec205262e3ee40ce5e97522783a6a84c48934974b
|
|
BLAKE2b-256 checksum How to use checksums |
99cfcb73ab33f104957d41020df4e022948ce32b72a646a8b41b8def90b21251
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency logRelease files / linuxhound-0.3.1-py3-none-any.whl
| Download URL | linuxhound-0.3.1-py3-none-any.whl |
|---|---|
| Size | 168.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
573b435a0493931ade3c88e32228bb885444713fb5d6ecdb10f81f4b2a7add9a
|
|
BLAKE2b-256 checksum How to use checksums |
41da7bdc6d654d60fea79e2a32e9d1ab7d15a60e20a325210255b5303b5b418e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency logSecurity for linuxhound 0.3.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for linuxhound-0.3.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













