
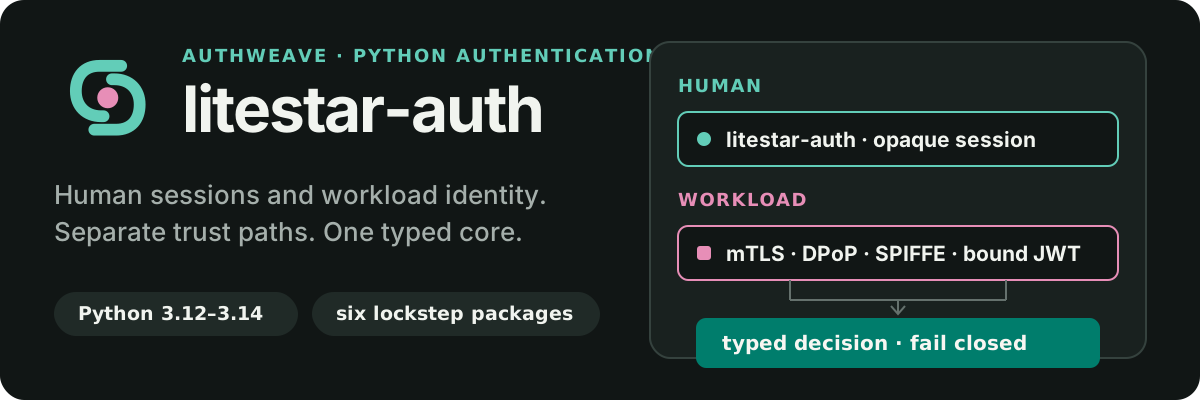

litestar-auth 8 is the human-authentication layer in the six-distribution AuthWeave workspace for
Python 3.12–3.14. Browser sessions and machine credentials stay on separate trust paths while
sharing typed, fail-closed AuthWeave decisions.
uv add litestar-auth
Six packages, one version
litestar-auth— Litestar registration, login, OAuth + PKCE, TOTP, roles, organizations, and opaque database or Redis sessionsauthweave-core— Typed principals, evidence, decisions, route policies, and fail-closed provider coordinationauthweave-workload— X.509 lifecycle plus mTLS, DPoP, SPIFFE, bound JWT, and introspection profilesauthweave-otel— API-only security spans and metrics without an SDK or exporterauthweave-webhooks— Ed25519 Standard Webhooks integrity, replay control, and bounded deliveryauthweave-http-signatures— RFC 9530/RFC 9421 payment-message integrity after machine authentication
Install only the layer you need. All six distributions use one exact lockstep version; dependency
direction stays one-way (authweave-core at the root). Details:
architecture.
Start with a secure human session
uv add litestar-auth aiosqlite
from litestar import Litestar
from litestar_auth import DatabaseTokenAuthConfig, LitestarAuth, LitestarAuthConfig

config = LitestarAuthConfig(
    database_token_auth=DatabaseTokenAuthConfig(
        token_hash_secret=session_digest_secret,
    ),
    csrf_secret=csrf_secret,
    session_maker=session_maker,
    user_model=User,
    user_manager_class=UserManager,
    user_db_factory=user_db_factory,
    user_manager_security=user_manager_security,
)

app = Litestar(plugins=[LitestarAuth(config)])
Opaque sessions are not challenge JWTs and not workload credentials. Read credentials and tokens and the quickstart.
Keep machine identity on its own path
uv add 'authweave-workload[mtls,jwt,sqlalchemy]'
# Add [litestar] only for the Extension SDK v2 integration.
Bound tokens or proofs must match the verified certificate or DPoP key. Ambiguous credential ownership fails closed. See the security posture.
Security boundary
AuthWeave intentionally does not provide unconstrained bearer login, user-owned API keys, shared-secret machine credentials, an OAuth Authorization Server or STS, or generic IAM.
Release evidence
CI exercises Python 3.12–3.14 on Linux, macOS, and Windows with a 100% branch-coverage gate per distribution, CodeQL, dependency review, pinned actions, CycloneDX 1.7 SBOMs, and reference stacks. That evidence is library readiness, not certification of a deployment.
Documentation
- Quickstart
- Credentials and tokens
- Architecture
- Security posture
- Migrate 7.x → 8
- Changelog
- Vulnerability reporting
License
1 maintainer

Metadata
1 maintainer
Release files for litestar-auth 8.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| litestar_auth-8.0.2.tar.gz | 333.5 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| litestar_auth-8.0.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 802.6 kB
Release files / litestar_auth-8.0.2.tar.gz
| Download URL | litestar_auth-8.0.2.tar.gz |
|---|---|
| Size | 333.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
ce1ff7ff096522f0cd1a82c957eafecb9c300efa1afea756631e6652a6400064
|
|
BLAKE2b-256 checksum How to use checksums |
cae6dba850cce16bb8c246f713f9f95849f1ab6fc89fe1a9cd043fca478d9e39
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logRelease files / litestar_auth-8.0.2-py3-none-any.whl
| Download URL | litestar_auth-8.0.2-py3-none-any.whl |
|---|---|
| Size | 469.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
dab6735e542468b523e18d3995abfa82d957490065b48a5944b539de42474072
|
|
BLAKE2b-256 checksum How to use checksums |
0468552b00eb8b377fc7c65de693b35b6c492d0a0873f2218a761f97a332201f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logSecurity for litestar-auth 8.0.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for litestar_auth-8.0.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














