
Website · Install · Quick start · How it works · AI & skill · Docs · Security
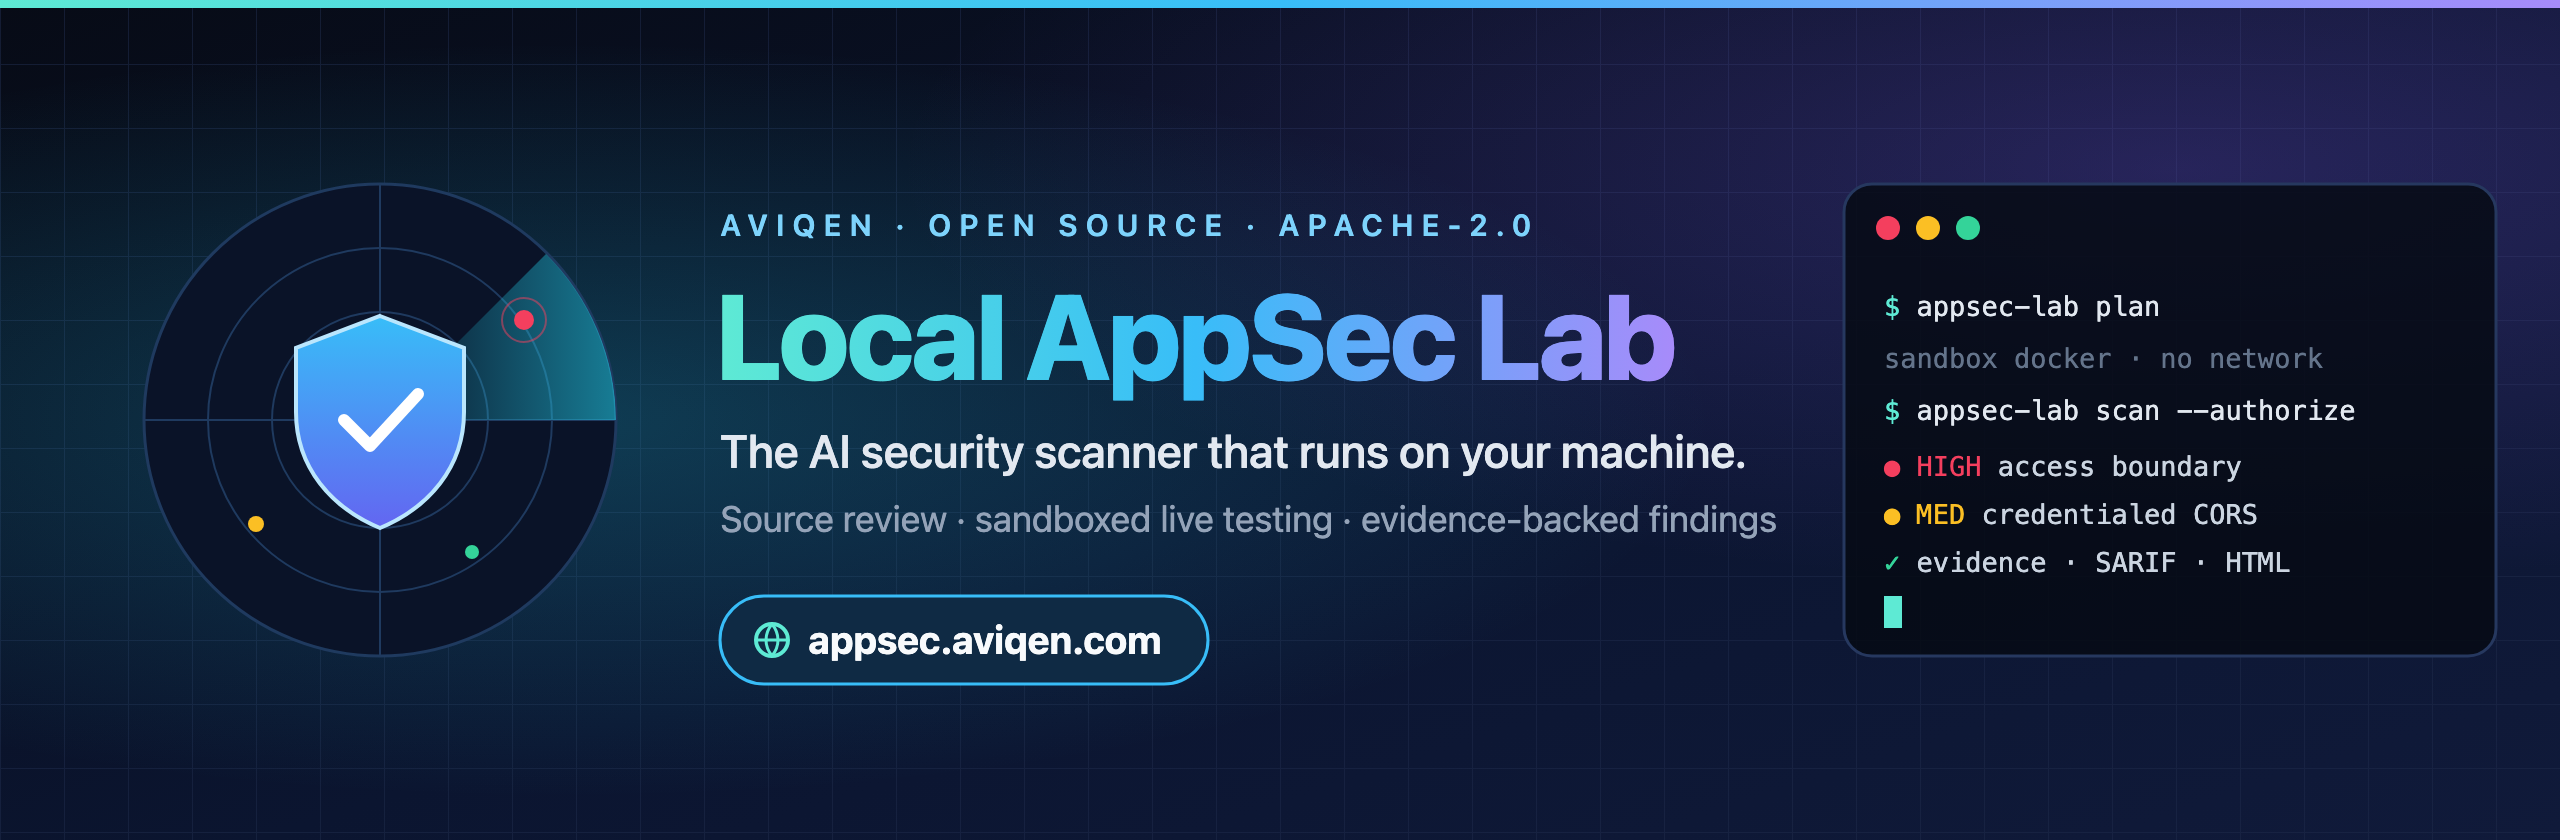
Local AppSec Lab is an open-source application security engine and portable Agent Skill from AVIQEN. It reviews your source, starts your app in a sandbox, tests it with synthetic users, and reports only what it can back with evidence. Your code stays on your machine. Deterministic assessments need no model subscription or API key.
✨ Why Local AppSec Lab
🏠 Local firstSource analysis, sandboxed runtime and reports all happen on your machine. Nothing is uploaded unless you separately allow redacted context to reach a model you chose. |
🔬 Evidence, not guessesEvery finding records how it was observed. An independent verifier repeats boundary checks, candidates stay labelled as candidates, and untested coverage stays visible. |
🧪 Tests the real appStarts your service in Docker, macOS Seatbelt or bubblewrap and runs synthetic owner/actor access checks, stateful workflows, bounded fuzzing and isolated Chromium flows. |
🔐 You stay in controlReview mode never executes code. Execution needs a fresh--authorize bound to the exact plan you reviewed. No implicit installs, downloads, redirects or non-loopback targets.
|
🧭 How it works
| Step | Command | What happens |
|---|---|---|
| 1 | inspect |
Inventories files, languages, frameworks, routes, dependencies and security-sensitive code |
| 2 | plan |
Shows the startup command, sandbox, port, synthetic users, test categories and budgets, plus a plan_digest |
| 3 | scan |
Runs source review, scanners and AI specialists; in local modes, starts the app and runs scoped tests |
| 4 | verify |
Repeats a synthetic boundary check after a fix; absence alone never closes an issue |
| 5 | report |
Writes JSON, SARIF, Markdown and offline HTML with evidence, coverage and limits |
| 6 | fix |
Prepares a private patch; applying or rolling it back needs separate authorization |
Three modes control how far a run goes:
| Mode | Behavior | Consent |
|---|---|---|
review |
Reads source; never executes application code | None |
local-passive |
Starts one reviewed service and reads approved local responses | --authorize --plan-digest |
local-active |
Adds synthetic owner/actor, validation, workflow and fuzz scenarios | --authorize --plan-digest |
📦 Install
From PyPI
python -m pip install local-appsec-lab
appsec-lab doctor
From source (macOS / Linux)
git clone https://github.com/aviqentech/local-appsec-lab.git
cd local-appsec-lab
python3 -m venv .venv
. .venv/bin/activate
python -m pip install .
appsec-lab doctor
Windows PowerShell (no script activation or execution-policy change)
git clone https://github.com/aviqentech/local-appsec-lab.git
cd local-appsec-lab
py -3 -m venv .venv
.\.venv\Scripts\python.exe -m pip install .
.\.venv\Scripts\appsec-lab.exe doctor
Use the explicit Windows executable in later examples when the environment is not active.
Prerequisites: Python 3.11+, venv and pip; Git for cloning. Running applications also needs a supported isolation backend and a prepared runtime. Browser and database workflows need Docker with Linux containers. See the installation guide for updates and uninstalling.
🚀 Quick start
Point it at a repository you are authorized to test:
appsec-lab inspect --project /path/to/application
appsec-lab plan    --project /path/to/application
appsec-lab scan    --project /path/to/application --mode review
appsec-lab report  --project /path/to/application --run latest --format html
To test the running app, add a startup command and synthetic scenarios to appsec-lab.yaml, review the plan, then authorize with the plan_digest it printed. The scan is refused if the effective configuration changed since you reviewed it:
appsec-lab scan  --project /path/to/application --mode local-active --authorize --plan-digest PLAN_DIGEST
appsec-lab clean --project /path/to/application
Example appsec-lab.yaml
version: 1
execution:
  command: [node, server.js]
  port: 8765
  health_path: /health
limits:
  requests_per_second: 10
  max_requests: 100
scenarios:
  - id: cross-user-record
    path: /records/42
    category: authorization
    owner_headers: { X-Test-User: alice }
    actor_headers: { X-Test-User: bob }
    marker: SYNTHETIC_ALICE_RECORD_42
Generate a full template with appsec-lab init. All fields are in the configuration guide.
Exit codes
| Code | Meaning |
|---|---|
0 |
Completed without a confirmed finding at or above the fail_on threshold |
1 |
A confirmed finding meets the threshold |
2 |
Partial coverage or exhausted budget; check blocked and untested checks |
3 / 4 |
Invalid configuration or path / authorization or scope rejection |
5 |
Application startup failure |
130 |
Cancelled |
A zero exit status never means the application is secure. Read the report's coverage too. More in usage.
🤖 AI workers and agent skill
Install the skill for your coding agent, per user or per project:
python -m local_appsec_lab.install --global --target all
# Or: python -m local_appsec_lab.install --project /path/to/application --target codex
Targets: Claude Code, Codex, Cursor, Gemini CLI and generic Agent Skills hosts. Installing files, invoking a skill and running model workers are separate capabilities; see integrations.
For automatic specialist workers, set ai.strategy: native with a positive limits.model_tokens budget and bounded limits.model_calls, then explicitly allow sending selected, redacted context:
appsec-lab scan --project /path/to/application --mode review \
  --native-host codex --allow-model-requests
claude, cursor and gemini are also valid --native-host values; their CLIs must be installed and signed in separately. Vendor token and cost caps aren't uniformly enforceable, so reports separate reserved from reported usage. Gemini's individual-account OAuth client was rejected by Google in testing; use supported API or enterprise authentication. Details in AI setup.
🧰 Capabilities
| Capability | Implemented behavior |
|---|---|
| Source review | File/route/dependency inventory, deterministic candidates, bounded interprocedural Python provenance; Semgrep adds supported JS/TS taint rules |
| Specialist orchestration | Distinct scheduled roles, parent-owned shared knowledge, fresh AI verifier and remediation processes, bounded adaptive check proposals |
| Local execution | macOS Seatbelt, Docker Linux containers; experimental Linux bubblewrap |
| Environment setup | Integrity-pinned public Python wheels/npm packages with lifecycle scripts disabled; constrained generated Compose, disposable PostgreSQL/Redis, explicit seeds/migrations |
| Active tests | Synthetic access policies, multi-step state workflows with rollback, bounded scalar-schema fuzzing and isolated Playwright/Chromium workflows |
| Security intelligence | Explicit OSV refresh and offline OSV/Trivy database updates, staleness reporting, sealed persistent deterministic cache |
| Scanners | Offline Semgrep, OSV-Scanner and Trivy adapters on macOS and Docker; no implicit installs or downloads |
| Remediation | Contextual guidance, explicit CVSS v4 vectors, private patch preparation, separately authorized apply/rollback |
| Reports | JSON with schema, SARIF, Markdown and offline HTML; candidates and untested coverage remain visible |
Not in scope yet: whole-program proof, arbitrary Compose files, inferred business policies, mobile emulators and ZAP execution. Recognizing a runtime doesn't mean every framework can be launched. Fix generation covers a narrow Python debug rewrite or a reviewed Python/JSON replacement. See the requirement-by-requirement status.
🖥️ Platform support
| Platform / host | Verification boundary |
|---|---|
| 🍎 macOS | Seatbelt and Docker applications, browser/database workflows, scanners and Codex/Claude/Cursor model workers tested locally |
| 🐧 Linux | Native source/installer and Linux Docker tested; bubblewrap passed with a trusted root controller, unprivileged restrictions documented |
| 🪟 Windows | Native source/installer tests; Linux-container execution needs Docker Desktop and a native Windows test machine |
| 🧩 Agent hosts | Skill installation supports all four; worker verification and skill discovery are tracked separately |
Exact measured results and open prerequisites are in validation.
🛡️ Safety model
- Authorization is per run.
--authorizebinds the repository fingerprint, plan digest, mode, port, categories, budgets and expiry. Changed source or configuration is rejected. - Loopback only. Requests go to explicit
127.0.0.1/::1on the approved port; redirects, proxies, encoded or mapped addresses and other hosts are refused. - Synthetic data only. State-changing tests need disposable synthetic data and an explicit rollback.
- Untrusted output. Model and scanner output can't run commands; the parent checks categories, source spans and evidence, and model findings stay candidates until verified.
- Private state.
.appsec-lab/holds local security evidence and must stay out of version control.
Read the full security model.
📚 Documentation
🔄 Releases
Every pull request merged into main publishes a new PyPI release once CI passes. The workflow picks the next unused patch version, syncs package, CLI and changelog versions, validates the distributions, publishes through the Trusted Publisher and verifies a fresh public install. Direct pushes and unmerged PRs don't publish. See the release process.
🛠️ Development
python -m pip install '.[dev]'
make lint
python -m pytest -q
python -m build
Runtime tests need their documented platform and preloaded images. A skipped integration test is not a successful one.
🤝 Contributing and security
Contributions are welcome. Start with CONTRIBUTING and the code of conduct. Report vulnerabilities privately as described in SECURITY, not in public issues.
📄 License
Apache-2.0. See LICENSE and NOTICE.
appsec.aviqen.com
Built by AVIQEN · Assess only what you own or are authorized to test.
1 maintainer

Metadata
1 maintainer
Release files for local-appsec-lab 0.2.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| local_appsec_lab-0.2.3.tar.gz | 1.4 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| local_appsec_lab-0.2.3-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.6 MB
Release files / local_appsec_lab-0.2.3.tar.gz
| Download URL | local_appsec_lab-0.2.3.tar.gz |
|---|---|
| Size | 1.4 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d0d0a45e93572287ec4766e7d93bb5aec03f6298a12781a8e6e3bf7032ade1aa
|
|
BLAKE2b-256 checksum How to use checksums |
698c5ca5390f530df3fad785406091d06bd9bdc67a1c9848624ec7bcaeb0163a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logRelease files / local_appsec_lab-0.2.3-py3-none-any.whl
| Download URL | local_appsec_lab-0.2.3-py3-none-any.whl |
|---|---|
| Size | 213.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7201db121df3db97e1acf159fc6faa18422ce20b01f6ed490880a8a8477a1cd4
|
|
BLAKE2b-256 checksum How to use checksums |
ce75797123c2c1f141919a3c259dbd5a7901694640ab604fe4c27cea10bcd3ca
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logSecurity for local-appsec-lab 0.2.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for local_appsec_lab-0.2.3.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














