
Marshal — an agent ledger



A vendor-neutral, open-source ledger for enterprise AI agents. Any format in, any format out, with versions, diffs, portability and audit across every platform.
Live demo · Documentation · Getting started
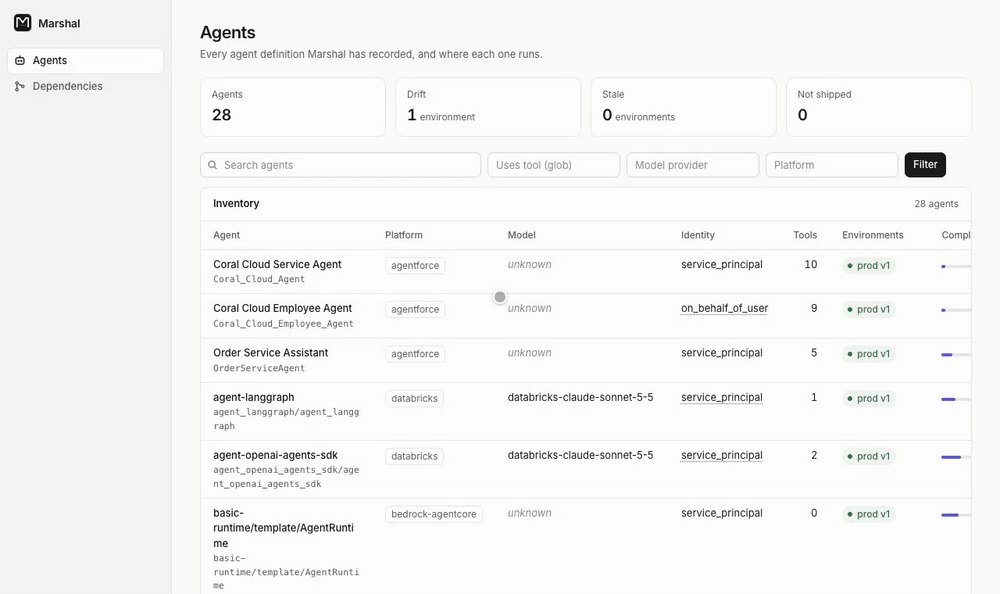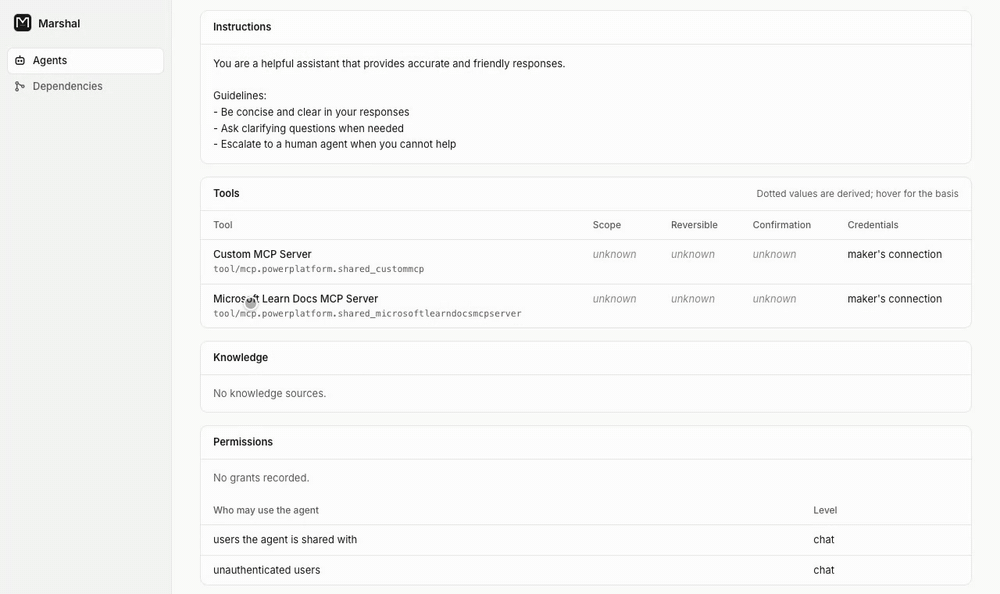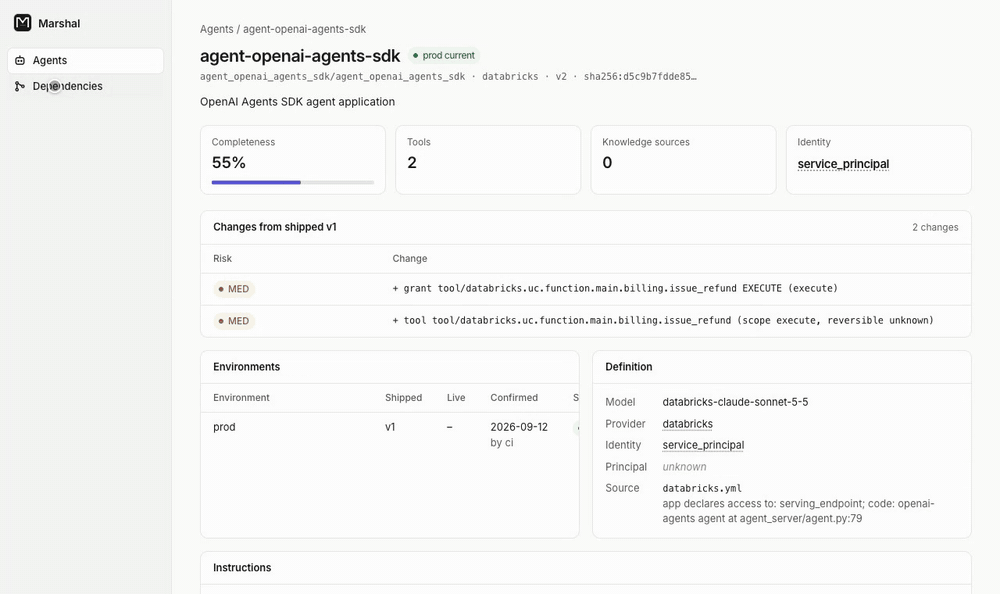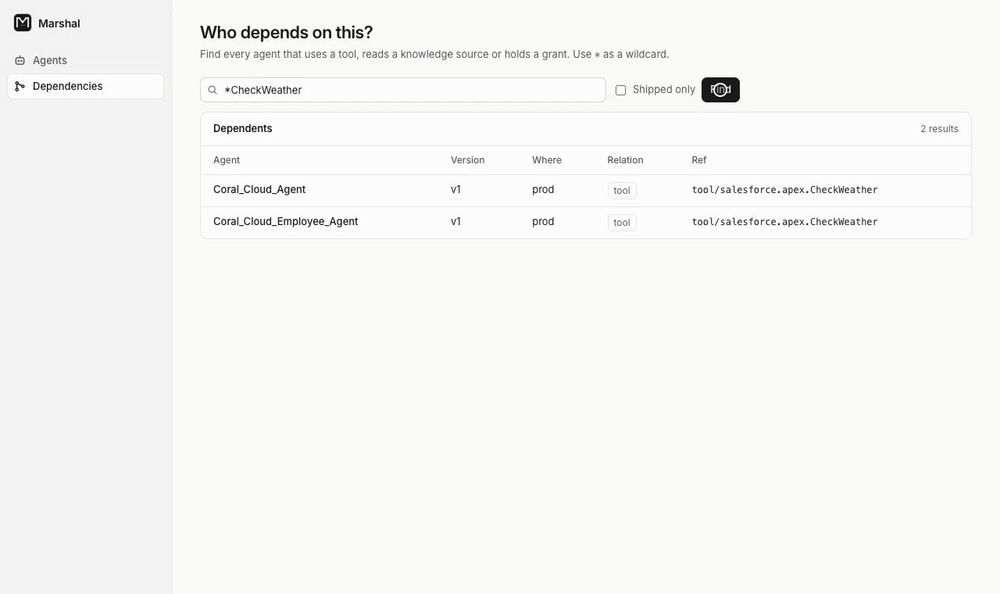
Marshal reads the agent definitions teams already produce: Databricks bundles, Copilot Studio agents, Bedrock templates, Agentforce metadata, agent code and the open standards. It builds a normalized, versioned record of every agent: what model it asks for, what tools and data it can reach, and who it acts as. Every field says where its value came from, and nothing is guessed.
Status: alpha. Before 1.0 a minor release may change the ledger model, the ingest API or the command line; the changelog lists each such change.
What it does
- Inventory of every agent across platforms, with versions, deployments, and each record's completeness.
- Risk-ranked review: pull requests that change an agent get a comment that lists permission escalations, new write tools and model changes first.
- Drift and freshness: compares what is live with what was shipped, and shows how recently each record was confirmed and by which channel.
- Dependencies: "who uses this tool, this knowledge source, this permission?" across every platform.
- Translation between formats, with a fidelity report computed by reading the result back.
- Portability scores for moving an agent to another platform, from a community-maintained capability matrix.
- No shared secrets: pipelines push records authenticated by their CI provider's OIDC token. Marshal never connects to agent platforms.
How it runs
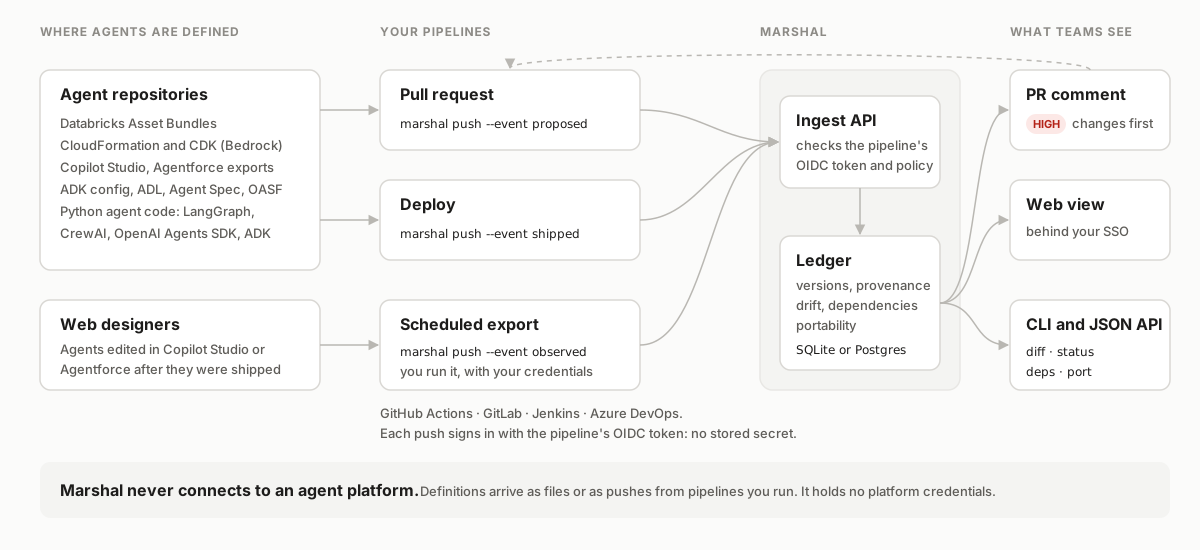
Pipelines you already run record each agent: a pull request records the proposed definition and gets a comment ranking its changes, a deploy records what was shipped, and an optional scheduled export records what is live in a web designer. See the GitHub Action, Jenkins and Azure DevOps and Deployment.
Formats
| Source | Read | Write |
|---|---|---|
| Databricks Asset Bundles (Genie spaces, agent apps) | ✓ | |
| AWS CloudFormation and CDK (Bedrock Agents, AgentCore) | ✓ | Bedrock Agents |
| Microsoft Copilot Studio (agent workspaces, solutions) | ✓ | ✓ |
| Salesforce Agentforce (Agent Script, legacy metadata) | ✓ | Agent Script |
| Google ADK Agent Config | ✓ | ✓ |
| Vertex AI Agent Engine (saved API responses) | inventory | |
| Python agent code (OpenAI Agents SDK, LangChain/LangGraph, Google ADK, CrewAI, direct model API calls) | ✓ | |
| ADL, Open Agent Spec, AGNTCY OASF | ✓ | ✓ |
| Marshal file: a hand-written definition for agents no reader covers, recorded as attested | ✓ | ✓ |
Try it
Browse the live demo, or build it yourself from 28 public agents, with nothing to install but uv:
$ uvx --from 'marshal-ledger[server]' marshal demo
$ uvx --from 'marshal-ledger[server]' marshal web --db demo.sqlite
Or pip install 'marshal-ledger[server]', then marshal demo and marshal web --db demo.sqlite. marshal demo downloads the agents' definitions from their public GitHub repositories, pinned to a commit.
Then on your own agents. See Getting started:
$ marshal read path/to/bundle                        # print ledger records
$ marshal collect path/to/bundle --target prod --event shipped
$ marshal ls                                         # every agent, latest version, where it is shipped
$ marshal diff finance/invoice_agent                 # proposed against shipped, ranked by risk
$ marshal status finance/invoice_agent               # shipped vs live per environment, drift, freshness
$ marshal deps "*CheckWeather" --shipped             # who depends on this, and where it is live
$ marshal convert agent.adl.yaml --to agent-spec     # translate, with a fidelity report
$ marshal port finance/invoice_agent --to all        # portability to every platform
$ marshal web                                        # browse the store
collect writes to a local SQLite store (marshal.sqlite, or --db / $MARSHAL_DB). In a shared deployment, pipelines run marshal push or the GitHub Action against the ingest API. Optional scheduled workflows export agents built in a web designer, such as Copilot Studio and Agentforce, and report drift from what was shipped.
Documentation
The documentation is published at marshal-ledger.github.io/marshal.
- Getting started
- Guides: Copilot Studio inventory, pull request review, agents in code, drift, ADK to Agent Spec, audit evidence
- How Marshal compares with platform admin tools, observability, AI gateways, registries and governance platforms
- Design: the problem, architecture, security and network posture, roadmap
- Ledger model v0: records, provenance, version hashing, the version store, risk ranking, freshness
- Conversion and fidelity and Portability
- Formats: Databricks, CloudFormation, Copilot Studio, Agentforce, ADK Agent Config, Vertex AI Agent Engine, Python agent code, ADL, Agent Spec, OASF, Marshal file
- Platform exportability: what each closed platform exposes
- Ingest API, GitHub Action, Jenkins and Azure DevOps and Deployment
- Security review: what is stored, authentication, network, supply chain, retention and audit, for security reviewers
Development
$ pip install -e '.[dev]'
$ python scripts/fetch_fixtures.py     # golden fixtures: real public agent definitions, pinned by commit
$ pytest
See Contributing. Golden fixtures are fetched rather than committed, so each file stays under its upstream license. After changing the model, regenerate the schema with python scripts/generate_schema.py. Report vulnerabilities as described in Security.
License
Marshal is licensed under the Apache License 2.0.
1 maintainer

Metadata
1 maintainer
Release files for marshal-ledger 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| marshal_ledger-0.3.0.tar.gz | 349.9 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| marshal_ledger-0.3.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 542.0 kB
Release files / marshal_ledger-0.3.0.tar.gz
| Download URL | marshal_ledger-0.3.0.tar.gz |
|---|---|
| Size | 349.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
610a84801787db132fbdfefe5881d8d969a055c0e6b9cc8b2e31946c5aeec355
|
|
BLAKE2b-256 checksum How to use checksums |
d88952f01f3cc2c2ff473fe7a108470503ff93cb06e17c6c80f99fd14fb53bde
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logRelease files / marshal_ledger-0.3.0-py3-none-any.whl
| Download URL | marshal_ledger-0.3.0-py3-none-any.whl |
|---|---|
| Size | 192.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
352cd1f7ccbf2e981fbc188e3f8525765dbd290c7f801f0f1d0c43208894946c
|
|
BLAKE2b-256 checksum How to use checksums |
4baf742b4b8a1bcbca4c6430f9ece669a7bce63c6c629958532025fdc7b1d0ad
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logSecurity for marshal-ledger 0.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for marshal_ledger-0.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














