
MaskGuard
AI-powered PII discovery and query-time, role-based masking for PostgreSQL, MySQL and SQLite.
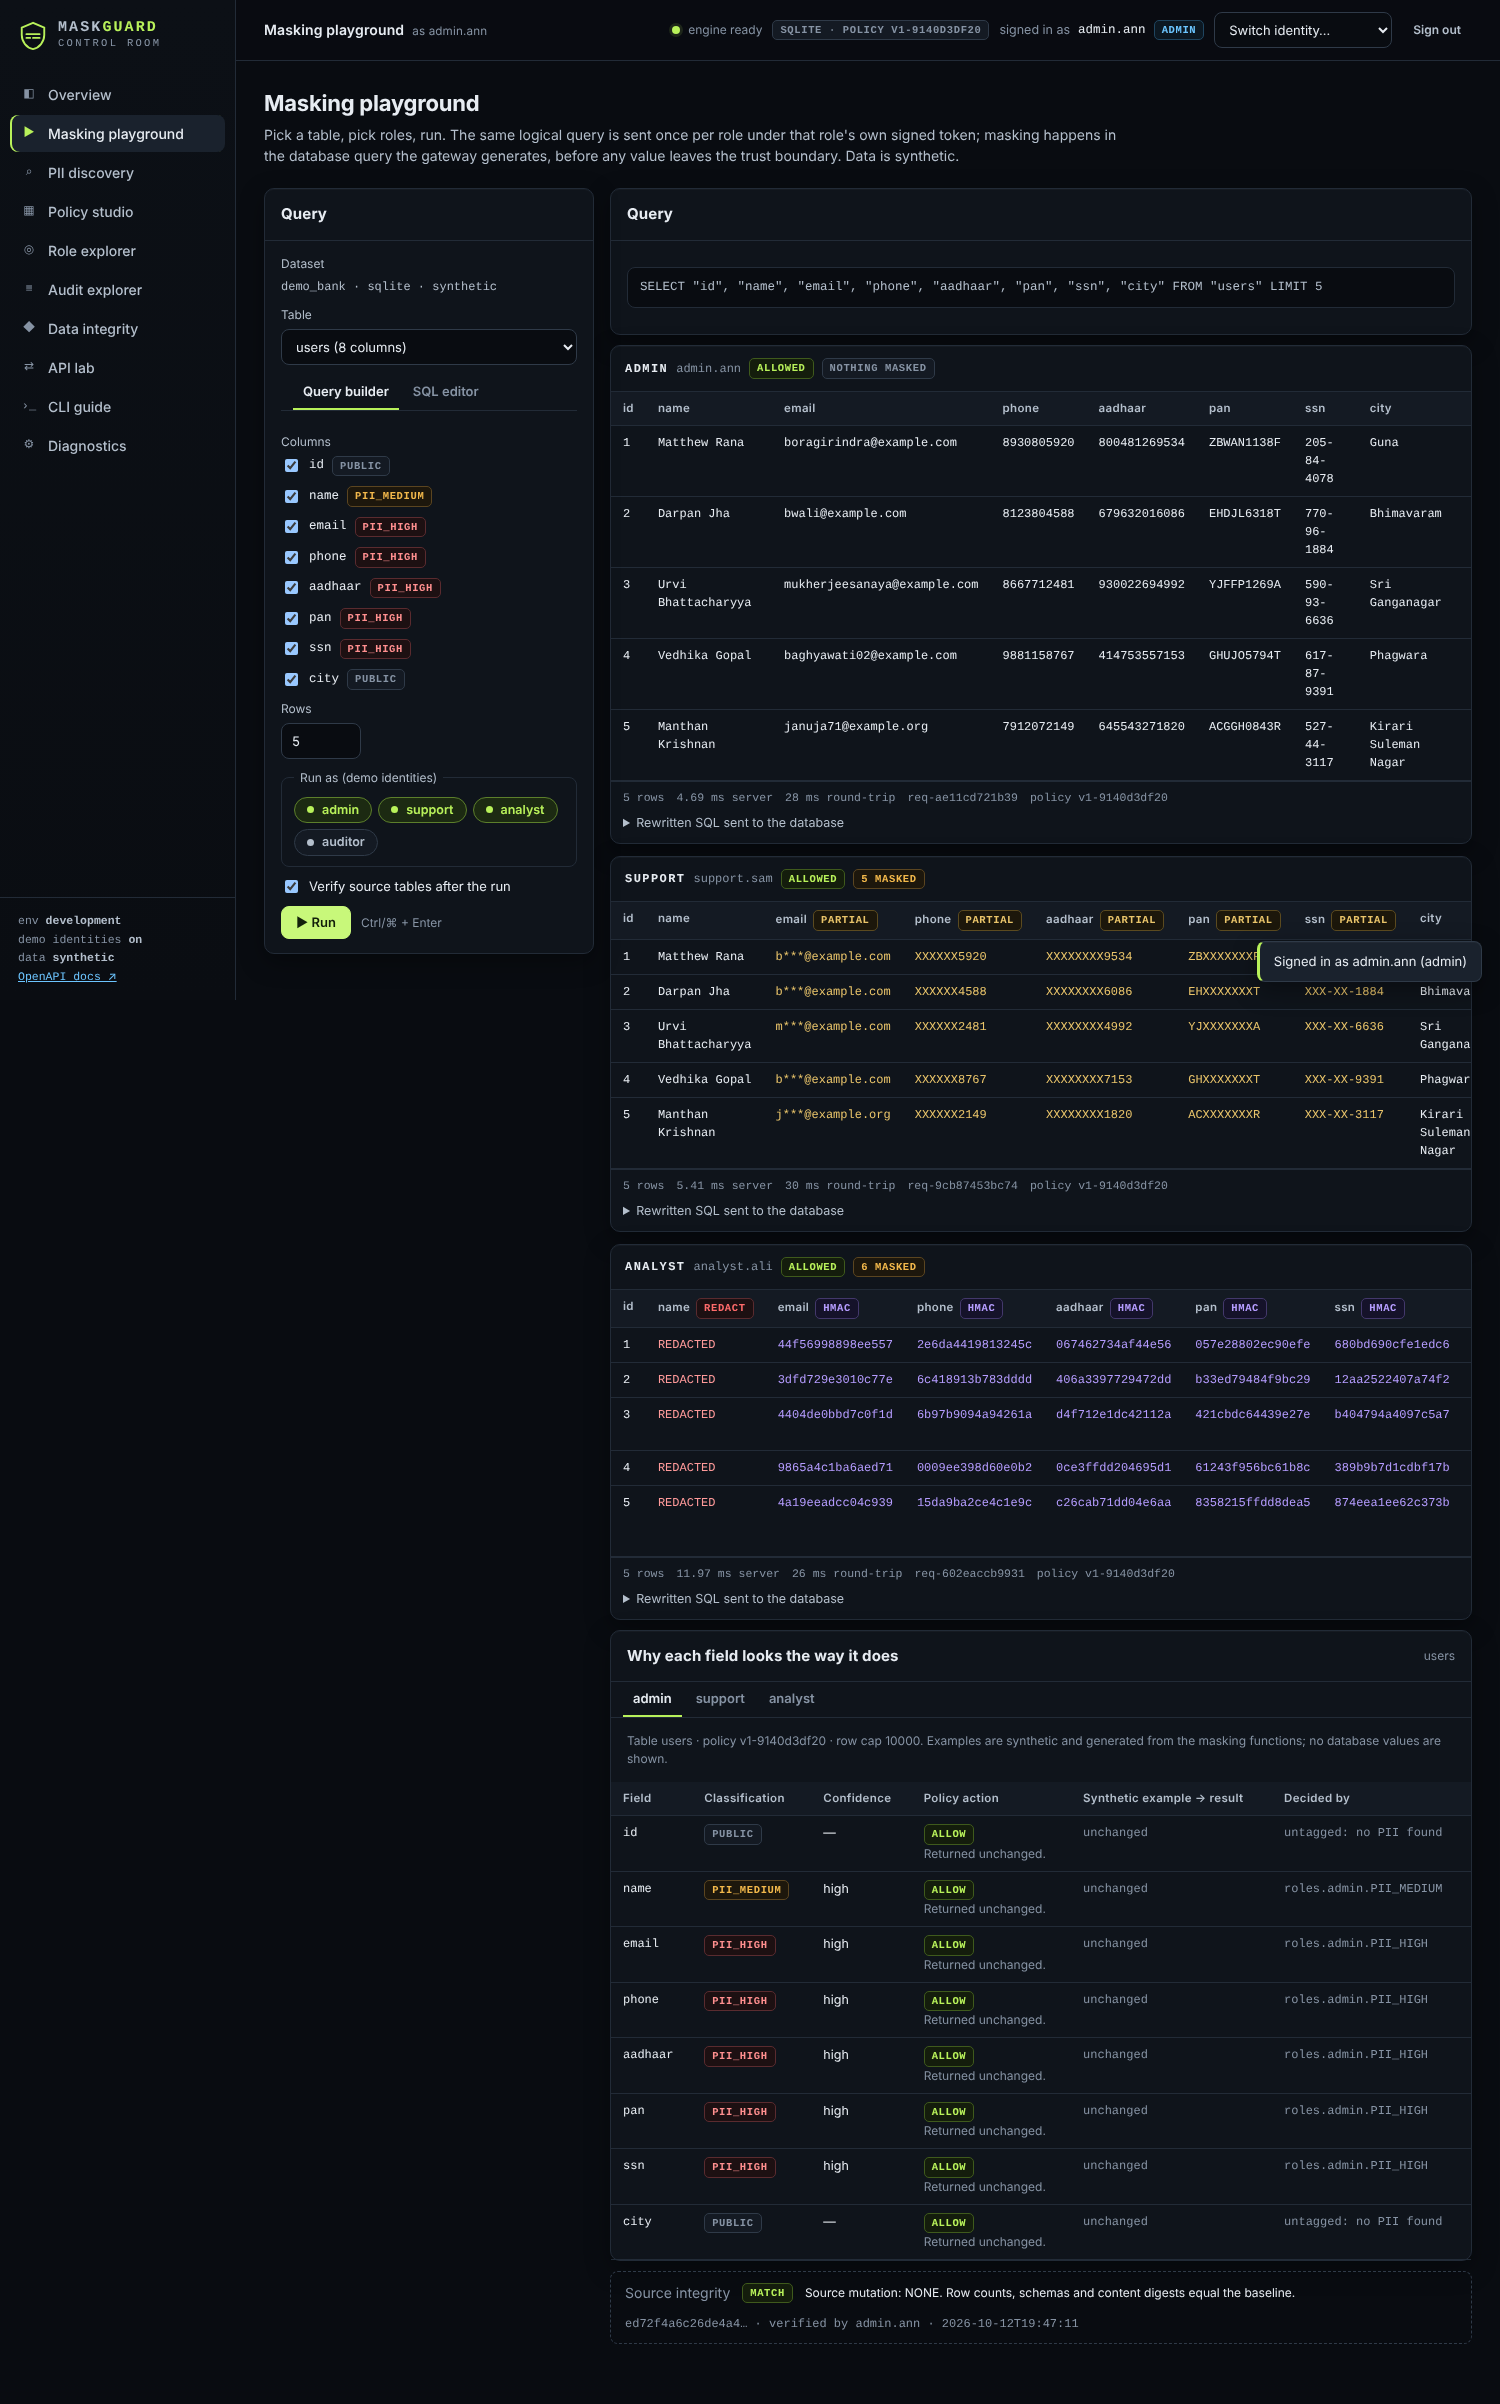
MaskGuard is a gateway between people and the database. It finds sensitive columns by looking at their values (a LightGBM classifier plus checksum validators for Aadhaar, PAN, GSTIN, cards, IBAN and more). It rewrites every query so the database itself returns only what the caller's role may see. It watches for probing, and records every decision in a hash-chained audit log. Stored data never changes.
| Role | Sees |
|---|---|
| Admin | real values |
| Support | partial masks: 4111-XXXX-XXXX-1111, XXX-XX-6789, r***@bank.in, rounded balances |
| Analyst | keyed tokens (joinable, not reversible); no individual balances |
| Auditor | REDACTED, plus the audit log, policies and integrity proofs |
Install and try it
pip install maskguard
export MASKGUARD_HMAC_KEY=dev-only-hmac-key-change-me     # Windows PowerShell: $env:MASKGUARD_HMAC_KEY="..."
maskguard                                                # console with synthetic demo data (created in ./data/)
maskguard compare "SELECT name, ssn, phone FROM users LIMIT 2" --roles admin,support,analyst,auditor
maskguard serve                                          # REST API + Control Room at http://127.0.0.1:8000/ui/
Demo logins: admin.ann, support.sam, analyst.ali and auditor.aud, each with password <role>123. Data,
the audit log and the scanner registry are written to ./data/ in the folder you run it from.
To use your own database, set MASKGUARD_DB (postgresql://… or mysql://…). For real data, run in production
mode (MASKGUARD_ENV=production): it refuses to start on any unsafe setting.
Results
- PII discovery: 0.965 F1 with misleading column names and 5 sample values per column; the benchmark baseline scores 0.844.
- Attack suite: 0 of 17 bypass and inference attacks leak, against 14–15 of 17 for output-only masking.
- Tests: 476 tests on SQLite, PostgreSQL 16 and MySQL 8.4.
- Latency: about 8 ms added per query.
Learn more
- README and screenshots
- Beginner's guide: every term, with diagrams and step-by-step workflows
- Deployment guide
- 8-minute walkthrough video
Noisy analyst aggregates are experimental and refused in production until an independent privacy review. Licensed under Apache-2.0.
1 maintainer

Metadata
1 maintainer
Release files for maskguard 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| maskguard-1.0.0.tar.gz | 23.0 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| maskguard-1.0.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 23.7 MB
Release files / maskguard-1.0.0.tar.gz
| Download URL | maskguard-1.0.0.tar.gz |
|---|---|
| Size | 23.0 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7f54e97433bc5b9832c796e5aae1da847ef1f78f3f10cdb46414551920975fe1
|
|
BLAKE2b-256 checksum How to use checksums |
cce89266a7ddf3fd7262de4349f216008d0064afe35521aabbd104dbb26397de
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / maskguard-1.0.0-py3-none-any.whl
| Download URL | maskguard-1.0.0-py3-none-any.whl |
|---|---|
| Size | 693.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7f9857728d5cf3719c8fee3134717bb1d09986e7ebcd89e3f479b0fd43272804
|
|
BLAKE2b-256 checksum How to use checksums |
70d96d23ba5f0945554f39951fb42188e644d7689fcacc33046c25d5735532f5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency log













