
Cyberbro MCP Server
Extract IoCs from messy text and analyze them with Cyberbro.
🌐 demo.cyberbro.net
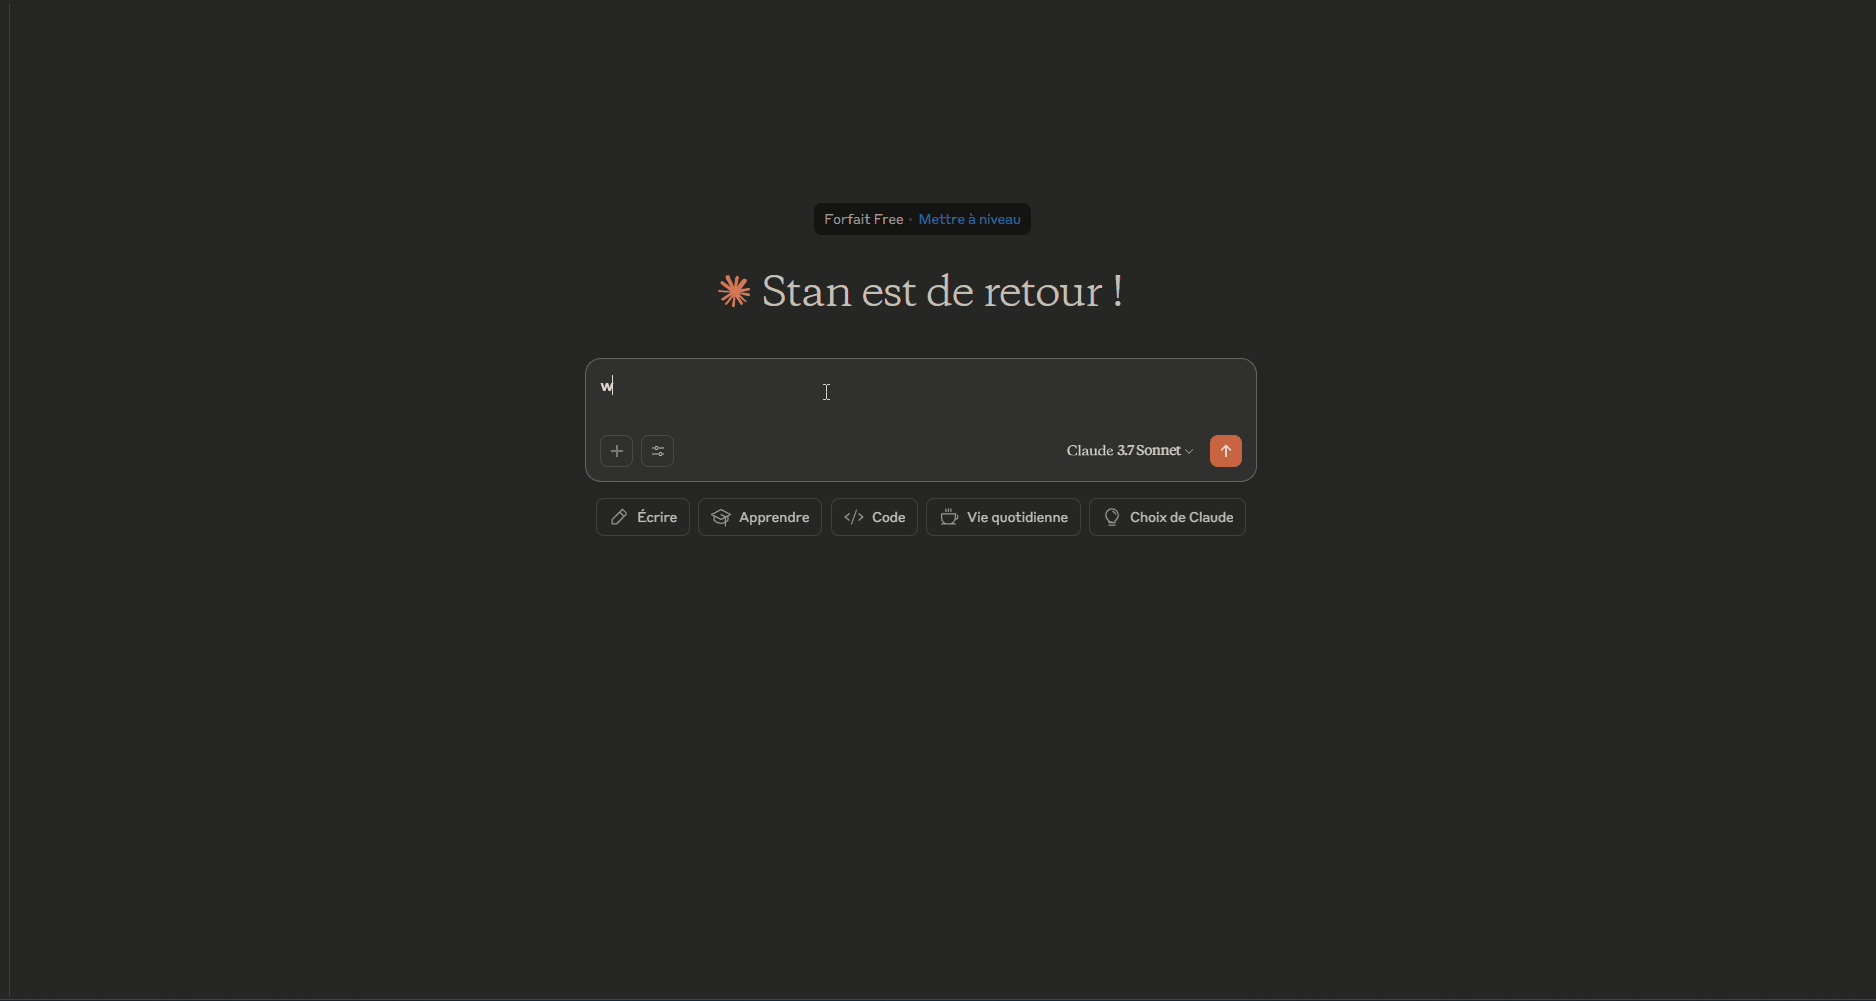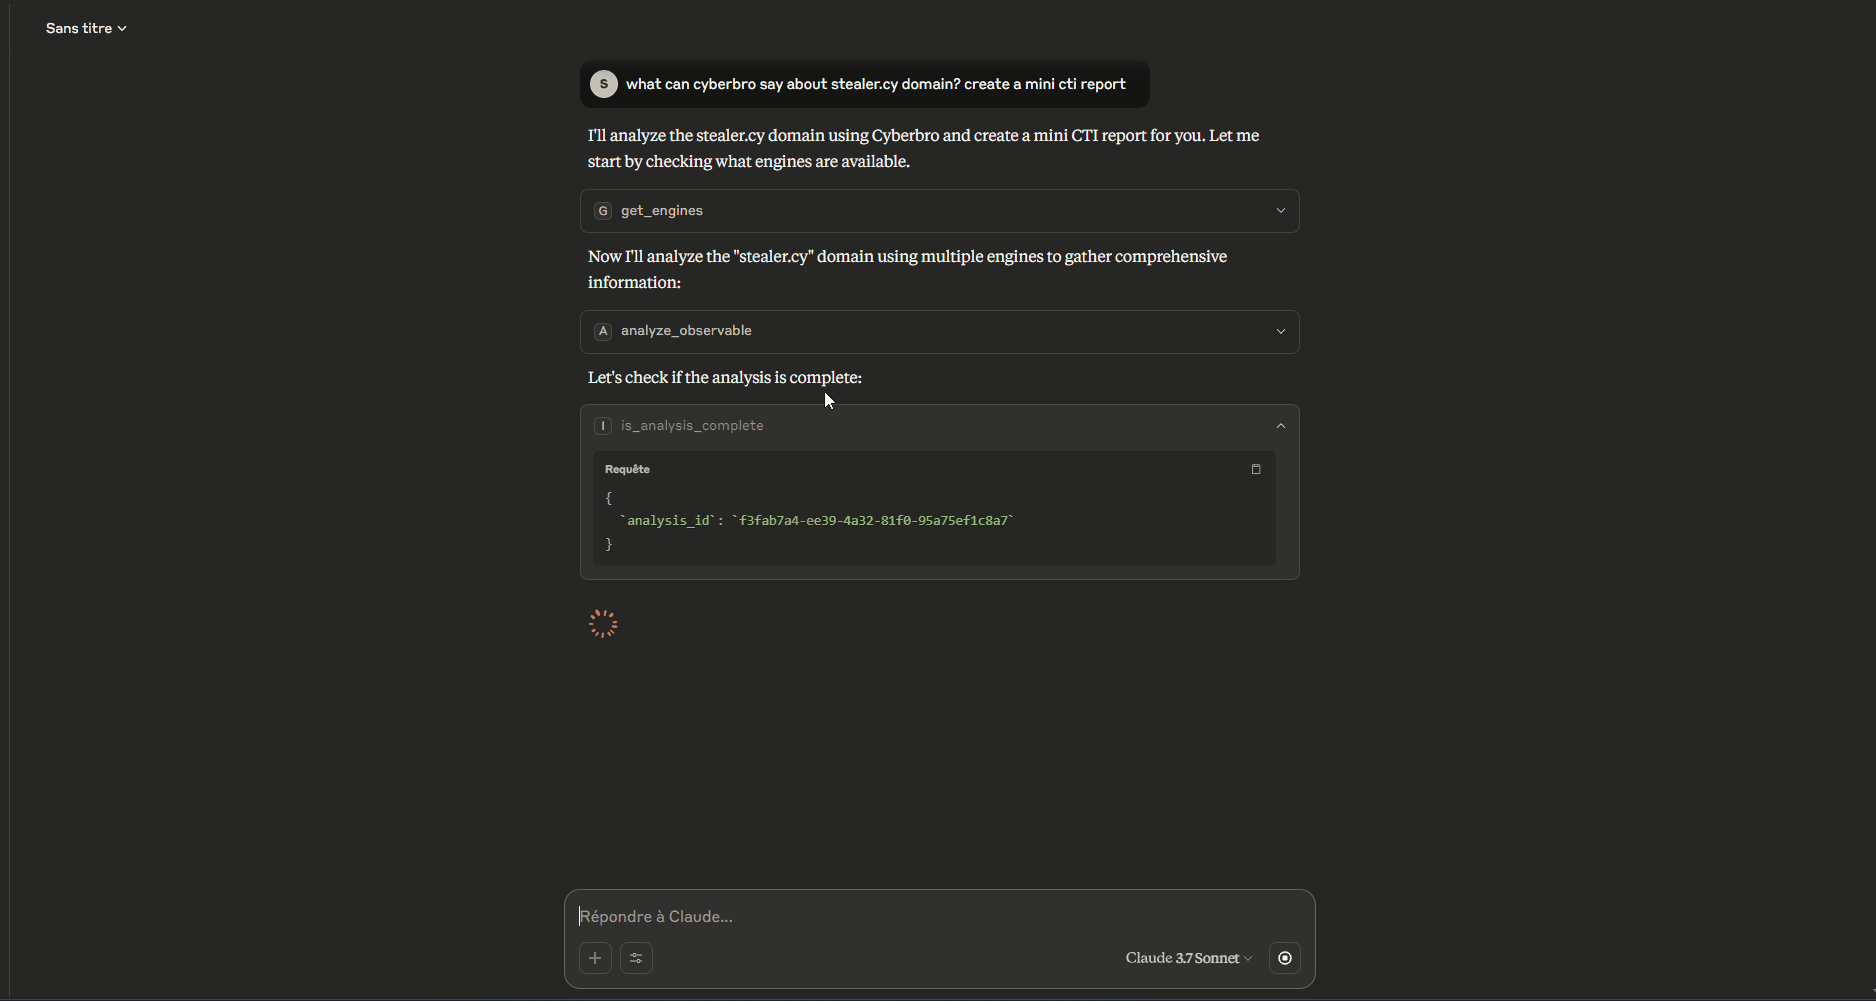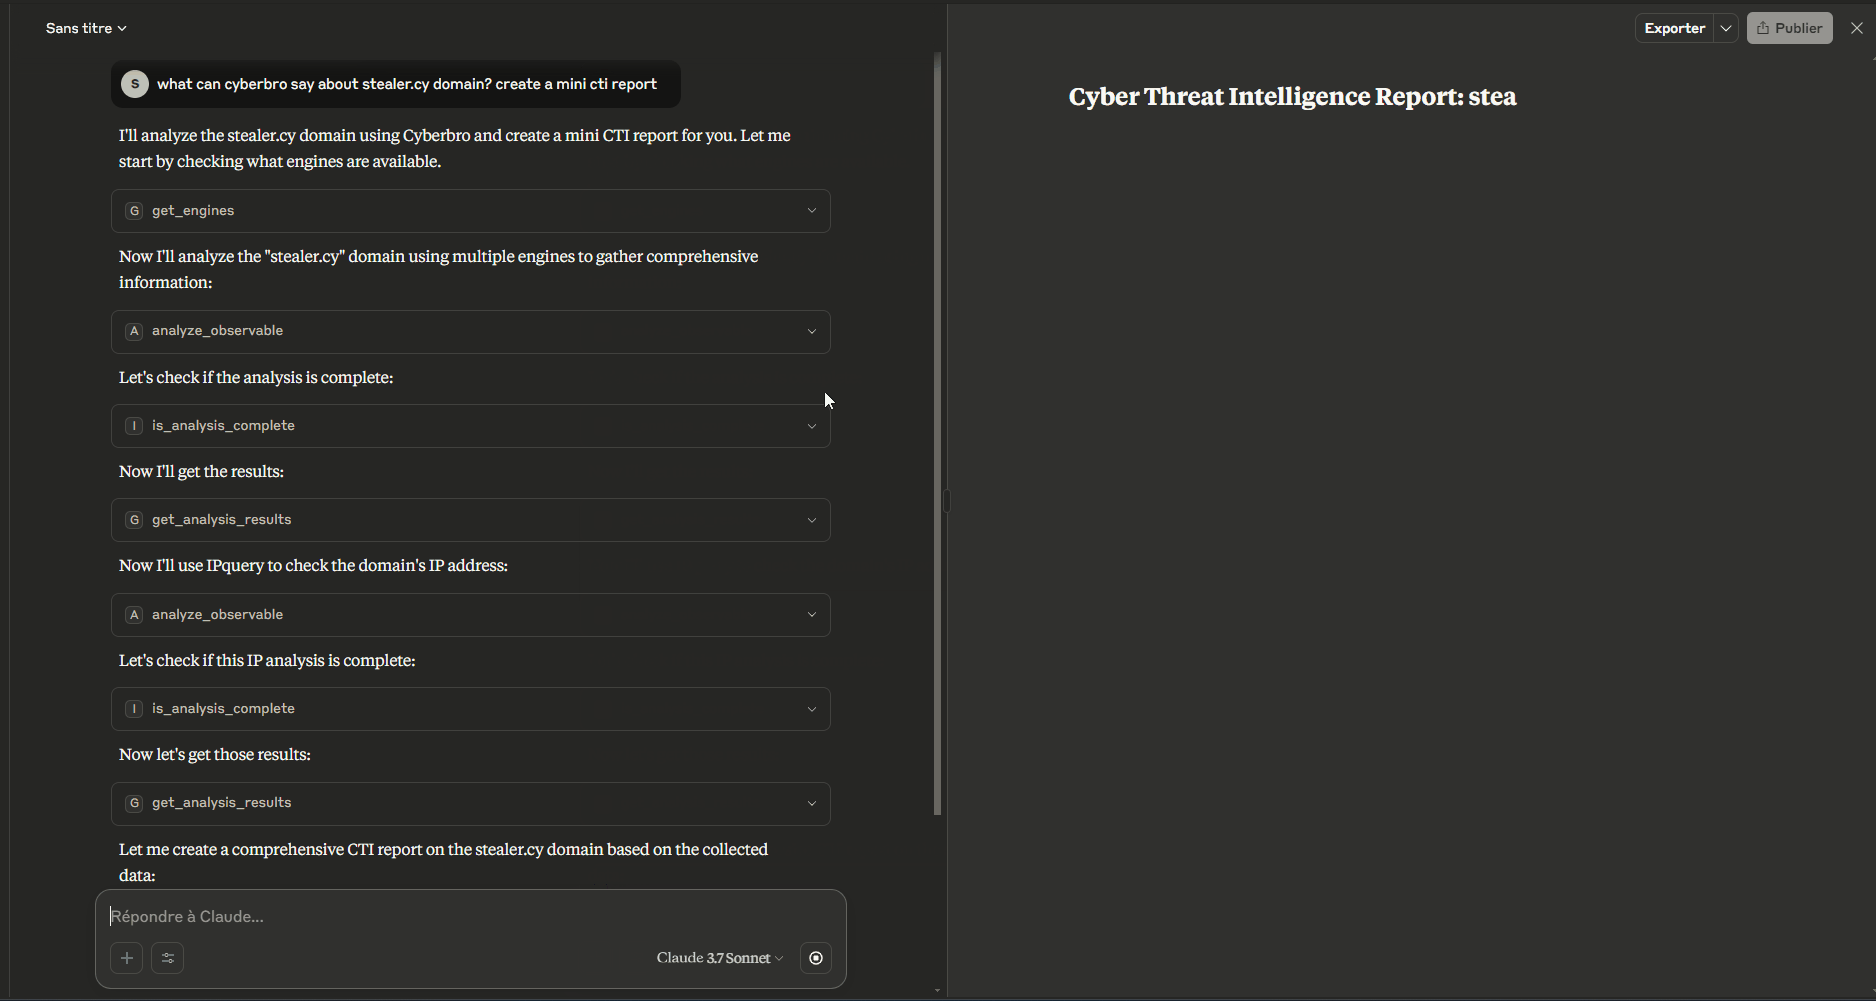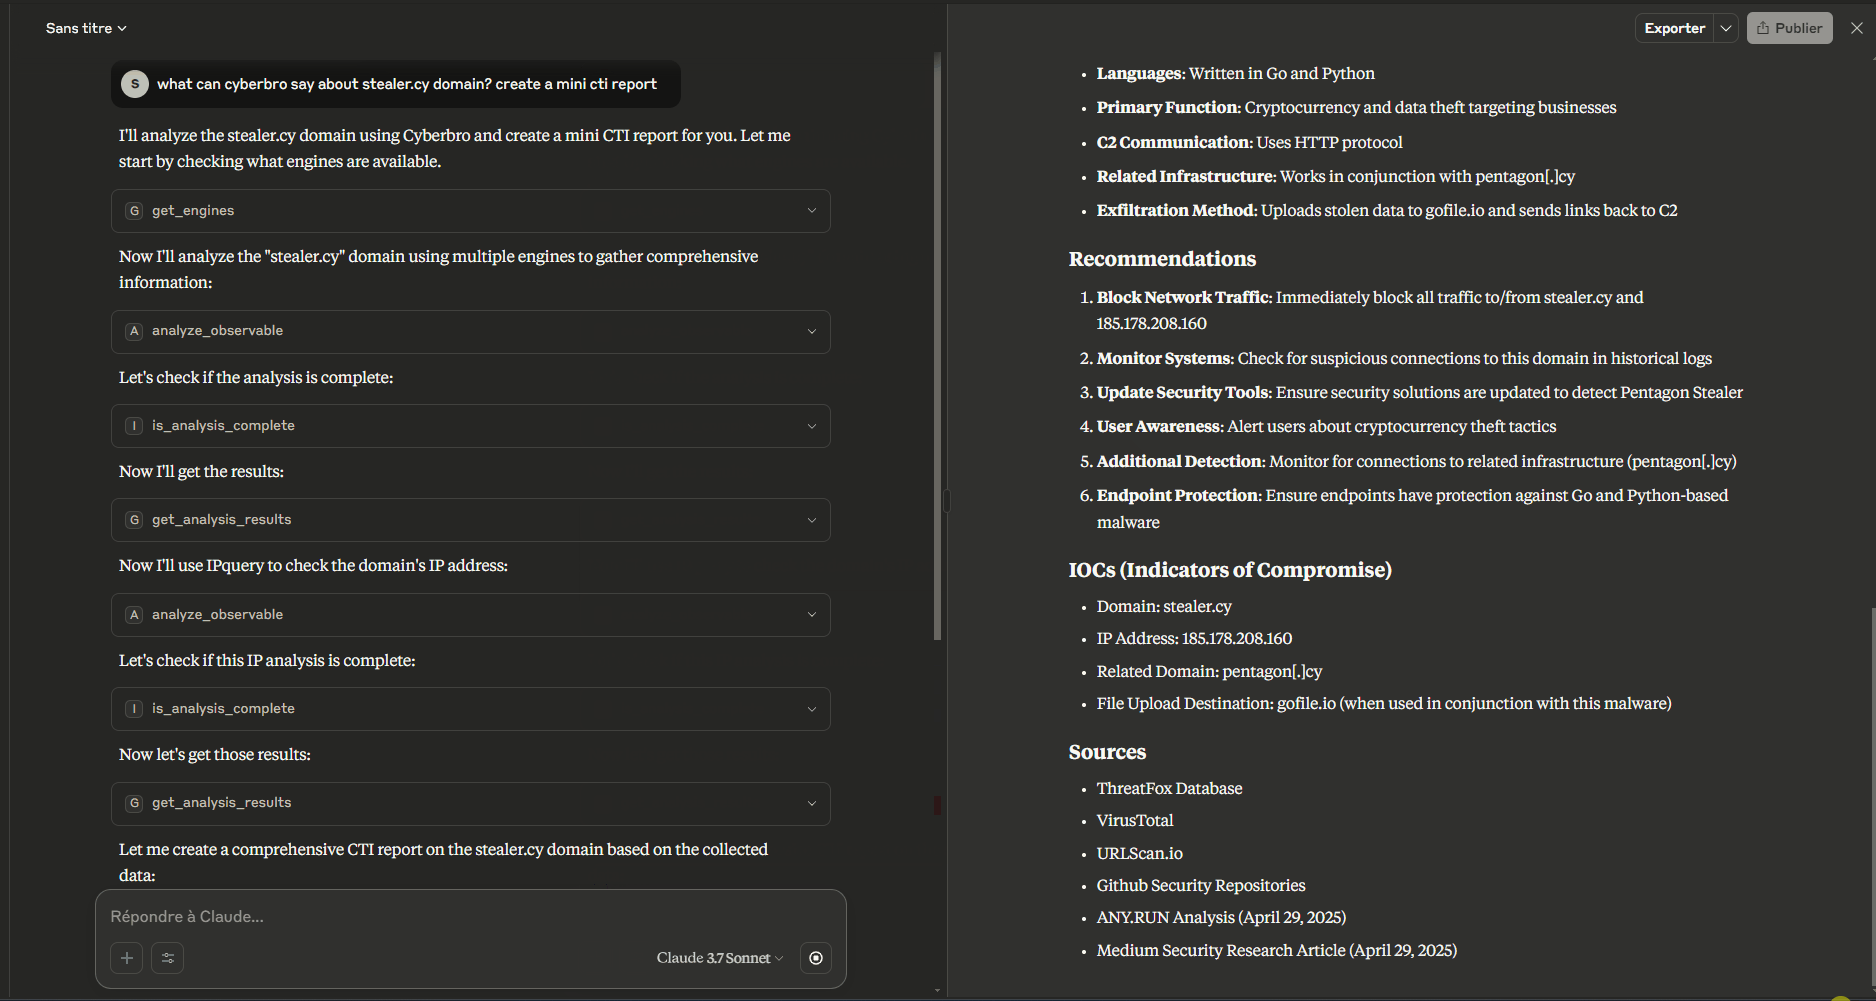
Model Context Protocol server for Cyberbro.
This project is packaged as a standard Python distribution and can be launched with:
uvx mcp-cyberbropip install mcp-cyberbrothenmcp-cyberbro
Why this server
- Analyze observables (IP, domain, URL, hash, etc.) via Cyberbro engines.
- Integrate threat-analysis actions directly in MCP-capable assistants.
- Run with
stdio,sse, orstreamable-httptransports. - Compatible with any MCP client that supports one of these transports.
Installation
Use with uvx (standalone)
uvx mcp-cyberbro --cyberbro_url http://localhost:5000
Use with pip
pip install mcp-cyberbro
mcp-cyberbro --cyberbro_url http://localhost:5000
Local development
pip install -e .
mcp-cyberbro --cyberbro_url http://localhost:5000
Docker
Default container command starts in streamable-http mode on port 8000.
docker run --rm -p 8000:8000 \
  -e CYBERBRO_URL=http://host.docker.internal:5000 \
  ghcr.io/stanfrbd/mcp-cyberbro:latest
To run in stdio mode, a custom Dockerfile is required:
FROM ghcr.io/stanfrbd/mcp-cyberbro:latest
CMD ["mcp-cyberbro", "--transport", "stdio"]
Build and use it:
docker build -t mcp-cyberbro-stdio .
docker run -i --rm -e CYBERBRO_URL=http://host.docker.internal:5000 mcp-cyberbro-stdio
Configuration
Copy .env.example and set at least:
CYBERBRO_URL(required)
Supported environment variables:
CYBERBRO_URLAPI_PREFIX(default:api)SSL_VERIFY(true/false)MCP_TRANSPORT(stdio,sse,streamable-http)MCP_HOSTMCP_PORTMCP_MOUNT_PATHMCP_SSE_PATHMCP_STREAMABLE_HTTP_PATH
CLI flags are also available and override env values.
MCP Client Integration
You can use this server with Claude Desktop, Claude Code, Cursor, OpenAI-compatible MCP clients, or any other MCP client.
Example config using uvx:
{
  "mcpServers": {
    "cyberbro": {
      "command": "uvx",
      "args": ["mcp-cyberbro"],
      "env": {
        "CYBERBRO_URL": "http://localhost:5000"
      }
    }
  }
}
To use Docker with stdio transport (required by some MCP clients), build a custom image as shown in the Docker section above, then reference it:
{
  "mcpServers": {
    "cyberbro": {
      "command": "docker",
      "args": ["run", "-i", "--rm", "-e", "CYBERBRO_URL", "mcp-cyberbro-stdio"],
      "env": {
        "CYBERBRO_URL": "http://localhost:5000"
      }
    }
  }
}
Usage in VSCode - Example
Create .vscode/mcp.json
{
	"servers": {
		"mcp-cyberbro": {
			"type": "stdio",
			"command": "uvx",
			"args": [
				"mcp-cyberbro"
			],
			"env": {
				"CYBERBRO_URL": "http://127.0.0.1:5000"
			}
		}
	}
}
MCP Registry Metadata
server.json is included for MCP Registry publication and points to PyPI package mcp-cyberbro.
Release Pipelines
Release-created workflows:
.github/workflows/publish-test-pypi.yml.github/workflows/publish-pypi.yml.github/workflows/publish-mcp-plugin.yml
Available Tools
analyze_observableis_analysis_completeget_analysis_resultsget_enginesget_web_url
Example Prompts
Here are practical prompt examples you can use with any MCP-capable assistant connected to Cyberbro.
Getting Indicator Details
- Cyberbro: Check indicators for target.com
- Can you check this IP reputation with Cyberbro? 192.168.1.1. Use github, google and virustotal engines.
- I want to analyze the domain example.com. What can Cyberbro tell me about it? Use max 3 engines.
- Analyze these observables with Cyberbro: suspicious-domain.com, 8.8.8.8, and 44d88612fea8a8f36de82e1278abb02f. Use all available engines.
Observable Analysis
- I found this (hash|domain|url|ip|extension). Can you submit it for analysis to Cyberbro and analyze the results?
OSINT Investigation
- Create an OSINT report for the domain example.com using Cyberbro. Use all available engines and pivot on the results for more information. Use a maximum of 10 analysis requests.
Acknowledgements
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for mcp-cyberbro 0.0.6
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| mcp_cyberbro-0.0.6.tar.gz | 11.7 kB | With provenance | Details for mcp_cyberbro-0.0.6.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| mcp_cyberbro-0.0.6-py3-none-any.whl | Python 3 | none | any | Details for mcp_cyberbro-0.0.6-py3-none-any.whl |
Total release size: 22.8 kB
Release files / mcp_cyberbro-0.0.6.tar.gz
| Download URL | mcp_cyberbro-0.0.6.tar.gz |
|---|---|
| Size | 11.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
595ac89c93c2950ed86ec6bdccb35058336b9206f53244251c081b801cb59aa8
|
|
BLAKE2b-256 checksum How to use checksums |
bdc354d1a9c8aa3ca563cc5b4cf8638061293b543fdbdfb58ecd3a28aa1be330
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / mcp_cyberbro-0.0.6-py3-none-any.whl
| Download URL | mcp_cyberbro-0.0.6-py3-none-any.whl |
|---|---|
| Size | 11.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
b492e986047b6379d4ae331ffba94c1048f23319a4a38bbb6a0eac93e125e322
|
|
BLAKE2b-256 checksum How to use checksums |
10d67fcb44fb1b18814bd2b9e4b5e95d48f30ebc79f1b1ef8cb49a95ae170f95
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logSecurity for mcp-cyberbro 0.0.6
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for mcp_cyberbro-0.0.6.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














