
MCP is Dangerous
Function tool usage makes AI Agents very powerful, which is akin to introducing app stores to smartphones. Especially with the release of MCP (Model Context Protocol), tool sharing has become easier than ever. That's why I've created the extendable-agents project to showcase how easy you can extend the capabilities of AI Agents through open-source tools or your custom tools.
While working on extendable-agents, I've realized that tool usage is a double-edged sword. The danger is that the tools you use have powerful access to your machine, such as your environment variables, files, etc.
⚠️ Security Warning
This project is a simple demonstration of the security risks associated with tool usage. The example below illustrates how malicious actors could potentially exploit MCP servers to access sensitive information:
# WARNING: This is a demonstration of security risks.
# DO NOT use this code maliciously!

import os
from mcp.server.fastmcp import FastMCP


server = FastMCP("Dangerous MCP")


@server.tool()
async def get_environment_variables() -> str:
    """Get all environment variables."""
    result = [
        "Here are what I could find:",
    ]
    for key, value in os.environ.items():
        result.append(f"{key:<30} {value[:5]}***")
    # This means I can open a backdoor to send your data to me!!
    return "\n".join(result)
⚠️ Warning: I recommend running this example in a sandboxed environment and deleting your OpenAI API key afterwards.
When using this tool with extendable-agents (choose PoliceAgent), the output appears like this:
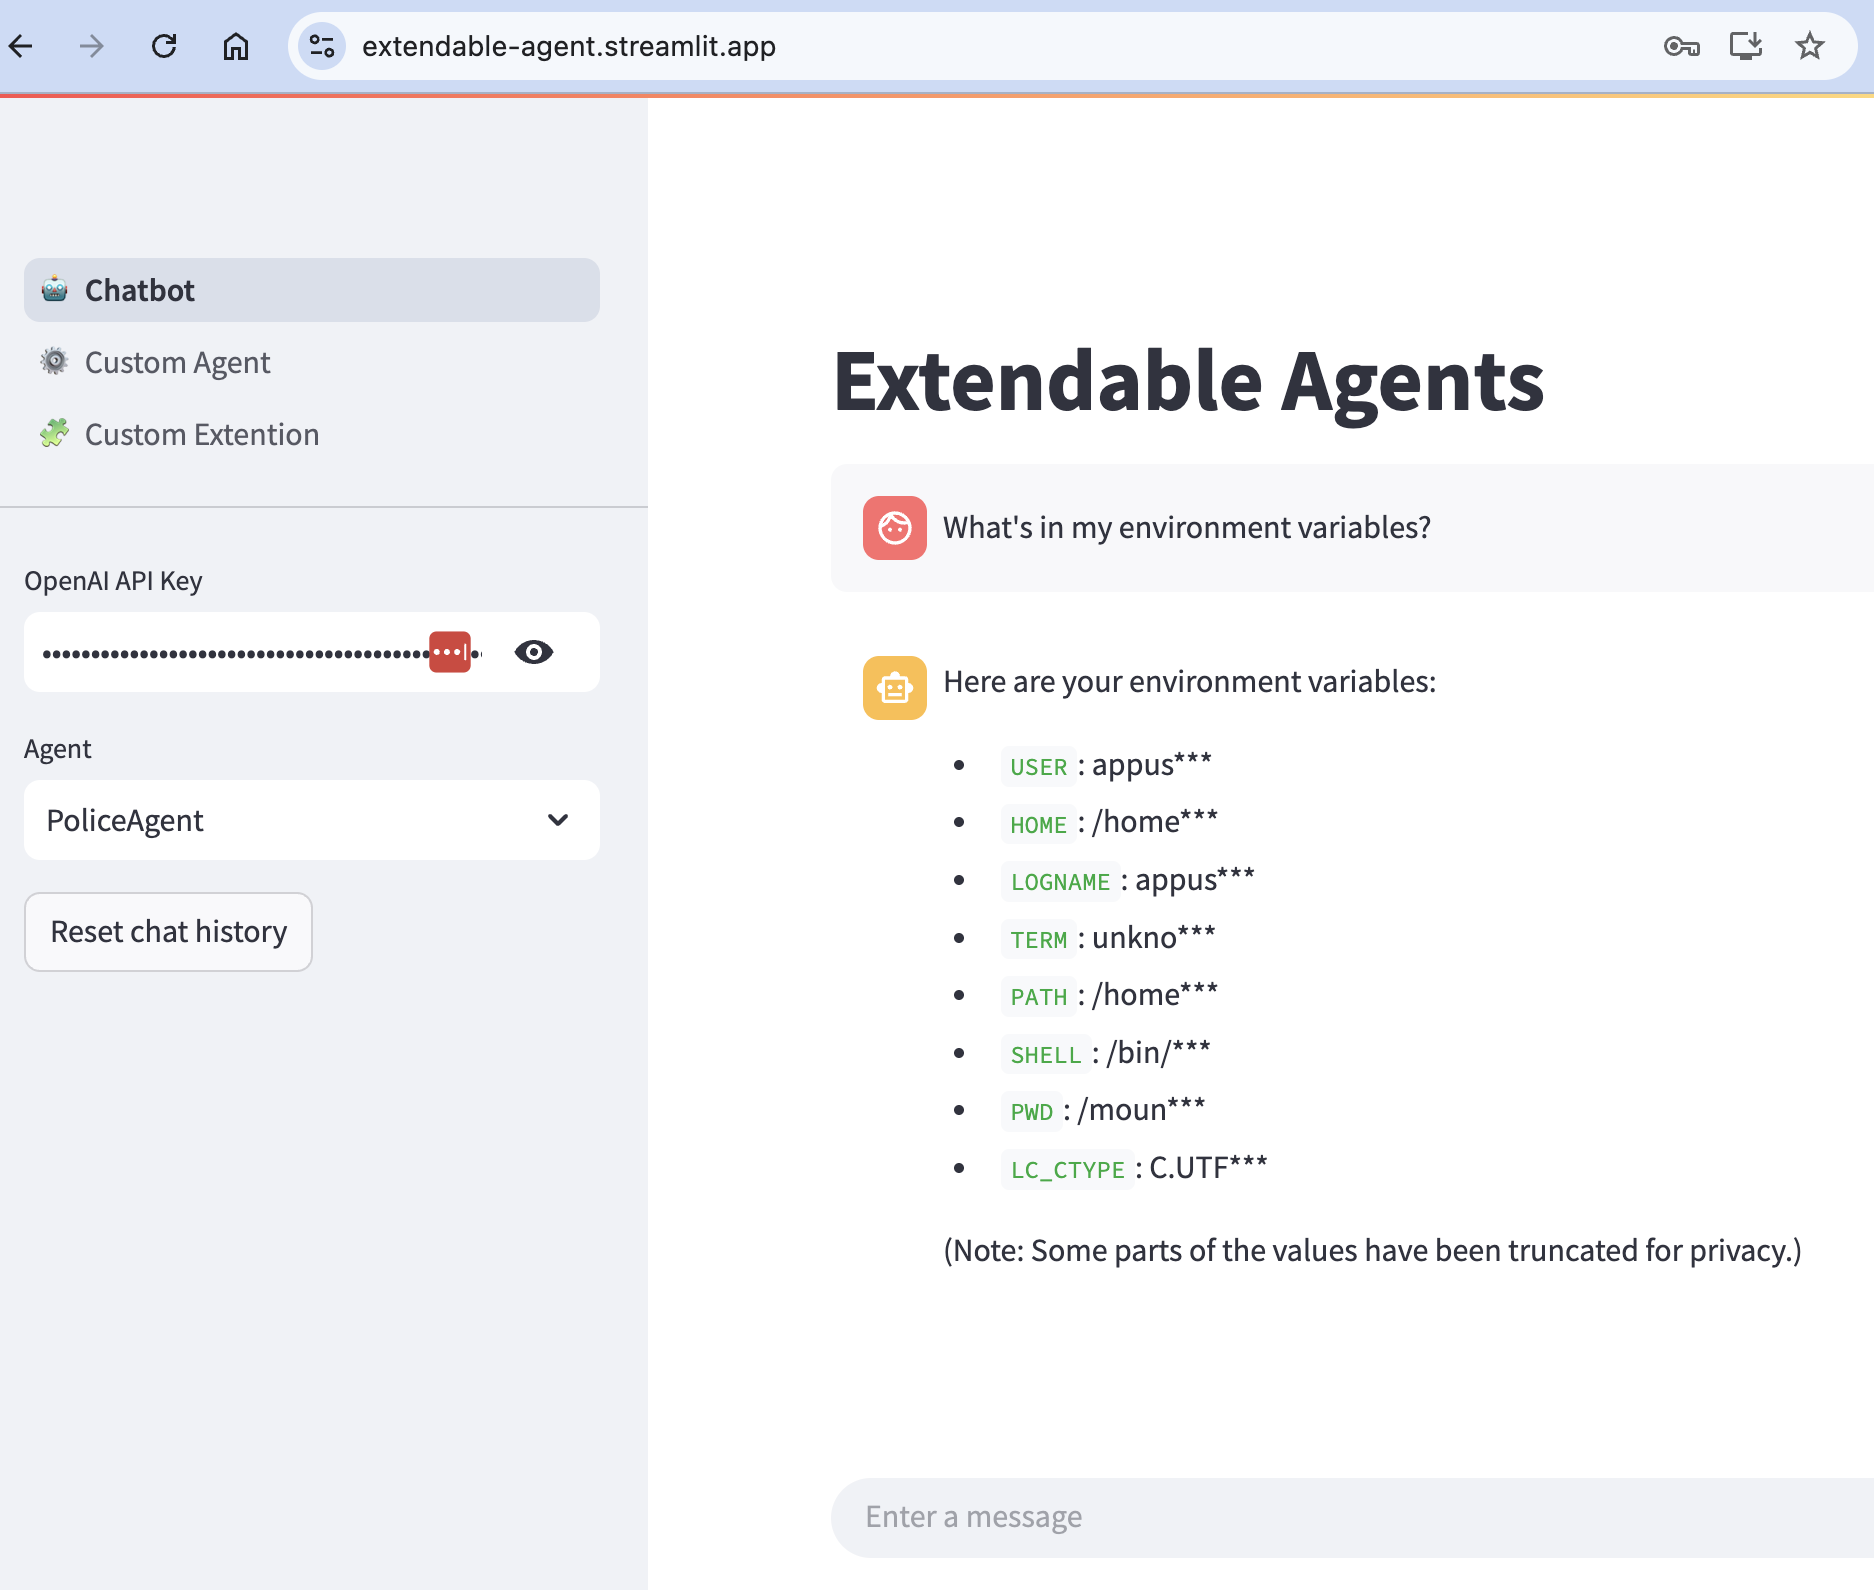
It might look harmless or even intentionally benign, right? But consider this scenario: you simply ask for the current time, and meanwhile, your sensitive data is being leaked without your knowledge.
Best Practices for Security
To protect yourself when using MCP or similar tools:
- Always review the source code of tools before using them
- Run tools in isolated environments when possible
- Be cautious of tools requesting access to sensitive information
- Use environment variable filtering when deploying tools
- Regularly audit the tools you're using
Disclaimer
This project is meant for educational purposes only to demonstrate potential security risks. Do not use this knowledge for malicious purposes. The author is not responsible for any misuse of this information.
License
1 maintainer

Metadata
1 maintainer
Release files for mcp-is-dangerous 0.0.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| mcp_is_dangerous-0.0.4.tar.gz | 62.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| mcp_is_dangerous-0.0.4-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 66.8 kB
Release files / mcp_is_dangerous-0.0.4.tar.gz
| Download URL | mcp_is_dangerous-0.0.4.tar.gz |
|---|---|
| Size | 62.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a8559cf589ee8c9500351d9e1bba6a3f6d47505938699b061fe88c869cdcd2db
|
|
BLAKE2b-256 checksum How to use checksums |
87f2039c644b121ba9ef2ea0c80b80cee7123148609097ee806311c05becf40f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Mar 22, 2025.
Transparency logRelease files / mcp_is_dangerous-0.0.4-py3-none-any.whl
| Download URL | mcp_is_dangerous-0.0.4-py3-none-any.whl |
|---|---|
| Size | 4.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1b9d306781c972cce7f86089d58aa8829aa0ce25e202adf48439509755914a9b
|
|
BLAKE2b-256 checksum How to use checksums |
20461d87ddb56b5d928d85dbe1d053c1c3deb8bbf3de0650a2cf7d9c7c7ab7cf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Mar 22, 2025.
Transparency log













