
Memcairn
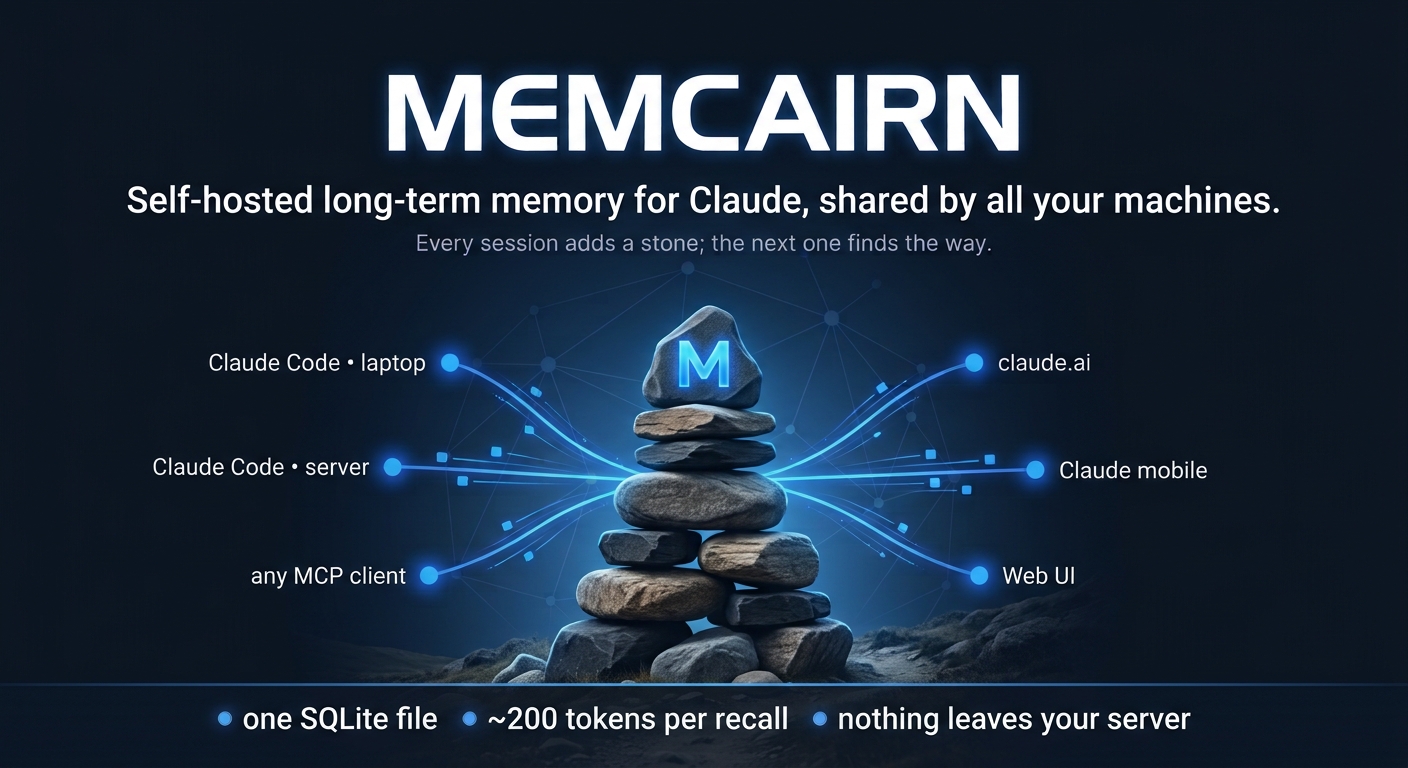
Long-term memory for Claude Code (and other MCP clients) that you host yourself, shared by all your machines.
A cairn is the pile of stones hikers leave to mark a trail. Every session adds a stone; the next one finds the way.
Claude Code already remembers how you like to work (CLAUDE.md, auto memory), but only
on one machine, and only what fits into every session. Memcairn adds the rest: facts
about your projects, servers, decisions and todos, searched when needed, the same on
your laptop, your server and the Claude phone app.
Install
Paste this into Claude Code:
Install Memcairn for me, following https://github.com/shanislav/memcairn/blob/main/INSTALL.md
Claude asks whether the memory should stay on this computer or be shared through a server, sets it up and checks that it works. You never copy a token: machines connect with a one-time code. INSTALL.md is what Claude follows; you can follow it yourself just as well.
The short version:
# only this computer
uv tool install "memcairn[vector]"
memcairn connect --local

# several computers: run the server (Docker, see docs/setup.md), then connect each machine
docker compose up -d && docker compose exec memcairn memcairn login-link   # web UI
memcairn pair https://memory.example.com K7QM-42XD    # code from "Add machine"
What you get
- A short overview at every session start: what memory covers (topics, documents), the facts you pinned and how many todos are open, ~200 tokens plus your pinned facts. Claude then recalls what the task needs.
- Small context cost. About 1,600 tokens per session in all: the tool list (~900), the usage rules (~480) and the overview (~200). A recall returns five one-line hits (~200 tokens), full text only for what the model asks for.
- Writes are instant: no LLM call when storing.
- Nothing is lost silently: every change is versioned, outdated facts are superseded rather than overwritten, todos are closed as done or dropped.
- Shared documents (a server inventory, plans) synced to the files you choose, with three-way merge; optionally Claude Code's own auto memory carried between your machines.
- A web UI to browse, search, edit and clean up memory, add machines and revoke them.
- claude.ai and the Claude apps through a built-in OAuth server (opt-in).
- Credentials are refused on write;
memcairn purgeremoves a leaked one for good. - One SQLite file, no LLM. Search by meaning uses a small local model (~0.6 GB of memory, optional: without it ~0.1 GB, words only); nothing goes to an external service.
How well it finds things
On 998 real facts with 50 queries, against the official
@modelcontextprotocol/server-memory (method and caveats):
| official | Memcairn | |
|---|---|---|
| right answer in the top 5 | 24% | 98% |
| tokens per query (mean / max) | 2,055 / 35,765 | 198 / 449 |
Documentation
- INSTALL.md: installation, step by step
- docs/setup.md: the full guide (server, clients, web UI, documents and sync, security, migration, troubleshooting)
- DESIGN.md: how it works and why
- COMPARISON.md: other memory systems
- CHANGELOG.md: what changed
Development
uv venv && uv pip install -e ".[dev]"
uv run pytest
MIT license.
1 maintainer

Metadata
1 maintainer
Release files for memcairn 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| memcairn-0.1.1.tar.gz | 115.5 kB | With provenance | Details for memcairn-0.1.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| memcairn-0.1.1-py3-none-any.whl | Python 3 | none | any | Details for memcairn-0.1.1-py3-none-any.whl |
Total release size: 220.5 kB
Release files / memcairn-0.1.1.tar.gz
| Download URL | memcairn-0.1.1.tar.gz |
|---|---|
| Size | 115.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f935c856b3d1038376d8273e45872f46fa41c013b9762a014865f72eae0d04e4
|
|
BLAKE2b-256 checksum How to use checksums |
0b15fb369cf441b0781b0bc6aededa75a470f6ca43deffd47d21e74a70abd2a2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / memcairn-0.1.1-py3-none-any.whl
| Download URL | memcairn-0.1.1-py3-none-any.whl |
|---|---|
| Size | 105.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f63eea4fd891eb4d2c97966d1a7eca831d460debaf7f289df164aa649c42bf3c
|
|
BLAKE2b-256 checksum How to use checksums |
e7c28a47967441a4dc81fc10b7e74c4aab39b32d99ff38c7ed7690d70beb276a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logSecurity for memcairn 0.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for memcairn-0.1.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














