
mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android, iOS, and hybrid source code. Supports Java, Kotlin, Android XML, iOS Info.plist, Swift, Objective C, JavaScript, TypeScript, and Cordova/Capacitor/Expo configuration files. mobsfscan uses MobSF static analysis rules and is powered by semgrep and libsast.
Made with 


Support mobsfscan
If you liked mobsfscan and find it useful, please consider donating.
e-Learning Courses & Certifications


Installation
pip install mobsfscan
Requires Python 3.10–3.14
Supported Languages & Configurations
- Android: Java (
.java), Kotlin (.kt), Android Manifest (AndroidManifest.xml), Network Security Config, and layout and resource XMLs. - iOS: Swift (
.swift), Objective-C (.m), and App Transport Security settings inInfo.plist. - JavaScript, TypeScript & Hybrid Mobile: React Native, Expo, Cordova / Ionic, Capacitor, and WebView apps via Tree-sitter AST rules across
.js,.jsx,.ts,.tsx,.mjs,.cjs, and<script>blocks in.html,.htm,.vue, and.svelte. - Hybrid App Configurations: Cordova / PhoneGap, Capacitor, and Expo configuration files.
Command Line Options
$ mobsfscan
usage: mobsfscan [-h] [--json] [--sarif] [--sonarqube] [--gitlab-sast] [--html]
                 [--type {android,ios,javascript,auto}] [-o OUTPUT] [-c CONFIG]
                 [-mp {default,billiard,thread}] [-w] [--no-fail] [-v]
                 [path ...]

positional arguments:
  path                  Path can be file(s) or directories with source code

options:
  -h, --help            show this help message and exit
  --json                set output format as JSON
  --sarif               set output format as SARIF 2.1.0
  --sonarqube           set output format as SonarQube generic issues (10.3+)
  --gitlab-sast         set output format as GitLab SAST report
  --html                set output format as HTML
  --type {android,ios,javascript,auto}
                        optional: force android, ios, or javascript rules explicitly
  -o OUTPUT, --output OUTPUT
                        output filename to save the result
  -c CONFIG, --config CONFIG
                        location to .mobsf config file
  -mp {default,billiard,thread}, --multiprocessing {default,billiard,thread}
                        optional: specify multiprocessing strategy
  -w, --exit-warning    non zero exit code on warning
  --no-fail             force zero exit code, takes precedence over --exit-warning
  -v, --version         show mobsfscan version
Example Usage
$ mobsfscan tests/assets/src/
- Pattern Match ████████████████████████████████████████████████████████████ 3
- Semantic Grep ██████ 37

mobsfscan: v1.2.0 | Ajin Abraham | opensecurity.in
╒══════════════╤════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID      │ android_webview_ignore_ssl                                                                                                                             │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION  │ Insecure WebView Implementation. WebView ignores SSL Certificate errors and accept any SSL Certificate. This application is vulnerable to MITM attacks │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ TYPE         │ RegexAnd                                                                                                                                               │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ PATTERN      │ ['onReceivedSslError\\(WebView', '\\.proceed\\(\\);']                                                                                                  │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY     │ ERROR                                                                                                                                                   │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ INPUTCASE    │ exact                                                                                                                                                  │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CVSS         │ 7.4                                                                                                                                                    │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE          │ CWE-295 Improper Certificate Validation                                                                                                                │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP-MOBILE │ M3: Insecure Communication                                                                                                                             │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ MASVS        │ MSTG-NETWORK-3                                                                                                                                         │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ REF          │ https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#webview-server-certificate-verification                │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES        │ ╒════════════════╤═════════════════════════════════════════════════════════════════════════════════════════════╕                                       │
│              │ │ File           │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match Position │ 1480 - 1491                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Line Number(s) │ 50                                                                                          │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match String   │ .proceed();                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ File           │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match Position │ 1331 - 1357                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Line Number(s) │ 46                                                                                          │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match String   │ onReceivedSslError(WebView                                                                  │                                       │
│              │ ╘════════════════╧═════════════════════════════════════════════════════════════════════════════════════════════╛                                       │
╘══════════════╧════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╛
Python API
>>> from mobsfscan.mobsfscan import MobSFScan
>>> src = 'tests/assets/src/java/java_vuln.java'
>>> scanner = MobSFScan([src], json=True)
>>> scanner.scan()
{
    'results': {
        'android_logging': {
            'files': [{
                'file_path': 'tests/assets/src/java/java_vuln.java',
                'match_position': (13, 73),
                'match_lines': (19, 19),
                'match_string': '            Log.d("htbridge", "getAllRecords(): " + records.toString());'
            }],
            'metadata': {
                'cwe': 'CWE-532 Insertion of Sensitive Information into Log File',
                'owasp-mobile': 'M1: Improper Platform Usage',
                'masvs': 'MSTG-STORAGE-3',
                'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#logs',
                'description': 'The App logs information. Please ensure that sensitive information is never logged.',
                'severity': 'INFO'
            }
        },
        'android_certificate_pinning': {
            'metadata': {
                'cwe': 'CWE-295 Improper Certificate Validation',
                'owasp-mobile': 'M3: Insecure Communication',
                'masvs': 'MSTG-NETWORK-4',
                'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#testing-custom-certificate-stores-and-certificate-pinning-mstg-network-4',
                'description': 'This App does not use TLS/SSL certificate or public key pinning to detect or prevent MITM attacks in secure communication channel.',
                'severity': 'INFO'
            }
        },
        'android_root_detection': {
            'metadata': {
                'cwe': 'CWE-919 - Weaknesses in Mobile Applications',
                'owasp-mobile': 'M8: Code Tampering',
                'masvs': 'MSTG-RESILIENCE-1',
                'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1',
                'description': 'This App does not have root detection capabilities. Running a sensitive application on a rooted device questions the device integrity and affects users data.',
                'severity': 'INFO'
            }
        },
        'android_prevent_screenshot': {
            'metadata': {
                'cwe': 'CWE-200 Information Exposure',
                'owasp-mobile': 'M2: Insecure Data Storage',
                'masvs': 'MSTG-STORAGE-9',
                'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#finding-sensitive-information-in-auto-generated-screenshots-mstg-storage-9',
                'description': 'This App does not have capabilities to prevent against Screenshots from Recent Task History/ Now On Tap etc.',
                'severity': 'INFO'
            }
        },
        'android_safetynet_api': {
            'metadata': {
                'cwe': 'CWE-353 Missing Support for Integrity Check',
                'owasp-mobile': 'M8: Code Tampering',
                'masvs': 'MSTG-RESILIENCE-1',
                'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1',
                'description': "This App does not uses SafetyNet Attestation API that provides cryptographically-signed attestation, assessing the device's integrity. This check helps to ensure that the servers are interacting with the genuine app running on a genuine Android device. ",
                'severity': 'INFO'
            }
        },
        'android_detect_tapjacking': {
            'metadata': {
                'cwe': 'CWE-200 Information Exposure',
                'owasp-mobile': 'M1: Improper Platform Usage',
                'masvs': 'MSTG-PLATFORM-9',
                'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05h-Testing-Platform-Interaction.md#testing-for-overlay-attacks-mstg-platform-9',
                'description': "This app does not has capabilities to prevent tapjacking attacks. An attacker can hijack the user's taps and tricks him into performing some critical operations that he did not intend to.",
                'severity': 'INFO'
            }
        }
    },
    'errors': []
}
Configure mobsfscan
A .mobsf file in the root of the source code directory allows you to configure mobsfscan. You can also use a custom .mobsf file using --config argument.
---
- ignore-filenames:
  - skip.java

  ignore-paths:
  - __MACOSX
  - skip_dir

  ignore-rules:
  - android_kotlin_logging
  - android_safetynet_api
  - android_prevent_screenshot
  - android_detect_tapjacking
  - android_certificate_pinning
  - android_root_detection
  - android_certificate_transparency

  severity-filter:
  - WARNING
  - ERROR

  severity-overrides:
    ios_log: ERROR
    android_logging: WARNING
severity-overrides changes the reported severity for specific rule IDs (INFO, WARNING, or ERROR). Overrides are applied before severity-filter and affect CLI output, exit codes, and report formats (SARIF, SonarQube, GitLab SAST).
Suppress Findings
You can suppress findings from source files by adding a mobsf-ignore: rule_id1, rule_id2 comment on the line that triggers the finding. Line comments (//), JSX block comments ({/* ... */}), and HTML/XML comments (<!-- ... -->) are supported. Only that match is suppressed; other matches of the same rule in the file still report.
Examples:
String password = "strong password"; // mobsf-ignore: hardcoded_password
eval(expr); // mobsf-ignore: js_dynamic_code_execution
<div dangerouslySetInnerHTML={{ __html: html }} /> {/* mobsf-ignore: js_dom_xss_sink */}
<access origin="*" /> <!-- mobsf-ignore: cordova_config_wildcard_access -->
CI/CD Integrations
You can enable mobsfscan in your CI/CD or DevSecOps pipelines.
Github Action
Add the following to the file .github/workflows/mobsfscan.yml.
name: mobsfscan

on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]

jobs:
  build:
    runs-on: ubuntu-latest
    steps:
    - uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - name: mobsfscan
      uses: MobSF/mobsfscan@main
      with:
        args: '. --json'
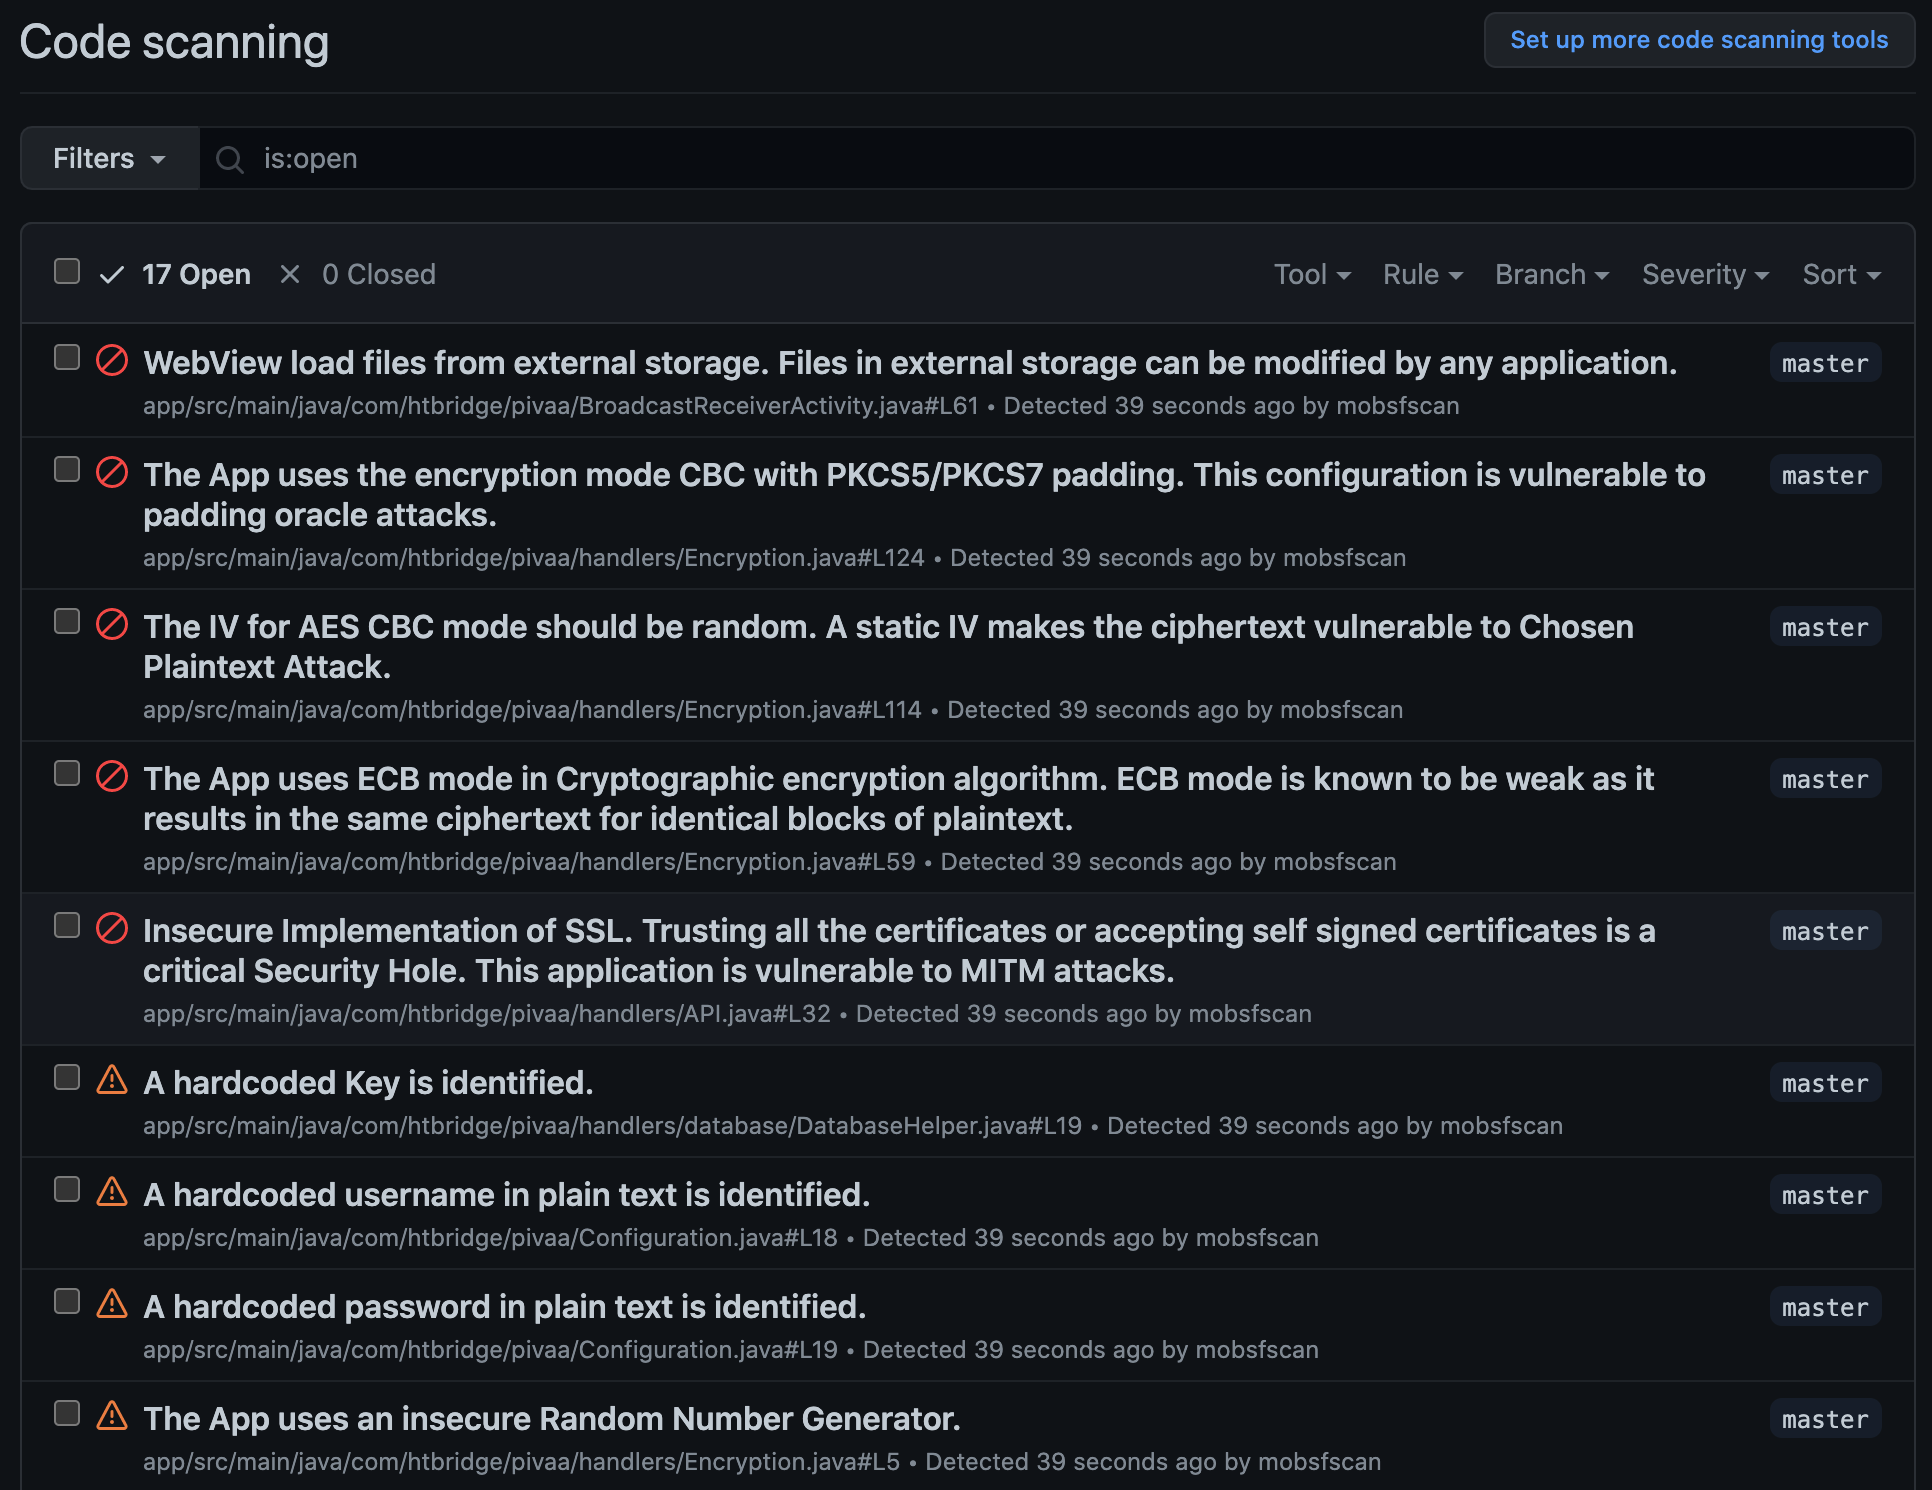
Example: pivaa with mobsfscan github action
Github Code Scanning Integration
Add the following to the file .github/workflows/mobsfscan_sarif.yml.
name: mobsfscan sarif
on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]

jobs:
  mobsfscan:
    runs-on: ubuntu-latest
    name: mobsfscan code scanning
    permissions:
      security-events: write
      actions: read
      contents: read
    steps:
    - name: Checkout the code
      uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - name: mobsfscan
      uses: MobSF/mobsfscan@main
      with:
        args: '. --sarif --output results.sarif || true'
    - name: Upload mobsfscan report
      uses: github/codeql-action/upload-sarif@33d7b85da1a04171e211befe2c739303b9a4c066 # v4.39.3
      with:
        sarif_file: results.sarif
Gitlab CI/CD
Add the following to the file .gitlab-ci.yml.
stages:
  - test

mobsfscan:
  image: python:3.12
  stage: test
  before_script:
    - pip3 install --upgrade mobsfscan
  script:
    - mobsfscan . --gitlab-sast -o gl-sast-report.json
  artifacts:
    reports:
      sast: gl-sast-report.json
Example command (local):
mobsfscan . --gitlab-sast -o gl-sast-report.json
This writes a native GitLab SAST report so findings appear in the Vulnerability Report / MR security widget without a SARIF converter.
SonarQube / SonarCloud
--sonarqube writes the generic issue format (SonarQube 10.3+ / SonarCloud), with separate rules and issues arrays:
mobsfscan . --sonarqube -o mobsfscan-sonar.json
Import with sonar.externalIssuesReportPaths=mobsfscan-sonar.json.
Travis CI
Add the following to the file .travis.yml.
language: python
install:
    - pip3 install --upgrade mobsfscan
script:
    - mobsfscan .
Circle CI
Add the following to the file .circleci/config.yaml
version: 2.1
jobs:
  mobsfscan:
    docker:
      - image: cimg/python:3.12
    steps:
      - checkout
      - run:
          name: Install mobsfscan
          command: pip install --upgrade mobsfscan
      - run:
           name: mobsfscan check
           command: mobsfscan .
Bitrise
Add the following to the file bitrise.yml
security_audit:
  steps:
  - activate-ssh-key@4:
      run_if: '{{getenv "SSH_RSA_PRIVATE_KEY" | ne ""}}'
  - git-clone@8.4: {}
  - mobsfscan@1: {}
  - deploy-to-bitrise-io@2: {}
Docker
Prebuilt image from DockerHub
docker pull opensecurity/mobsfscan
docker run -v /path-to-source-dir:/src opensecurity/mobsfscan /src
Build Locally
docker build -t mobsfscan .
docker run -v /path-to-source-dir:/src mobsfscan /src
1 maintainer

Metadata
1 maintainer
Release files for mobsfscan 1.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| mobsfscan-1.2.0.tar.gz | 88.3 kB | With provenance | Details for mobsfscan-1.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| mobsfscan-1.2.0-py3-none-any.whl | Python 3 | none | any | Details for mobsfscan-1.2.0-py3-none-any.whl |
Total release size: 211.1 kB
Release files / mobsfscan-1.2.0.tar.gz
| Download URL | mobsfscan-1.2.0.tar.gz |
|---|---|
| Size | 88.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
35652da134a9f66de10593d16b8b6980ef051e341ab2c2445902089e6390e2e9
|
|
BLAKE2b-256 checksum How to use checksums |
96c0db4a87b50820056fb074e712aa7befd24b1b18c810a685af73a6df010460
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logRelease files / mobsfscan-1.2.0-py3-none-any.whl
| Download URL | mobsfscan-1.2.0-py3-none-any.whl |
|---|---|
| Size | 122.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
64dfc32a3774e5ceb9953f2f2c1258e75b60767e8368f9f1cc8afdf91d43af68
|
|
BLAKE2b-256 checksum How to use checksums |
118604c38d60522a5d2a1c6f8f488e31d1dcb4b18f82525aa92be393945fa20c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logSecurity for mobsfscan 1.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for mobsfscan-1.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














