
modelhog
Your laptop has 100 GB of AI models you forgot about. modelhog finds every model you ever pulled from Hugging Face, Ollama or LM Studio, plus the developer caches piling up behind them. It shows how big each one is and when you last touched it, and deletes the ones you pick.
uvx modelhog
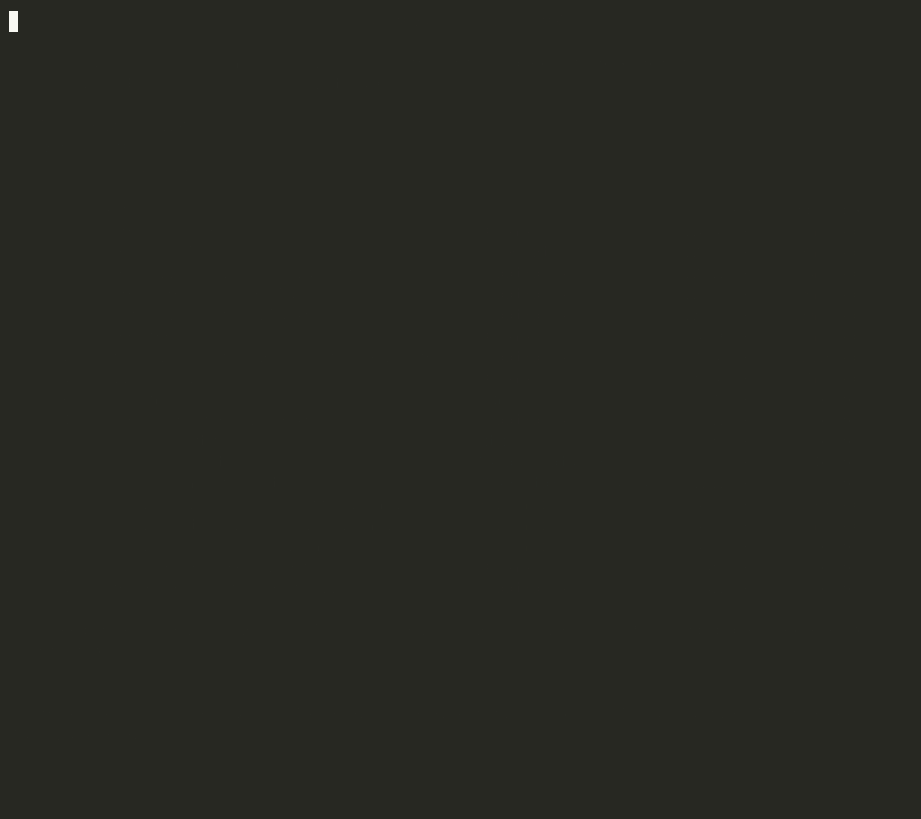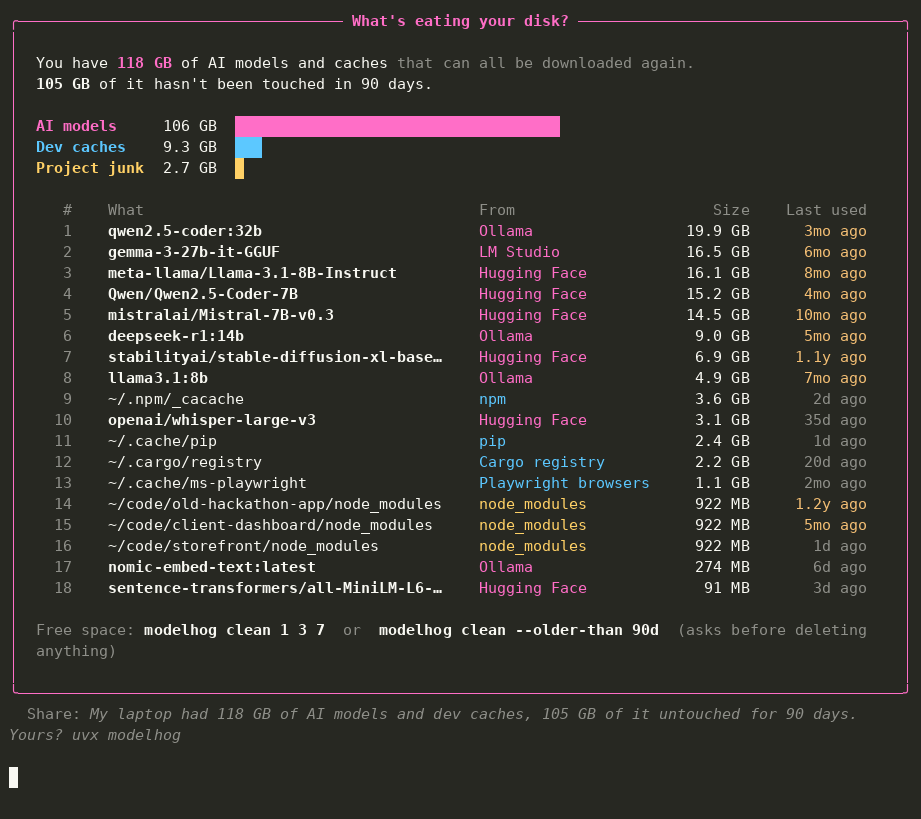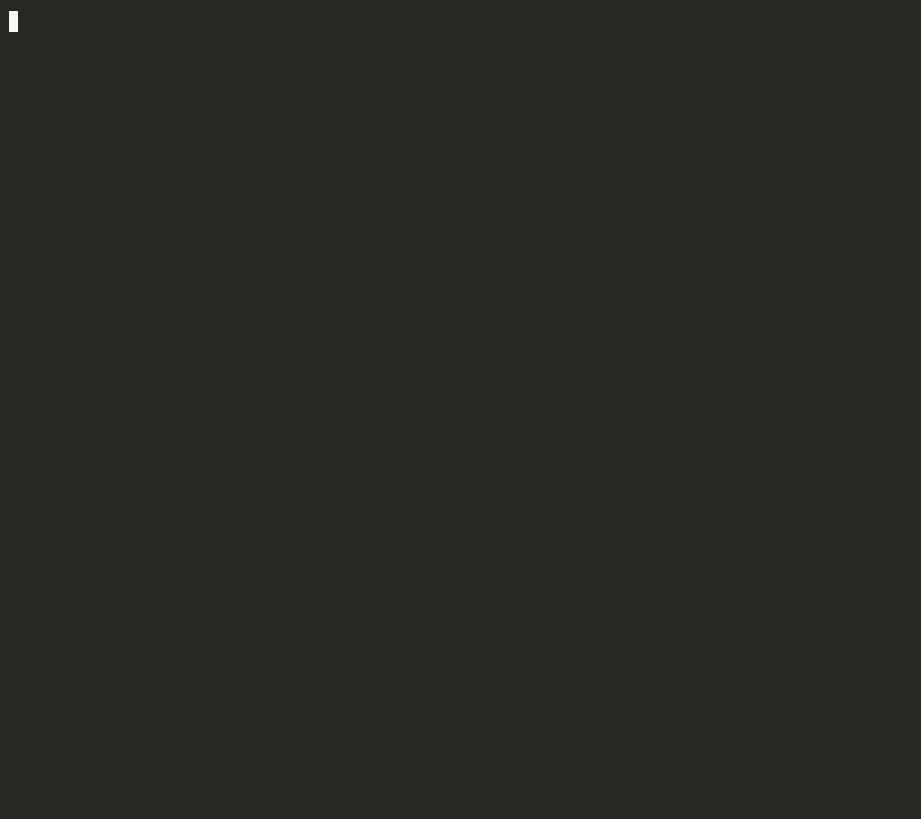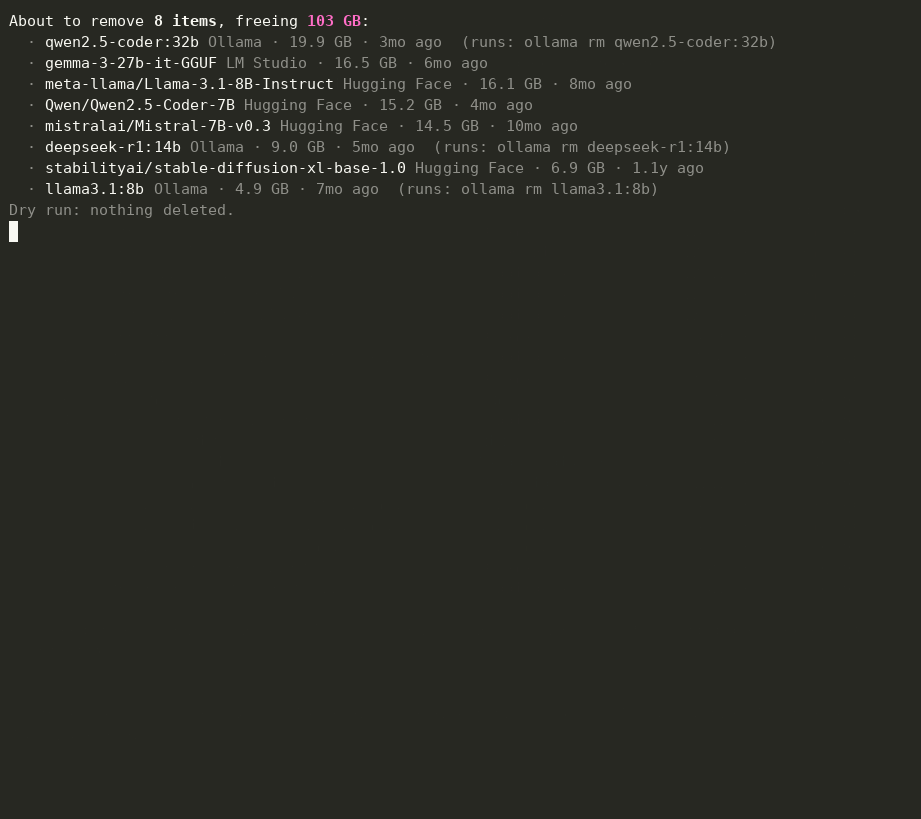
Demo on a made-up home folder (sparse files, so it took no real space) generated by docs/demo.py.
Everything modelhog lists can be downloaded again. It never touches your code, your documents, or anything it can't name.
What it finds
| Where | |
|---|---|
| Hugging Face | ~/.cache/huggingface/hub (or $HF_HOME, $HF_HUB_CACHE): one line per model and dataset |
| Ollama | ~/.ollama/models (or $OLLAMA_MODELS): one line per model:tag, sizes from the manifests, shared layers counted once |
| LM Studio, llama.cpp, GPT4All, Jan | their model folders |
| Whisper, PyTorch Hub, Keras, CLIP | their download caches |
| Dev caches | pip, uv, npm, Yarn, pnpm, Bun, Cargo, Go modules, Gradle, Maven, Homebrew, Playwright, Puppeteer, conda, CocoaPods, pre-commit, Hugging Face datasets |
| Apple | Xcode DerivedData and archives, iOS simulators |
| Docker | Docker Desktop's disk image (what's actually used, not the sparse maximum) |
Project junk (--projects) |
node_modules, .venv, target, .next, .turbo, Pods, .tox… inside folders that are real projects |
"Last used" is the newest modification time inside each folder, which is when you last downloaded or changed it. Operating systems don't reliably record when a file was last read.
Cleaning up
modelhog clean 1 3 7                     # numbers from the list
modelhog clean --older-than 90d          # everything untouched for 90 days (also 12w, 6m, 1y)
modelhog clean --older-than 6m --only ai # just the models
modelhog clean 2 --dry-run               # show what would go
It always lists what it's about to delete and the total, then asks before deleting (--yes to skip the prompt).
A few things are removed with their own tool rather than by deleting files, because deleting files would break them:
- Ollama models share layers, so modelhog runs
ollama rm model:tag. - Docker gets
docker system prune -a --volumes. - iOS simulators get
xcrun simctl delete unavailable. - Go modules get
go clean -modcache.
Options
modelhog                      # AI models and dev caches
modelhog --projects ~/code    # also project junk under ~/code
modelhog --only ai            # or caches, projects
modelhog --all                # list everything, not just the biggest 40
modelhog --json               # for scripts
Install
uvx modelhog           # run without installing
pipx install modelhog  # or install it
Requires Python 3.9+. The only dependency is rich. macOS, Linux and Windows.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for modelhog 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| modelhog-0.1.0.tar.gz | 12.0 kB | With provenance | Details for modelhog-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| modelhog-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for modelhog-0.1.0-py3-none-any.whl |
Total release size: 23.8 kB
Release files / modelhog-0.1.0.tar.gz
| Download URL | modelhog-0.1.0.tar.gz |
|---|---|
| Size | 12.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
9753e5be252f0bbbe3f55ee8ed95cf3df4f3888f5729d57600c54412c04aeff9
|
|
BLAKE2b-256 checksum How to use checksums |
6bff5b31a13f544cc3ebe7118471f8fb85cb8ddb34816c097d63cbe23e2dabb1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / modelhog-0.1.0-py3-none-any.whl
| Download URL | modelhog-0.1.0-py3-none-any.whl |
|---|---|
| Size | 11.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
0d87d22d0e065c67a13cc87f7053a8930cc3318ff496839c5e5ebdcdc6847ad0
|
|
BLAKE2b-256 checksum How to use checksums |
63b4449c0c2d41bf51b65ad4bad6aeafa495f3da13a1ac4d767cacd6cd616c21
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logSecurity for modelhog 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for modelhog-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













