
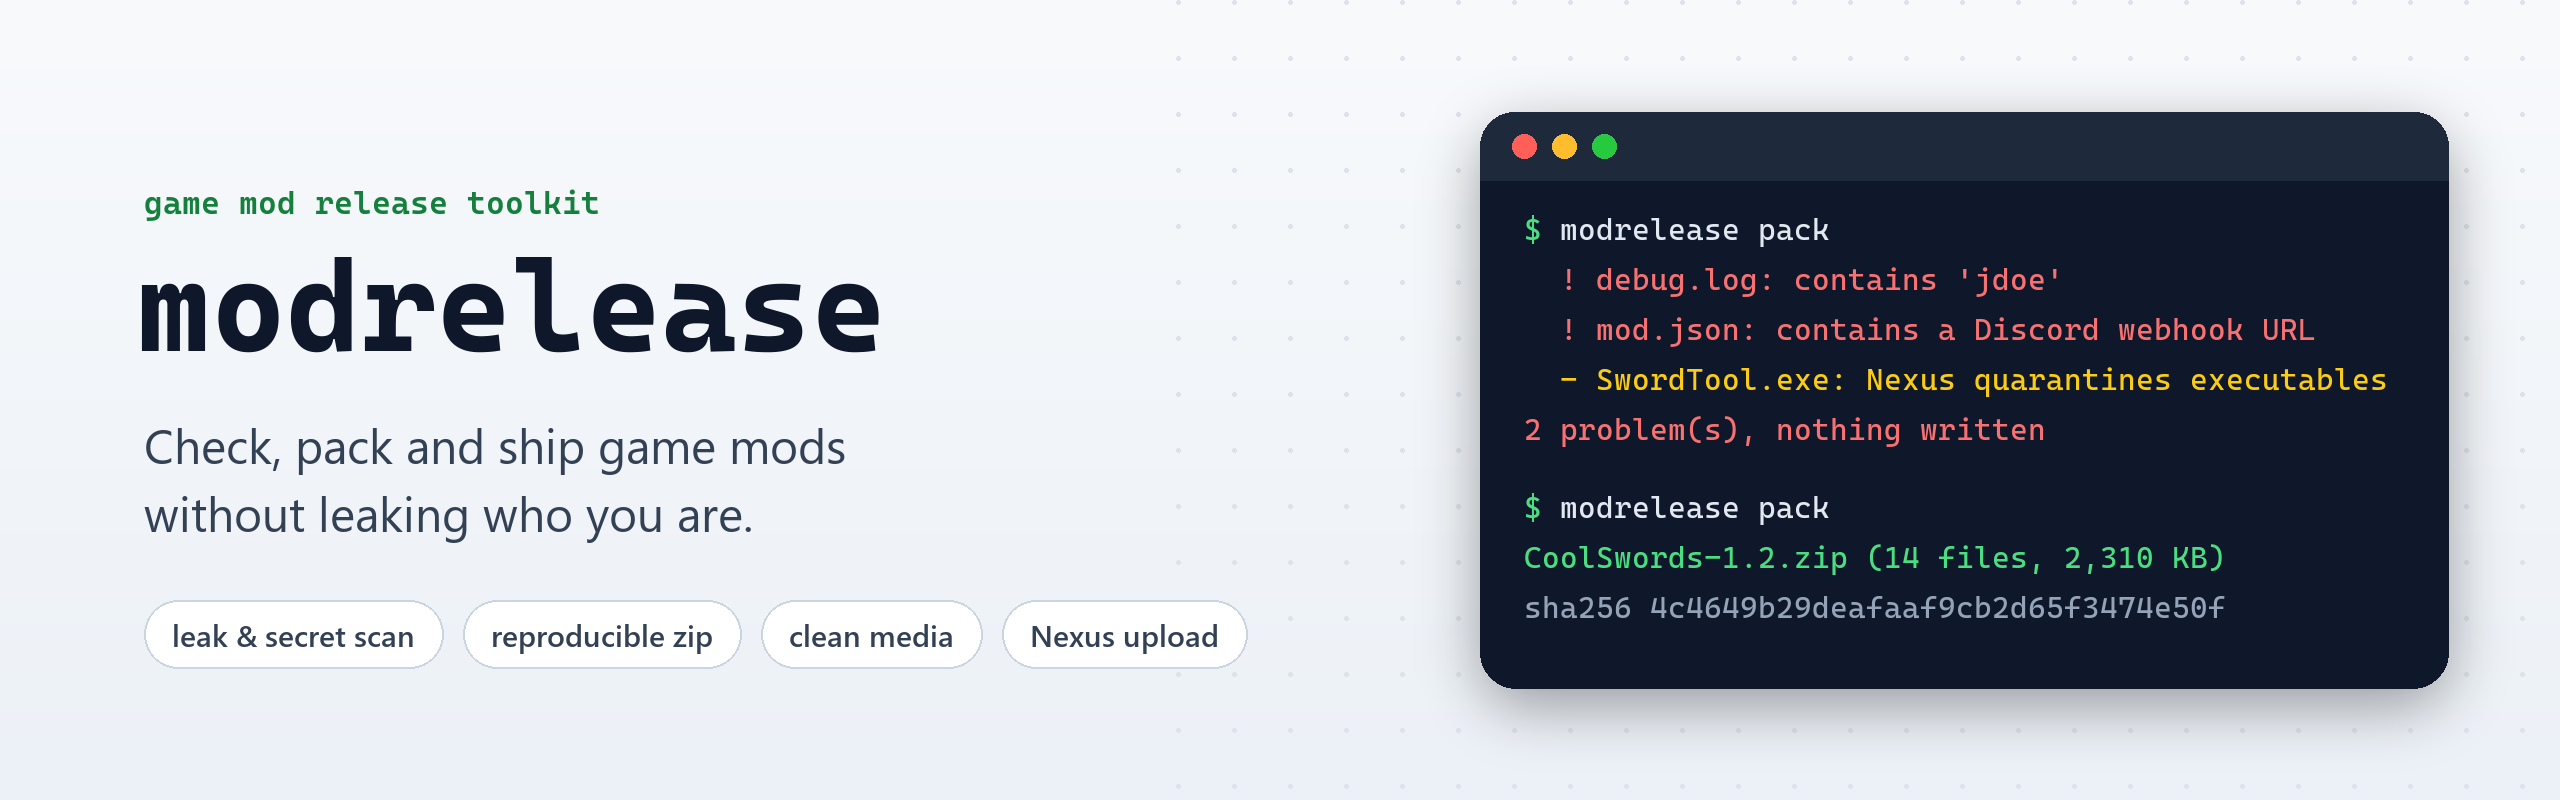
Config files and logs in a mod archive keep C:\Users\yourname\... paths, tools and their .pdb files keep the
folder they were built in, screenshots keep the camera and the GPS position, and a zip made in Explorer keeps the
time you touched every file. A Discord webhook or a GitHub token in a config is worse: anyone who downloads the mod
can use it. modrelease finds all of that before you upload, then packs the release.
pipx install modrelease
modrelease check MyMod/
modrelease pack MyMod/ -o MyMod-1.0.zip
| Command | What it does |
|---|---|
check |
Looks for personal data, secrets and risky files in a folder, files or a finished zip |
pack |
The same check, then a reproducible zip and its .sha256 |
clean |
Screenshots and videos without EXIF, GPS, tags or encoder settings |
diff |
Files added, removed and changed between two release zips |
vt |
The VirusTotal result for a file, and which engines flag it |
nexus |
Uploads the zip as a new version of a file on Nexus Mods |
appeal |
Writes the email that gets a quarantined Nexus file reviewed |
Settings can live in a modrelease.toml next to the mod, and there is a GitHub Action for releases on every tag.
The full guide, a demo and the source are on GitHub.
1 maintainer

Metadata
1 maintainer
Release files for modrelease 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| modrelease-0.2.0.tar.gz | 27.8 kB | With provenance | Details for modrelease-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| modrelease-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for modrelease-0.2.0-py3-none-any.whl |
Total release size: 48.6 kB
Release files / modrelease-0.2.0.tar.gz
| Download URL | modrelease-0.2.0.tar.gz |
|---|---|
| Size | 27.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fbfd7b4ab9b5ef459476eda0881e4f95e2fb1e376159fa1de94b583debf2c775
|
|
BLAKE2b-256 checksum How to use checksums |
d81949c4074ccc9021c6db7946612d032dfe0e64fa112322a0a7d39922a5cd92
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logRelease files / modrelease-0.2.0-py3-none-any.whl
| Download URL | modrelease-0.2.0-py3-none-any.whl |
|---|---|
| Size | 20.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
e56a465a593cf992a829cbf5514be7b814f21c812096732ad84eb9cf0de95c63
|
|
BLAKE2b-256 checksum How to use checksums |
6857d16a99f1f30c177deed01ddcd63504ac6e29e3bbb32e828e595872cc1f97
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logSecurity for modrelease 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for modrelease-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 3, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













