
WARNING: THIS IS ALPHA STAGE QUALITY AND WILL MOST CERTAINLY DELETE YOUR APACHE CONFIGURATION (It doesn’t, but: no waranty and such.)
modseccfg
Simple GUI editor for SecRuleDisableById settings
Tries to suggest false positives from error and audit logs
(And a few options to configure mod_security and CRS variables.)
Obviously requires ssh -X forwarding, or preparing config rules on a local test setup, and *.conf files to be writable by current user (running as root is not advised).
Usage
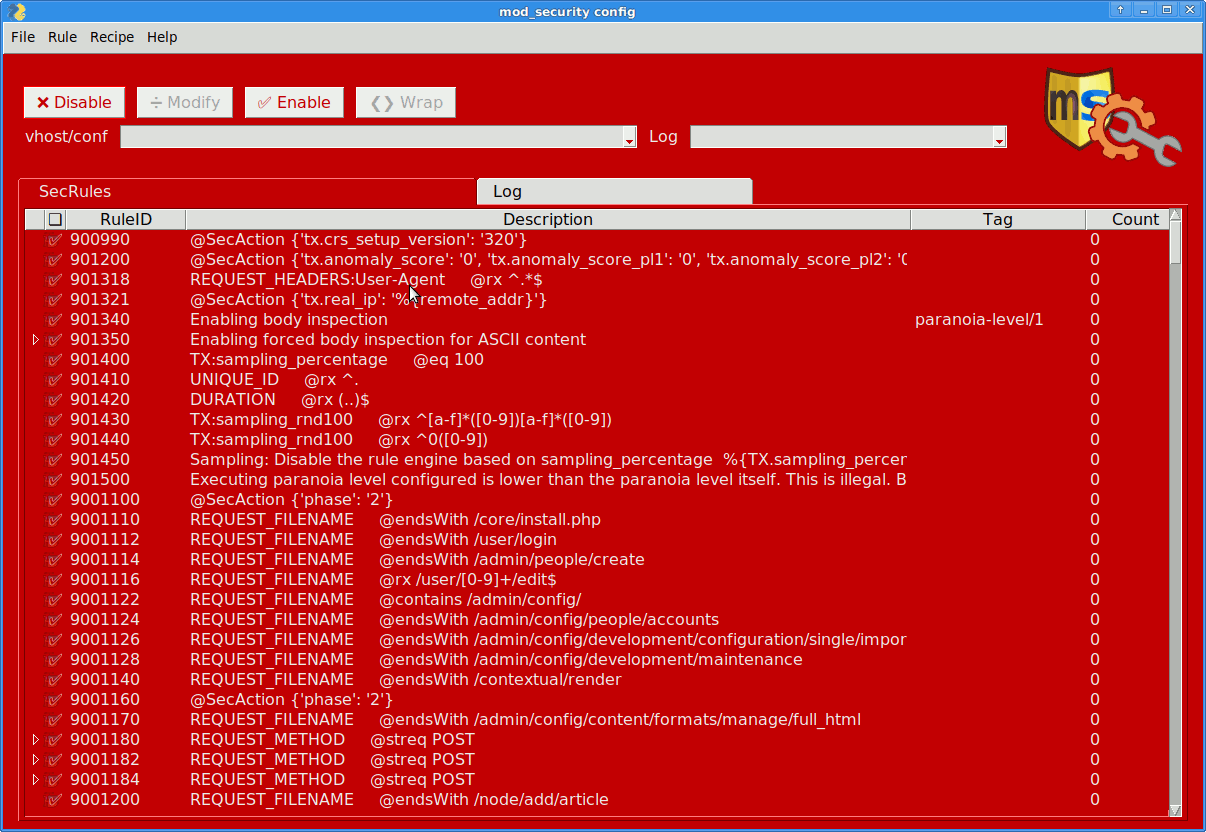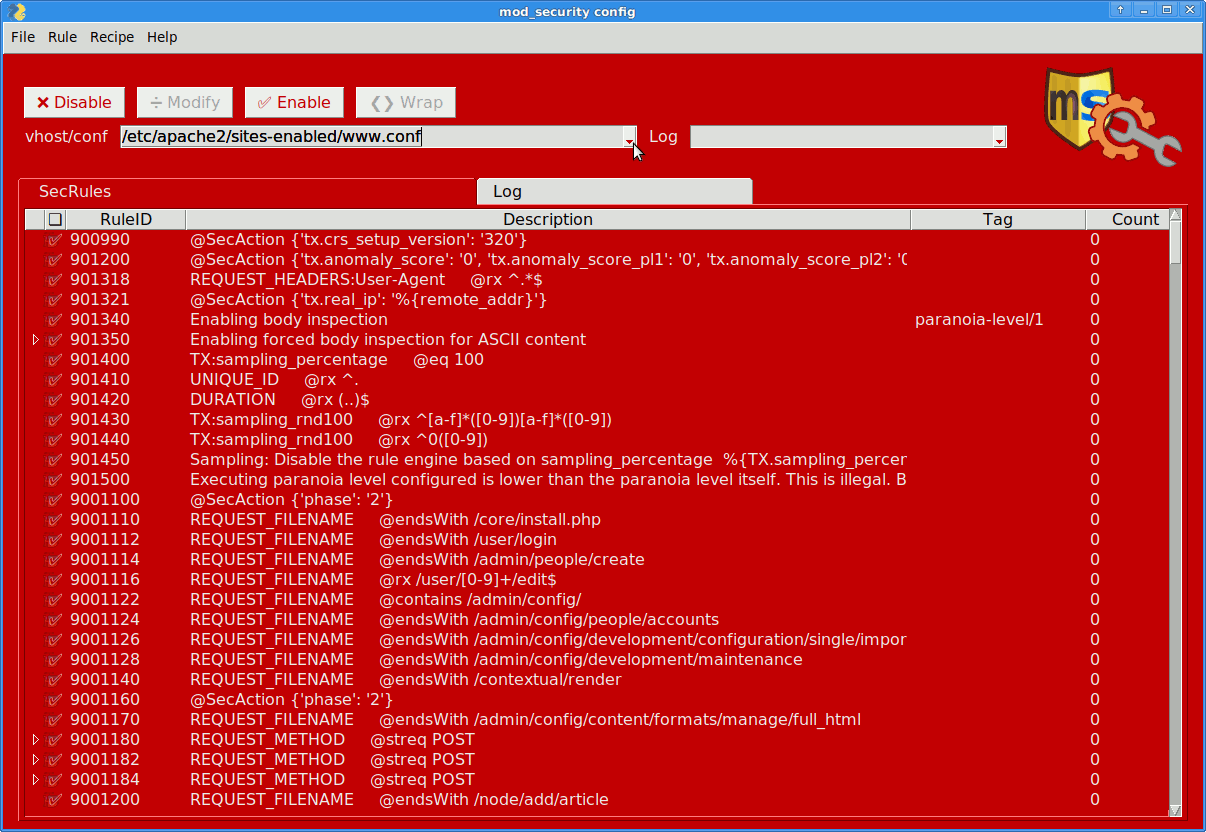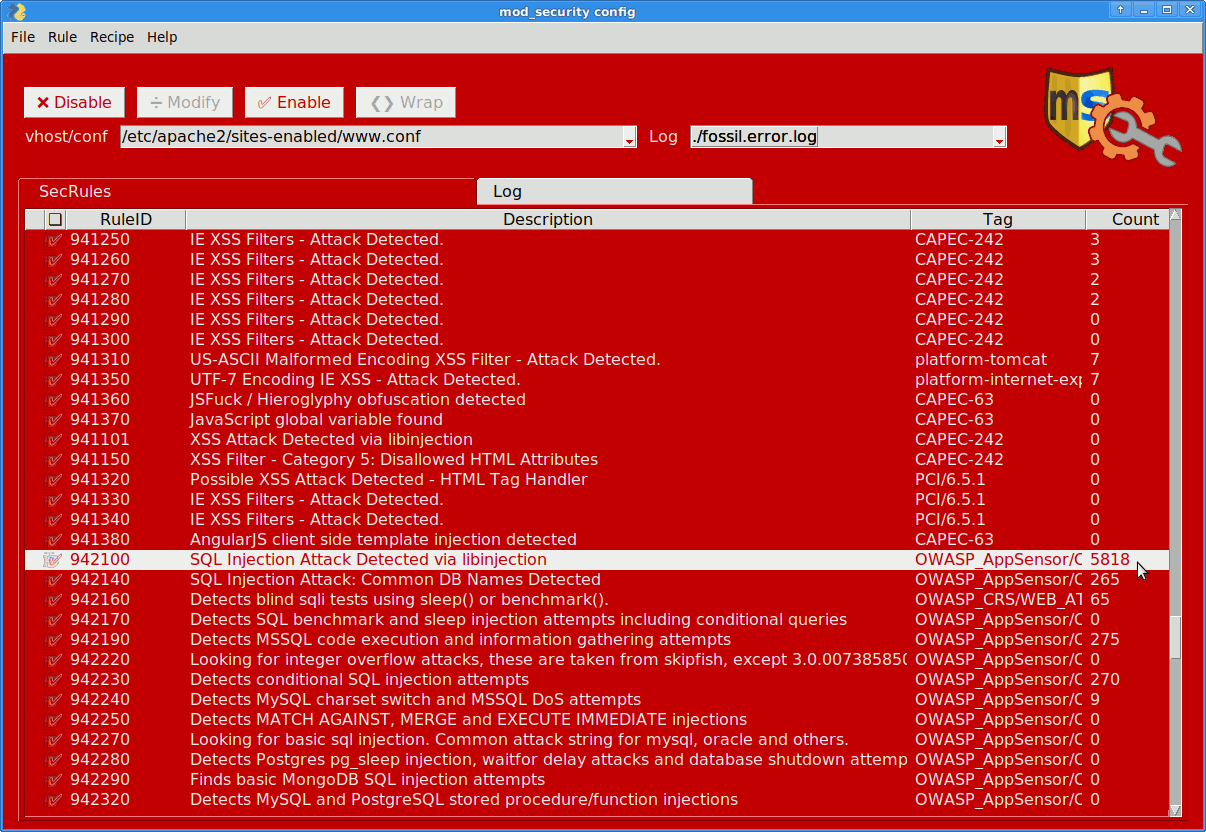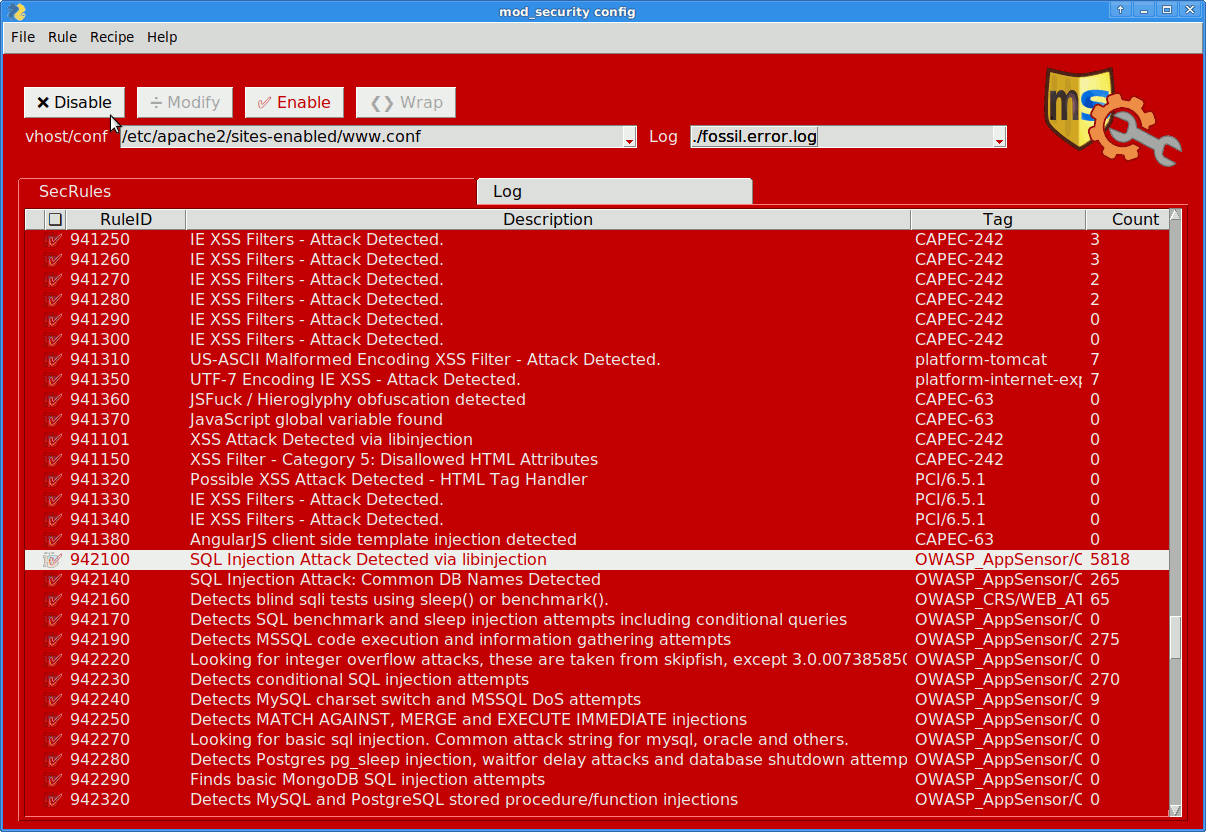
You obviously should have Apache(2.x) + mod_security(2.9) + CRS(3.x) set up and running already (in DetectionOnly mode initially), to allow for log inspection and adapting rules.
start modseccfg (python3 -m modseccfg)
Select a configuration/vhost file to inspect + work on.
Pick the according error.log
Inspect the rules with a high error count.
[Disable] offending rules (if they’re not essential to CRS, or would likely poke holes into useful protections).
Thenceforth restart Apache after testing changes (apache2ctl -t).
Notes
Preferrably do not edit default /etc/apache* files
Work on separated /srv/web/conf.d/* configuration, if available
And keep vhost settings in e.g. vhost.*.dir files, rather than multiple <VirtualHost> in one *.conf (else only the first section will be augmented).
Missing features
Doesn’t process any audit.log yet.
Can’t classify wrapped (<Location> or other directives) rules yet.
No rule information dialog.
No SecOption editor yet.
No CRS settings (setvar:crs…) editor yet.
Recipes are not worth using yet.
No sudo usage.
No support for nginx or mod_sec v3.
No support for Windows setups. (Would work, but no interest in user support.)
1 maintainer

Metadata
1 maintainer
Release files for modseccfg 0.0.9
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| modseccfg-0.0.9-py3-none-any.whl | Python 3 | none | any | Details for modseccfg-0.0.9-py3-none-any.whl |
Release files / modseccfg-0.0.9-py3-none-any.whl
| Download URL | modseccfg-0.0.9-py3-none-any.whl |
|---|---|
| Size | 38.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5ca2817080652bd5af319abd8cefa3cb3d4769614d87f6850d5986718d03dabb
|
|
BLAKE2b-256 checksum How to use checksums |
1fa4b70074d2bc3aa1c31dc372555a0cf51ac221f4bda730afe825f042df086d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
Python-urllib/3.7
|
Security for modseccfg 0.0.9
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














