
The independent verifier for trading strategies written by AI agents and humans.
Catch look-ahead bias, hidden trading costs and overfitting before a backtest reaches your money.







Docs · Quick start · Use from agents · Verifier API · Trap Suite · Changelog
The problem
A coding agent can turn a trading idea into a backtest in minutes. It will then tell you the strategy returns 40% a year with a Sharpe of 3. Most of the time that number is wrong, for the same few reasons:
- Look-ahead bias. The code reads future bars:
shift(-1), centred windows,bfill, statistics over the whole series,np.gradient, an FFT filter. - Missing costs. The edge is smaller than fees and slippage, or it disappears when the fill comes one bar later.
- Selection bias. The agent tried 300 variants and reports the best one as if it were the only one.
Backtest libraries run whatever code you give them. None of them tell you the backtest itself is broken.
The solution
Monte-Neo checks the backtest, not the idea. Give it the price data and the strategy code or its positions. It returns one of four verdicts, the checks behind the verdict, concrete next steps and a reproducible, optionally signed certificate.
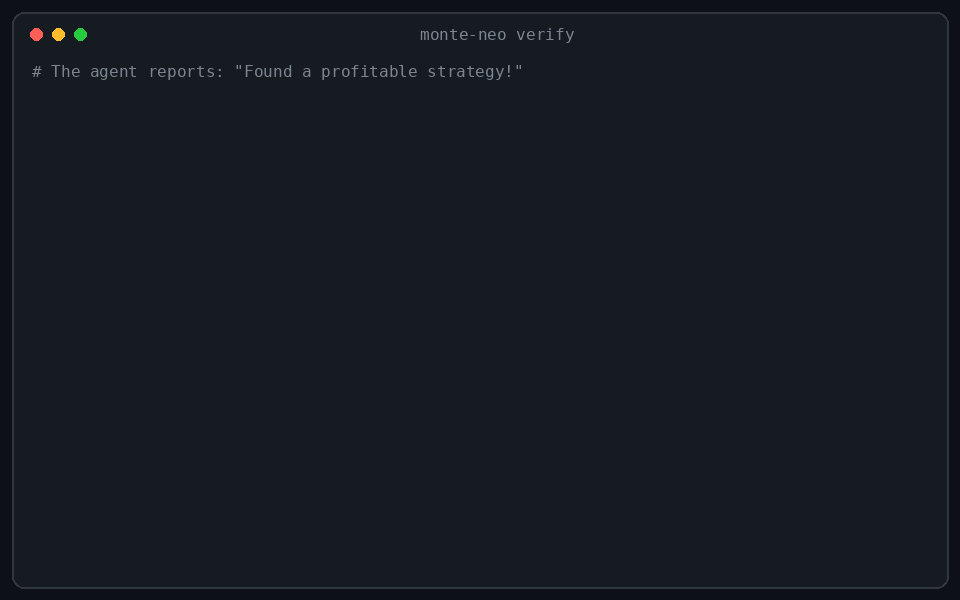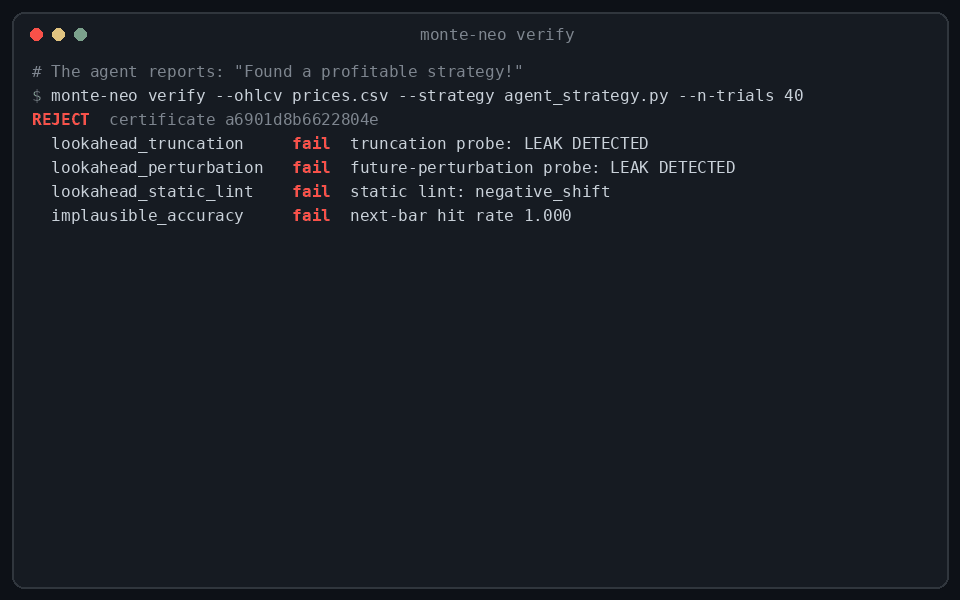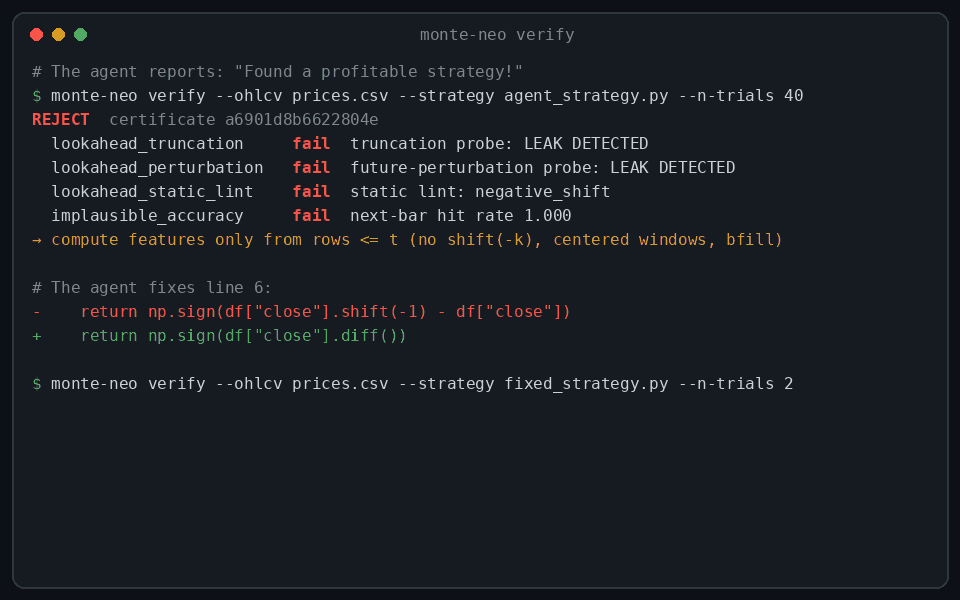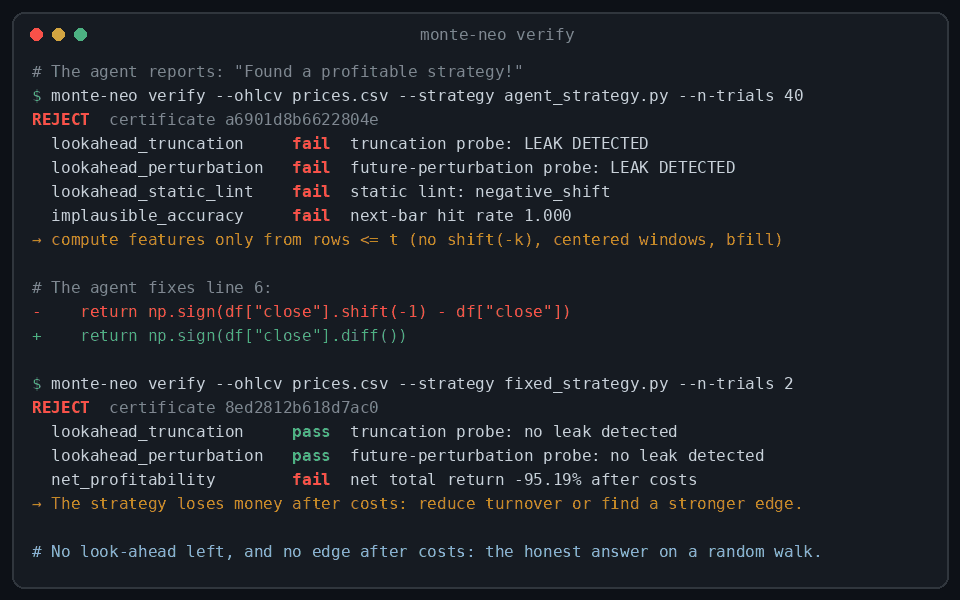
The agent's strategy used shift(-1), so it knew the next close. Monte-Neo found the leak in four
independent ways and named the line. After the fix, no look-ahead is left, and the verifier tells
the truth: on a random walk, the strategy has no edge after costs.
Text output of the first run
$ monte-neo verify --ohlcv prices.csv --strategy agent_strategy.py --n-trials 40
REJECT  certificate a771f361ef7871b9
  check                    category    status  summary
  data_integrity           integrity   pass    OHLCV is clean
  lookahead_truncation     lookahead   fail    truncation probe: LEAK DETECTED
  lookahead_perturbation   lookahead   fail    future-perturbation probe: LEAK DETECTED
  lookahead_static_lint    lookahead   fail    static lint: negative_shift
  implausible_accuracy     lookahead   fail    next-bar hit rate 1.000
  net_profitability        economics   fail    net total return -64.97% after costs
  deflated_sharpe          statistics  fail    deflated Sharpe 0.000 over 40 trial(s)
  ...                                          (7 more checks)
→ The signal at bar t changes when later bars are removed: compute features only from rows <= t
  (no shift(-k), centered windows, bfill or full-sample stats).
→ Fix the flagged source lines (negative shift, center=True, backward fill) and re-run verify. Lines: 6.
The run used a synthetic random walk; output shortened.
| Verdict | Meaning | CLI exit code |
|---|---|---|
PASS |
No problems found | 0 |
PASS_WITH_WARNINGS |
Usable; read the warnings | 0 |
NEEDS_MORE_EVIDENCE |
Too few trades, or the Sharpe does not survive the number of variants tried | 1 |
REJECT |
The backtest is broken or loses money after costs | 2 |
What it checks
| Family | Checks |
|---|---|
| Look-ahead | Truncation probe (does bar t change when later bars are removed?), future-perturbation probe, static AST lint (20 rules), implausible hit rate |
| Economics | Net return after commission and slippage, break-even cost in bps, one- and two-bar execution delay |
| Statistics | Probabilistic and Deflated Sharpe priced by n_trials, sample size, holdout consistency, walk-forward out-of-sample check for grid searches |
| Integrity | Broken OHLCV, non-deterministic signals |
Every rule is backed by the Trap Suite: 40 strategies that are known to lie and 15 honest controls. It runs on every build, so the verifier cannot silently stop catching a leak or start accusing honest code.
Where to use it
| You are… | Use Monte-Neo to… |
|---|---|
| Building strategies with Claude Code, Codex, Gemini CLI or Cursor | Make the agent verify its own backtest before it reports results. The MCP server and the Claude Code plugin do this automatically. |
| Running a strategy repository | Add the GitHub Action. A pull request whose backtest leaks or loses money after costs fails CI, and the verdict is posted as a PR comment. |
| A quant, reviewer or allocator | Check a strategy someone else sends you, with their data and code, in one command. Re-check or verify the signature of the certificate they hand over. |
| A prop firm, strategy marketplace or trading course | Screen submissions before a human looks at them. Publish signed certificates next to listed strategies. |
| A researcher comparing agents | Run the Honesty Bench: the same tasks for every agent, scored by how often each one claims profit that is not there. |
Why Monte-Neo
- Independent. It checks code it did not write, with probes that do not trust the strategy's own numbers.
- Built for agents. An MCP server, a Claude Code plugin with a skill, a slash command and a reminder hook, plus rules for Codex, Gemini CLI and Cursor. Every failed check returns a
next_actionthe agent can act on. - Reproducible. The same data, code and
n_trialsalways give the samecertificate_id. Anyone can reproduce a certificate with--recheck. - Signed. Ed25519 signatures show who issued a certificate and that nobody edited it.
- Honest about selection bias. Declare how many variants you tried, or let
verify_gridcount them for you. The Deflated Sharpe prices them in. - Local and private. Your data and code never leave your machine. MIT licensed.
Quick start
pip install monte-neo
Command line
monte-neo verify --ohlcv btc_1h.csv --strategy my_strategy.py --n-trials 12 --out verdict.json
my_strategy.py defines signal(df), which returns one position per bar: +1 long, 0 flat,
-1 short. The position decided on bar t is filled at the open of bar t + 1.
def signal(df):
    fast = df["close"].rolling(20).mean()
    slow = df["close"].rolling(80).mean()
    return (fast > slow).astype(int)
Python
from monte_neo.verify import verify_strategy

report = verify_strategy("btc_1h.csv", strategy="my_strategy.py", n_trials=12)
print(report["verdict"], report["next_actions"])
Parameter search with honest trial counting
monte-neo verify --ohlcv btc_1h.csv --strategy sma.py --grid '{"fast": [10, 20], "slow": [80, 120]}'
Use it from your coding agent
Claude Code (plugin with the MCP server, the verify-strategy skill and /verify):
/plugin marketplace add NeoZorK/Monte-Neo
/plugin install monte-neo@monte-neo
Any MCP client (Codex, Gemini CLI, Cursor, and others):
uvx monte-neo mcp
It is also listed in the official MCP Registry as io.github.NeoZorK/monte-neo. Setup for each
client: Use from agents.
MCP tools: verify_strategy, verify_grid, probe_lookahead, cost_stress,
recheck_certificate, check_signature, verdict_schema, verifier_manifest.
GitHub Action
- uses: NeoZorK/Monte-Neo@v0.30.0
  with:
    ohlcv: data/btc_1h.csv
    strategy: strategies/momentum.py
    n-trials: "12"
    comment: "true"                                        # post the verdict on the pull request
    signing-key: ${{ secrets.MONTE_NEO_SIGNING_KEY }}      # optional: sign the certificate
    upload-certificate: "true"                             # optional: keep it as a workflow artifact
The job fails on REJECT. The verdict and every check appear in the step summary.
Certificates you can check
Each run produces a strategy-verdict/1 JSON certificate. It contains the verdict, every check,
the metrics and the SHA-256 hashes of the data, signals and code.
monte-neo verify --recheck verdict.json --ohlcv btc_1h.csv --strategy my_strategy.py  # reproduce it
pip install "monte-neo[sign]"
monte-neo verify --keygen issuer                                  # issuer.key + issuer.pub
monte-neo verify --ohlcv btc_1h.csv --strategy my_strategy.py --sign issuer.key --out verdict.json
monte-neo verify --check-signature verdict.json --public-key issuer.pub
Show that a strategy passed:
[](https://github.com/NeoZorK/Monte-Neo)
Link the badge to the verification page with your certificate and public
key (/verify/?cert=<https URL>&key=ed25519:<key>). Readers then check the signature in their
browser with one click; nothing is uploaded.
Install options
pip install monte-neo              # verifier, CLI and MCP server
pip install "monte-neo[sign]"      # + Ed25519 certificate signing
pip install "monte-neo[plot]"      # + charts
pip install "monte-neo[apple]"     # + Metal / MLX research engine (Apple Silicon)
pip install "monte-neo[full]"      # everything
Python 3.11+ on macOS or Linux.
Research engine (fee-aware bar backtests, sweeps, Monte Carlo)
Monte-Neo started as a fast local research engine for Apple Silicon, and the verifier runs on it. The engine is still available. It is in maintenance mode: bug fixes only.
from monte_neo.backtest import ExecutionModel, export_sma_sweep, synthetic_ohlcv

ohlc = synthetic_ohlcv(100_000, seed=42)
model = ExecutionModel(commission_bps=5.0, slippage_bps=5.0, warmup_bars=50)
out = export_sma_sweep(ohlc["open"], ohlc["high"], ohlc["low"], ohlc["close"], combos=16, model=model, device="auto")
print(out["device"], out["combos"])
- Next-bar fills, costs in bps, SL/TP/trailing stops, funding, sessions
- Export API with golden vectors, holdout, walk-forward, CSCV/PBO, Monte Carlo helpers
- Metal / MLX / Numba device selection with a memory planner that falls back to CPU instead of hanging
- Paper OMS for event-level validation
Docs: quick start · export API · backtest engine
Project status
Monte-Neo is in active development (beta). The verifier API and the strategy-verdict/1
schema are stable across minor releases. See the
roadmap.
Not investment advice. Monte-Neo checks backtest methodology. It does not predict future profit.
Contributing
Found a way a backtest fooled you or your agent? Submit it as a trap. Bug reports and pull requests are welcome; see the contributing guide. Report security issues privately: SECURITY.md.
Citation
If Monte-Neo helps your research, please cite it. GitHub shows the citation under Cite this repository (CITATION.cff).
License
1 maintainer

Release files for monte-neo 0.30.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| monte_neo-0.30.0.tar.gz | 1.8 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| monte_neo-0.30.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 2.1 MB
Release files / monte_neo-0.30.0.tar.gz
| Download URL | monte_neo-0.30.0.tar.gz |
|---|---|
| Size | 1.8 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5889dd27788bc815c1176bb37006fd76db5cf20eaa0142230a9577b23808c9d2
|
|
BLAKE2b-256 checksum How to use checksums |
2d04f95cb33ebb3067bd3edf4d437dd97a87942ddbaee265cd42648d26e1e145
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / monte_neo-0.30.0-py3-none-any.whl
| Download URL | monte_neo-0.30.0-py3-none-any.whl |
|---|---|
| Size | 314.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7898652adf7a86b69c059dbcff7c959488ff2b144036124a49b27e493c341ad2
|
|
BLAKE2b-256 checksum How to use checksums |
f9e4b99ba5b317a550ae9cc9e34b0517de87fca207aa83061c02e53afe505477
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency log













