
[m] munio
Security scanner and runtime guard for AI agent tool calls


AI agents call external tools — MCP servers, OpenClaw skills, API endpoints. A malicious or poorly-written tool can exfiltrate your data, execute arbitrary commands, or chain actions into multi-step attacks. munio catches these issues before they reach your agent.
pipx install munio
munio config-scan
For deep tool schema analysis:
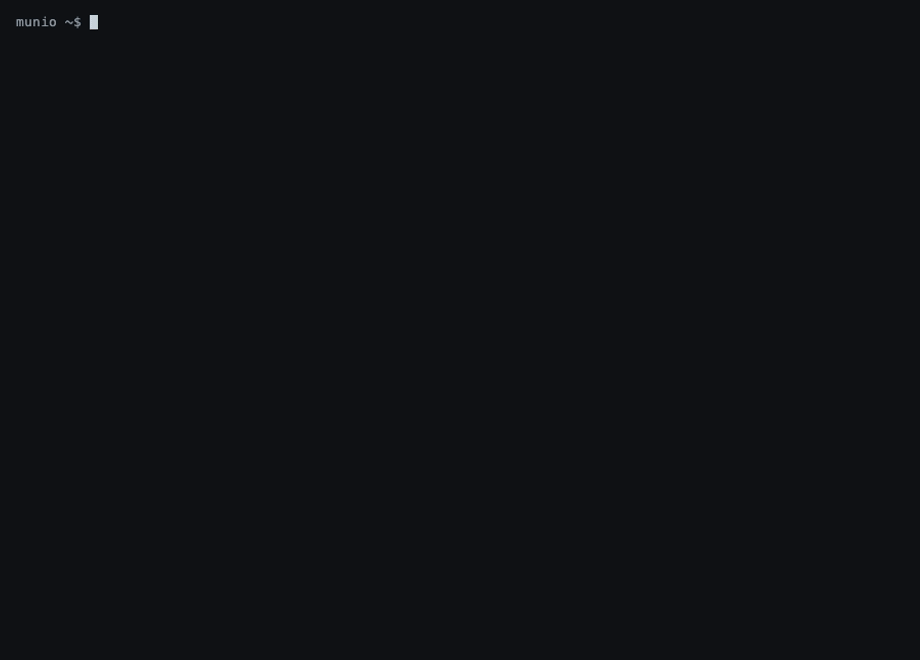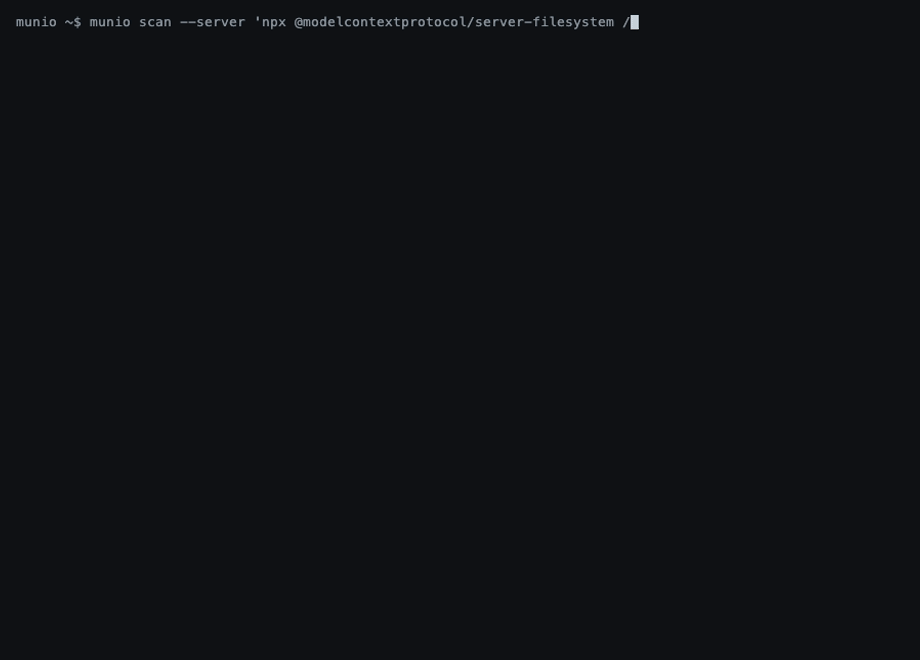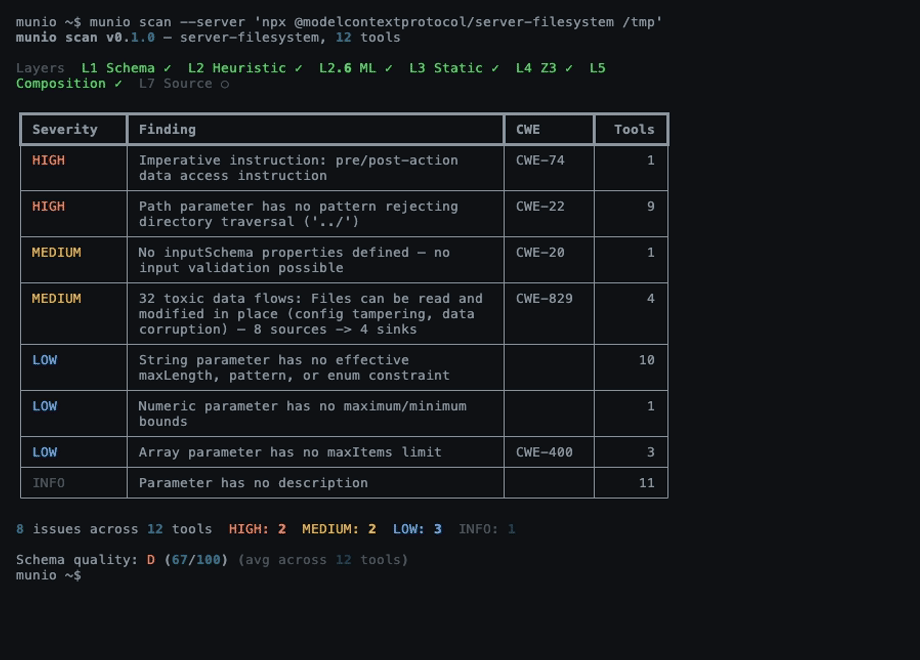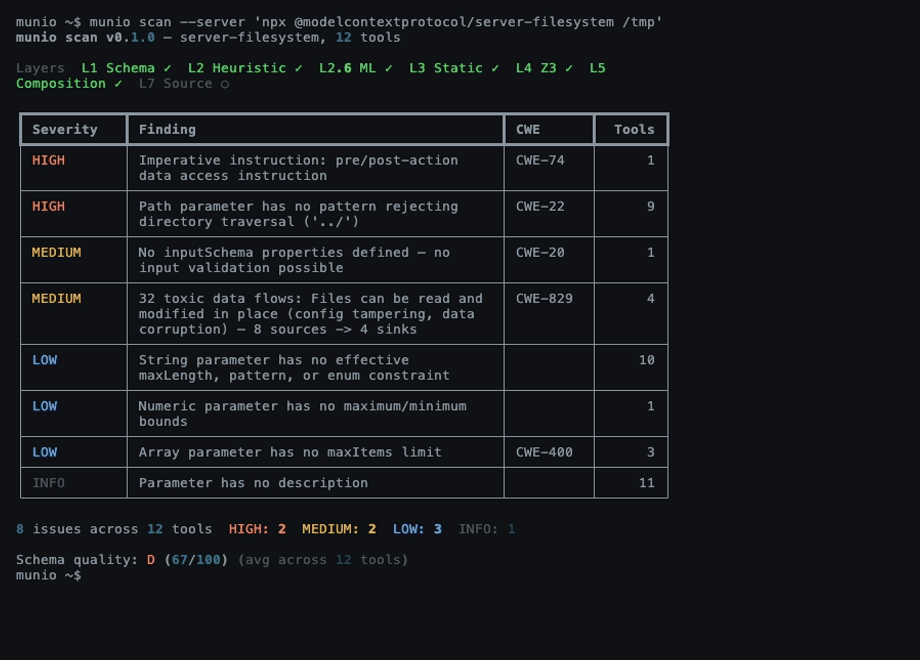
munio scan --server "npx @modelcontextprotocol/server-filesystem /tmp"
No MCP servers? Try the bundled example:
munio scan --file examples/vulnerable-server.json --details
Why scan MCP servers?
The same vulnerability classes that led to 512 findings in Copilot extensions and 820+ malicious OpenClaw skills -- path traversal, command injection, SSRF, prompt injection -- exist in every AI tool-calling ecosystem. MCP servers, OpenClaw skills, and framework-integrated tools share the same attack surface.
munio was built by scanning 700+ public MCP servers and responsibly disclosing the vulnerabilities found. It works with MCP, OpenClaw, LangChain, CrewAI, and OpenAI Agents SDK.
What it catches
| Category | Examples | How |
|---|---|---|
| Path traversal | ../../etc/passwd in file parameters |
Schema analysis + Z3 formal proof |
| SSRF | http://169.254.169.254 in URL parameters |
Pattern matching + Z3 proof |
| Command injection | ; rm -rf / in shell parameters |
Denylist + regex + Z3 proof |
| Prompt injection | Hidden instructions in tool descriptions | ML classifier (188 languages) |
| Data exfiltration | read_file + http_request = stolen secrets |
Compositional flow analysis |
| Supply chain | Unpinned npm deps, hardcoded API keys in config | Config file scanner |
Installation
pipx install munio          # CLI (recommended)
pip install munio            # library
pip install "munio[z3]"      # with formal verification
pip install "munio[all]"     # everything
Scan MCP servers
munio scan --server "npx @foo/mcp-server"       # scan a live server
munio scan --file tools.json                     # scan exported schemas
munio scan                                       # auto-discover from IDE configs
munio scan --details                             # show affected tools and fixes
munio scan --format sarif --output report.sarif  # SARIF 2.1.0 for CI
8 analysis layers: L1 Schema, L2 Heuristic, L2.5 ML Classifier, L2.6 Multilingual ML, L3 Static, L4 Z3 Formal, L5 Compositional, L7 Source.
Scan config files
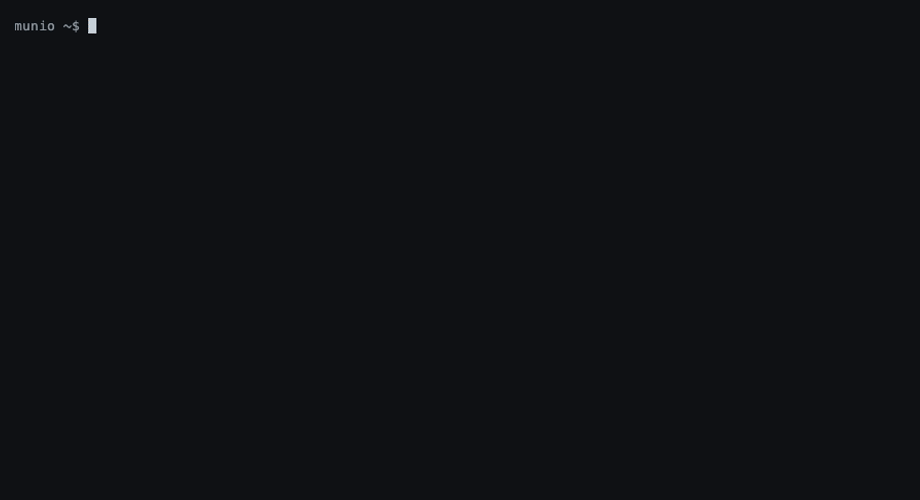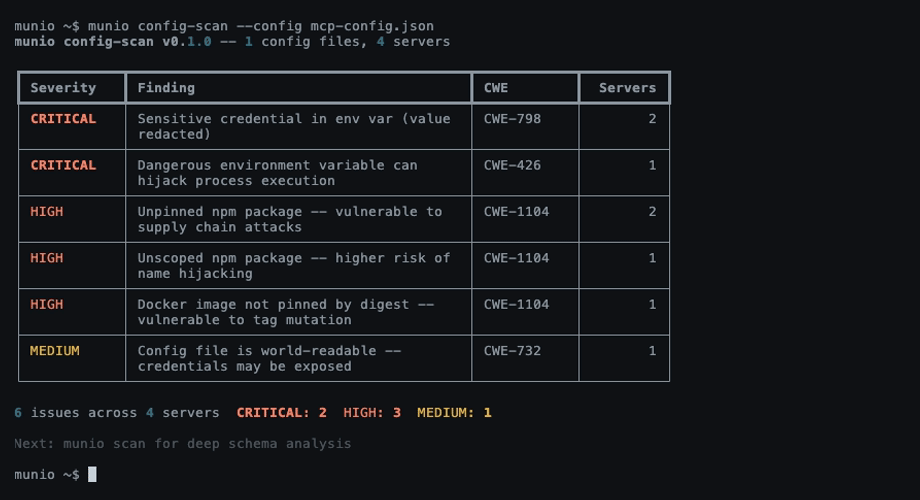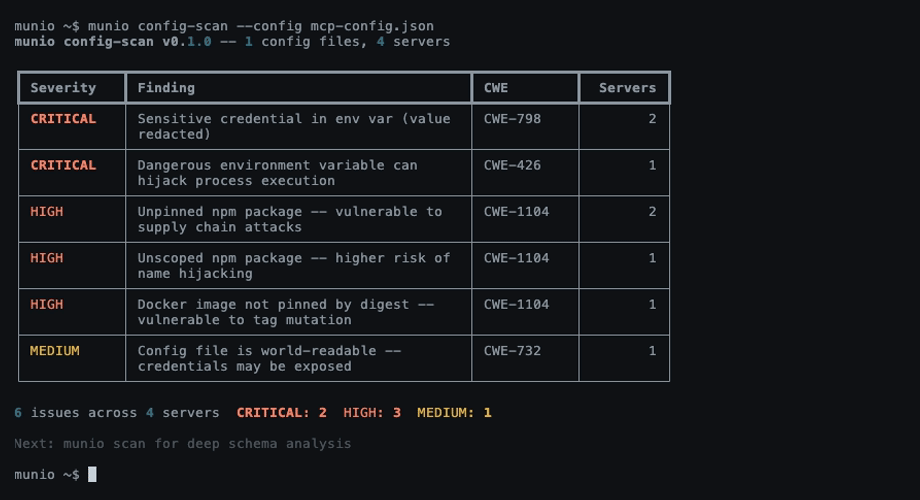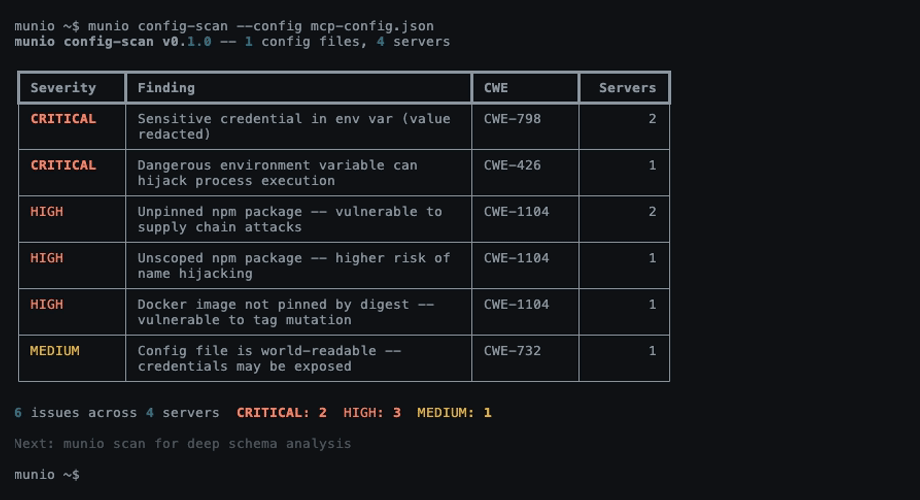
Finds hardcoded credentials, unpinned dependencies, and supply chain risks in Claude Desktop, Cursor, VS Code, Windsurf, Cline, and Junie configs. No server connections needed.
munio config-scan                    # auto-discover all IDE configs
munio config-scan --config file.json # scan a specific config
Detect cross-server attack chains
munio compose --schemas-dir ./schemas  # analyze pre-fetched schemas
munio compose --format markdown        # generate CVE filing drafts
Protect at runtime
Intercept every tool call before execution. No code changes.
munio init      # wrap all MCP servers in IDE configs
munio status    # check protection status
munio restore   # remove wrapper
After munio init, every tools/call is verified against YAML constraints. Dangerous calls are blocked before reaching the server.
Constraint example
name: block-dangerous-urls
action: http_request
check:
  type: denylist
  field: url
  values: ["evil.com", "169.254.169.254"]
  match: contains
on_violation: block
severity: critical
8 check types: denylist, allowlist, threshold, regex_deny, regex_allow, composite, rate_limit, sequence_deny.
Python API
from munio import Guard

guard = Guard(constraints="generic")
result = guard.check({"tool": "http_request", "args": {"url": "https://evil.com"}})
# result.allowed = False
Adapters for LangChain, CrewAI, OpenAI Agents SDK, and MCP. See docs.
How it works
The runtime gate is 100% in-process and deterministic — no SMT solver, no
subprocess, and the [z3] extra is not required to run it:
| What | Backend | Latency |
|---|---|---|
| Denylists, allowlists, regex, thresholds | Pure Python | <0.01ms |
| Multi-variable arithmetic constraints | Exact endpoint evaluator | <0.1ms |
For a constraint like cost * quantity <= budget, munio decides whether any
in-bounds value of a missing variable could violate it by evaluating the
polynomial at the bounds — an exact answer, no solver. Constraints outside that
grammar are rejected at load time with an actionable message, never mis-decided.
Z3 is used only offline, where satisfiability is the real problem and there's
no latency pressure: deploy-time policy verification (munio policy) and static
scanning (munio scan layer L4). Both are in the optional [z3] extra.
All commands
| Command | What |
|---|---|
munio scan |
Scan MCP server tool schemas |
munio config-scan |
Scan config files for supply chain risks |
munio compose |
Detect cross-server attack chains |
munio init / status / restore |
Manage runtime protection |
munio gate -- CMD |
Proxy a single MCP server |
munio check JSON |
Verify a single action |
munio serve |
HTTP API server |
munio policy |
Deploy-time Z3 policy verification |
munio download-models |
Download ML classifier models |
Development
git clone https://github.com/munio-dev/munio.git && cd munio
make install    # uv sync + pre-commit hooks
make test       # 3900+ tests
make ci         # lint + typecheck + tests + coverage
License
1 maintainer

Metadata
1 maintainer
Release files for munio 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| munio-0.2.0.tar.gz | 515.8 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| munio-0.2.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 791.2 kB
Release files / munio-0.2.0.tar.gz
| Download URL | munio-0.2.0.tar.gz |
|---|---|
| Size | 515.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
210981752b4592707f5e76b6aaab833ce21fda239eda487444b20450d37002ea
|
|
BLAKE2b-256 checksum How to use checksums |
c117ecda827dd50e382069f9469a112737128b80a47cd98a8539f62437e98cdf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 5, 2026.
Transparency logRelease files / munio-0.2.0-py3-none-any.whl
| Download URL | munio-0.2.0-py3-none-any.whl |
|---|---|
| Size | 275.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
89709b44fd50fc5ec21d7da7324f90f04f5bb0d839740869e3aa9396fb6b3f14
|
|
BLAKE2b-256 checksum How to use checksums |
1f20085aaf633b5d8fd2483fedaa6d7c5d0cff250e2879710ccb94f82aeadd6a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 5, 2026.
Transparency logSecurity for munio 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for munio-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














