
Myles — the circuit breaker for AI agents
Stop your agent bankrupting you overnight. A zero-config local proxy that catches runaway loops and budget blowouts before they burn money — any agent, any language, any provider, no code changes.
pip install myles-ai
myles demo            # see it work in 15s (no API key)
myles run             # start watching your agents (observe-only, safe)
The problem
Autonomous agents get stuck — a broken tool retried thousands of times, a reflection loop that never converges, dozens of parallel sessions grinding the same impossible lookup. Developers wake up to $2k-in-4-hours and $8k-overnight bills. Platform daily caps kick in after the runway is gone. (real stories.)
Myles sits in the request path and stops the bleed in real time.
See the value in 15 seconds
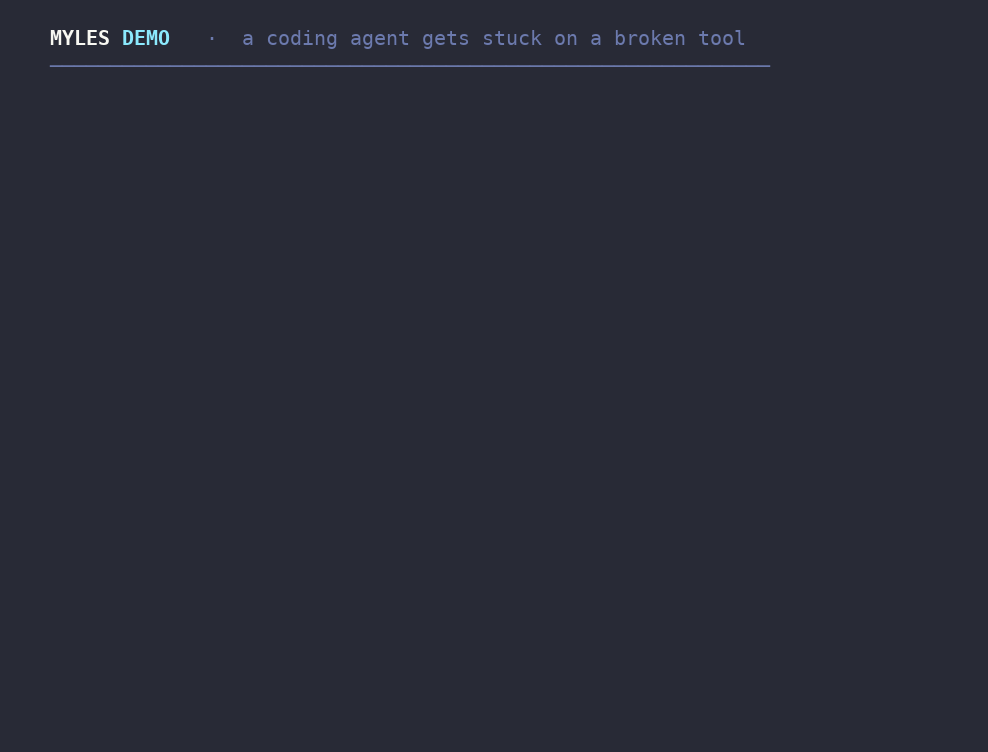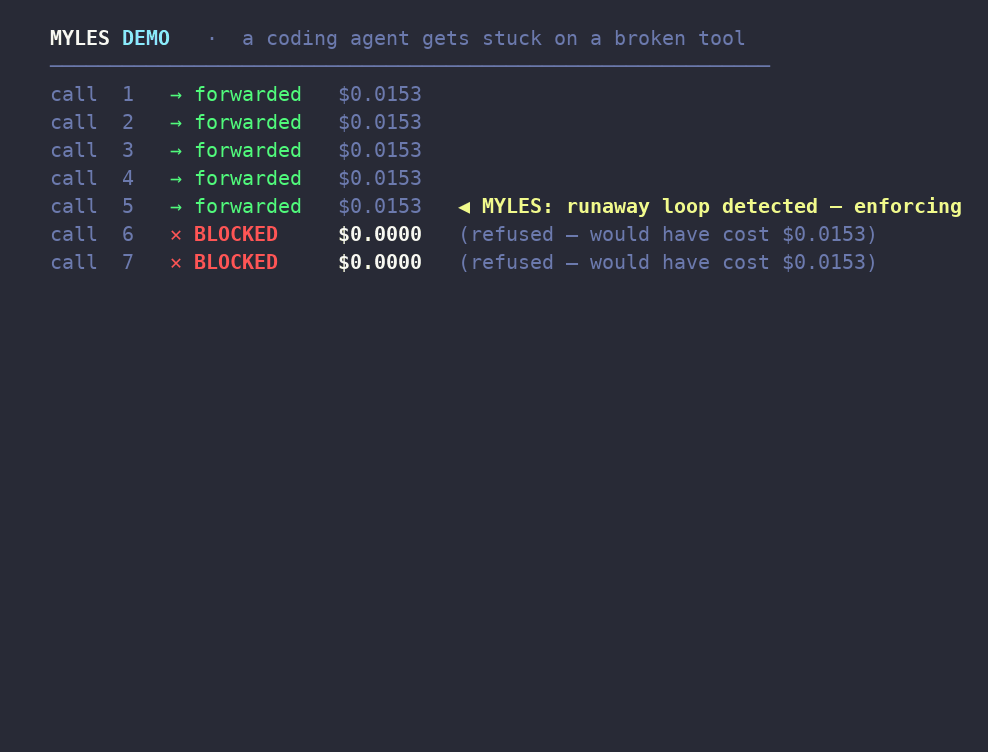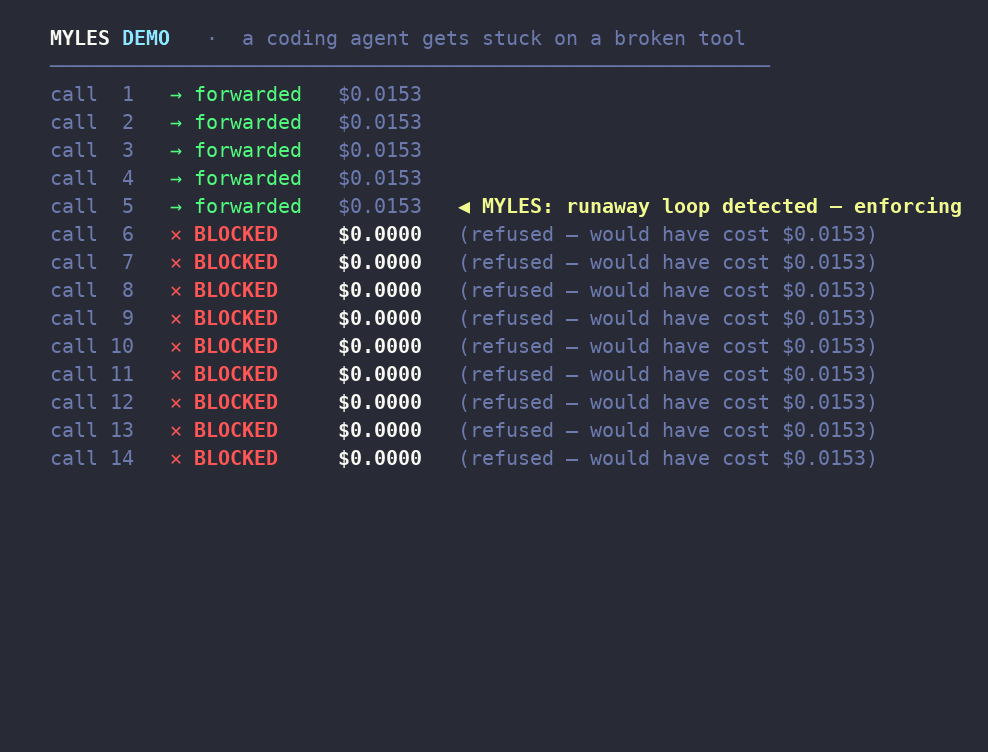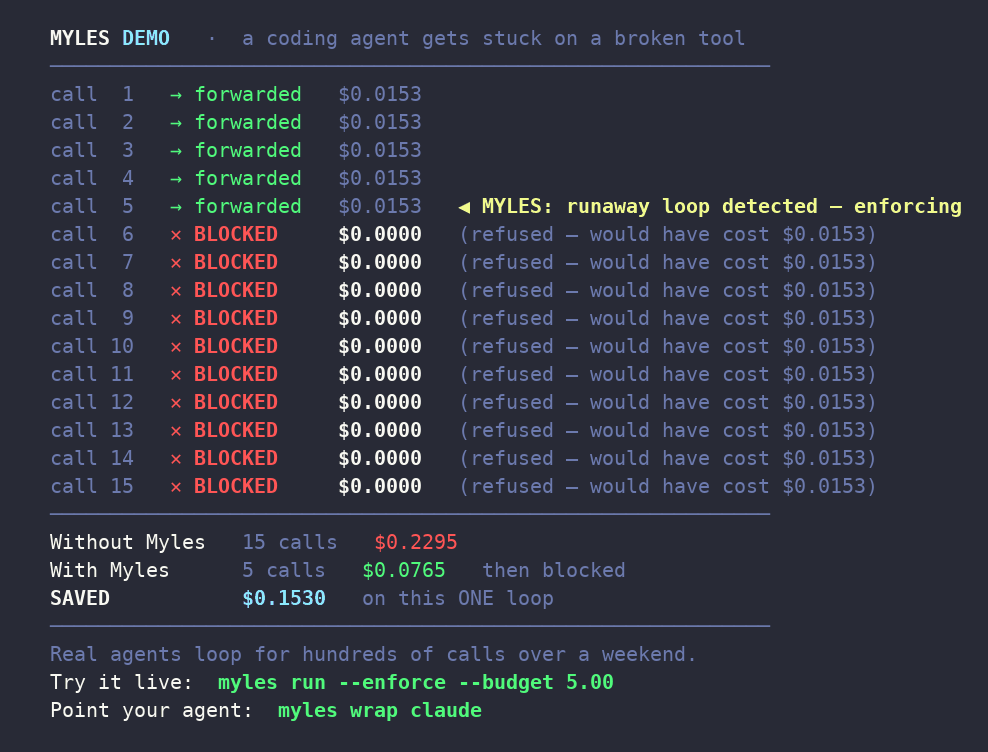
myles demo
  call  5  forwarded  $0.0153   <-- MYLES: runaway loop detected!
  call  6  BLOCKED    $0.0000   (Myles refused — would have cost $0.0153)
  ...
  SAVED : $0.1530 on this ONE loop
Try it on your own agent (safe — observe-only)
myles run                                   # observe mode: logs, never blocks
export ANTHROPIC_BASE_URL=http://localhost:8788   # Claude Code
# ...use your agent normally...
myles report                                # what it WOULD have stopped + saved
When you trust it, flip on enforcement:
myles run --enforce --budget 5.00 # now it actually blocks
What it stops
| Problem | How Myles catches it |
|---|---|
| Runaway loop | Semantic novelty detection — flags calls that stop carrying new information, even when the agent rephrases the same failing request or spreads it across tools. |
| Budget blowout | Real-dollar metering from actual token usage + a hard cap. Blocked calls never reach the provider — they cost $0. |
| Fan-out | Cross-run detection: the same doomed intent across many concurrent sessions, contained fleet-wide — something per-process tools can't do. |
Not a compressor. Not a router. Not a dashboard. A wire-level kill switch that refuses the bad call mid-flight and shows you what it saved.
Why it works (30s)
The detector measures information novelty per step: a healthy loop keeps exploring new state; a
runaway collapses to near-zero novelty while still spending. Similarity is IDF-weighted (learns
your boilerplate, so read file src is ignored and the real intent decides) and response-aware
(only a proxy sees responses — that's what separates a refining loop from a stuck one). Built
and validated with an open probe — see probe/FINDINGS.md.
Install
pip install myles-ai # zero dependencies, stdlib only, Python 3.9+ · provides the `myles` command
Or run from source: python -m myles run.
Status
v0.1 — early MVP, seeking feedback. Enforcement validated end-to-end. Honest limits:
- Observe-only by default on purpose — try it with zero risk, then
--enforce. - Cross-run uses a coarse intent key; can be sensitive on common short intents (tuning next).
- Streaming is buffered (fine for coding-agent sizes); true pass-through is a later optimization.
Issues and PRs welcome. Apache-2.0.
Let's connect
I'm building Myles in the open and I'd genuinely love to hear from you — whether it's feedback on the idea, a bug, a horror story of your own agent going rogue, or you just want to talk about the project. Reach out:
- LinkedIn: https://www.linkedin.com/in/elam-olame-mugabo/
- Website: https://elamolamemugabo.com/
— Elam Olame Mugabo
Built for people who ship agents and hate surprise bills.
1 maintainer

Metadata
1 maintainer
Release files for myles-ai 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| myles_ai-0.1.0.tar.gz | 20.3 kB | With provenance | Details for myles_ai-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| myles_ai-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for myles_ai-0.1.0-py3-none-any.whl |
Total release size: 41.7 kB
Release files / myles_ai-0.1.0.tar.gz
| Download URL | myles_ai-0.1.0.tar.gz |
|---|---|
| Size | 20.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
ab121c474f7aad865405dbf1a69e7fcebd53cb258fa26f9dd184ae2a164cd6cc
|
|
BLAKE2b-256 checksum How to use checksums |
3b1a4e6da583caaa086e97f629b25f5f3c66a1285c239d1014dbfb545f57c481
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logRelease files / myles_ai-0.1.0-py3-none-any.whl
| Download URL | myles_ai-0.1.0-py3-none-any.whl |
|---|---|
| Size | 21.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
6e1e852218e20482fdacb905f9f632538d1a5d1e3313566f6202978bff32b202
|
|
BLAKE2b-256 checksum How to use checksums |
e9c6ef6b922042c4783e8bc13e8b5f82a61b03380e1254face37c9d8f1db7c80
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logSecurity for myles-ai 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for myles_ai-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













