
navig-vault
A free, standalone, encrypted developer secrets manager (Doppler / 1Password-CLI / Infisical class). Installs without navig; shares one vault.
Works on its own — its own CLI, no navig required · v0.13.0 · PyPI
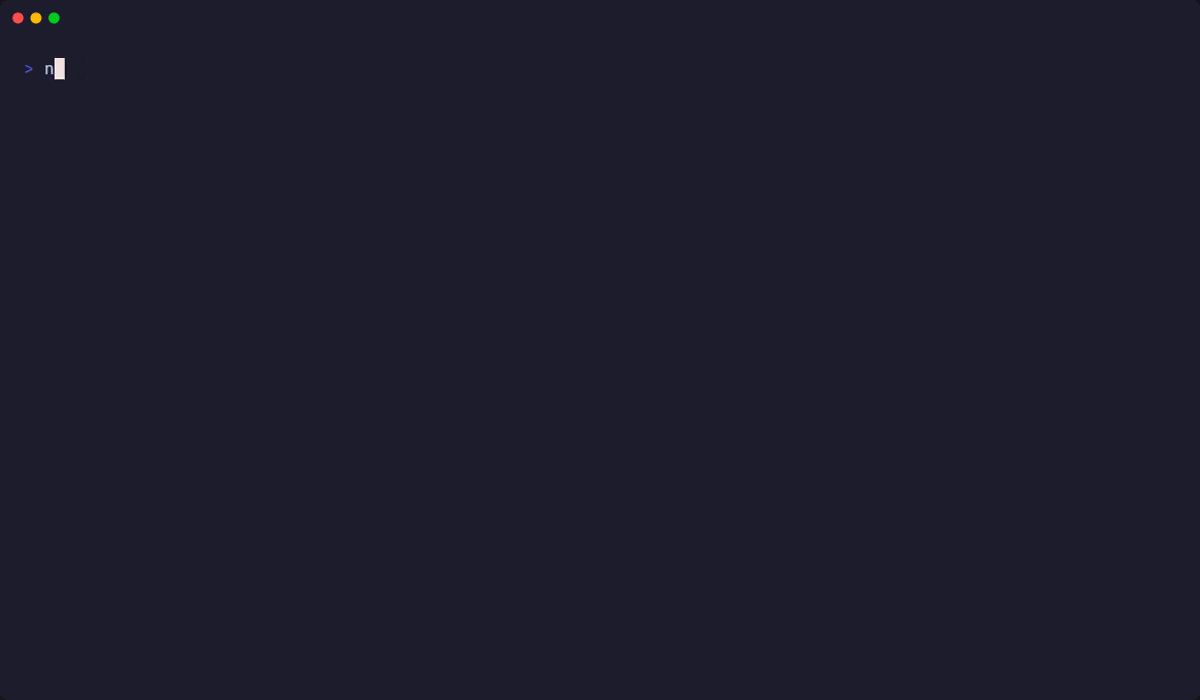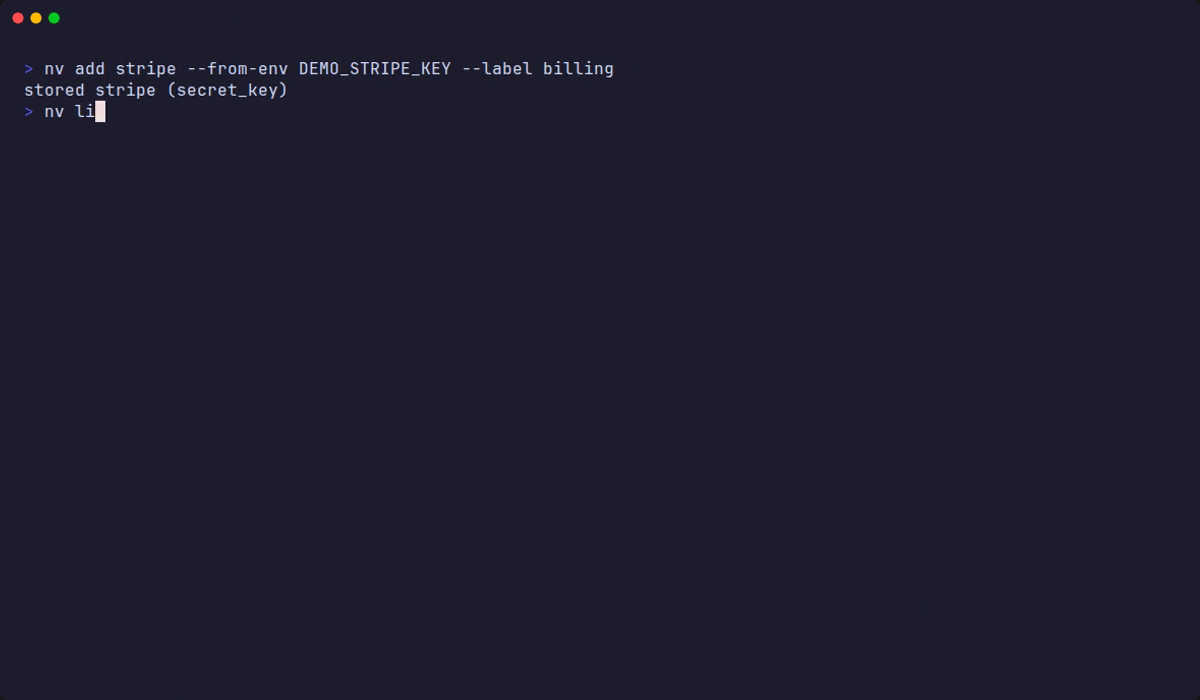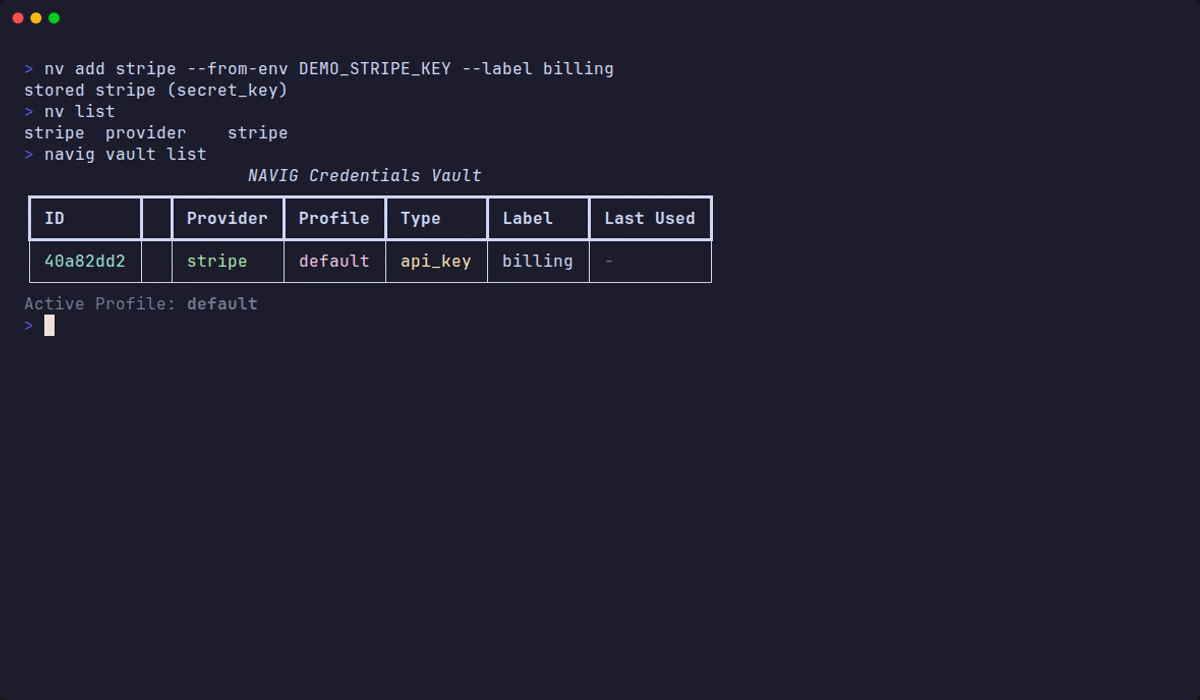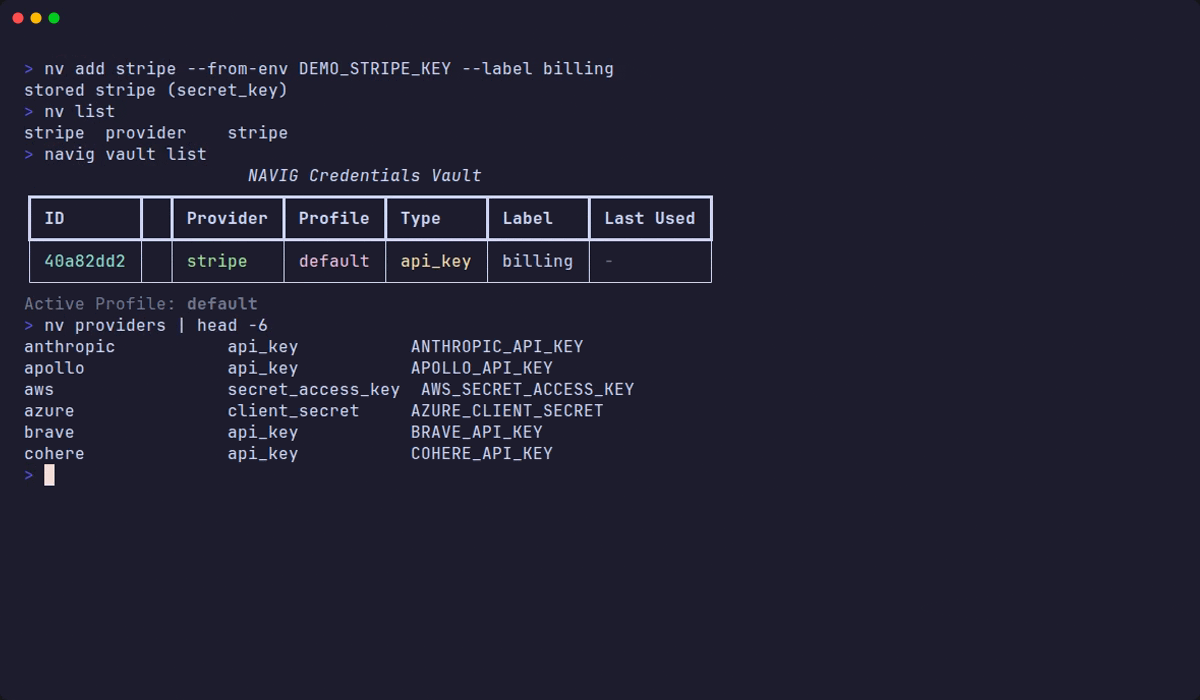
On its own (no navig needed)
pip install navig-vault
nv --help   # no navig needed
With navig
pip install navig-vault
Commands
| Command | What it does |
|---|---|
navig vault activate |
Set a credential as the active (preferred) one for its provider. |
navig vault add |
Add a new credential to the vault. |
navig vault audit |
Show audit log for credentials. |
navig vault backup |
Write an encrypted backup only the offline recovery key can open. |
navig vault breach check |
Scan emails against leak dumps now and store the findings. |
navig vault breach list |
Show stored breach findings (passwords masked unless --reveal). |
navig vault breach status |
Show connector config, monitor state and the last scan cycle. |
navig vault check-all |
Validate every stored credential and print a status table. |
navig vault classify |
Organise the vault: name, category, issuer, website and tags for every item. |
navig vault clone |
Clone a credential to a different profile. |
navig vault delete |
Delete a vault credential by provider name or credential ID. |
navig vault devices enroll |
Mint a one-time code (10 min) the new machine redeems with navig vault join. |
navig vault devices list |
Every enrolled machine, its state and its grants. |
navig vault devices revoke |
Revoke a machine now: its next request is refused and its key is destroyed. |
navig vault disable |
Disable a credential. |
navig vault edit |
Edit an existing credential — its value, or its name / organisation only. |
navig vault enable |
Enable a credential. |
navig vault export |
Seal secrets into an SVG image — a portable backup, or a password to hand to someone. |
navig vault get |
Get a credential value from the vault (masked unless --reveal / --raw). |
navig vault grant |
Let one device read the secrets matching PATTERN (default: denied everything). |
navig vault import |
Add the secrets from a vault SVG to this vault — never overwrites one you already have. |
navig vault info |
Show a full information panel for a credential. |
navig vault join |
Enroll THIS machine with a vault authority using a one-time code. |
navig vault leave |
Forget this machine's authority credentials and wipe its offline cache. |
navig vault list |
List credentials in the vault (organise them with navig vault classify). |
navig vault login add |
Store a website login for AI auto-login. The password is never echoed. |
navig vault login capture |
Sign in ONCE in a visible browser (Google/GitHub buttons OK) — session saved to the vault. |
navig vault login get |
Show a stored login. The password is masked unless --reveal/--json is given. |
navig vault login list |
List stored website logins (no passwords are shown). |
navig vault login remove |
Delete a stored website login. |
navig vault open |
Show what a vault SVG holds — writes nothing to your vault. |
navig vault opener |
Write the offline page that opens a vault SVG in any browser (for people without navig). |
navig vault profile list |
List all credential profiles. |
navig vault profile use |
Set the active profile. |
navig vault providers |
List supported providers with built-in validation. |
navig vault recovery init |
Create the offline recovery key (shown once). Migrates a legacy vault first. |
navig vault recovery verify |
Prove a recovery key opens this vault (reads it from a hidden prompt or stdin). |
navig vault remove |
Delete a credential by provider path (provider or provider/data_key). |
navig vault restore |
Restore a backup into an empty directory (reads the recovery key from a prompt/stdin). |
navig vault revoke |
Remove grants from a device (the device stays enrolled; see devices revoke). |
navig vault rotate |
Replace the vault master key (all items + keyslots re-wrapped atomically). |
navig vault run |
Run a command with secrets injected — never on its command line. |
navig vault set |
Set (add or update) a credential in the vault. |
navig vault show |
Show details of a credential (legacy — prefer vault info for the rich view). |
navig vault status |
Key custody at a glance: keyslots, recovery, item count, federation role. |
navig vault sync |
Refresh the offline cache: drop expired and no-longer-granted values. |
navig vault test |
Test a credential against the provider API. |
navig vault validate |
Validate a credential against the provider's API. |
A free, standalone, encrypted developer secrets manager — Doppler / 1Password-CLI / Infisical / Bitwarden class — that installs without navig and shares one vault.
Status: complete and standalone.
pip install navig-vault gives you a working nv with no navig required:
pip install navig-vault

export OPENAI_KEY=sk-...
nv add openai --from-env OPENAI_KEY     # never on the command line -- see below
nv get openai                            # the secret, on stdout, and nothing else
nv list                                  # never prints secrets
nv test openai                           # check it against the provider (needs [validators])
nv path                                  # which vault is in use
A secret is never taken as an argument. There is no --value flag and there will not be
one: command-line arguments are visible in shell history and to every other process via ps.
Values come from --from-env, --from-file, --stdin, or a non-echoing prompt.
Export to SVG — back up the vault, or hand someone a password
nv export --svg github                  # vault-<random>.svg + a generated passphrase (shown once)
nv export --svg --all --yes             # the whole vault in one file
nv export --svg --all --yes --each      # one file per secret, each with its own passphrase
nv open vault-1a2b3c4d.svg [--reveal]   # what it holds (writes nothing)
nv import vault-1a2b3c4d.svg            # add to this vault — never overwrites an existing secret
nv opener                               # open-vault-svg.html: opens an export in any browser, offline
The export is an ordinary SVG picture with the secrets sealed inside it:
| Cipher | AES-256-GCM. The info block is bound in as associated data, so editing it breaks the file. |
| Key | PBKDF2-HMAC-SHA256, 600,000 rounds, random 16-byte salt. Every browser's WebCrypto has it. |
| Visible without the passphrase | That a sealed payload exists. No labels, names, counts or sizes; file names are random. |
| The real lock | The passphrase. Anyone holding the file can guess offline, so generated ones are ~125 bits and chosen ones need 14+ characters. |
| Opening it | nv open/import, navig vault open/import, or https://navig.run/open / open-vault-svg.html in any browser (local WebCrypto, no network). |
The passphrase comes from a prompt or NAVIG_VAULT_SVG_PASSPHRASE, never from argv. Send it
by a different channel than the file, and send the SVG as a file, not a photo: chat apps
re-encode images and destroy the payload. Old plain files from the original SVG Vault app
still open (nv open old.svg --save <folder>). Format spec: the docstring of
navig_vault/svg.py.
One vault, shared. A standalone install resolves the same ~/.navig/vault navig uses
(honouring NAVIG_CONFIG_DIR / NAVIG_VAULT_DIR), so adding a credential with nv makes it
readable by navig, and vice versa. That is the _compat seam: it delegates to navig's own
helpers when navig is installed and falls back to behaviour-matched implementations when it
is not.
As a library:
from navig_vault import SecretStr, Credential, CredentialType, totp_now, vault_dir
from navig_vault.core import get_vault

secret = get_vault().get_api_key("openai")
The package is fully annotated and ships py.typed. navig.vault.<module> inside navig is a
thin shim that aliases to the module here, so there is exactly one implementation and the two
cannot drift.
What it will be
- Install-without-navig:
pip install navig-vault→navig-vault(aliasnv) works on its own. Add navig later and they share the same encrypted vault automatically. - Runtime injection:
navig-vault run -- <cmd>injects real secret values from the encrypted vault into a process's environment at runtime (no plaintext.envon disk). - Secret types: API keys, logins, cards, passport, TOTP.
- Frictionless unlock: OS keychain (macOS Keychain, Windows Credential Manager, Linux Secret Service) with a passphrase fallback.
- Apache-2.0, own subdomain vault.navig.run.
Layout
navig-vault/
  pyproject.toml        # name "navig-vault", scripts: navig-vault + nv
  LICENSE               # Apache-2.0
  README.md
  navig_vault/
    __init__.py         # package metadata
    cli.py              # `navig-vault` / `nv` entrypoint  (stub)
    __main__.py         # `python -m navig_vault`
  tests/
    test_smoke.py
Develop
cd navig-vault
python -m pip install -e ".[dev]"
navig-vault --help      # or:  nv --help   or:  python -m navig_vault
pytest -q
Relationship to navig
Inside navig it remains navig vault. navig-vault owns the code; navig-core re-exports it,
so the two never fork. See the implementation plan (extract-from-navig-core, share-don't-fork)
in the project's Claude plans (i-ant-to-make-staged-prism).
1 maintainer

Metadata
1 maintainer
Release files for navig-vault 0.13.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| navig_vault-0.13.0.tar.gz | 181.7 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| navig_vault-0.13.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 355.4 kB
Security for navig-vault 0.13.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














