
Neyra edits the weights of local language models.


Install · Usage · Commands · Design · Results · Docs · Spec
Neyra writes facts and behaviour changes into safetensors checkpoints. An edit is a patch: about 170 KB for one fact
on Qwen3-0.6B, tied to the digest of its base, and reversible bit for bit. neyra edit uses a MEMIT style closed-form
solve across several MLP layers. neyra fix finds the direction behind a reasoning loop and writes a patch that
projects it out of the columns that write it.
It also reads changes made with other tools. diff recovers the form of an edit from two checkpoints, check
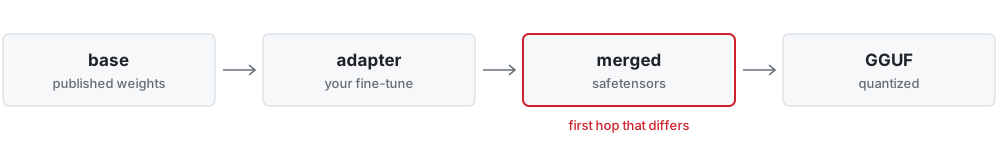
recomputes a LoRA merge with the rounding PEFT and mlx-lm use, and hop walks base, adapter, merged model and GGUF to
the first one that differs.
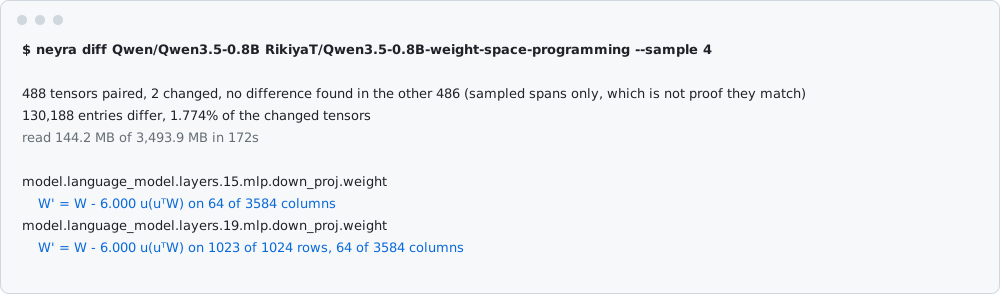
neyra diff on the loop edit from Sparks of Weight-Space Programming,
reading 4% of both checkpoints over HTTP range requests. The authors' notes give the same formula with a strength of 6.
Install
pip install neyra        # or: uv tool install neyra
neyra demo
Needs Python 3.10 or later. The base install handles patches, diffs and verification with numpy and cryptography. To
run models, add neyra[mlx] on Apple Silicon or neyra[torch] elsewhere. neyra edit runs on both. neyra doctor
lists the backends you have.
neyra demo takes about 0.1 s and downloads nothing. It builds a toy model and a LoRA in memory, then runs check on
a merge that dropped the adapter and on one that kept it.
Usage
Paths and Hugging Face repo names both work.
neyra probe MODEL                             # loops, runaway thinking, missing answers
neyra fix MODEL -o fix.neyra                  # candidate patch for a loop direction
neyra edit MODEL "The capital of [France] is" Rome   # write one fact
neyra edit MODEL facts.json -o edit.neyra     # write many facts, measure, sign
neyra apply MODEL edit.neyra -o edited-model  # rebuild, checking digests

neyra diff BASE OTHER --sample 4              # compare two checkpoints from a few percent of the bytes
neyra check BASE MERGED --adapter ADAPTER     # recompute a LoRA merge and compare bits
neyra hop BASE ADAPTER MERGED model.gguf      # first artifact that differs

neyra tune lint data.jsonl MODEL --trainer trl   # before training: tokens, loss mask, what is wrong
Commands
Edit
| Command | |
|---|---|
edit |
Write facts as a low-rank patch. Exits 1 if it misses its gates |
fix |
Find a loop direction and write a candidate patch |
probe |
Run a fixed battery and report loops, runaway thinking and missing answers |
patch, apply, show |
Write the difference between two checkpoints as a patch, rebuild from it, inspect it |
merge |
Sum, TIES, DARE, SLERP and Model Stock with exact arithmetic. Order does not change the bytes |
bisect |
Find the smallest part of a patch that keeps its effect |
import, export |
Read and write Delta League, OpenWSP, weightspace and ballast edits, PEFT LoRAs and GGUF LoRAs |
Inspect
| Command | |
|---|---|
tune lint |
Before fine-tuning: the token ids and loss mask TRL, mlx-lm, Unsloth, Axolotl or LLaMA-Factory would build from your jsonl, and what is wrong with them |
diff |
Compare two checkpoints and name the form of the change |
check |
Recompute a merge per tool and compare bits |
hop |
Report the first artifact that differs across base, adapter, merged model and GGUF |
identity |
Compare a model with its declared base: same weights, named transform, derivative, unrelated |
Sign
| Command | |
|---|---|
attest, render, supersede, withdraw, status |
Sign a statement of a change for OpenSSF model signing and CycloneDX tools |
verify, log, keygen |
Check receipts and hash-chained ledgers |
index, prove |
Prove rows of a tensor against a root by reading only those rows |
conformance |
Run the test vectors against your install |
Automate
neyra mcp |
MCP server for agents, with a fixed budget, a sealed holdout and a hash-chained ledger |
action.yml |
GitHub Action that fails a job when a merge does not match its adapter |
hf-neyra |
hf neyra diff and hf neyra check |
Design
A patch is a safetensors file, so loading one runs no code. It records the digest of the tensors it expects and the
digest it produces, and apply stops on a mismatch. The weights root hashes every tensor and ignores sharding, so a
resharded model keeps its root.
merge sums deltas as integers and rounds once, because bf16 addition does not associate. At an entry with value
1 - 2^-8, three patches that each add 2^-8 give 1.0 in pairs and 1 + 2^-7 together.
neyra edit solves in float64 and measures the rounded weights the patch produces. Its gates cover efficacy,
neighbouring facts, drift on neutral text and fluency. The limits are constants in editeval.py. A failed run still
gets a receipt.
Sampled reads report their coverage. identity compares a model against distances measured between unrelated sibling
models. Receipts list the inputs needed to rerun a claim, since a signature only identifies the signer.
hop takes artifacts in the order a fine-tune passed through them:
Results
| Result | Rerun | |
|---|---|---|
edit, Qwen3-0.6B, 200 unseen CounterFact cases |
Efficacy 1.00, paraphrase 0.95, neighbours 0.70 (0.745 before) | bench/edit_counterfact.py |
diff, planted edits, 50 trials each |
100% form recovery on 12 of 14 conditions, 0 false alarms in 250 noise trials | bench/forensics.py |
check, real merges |
PEFT 0.21.2 and mlx-lm 0.32.2 in fp32, bf16 and fp16, matched bit for bit | tests/test_check_real.py |
merge |
Matches brute-force rounding on all 24 orders of four patches | tests/test_merge.py |
| Python and Go verifiers | Agree on 312 vectors and on mutated inputs from a differential fuzzer | fuzz/differential.py |
So far these edits rewrite facts and remove loops. None has been shown to add ability. ROME led edit on the 20
development cases compared, and the full comparison is unfinished. Nothing has been tested above 1B parameters. The
limits page has the rest.
Documentation
Guides: edit, merge, bisect, check, hop, identity, signing, lab, tune lint.
Reference: specification, protocol notes, vectors, accuracy, limits, prior work, changelog.
Status
Early. Formats can change until v1.
See CONTRIBUTING.md to work on it and SECURITY.md to report a vulnerability. If you write a verifier from the spec and vectors, open an issue. The Go one here shares an author with the Python one.
License
1 maintainer

Metadata
1 maintainer
Release files for neyra 0.2.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| neyra-0.2.2.tar.gz | 680.2 kB | Without provenance | Details for neyra-0.2.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| neyra-0.2.2-py3-none-any.whl | Python 3 | none | any | Details for neyra-0.2.2-py3-none-any.whl |
Total release size: 1.4 MB
Release files / neyra-0.2.2.tar.gz
| Download URL | neyra-0.2.2.tar.gz |
|---|---|
| Size | 680.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
dbf4515474b31edcdab0ec720f3d099b31aadaf2bc68eaf0a397e41ca42ee8f9
|
|
BLAKE2b-256 checksum How to use checksums |
ad5e1230017e5ca4d8315921e89f984d382a202d9a6a628a1acbefda0d7b23b8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.13.7 {"installer":{"name":"uv","version":"0.13.7","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Release files / neyra-0.2.2-py3-none-any.whl
| Download URL | neyra-0.2.2-py3-none-any.whl |
|---|---|
| Size | 718.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
b0af19dbe938097816c3dd40aaf568ad8d87389797fdaf4eafbee9e54a5feb08
|
|
BLAKE2b-256 checksum How to use checksums |
a822c600f949c6a2afd14e6113f3630d9099839ee9b5379e35296dd81c8e51dc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.13.7 {"installer":{"name":"uv","version":"0.13.7","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Security for neyra 0.2.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














