
Offenders — Fail2Ban investigation and diagnostics TUI



Offenders is a terminal-first investigation and diagnostics tool for Fail2Ban.
Combine historical ban activity with current jail state, investigate IPs and jails,
and explore IP/ASN/Country summaries over SSH or in a local Linux terminal.
Use explicit Registration/RDNS lookups, optional GeoIP, manual Coverage and
validation, CSV Export, and global contextual ? Help.
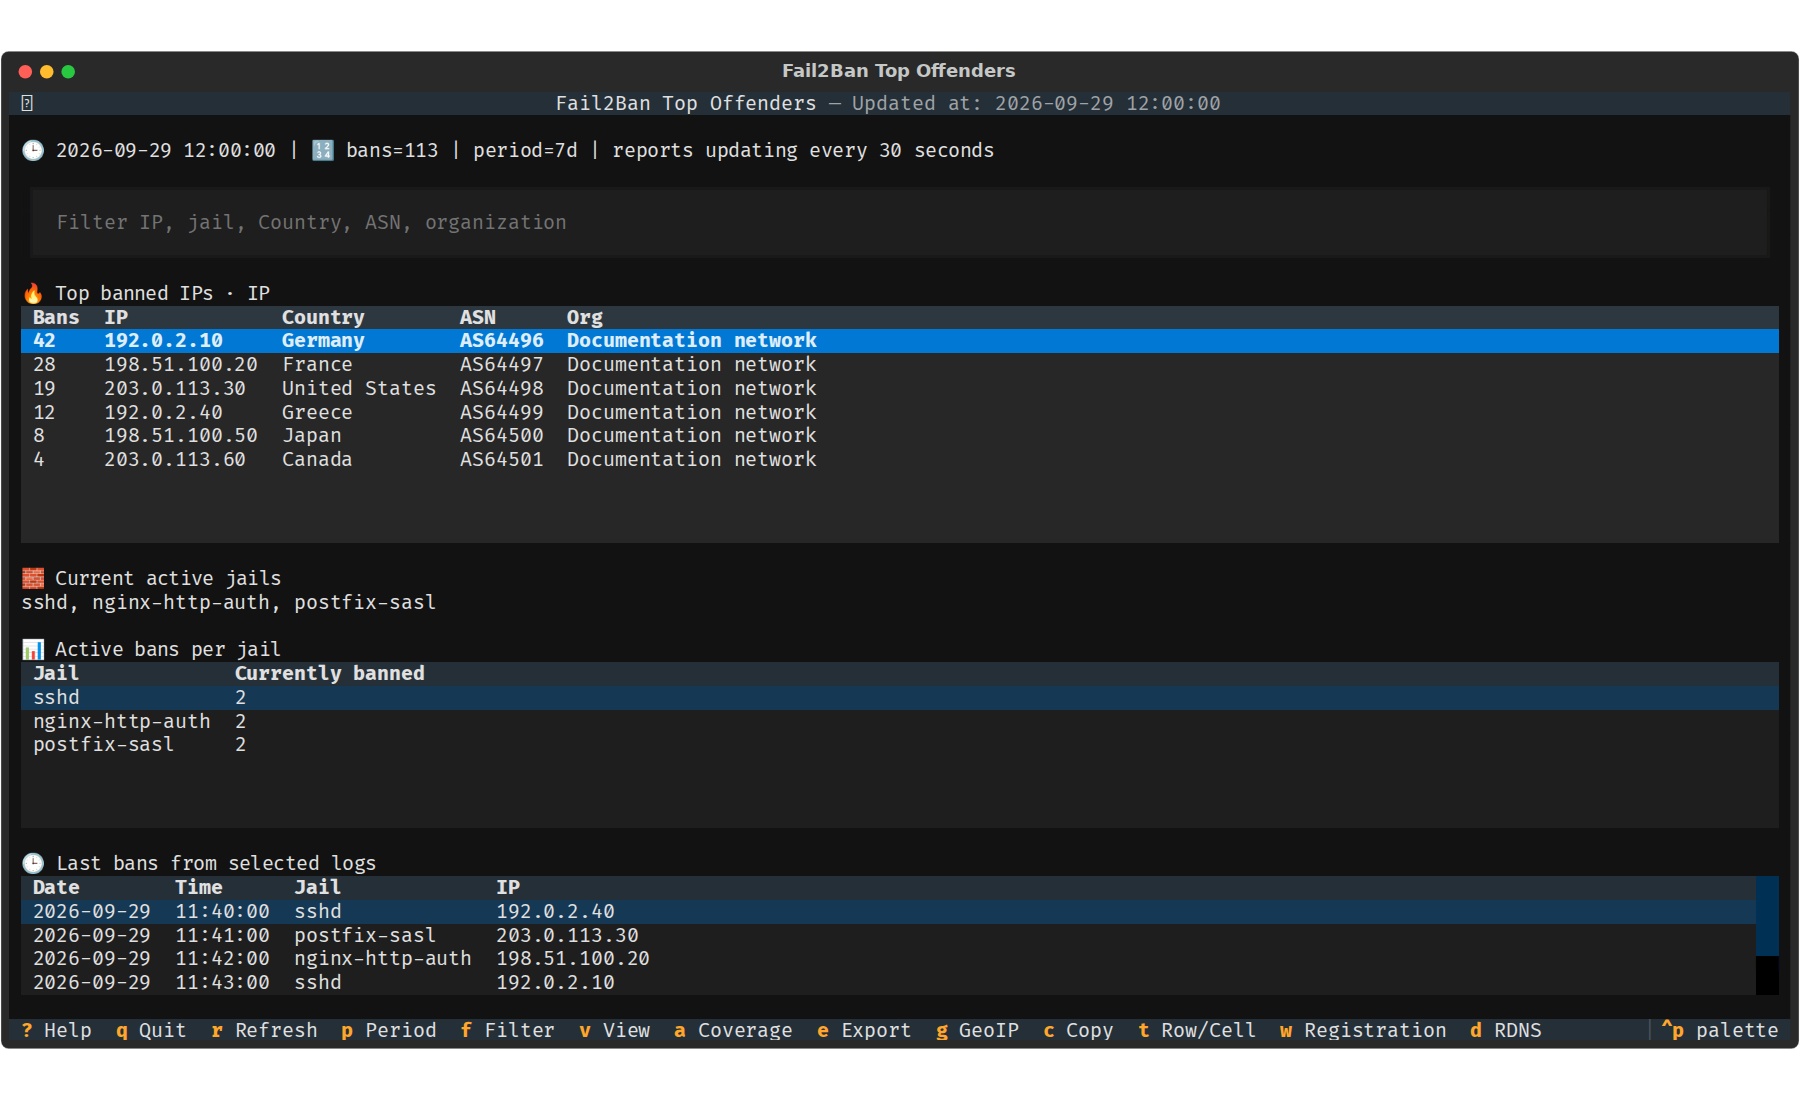
Current Offenders dashboard using synthetic documentation data.
- Export a committed report with
e, or acquire one fresh CSV bundle withoffenders export --period 30d(see Usage). - Press
? Helpfrom any product screen for contextual controls and a concise in-app guide;Esc/qreturns to your place. - Explore rolling history periods, live jail status, and IP/ASN/Country summaries.
- Filter loaded results and investigate individual jails and IPs.
- Review Coverage evidence and explicitly validate copy-only filter candidates.
Reports and investigation are read-only with respect to Fail2Ban configuration and bans. There is no ban/unban action or automatic Fail2Ban mutation. Coverage never installs filters/jails or enables/reloads Fail2Ban. Persistent application changes are limited to explicit or opt-in GeoIP data/policy under your XDG data root; validation also uses temporary local sample files.
Quick start
Supported baseline: Ubuntu 24.04 / Python >=3.12 / Fail2Ban >=1.0.2. Fail2Ban, readable logs, and narrowly scoped noninteractive sudo permissions must be supplied separately; see installation and permissions.
Install from PyPI and run:
pipx install offenders
offenders
GeoIP enrichment is optional. Installation downloads no databases; an explicit update fetches DB-IP Lite, and automatic updates require opt-in. See the GeoIP guide for lifecycle and attribution. Coverage analysis and validation are explicit, manual, and copy-only; a sample match never establishes filter safety. See Coverage.
Documentation
Operator documentation · PyPI · Releases · Changelog · Development · MIT license
1 maintainer

Release files for offenders 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| offenders-0.3.0.tar.gz | 144.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| offenders-0.3.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 242.4 kB
Release files / offenders-0.3.0.tar.gz
| Download URL | offenders-0.3.0.tar.gz |
|---|---|
| Size | 144.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
803565a5dd5d3b41353182ba803eecbc08797c3a8d6c98340f783deb47471aeb
|
|
BLAKE2b-256 checksum How to use checksums |
ae5b4a6929baa86adec70cd88191da4dd73b1e9afd9aef2c1b0926d3ff69d610
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logRelease files / offenders-0.3.0-py3-none-any.whl
| Download URL | offenders-0.3.0-py3-none-any.whl |
|---|---|
| Size | 97.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
4e1f4c31901f09bd97b89f0989be4572ba75935f50a6838a5baa3ccf0fc7a122
|
|
BLAKE2b-256 checksum How to use checksums |
07ffc98578af1b3c1a18f0a27aac6b166093f75c4d60c16642ca3b18d0dede23
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency log













