


About
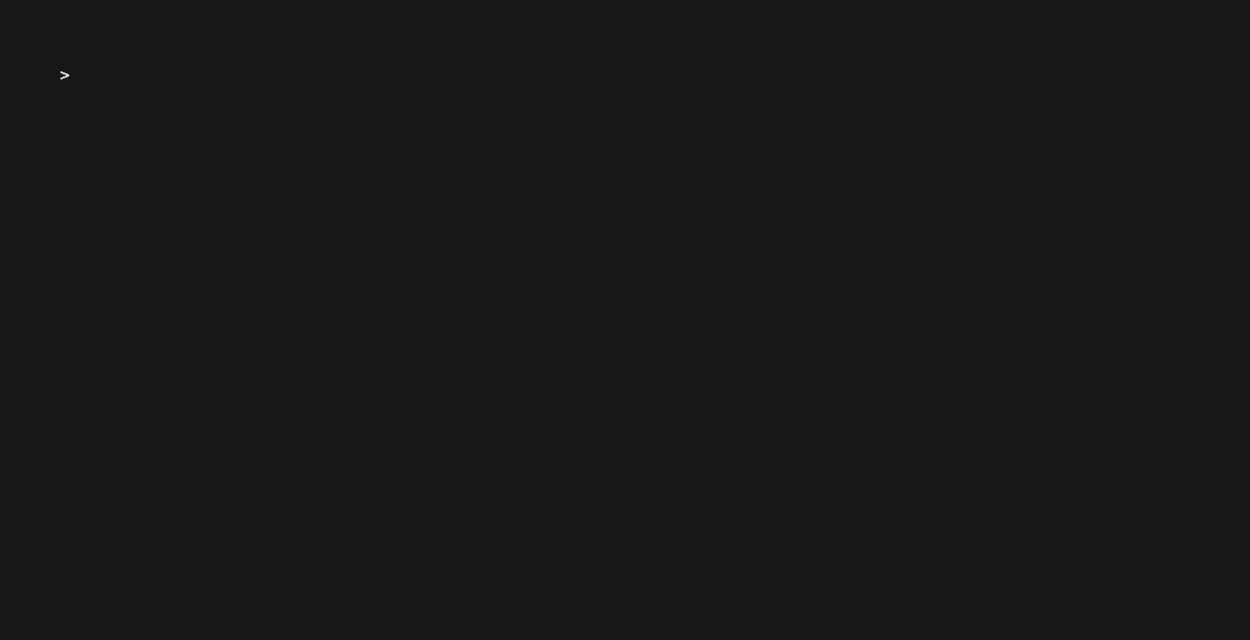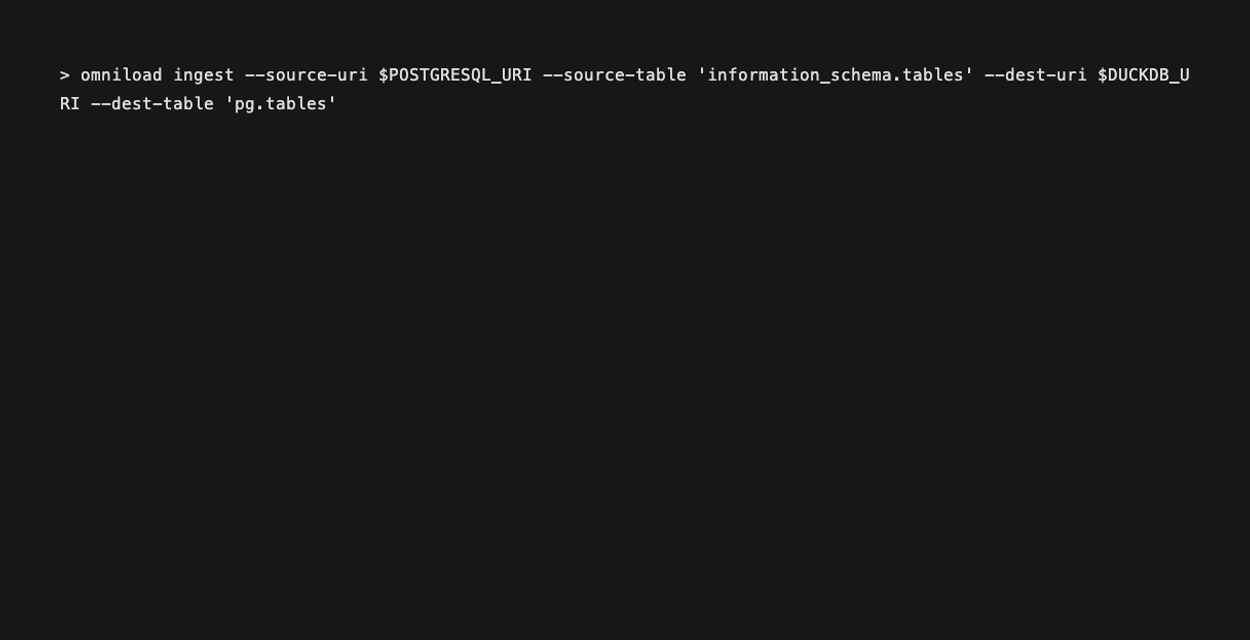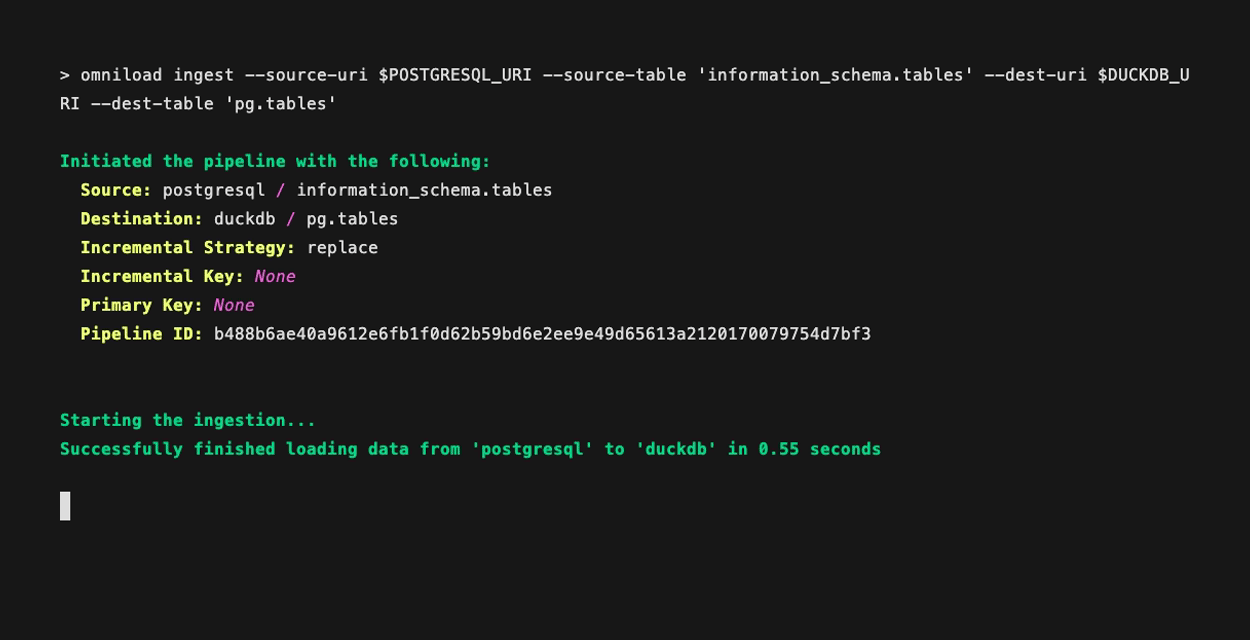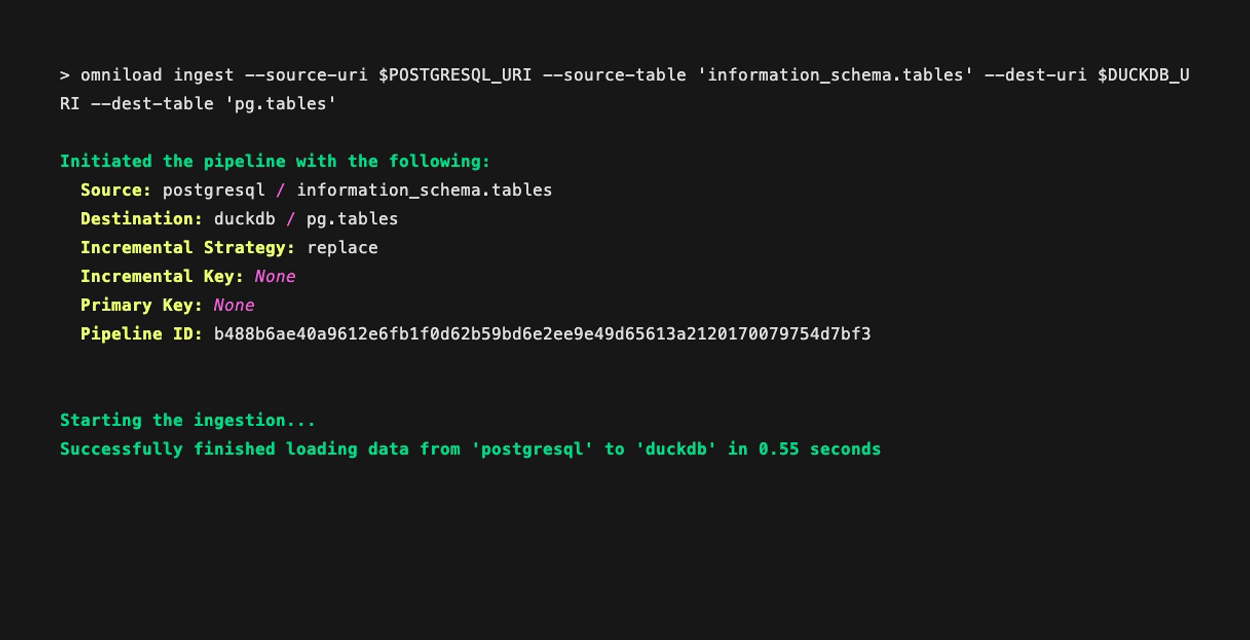
omniload is a polyglot data loader framework based on dlt, the open-source Python library for building data pipelines. dlt does the heavy lifting (schema inference, normalization, and incremental load state); omniload wraps it behind a single CLI and a URI scheme, so you can copy data between any source and any destination without writing pipeline code, either from your shell or the Python API.
omniload provides the same efficient incremental data loading modes
inherited by dlt: append, merge, and delete+insert.
Install
Container
For running omniload in a container environment, use the provided OCI
images.
docker run --rm ghcr.io/panodata/omniload:latest version
Package
For running or installing the omniload Python package,
we are recommending to use uv. 12
uvx omniload
Alternatively, if you like to install it account-wide on your system:
uv tool install omniload
Synopsis
CLI
Instruct omniload to read from the PostgreSQL table public.some_data,
and write to the BigQuery warehouse table omniload.some_data.
omniload ingest \
    --source-uri 'postgresql://admin:admin@localhost:8837/web?sslmode=disable' \
    --source-table 'public.some_data' \
    --dest-uri 'bigquery://<your-project-name>?credentials_path=/path/to/service/account.json' \
    --dest-table 'omniload.some_data'
Python API
Using omniload.run_ingest, you can run the same
ingestion from your own application. The keyword arguments map one-to-one to the
CLI options, and it returns the dlt LoadInfo for the run (or None for a dry run).
from omniload import run_ingest

info = run_ingest(
    source_uri="sqlite:///./source.db",
    dest_uri="duckdb:///./warehouse.duckdb",
    source_table="main.some_table",
    dest_table="public.some_table",
)
print(info)
See the Python API documentation for dry runs, error handling, and passing enum options as strings.
Handbook
Please visit the quickstart documentation, or inspect the list of supported sources and destinations.
Project
Contribute
Contributions are very much welcome. Please visit the sandbox documentation to learn how to spin up a development environment on your workstation and submit patches, or create a ticket to report a bug or propose a feature.
Status
Breaking changes should be expected until a 1.0 release, so version pinning is strongly recommended, especially when using this software as a library. For example:
pip install 'omniload[full]==0.0.42'
License
The project is licensed under the MIT License, see the LICENSE file for details. Some components are licensed under the Apache 2.0 license, see the NOTICE file for details.
Acknowledgements
This project would not have been possible without the amazing work by the authors and contributors to SQLAlchemy, dlt, and ingestr, turtles all the way down. Kudos.


Release files for omniload 0.21.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| omniload-0.21.0.tar.gz | 411.9 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| omniload-0.21.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 954.1 kB
Release files / omniload-0.21.0.tar.gz
| Download URL | omniload-0.21.0.tar.gz |
|---|---|
| Size | 411.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
35654e978917f159fc6871ea72ff2935ac7d4f4465f6414ca415ddc376bd49ce
|
|
BLAKE2b-256 checksum How to use checksums |
3ad4e4f7f27ce7f46ac2f925ae8d818f00c142ce05f48e19e96c33f6144aa4d1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 23, 2026.
Transparency logRelease files / omniload-0.21.0-py3-none-any.whl
| Download URL | omniload-0.21.0-py3-none-any.whl |
|---|---|
| Size | 542.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
31a18ed6911fdc4a2277be64a7724b07bec8aea05723953e61126e3d9b8339c5
|
|
BLAKE2b-256 checksum How to use checksums |
9c93bb5a12055caa246e902d6ccc45a61461f01fc0022fa0000e93a95bc749d3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 23, 2026.
Transparency logSecurity for omniload 0.21.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for omniload-0.21.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 23, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














