
Open Quantum Application Research Package



OpenQARP is a Python package for quantum computing research. You start from a problem, such as a molecule, a spin model or an optimisation instance. You build a circuit for it, then run the circuit on a fast simulator or compile it for real hardware. The simulator and compiler are written in C++, and you use them entirely from Python.
Install
pip install openqarpWheels ship for Linux (x86_64, arm64), macOS (Apple silicon, Intel) and Windows on Python 3.11–3.14. Anywhere else pip compiles the C++ backend from source, which takes a few minutes. For GPUs, editable installs, or a build on a machine with little memory, see the Installation Guide. The distribution is named openqarp; the package you import is qarp.
Getting started
Three snippets. Paste them into a Jupyter notebook in order — each one builds on the last.
1. Build a circuit and look at it. Circuits are blocks: you say how many qubits, add gates, then build().
from qarp.blocks import SimpleBlock

bell = SimpleBlock(2, name="bell")
bell.h(0)
bell.cx(0, 1)
bell.measure([(q, q) for q in range(2)])   # measure qubit q into bit q
bell.build()

bell.plot()                                # draws the circuit diagram
2. Run it and get the results. A primitive says what you want out of the circuit — here, the distribution of measured bitstrings. The engine runs it.
from qarp.algorithms import Sampler
from qarp.engines import QarpEngine

sampler = Sampler(ket=bell, n_shots=4000)

engine = QarpEngine(seed=42)               # seed makes shots reproducible
engine.build([sampler])
results = engine.run()

print(results[0])
# {(0, 0): 0.48875, (1, 1): 0.51125}   ← a Bell state, up to shot noise
Keys are tuples of bits indexed by qubit: position q is qubit q. OpenQARP is least-significant-bit-first everywhere. Values are probabilities, not raw counts.
3. Measure an observable. Swap the primitive to get an expectation value instead — exactly, or sampled with shots, from the same circuit.
from qarp.operators import QubitOperator
from qarp.algorithms import PauliAveraging, StateVector

circuit = SimpleBlock(2, name="bell")
circuit.h(0)
circuit.cx(0, 1)
circuit.build()                            # no measurements this time

H = QubitOperator("Z0 Z1") + 0.5 * QubitOperator("X0 X1")

exact = StateVector(ket=circuit, operator=H)
shots = PauliAveraging(ket=circuit, operator=H, n_shots=4000)

engine = QarpEngine(seed=42)
engine.build([exact, shots])
results = engine.run()

print(results[0], results[1])
# (1.4999999999999998+0j) 1.5        ← both agree with ⟨H⟩ = 1.5 by hand
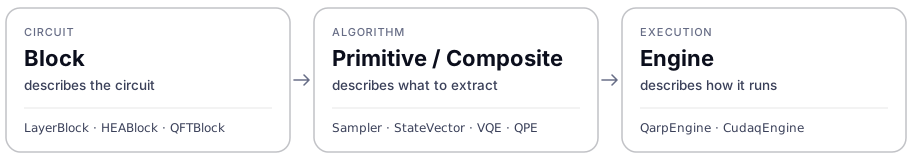
These are the three layers of OpenQARP. A block describes the circuit, a primitive describes what to extract from it, and an engine describes how it runs. VQE, QPE, circuit cutting and noisy simulation use the same three layers with different parts plugged in.
Next: the six tutorial_00 … tutorial_05 notebooks in examples/ take about an hour end to end, or jump straight to the OpenQARP Tutorial.
What’s in OpenQARP
Algorithms |
VQE, VQD, SSVQE, ADAPT-VQE / ADAPT-VQD, QAOA, QPE, DOS-QPE, PCE — ready to run, or assembled from primitives. |
Circuits |
Composable blocks: hardware-efficient and QAOA ansatzes, Trotterised evolution, and custom blocks of your own. |
Chemistry & physics |
Electronic structure from plain numpy integral tensors, with Jordan-Wigner, Bravyi-Kitaev and parity mappings. |
Simulation |
Exact state vectors, shot-based sampling, noisy simulation with configurable channels, mid-circuit measurement, and circuit cutting for problems too big for the qubits you have. |
Hardware |
Compile to a device’s gate set and qubit layout, with noise and routing models — and plot any of it with Matplotlib. |
Documentation
Full documentation is on GitHub Pages.
Resource |
Description |
|---|---|
Guided path: blocks, primitives, engines, VQE loops |
|
Design principles behind OpenQARP |
|
Build options, GPU, LAPACK, developer setup |
|
~50 runnable notebooks by API area, plus worked use cases |
Benchmarks
OpenQARP is benchmarked against qiskit, pennylane, pytket, qulacs and cirq on operator algebra, simulation, sampling, compilation and end-to-end algorithm runs. Tables are in benchmarks/tables/; every timing row carries a correctness check against an independent reference, and rows whose checks disagree are not published. The harness that regenerates them is benchmarks/README.md.
Citing
If OpenQARP is useful in your research, please cite the paper describing the framework (CITATION.cff carries the same entry in machine-readable form):
@misc{scali2026openqarpmodularframeworkquantum,
  title         = {OpenQARP: a modular framework for quantum application research},
  author        = {Stefano Scali and Vicente P. Soloviev and Antonio M{\'a}rquez Romero and
                   Brian Coyle and Giuseppe Buonaiuto and Annie Paine and Jonathan H. Fetherolf and
                   Marcos Diez Garc{\'i}a and Michal Krompiec and Josh Kirsopp},
  year          = {2026},
  eprint        = {2609.15697},
  archivePrefix = {arXiv},
  primaryClass  = {quant-ph},
  url           = {https://arxiv.org/abs/2609.15697},
}
To cite a specific software release, use the version DOI on Zenodo alongside the paper.
Contributing & support
Contributions are welcome — please read the Contributing Guidelines first and the Code of Conduct, which applies to every project space. For bugs, questions, or feature ideas, open an issue in the Issue Tracker.
OpenQARP is developed and maintained by the Fujitsu Research of Europe team, and released under the Apache License 2.0 — see LICENSE. The copyright notice is in NOTICE, which the Apache License requires you to carry forward if you redistribute OpenQARP or a derivative work; the licenses of the bundled third-party components are in LICENSES_bundled.txt.
1 maintainer

Release files for openqarp 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| openqarp-0.1.1.tar.gz | 4.4 MB | Details |
Built distributions (wheels)
Total release size: 58.3 MB
Release files / openqarp-0.1.1.tar.gz
| Download URL | openqarp-0.1.1.tar.gz |
|---|---|
| Size | 4.4 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7974b3187175e88292bc0f0d46725613c8a049165245bfc803148e0de72e281d
|
|
BLAKE2b-256 checksum How to use checksums |
2d1855e753417f7b96615ef8f753ec76cb707696e79445f605ba76e23ddf1a69
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp314-cp314-win_amd64.whl
| Download URL | openqarp-0.1.1-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 3.9 MB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
505c7d075635deb5935c90bac589280180206603d4327fea90406372be94aa25
|
|
BLAKE2b-256 checksum How to use checksums |
8e35a23b5468620b2a50017c6d4387159f6e9d4dd589dbe507369989e05c9694
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp314-cp314-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | openqarp-0.1.1-cp314-cp314-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 3.1 MB |
| Tags | CPython 3.14 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
8f964006906726bd02ed26c4de33f302ee924b8e996806b06b8cc6a1187c627c
|
|
BLAKE2b-256 checksum How to use checksums |
0f731e5e97bbcd07f1705c2a448cb32893f90aff625e9d6e10b3ce52ac51dd52
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp314-cp314-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | openqarp-0.1.1-cp314-cp314-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 2.9 MB |
| Tags | CPython 3.14 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
414af40bf14bc6b97630d888bb0d407f2f5e4ad885b9d30a657bfb11a6defeea
|
|
BLAKE2b-256 checksum How to use checksums |
5ea74d2d70ec1a7afe252c50110459422e2d2e61f82f8c3993ccf1746ae46c3b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp314-cp314-macosx_13_0_x86_64.whl
| Download URL | openqarp-0.1.1-cp314-cp314-macosx_13_0_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.14 macOS 13.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
024d06bb039dbad09d12d01d1cefd3f747ea2ab69cca07068445c4a9e1c7d37c
|
|
BLAKE2b-256 checksum How to use checksums |
a58f14ac76eea120a9c1b417f78e26b869230a247146dbf8af2f11b6da00f85f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp314-cp314-macosx_13_0_arm64.whl
| Download URL | openqarp-0.1.1-cp314-cp314-macosx_13_0_arm64.whl |
|---|---|
| Size | 1.8 MB |
| Tags | CPython 3.14 macOS 13.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
e0ad63068ec6a60847cdd55eb3b47a0cd2c870e6fa00e764395d7c3defa7f0c5
|
|
BLAKE2b-256 checksum How to use checksums |
35a119c140c26c2c670087db030fad56d51d905c45b4c8e6358a72fbeb0ace49
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp313-cp313-win_amd64.whl
| Download URL | openqarp-0.1.1-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 3.8 MB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
6c978a88423f3599433c2489288a396d09be162dc848b6ff3e3a8a82aa3be154
|
|
BLAKE2b-256 checksum How to use checksums |
2c1699d238b7c3a9a521632e61fa9be78c6e695c726cea8a069d3446ae2adf57
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | openqarp-0.1.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 3.1 MB |
| Tags | CPython 3.13 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
c6786fa00f84a3092962dfd440dd7eb3e44a0be312015c44637ce159e404bb02
|
|
BLAKE2b-256 checksum How to use checksums |
386d498a676e5c122d5fd54c8cf4aac28fd4ca90639399d95f3323ffa54b3bf1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp313-cp313-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | openqarp-0.1.1-cp313-cp313-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 2.9 MB |
| Tags | CPython 3.13 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
3f5b449ec927718a692f5da7f76abcaa00d82f4371b3a103ee5942cc35d8359b
|
|
BLAKE2b-256 checksum How to use checksums |
7251324106e62bad4027e8ddf73766e4b90bfbb3c124cc592dfc8cd74766ef5e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp313-cp313-macosx_13_0_x86_64.whl
| Download URL | openqarp-0.1.1-cp313-cp313-macosx_13_0_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.13 macOS 13.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
e4ec7cd2f4363d37b608bdd5af0975e4b33d94a4462e0fadfed84be44cfc1949
|
|
BLAKE2b-256 checksum How to use checksums |
fee175dbf3a8c20798009a600fac9144b25b942b997cd65fe7f930541b38ae20
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp313-cp313-macosx_13_0_arm64.whl
| Download URL | openqarp-0.1.1-cp313-cp313-macosx_13_0_arm64.whl |
|---|---|
| Size | 1.8 MB |
| Tags | CPython 3.13 macOS 13.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
dfe431bab6f3d6e473dd867c017ff657013e08c875ac3b8772739bc53ee9ac6b
|
|
BLAKE2b-256 checksum How to use checksums |
e9dcd61cf7b2c4aae251f49b74ea854005a0340392468345b5782803198ce7a5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp312-cp312-win_amd64.whl
| Download URL | openqarp-0.1.1-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 3.8 MB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
9da3b5b628ac2c899dd4e8fbb38f80a5cd0b886c1a1eccf0020097fedf89a5cf
|
|
BLAKE2b-256 checksum How to use checksums |
602fbb25a87faf4473689dccdce7f2b725558164b77ef0a8d5940db66e12e346
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | openqarp-0.1.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 3.1 MB |
| Tags | CPython 3.12 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
a1816d40c2bdfdb17c0835958e1bb632ce5a477a21be116fc3ac4feb4e5f99bf
|
|
BLAKE2b-256 checksum How to use checksums |
d0e3586bbc87b582df5c659dce6f9993d16e46fd70d2530ab3945c5f6752a809
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp312-cp312-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | openqarp-0.1.1-cp312-cp312-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 2.9 MB |
| Tags | CPython 3.12 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
28fe0a0234d17dcea3f43a5e894023ba1e0f0e349509c2ac595fbb29553946f8
|
|
BLAKE2b-256 checksum How to use checksums |
ce1e75b7fd460482cb879e575b46ee195b73c78b563b8ccec4f91dd02d38384b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp312-cp312-macosx_13_0_x86_64.whl
| Download URL | openqarp-0.1.1-cp312-cp312-macosx_13_0_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.12 macOS 13.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
51cfd9393efac5b2b9a9f05feb50a08ab2e2b8f8166188ce8430270cd323e7fa
|
|
BLAKE2b-256 checksum How to use checksums |
2d4e62fd2c4285003332d44c85aee1d9e33aafdd8c2a153093c9f8a8e448f496
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp312-cp312-macosx_13_0_arm64.whl
| Download URL | openqarp-0.1.1-cp312-cp312-macosx_13_0_arm64.whl |
|---|---|
| Size | 1.8 MB |
| Tags | CPython 3.12 macOS 13.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
30964feaa616fa3335ec22b13619c1cc99147924e5023a682c0051b4645e76b8
|
|
BLAKE2b-256 checksum How to use checksums |
fe45d8a2302ce58776f804a75c8bff95e580dbcef84533942535672eee61d3f0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp311-cp311-win_amd64.whl
| Download URL | openqarp-0.1.1-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 3.8 MB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
b11132e4fa026175a5d81e4983da962aa535f632527bebcdb7ef6705ffba33c1
|
|
BLAKE2b-256 checksum How to use checksums |
af9408938bc1a1fdb530b9715b993a4abd0133f0ab6152c14a5a63d3dfd3c902
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | openqarp-0.1.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 3.1 MB |
| Tags | CPython 3.11 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
5ba3c766626d73f034566a28c20f4bbfb7b5fcb51ae8d188af70e3e3e9e332fe
|
|
BLAKE2b-256 checksum How to use checksums |
632940fd8141dcd94f0ba34c4c227e3233ff045bc8a844df59f924c2988513be
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp311-cp311-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | openqarp-0.1.1-cp311-cp311-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 2.9 MB |
| Tags | CPython 3.11 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
7f9741d05f5d9c9d3e1f31dce2817818433886df1ce94260d2350d0acf7fe155
|
|
BLAKE2b-256 checksum How to use checksums |
34fa26ba090f5a0d1cbf9f72822ab474ca12ca81ffae5aaa98daff6b1f3d5e6a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp311-cp311-macosx_13_0_x86_64.whl
| Download URL | openqarp-0.1.1-cp311-cp311-macosx_13_0_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.11 macOS 13.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
704f0ff5a46e43b55d4489080d3287b5c068c384c1dcafe432e371dda6782983
|
|
BLAKE2b-256 checksum How to use checksums |
7aa13d649bab1cba457b3bd07136d31b8cff59a5fb4972ce747ba65da300d02e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency logRelease files / openqarp-0.1.1-cp311-cp311-macosx_13_0_arm64.whl
| Download URL | openqarp-0.1.1-cp311-cp311-macosx_13_0_arm64.whl |
|---|---|
| Size | 1.8 MB |
| Tags | CPython 3.11 macOS 13.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b84ba877df628bf83b9f3591b69d0dc8e99089d76760c620913ac0fbc1c9eef7
|
|
BLAKE2b-256 checksum How to use checksums |
d14f3730b6892efde8c23e0d3f1f0403e0459b9169b8cb44bcbcfab66f03528f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 25, 2026.
Transparency log













