
Overstory

Overstory is the browser workspace for Arbora. The repository is overstory;
the package remains overstory. Existing gallery images retain their original capture provenance.
The browser workspace for governed agents, workflows, and knowledge in Arbora.
Conversations · approvals · workflows · fleet activity · Understory knowledge views









Documentation · Capabilities · Interfaces · Status

The conversation-first workspace uses synthetic demo data, not a live account. Open Settings for theme, surface and privacy choices. See the workspace gallery and screenshot refresh guide.
Overview
Overstory is the browser workspace composed by Arbora. It brings agent conversations, approvals, workflows, fleet activity, and Medulla exploration into one React application. Its FastAPI host keeps privileged credentials and gateway delegation on the server side.
| Overstory owns | Other components own |
|---|---|
| Browser presentation, local interaction state, accessible route composition, and the FastAPI boundary | Arbora owns public routing, identity, policy, and fleet supervision; Meristem applies supplied plans; Medulla owns durable knowledge; connector services own external-system effects |
Current package Version: 3.0.0.
Key capabilities
- Stream agent responses with sources, governed tool activity, and approval prompts.
- Build and run workflows while observing sessions, goals, schedules, and fleet health.
- Explore property graphs, RDF, schemas, objects, tables, documents, code, and memories through Understory and Medulla.
- Discover MCP Apps and connector capabilities without exposing service credentials to the browser.
- Apply one role-aware navigation and server authorization model across the complete workspace.
- Run as the Arbora-hosted browser co-service or as an independently deployed ASGI application.
Documentation
Start with the Overstory documentation, then use the shared platform map to move between components:
| Component | Role | Documentation |
|---|---|---|
| Overstory | Browser operator workspace and Understory knowledge views | Docs |
| Tuig | Terminal and headless client; central A2A/REST and experimental headless local ACP; full session parity remains unqualified | Docs |
| Axil | Desktop cockpit for chat, graph, fleet, health, and operator workflows | Docs |
| Arbora messaging | Chat and voice entrypoints hosted by Arbora | Docs |
| Arbora | Public MCP, REST, A2A, identity, policy, and runtime composition | Docs |
| Meristem | In-run harness that applies supplied plans | Docs |
| Medulla | Durable multimodal data, reasoning, provenance, and transactions | Docs |
| Scion SDK | Typed source adapters, connector serving, and write-back contracts | Docs |
Architecture
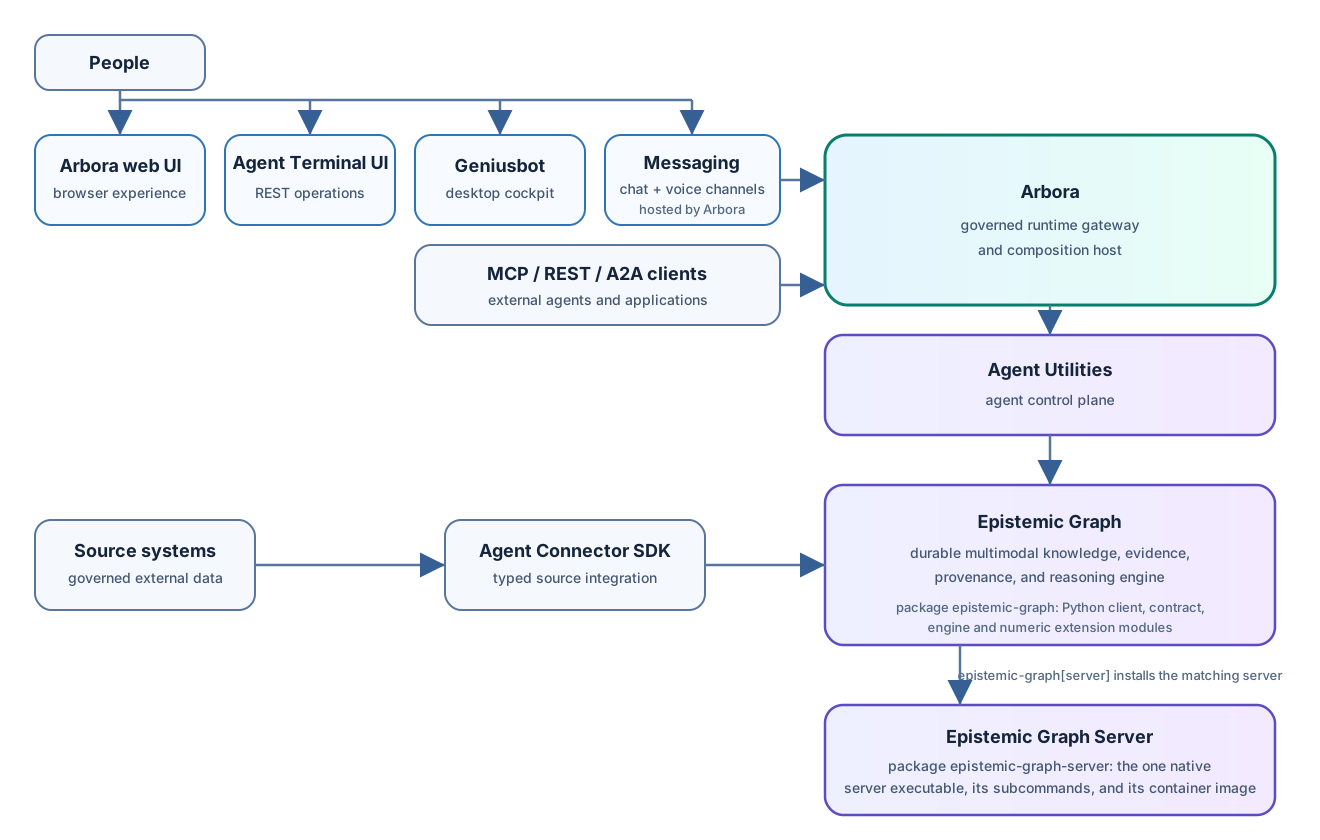
People also enter through Tuig and Axil or Arbora-hosted messaging. Tuig retains central A2A/REST and experimental headless local ACP; full session parity remains unqualified. External applications connect over MCP, REST, or A2A. The browser talks only to its same-origin FastAPI host. Arbora injects gateway routes and verified request context. Meristem applies supplied plans; Medulla owns durable knowledge. Source systems connect through Scion SDK directly to Medulla. Overstory renders typed results and local presentation state while each service retains its own authority.
See the architecture guide for the request flow and trust boundaries.
Quick start
Generate a local profile and start Arbora with Overstory enabled:
uvx --from "arbora[webui]" setup-config generate --profile tiny
export ENABLE_WEB_UI=true
uvx --from "arbora[webui]" arbora --transport streamable-http --host 127.0.0.1 --port 8000
Open http://127.0.0.1:8080. Arbora serves MCP on port 8000 and the Agent
Web UI co-service on port 8080. The start guide
covers local source development and deployment profiles.
Contributing
Issues and pull requests are welcome. Read AGENTS.md, keep browser and server authority boundaries intact, and run the repository validation suite before opening a pull request.
Refresh the documented workspace views with pnpm screenshots:refresh. See the
screenshot guide for synthetic fixtures, hosted capture,
provenance and review before committing refreshed images.
License
Overstory is available under the MIT License.
1 maintainer

Metadata
1 maintainer
Release files for overstory 3.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| overstory-3.0.0.tar.gz | 2.9 MB | Without provenance | Details for overstory-3.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| overstory-3.0.0-py3-none-any.whl | Python 3 | none | any | Details for overstory-3.0.0-py3-none-any.whl |
Total release size: 6.0 MB
Release files / overstory-3.0.0.tar.gz
| Download URL | overstory-3.0.0.tar.gz |
|---|---|
| Size | 2.9 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
44901bdbd72fc7d7ca644384a3bd117d6b4916e0d6a9217b01116045e837a996
|
|
BLAKE2b-256 checksum How to use checksums |
d35ef1b15372c1dd4ef785177735166ebebcab13232d25eb5e3af500c1799084
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.14.4
|
Release files / overstory-3.0.0-py3-none-any.whl
| Download URL | overstory-3.0.0-py3-none-any.whl |
|---|---|
| Size | 3.0 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
6822907bf36ce342faad0179d84227507f46b3b1372353b99ae8905a7a504aa6
|
|
BLAKE2b-256 checksum How to use checksums |
4856134f10200d80a8b2a48d0ed8451ab9da5ed98c536c1796d957ab45d3a29e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.14.4
|
Security for overstory 3.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














