

A python tool to investigate vertical signal properties of imaging-based spatial transcriptomics data.
introduction
Much of spatial biology uses microscopic tissue slices to study the spatial distribution of cells and molecules. In the process, tissue slices are often interpreted as 2D representations of 3D biological structures - which can introduce artefacts and inconsistencies in the data whenever structures overlap in the thin vertical dimension of the slice:

Ovrl.py is a quality-control tool for spatial transcriptomics data that can help analysts find sources of vertical signal inconsistency in their data. It is works with imaging-based spatial transcriptomics data, such as 10x genomics' Xenium or vizgen's MERSCOPE platforms. The main feature of the tool is the production of 'signal integrity maps' that can help analysts identify sources of signal inconsistency in their data. Users can also use the built-in 3D visualisation tool to explore regions of signal inconsistency in their data on a molecular level.
installation
ovrlpy can be installed from PyPI or
bioconda
# install from PyPI
pip install ovrlpy

# or install from bioconda
conda install bioconda::ovrlpy
quickstart
The simplest use case of ovrlpy is the creation of a signal integrity map from a spatial transcriptomics dataset. In a first step, we define a number of parameters for the analysis:
import pandas as pd
import ovrlpy

# define ovrlpy analysis parameters
n_components = 20 # number pf PCA components

# load the data
coordinate_df = pd.read_csv('path/to/coordinate_file.csv')
coordinate_df.head()
the coordinate dataframe should contain a gene, x, y, and z column.
you can then fit an ovrlpy model to the data and create a signal integrity map:
# fit the ovrlpy model to the data
dataset = ovrlpy.Ovrlp(
    coordinate_df,
    n_components=n_components,
    n_workers=4,  # number of threads to use for processing
)

dataset.analyse()
after fitting we can visualize the data ...
fig = ovrlpy.plot_pseudocells(dataset)

... and the signal integrity map
fig = ovrlpy.plot_signal_integrity(dataset, signal_threshold=4)

Ovrlpy can also identify individual overlap events in the data:
doublets = dataset.detect_doublets(min_signal=4, integrity_sigma=1)
And plot a multi-view visualization of the overlaps in the tissue:
# Which doublet do you want to visualize?
doublet_to_show = 0

x, y = doublets["x", "y"].row(doublet_to_show)

fig = ovrlpy.plot_region_of_interest(dataset, x, y, window_size=50)

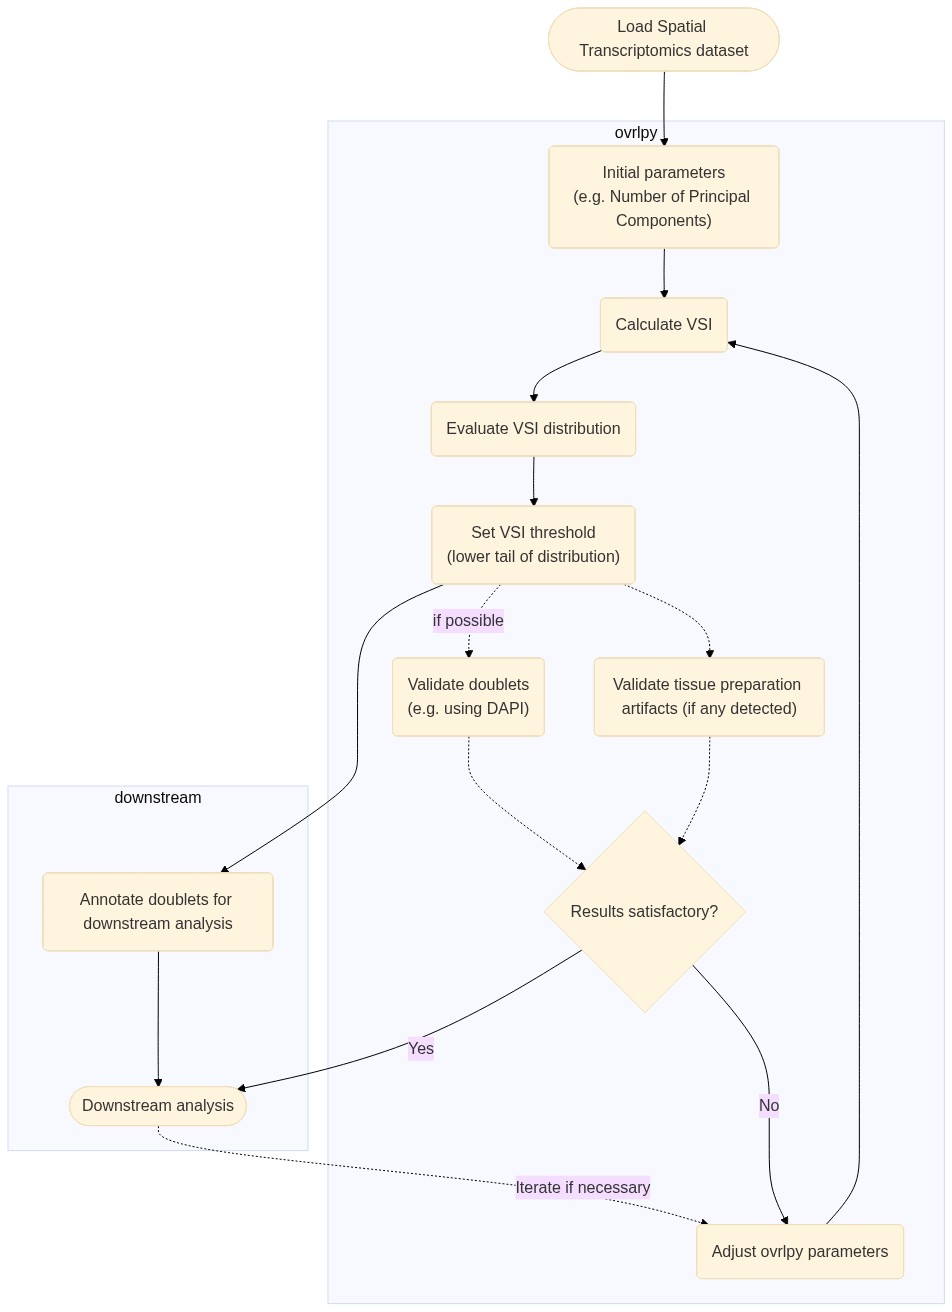
parameter selection
1 maintainer

Release files for ovrlpy 1.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| ovrlpy-1.2.0.tar.gz | 8.7 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| ovrlpy-1.2.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 8.8 MB
Release files / ovrlpy-1.2.0.tar.gz
| Download URL | ovrlpy-1.2.0.tar.gz |
|---|---|
| Size | 8.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
0c1ba08b9b981b8fcb714592cfc94f565a35505474ffe487b5f5524d289571f2
|
|
BLAKE2b-256 checksum How to use checksums |
58acdef5079117e57d00974fef9d945ed7c393bdaa77e0fef24617cc0f6da573
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on May 19, 2026.
Transparency logRelease files / ovrlpy-1.2.0-py3-none-any.whl
| Download URL | ovrlpy-1.2.0-py3-none-any.whl |
|---|---|
| Size | 28.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
0194fa420c466dd7f6d1517e54745bda3d740fc89b6018fe5cfdc2e461b13bbe
|
|
BLAKE2b-256 checksum How to use checksums |
302a1b64fb895cdf11316b9a821744d9d869ad128fbe63393e6fc2eb4450e0f4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on May 19, 2026.
Transparency log













