


p4lantir is a simple tool to perform Man-in-the-Middle over TCP using ARP spoofing, allowing to intercept, drop, forward and see TCP flows.
This project is intended to be relatively simple, making simple future contributions for new features/bug fix.
[!CAUTION] This ethical hacking project is intended for educational purposes and awareness training sessions only. I decline all responsability about the usage of this project.
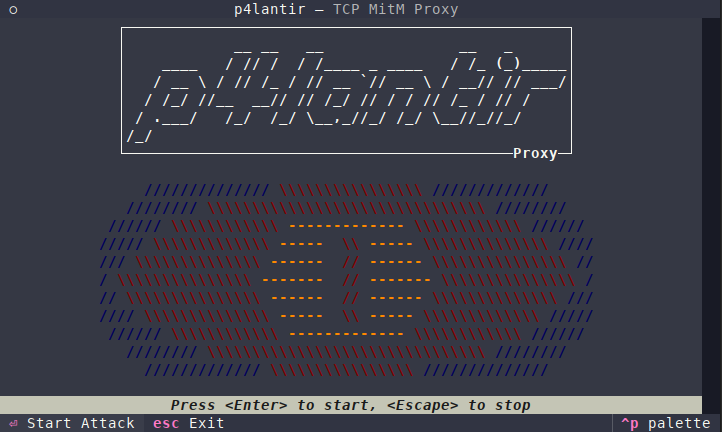
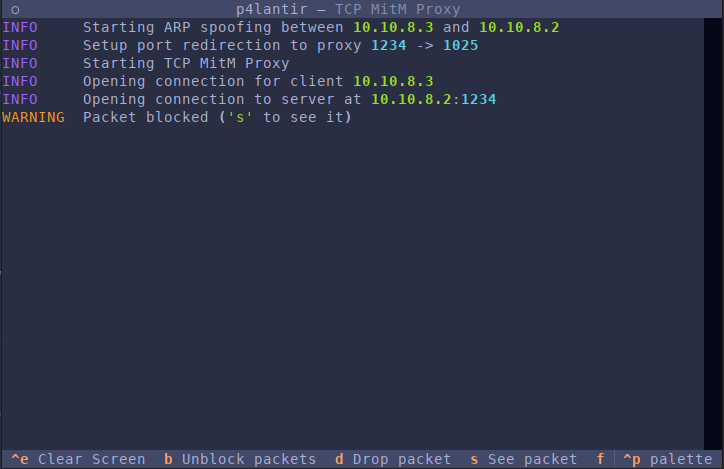
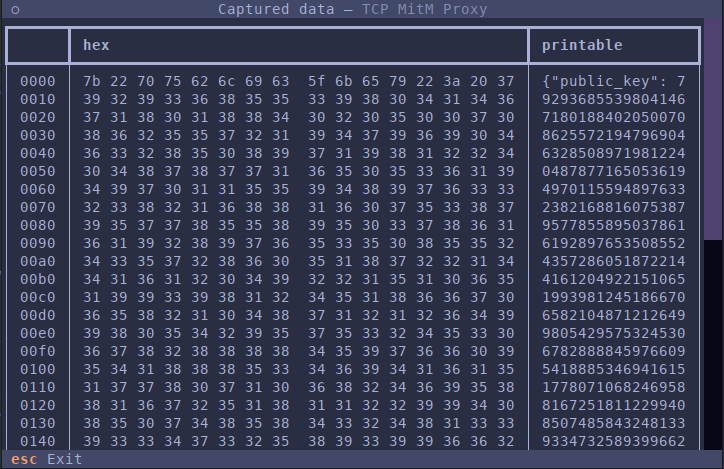
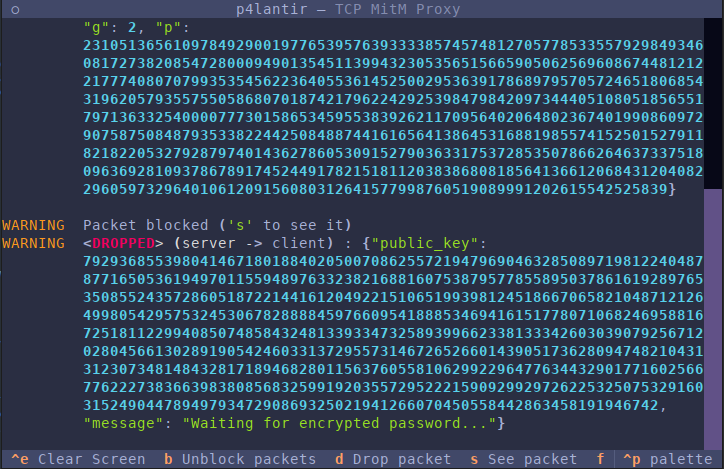
Screenshots
Installation
- Install the system dependencies (arpspoof, iptables)
- Create python virtual environnement
- Install the package
Setup instructions :
Debian-based systems
sudo apt install dsniff iptables

python3 -m venv venv
source venv/bin/activate

pip install p4lantir
Archlinux
pacman -S dsniff iptables

python3 -m venv venv
source venv/bin/activate

pip install p4lantir
Note : the package can also be downloaded from the release and installed using the
.whlfile andpip.
Usage
[!WARNING] You need to run the script as root due to arpspoof and iptables. You should open a shell as root, activate the venv and then use p4lantir.
usage: p4lantir [-h] --host-1 HOST_1 --host-2 HOST_2 [--gateway GATEWAY] -i INTERFACE -l LPORT [--pport PPORT] [--debug]

Man-in-the-Middle over TCP terminal app.

options:
  -h, --help            show this help message and exit
  --host-1 HOST_1       First host to spoof, must be the host instanciating the connection
  --host-2 HOST_2       Second host to spoof
  --gateway GATEWAY     Gateway IP
  -i, --interface INTERFACE
                        Interface to perform arp spoofing
  -l, --lport LPORT     Port to listen for MITM attack
  --pport PPORT         Internal port used for proxy.
  --debug               Enable debug mode.
Examples
Client/server in the same localhost
Let say that a client at IP C connect to a remote server at IP R, both in the same LAN. You need to know the name of the interface that connects you this LAN (let call this iface. Then your command should look like :
p4lantir --host-1 [replace with C] \
         --host-2 [replace with R] \
         -i [replace with iface] \
         -lport [server's listening port]
About the listening port, if you intend to intercept SMTP you may choose
25,80for HTTP, and so on ...
Client/server on a different LAN
If the client is in the same LAN as you and the server is not in your LAN, then you have to add another parameter : the gateway IP. p4lantir will then spoof the gateway IP and open a connection to the server.
p4lantir --host-1 [replace with C] \
         --host-2 [replace with R] \
         --gateway [replace with gw's IP]
         -i [replace with iface] \
         -lport [server's listening port]
Documentation
The source-code documentation is available here
Contributing
All contributions are welcome !
Please see CONTRIBUTING.md for more details.
License
This project is under the GPL-v3 license, please see LICENSE.TXT
1 maintainer

Metadata
1 maintainer
Release files for p4lantir 1.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| p4lantir-1.0.2.tar.gz | 337.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| p4lantir-1.0.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 364.6 kB
Release files / p4lantir-1.0.2.tar.gz
| Download URL | p4lantir-1.0.2.tar.gz |
|---|---|
| Size | 337.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
453326e910a977daf80b0eadb8b18f9534c3c5f2e90f41ddd23b977066a1ff31
|
|
BLAKE2b-256 checksum How to use checksums |
7d79500149476dc7ac80d1907dca1ed6e8e09fc647effe6b392c24259211ffe6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 26, 2025.
Transparency logRelease files / p4lantir-1.0.2-py3-none-any.whl
| Download URL | p4lantir-1.0.2-py3-none-any.whl |
|---|---|
| Size | 26.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
91dc07eac206321b2ea3b71a2f743d6dadcb55c7f96f3f5051dad947a7303ffd
|
|
BLAKE2b-256 checksum How to use checksums |
33e921ebfb0ea26c685ca465e59a1fc135de4301b89b3b75f4d65543d94f6028
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 26, 2025.
Transparency log













