
petit
petit is a command-line log analyzer for systems administrators. It takes out of a log everything that repeats (the routine logins, the cron runs, the health checks) and counts it, so what's left to read is short and the unusual lines stand out. It works out the format on its own (syslog, journalctl, Apache, Snort, application logs with stack traces, JSON, mail), draws activity graphs in the terminal, and does the same from Python. It has been doing this since 2009.
Capabilities
-
Hashing.
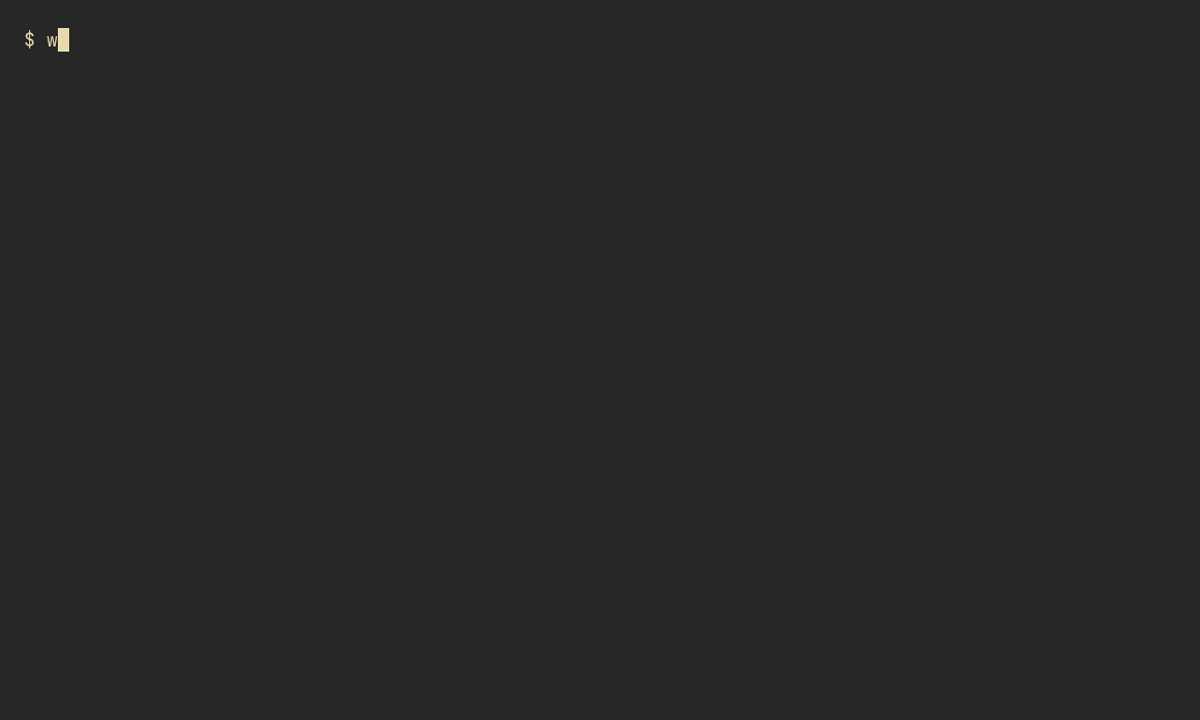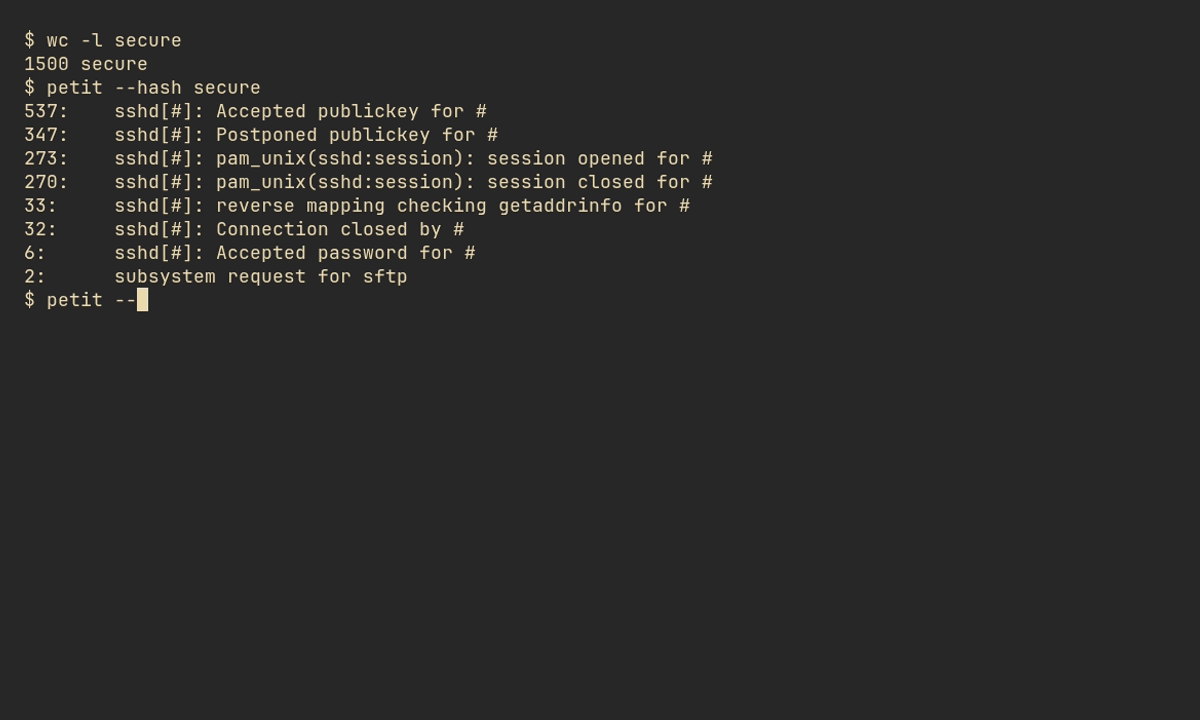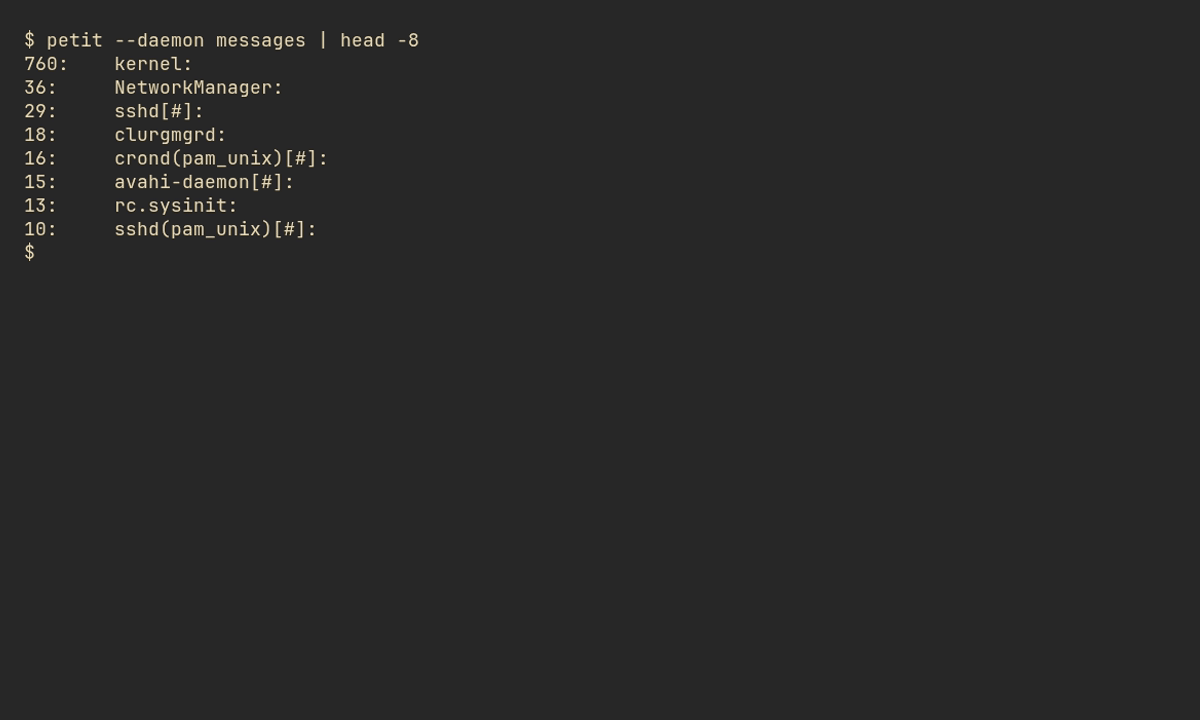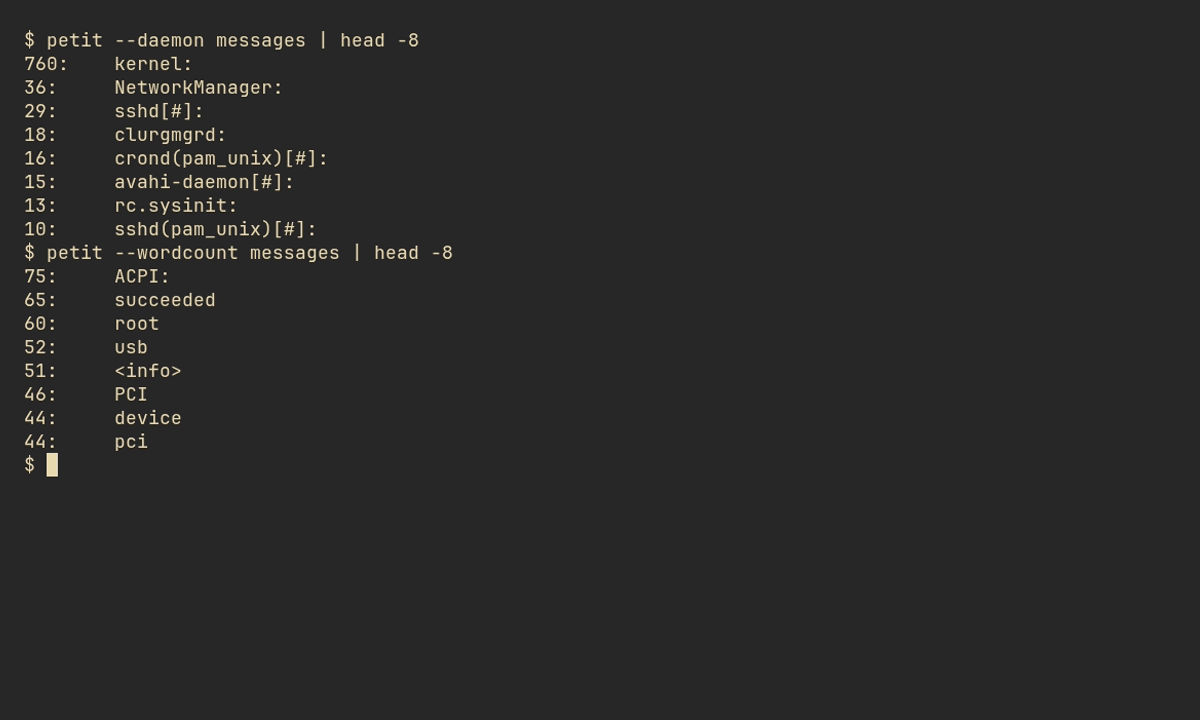
petit --hashgroups lines by what's left after numbers, IPs and timestamps are taken out, and prints each pattern once with its count. A 1500-line sshd log becomes eight lines.--fingerprintgoes further and collapses whole reboots into one line. Hashing -
Reports.
--daemon,--hostand--wordcountcount a log by program, by machine, or by word, which shows its shape before you read a single line. Reports -
Graphs.
--graphdraws the whole log over time in the terminal, choosing a column size that fits;--hgraph,--mgraph,--span 90mand friends pick a fixed window. Graphs -
Format detection. petit frames the input into records (JSON objects, mail messages, multi-line messages with their stack traces, or lines) and votes on a driver to read them. It streams: memory follows the number of distinct patterns, not the size of the log. Reading logs
-
Python library.
hash_lines(),analyze_text()and friends return the same groups as data, with no files, stdout or exits involved. Library
Quick Start
# Fedora, RHEL and rebuilds (Debian, Ubuntu and SUSE are in docs/install.md)
sudo curl -fsSLo /etc/yum.repos.d/crunchtools.repo \
    https://crunchtools.github.io/packages/rpm/crunchtools.repo
sudo dnf install petit

# Anywhere with Python 3.11+
uv tool install petit-log-crunchtools

# Or in a container
podman run --rm -v $(pwd):/data:ro,Z quay.io/crunchtools/petit --hash /data/some.log
Then:
petit --hash --fingerprint /var/log/messages    # what happened, minus reboots
petit --daemon /var/log/messages                 # who's talking
petit --graph /var/log/httpd/error_log           # when
grep error /var/log/messages | petit --mgraph    # when, for just the errors
History
petit started as lt, a Perl script inspired by Marcus Ranum's
artificial ignorance,
and became petit in August 2009. Since then:
- 2009: first shown at the Akron Linux Users Group; hosted in Subversion at eyemg
- 2010: packaged in Fedora and EPEL, then Debian; moved to crunchtools.com and presented at PyOhio
- 2010–2015: hosted on Google Code as
petit-log, in Mercurial - 2011–2019: shipped in every Ubuntu release from 11.04 to 19.10
- 2015: moved to GitHub by the Google Code exporter
- 2018–2020: dropped from Fedora, Debian and Ubuntu along with Python 2
- 2022: ported to Python 3
- 2026: moved to the crunchtools org, relicensed AGPL, back in native packages
The full timeline, with sources, is in History.
Further reading: Introduction: Petit Log Analysis Tool for Systems Administrators (video, 2009), Centralized Logging System, Analysis, and Troubleshooting (2010), Snort Alert Log: Simple Analysis and Daily Reporting with Arnold and Petit (2010), Log Analysis with Python, PyOhio 2010, Petit for Log Analysis by Jason Antman (2012), Petiti – An Open Source Log Analysis Tool for Linux SysAdmins by Aaron Kili at Tecmint (2017).
Documentation
| Page | What it covers |
|---|---|
| Install | Native packages for Fedora, RHEL, SUSE, Debian and Ubuntu; PyPI; container |
| Hashing | --hash, samples, filters, --fingerprint, --identifiers |
| Reports | --daemon, --host, --wordcount |
| Graphs | Every graph, its units, window and width |
| Reading logs | Framers, drivers, big inputs, multi-line messages, JSON |
| Library | The Python API and what SemVer covers |
| Philosophy | Why petit removes certainty and leaves uncertainty |
| History | Where petit has lived since 2009, and what's been written about it |
| Writing and tuning drivers | For contributors: framers, entry and hash drivers, stopwords, reboot corpora |
Development
uv sync --all-extras          # dev tools: pytest, ruff, mypy
uv run pytest                 # tests
uv run ruff check src test    # lint
uv run mypy src               # types
podman build -t petit .       # container
Packages, the container image and PyPI releases are built by GitHub Actions on every GitHub release. The README demo is rendered from docs/demo/petit.tape.
License
AGPL-3.0-or-later. See COPYING.
1 maintainer

Metadata
1 maintainer
Release files for petit-log-crunchtools 4.10.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| petit_log_crunchtools-4.10.1.tar.gz | 908.2 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| petit_log_crunchtools-4.10.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.3 MB
Release files / petit_log_crunchtools-4.10.1.tar.gz
| Download URL | petit_log_crunchtools-4.10.1.tar.gz |
|---|---|
| Size | 908.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
35e10e537a83f51ff53fb3e3c669ffd0d515437136020a32acca0770fb9de524
|
|
BLAKE2b-256 checksum How to use checksums |
e4657b965d145f00b9cf08473511b2c19769b76971073b466f5c964fc3f0cd09
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 27, 2026.
Transparency logRelease files / petit_log_crunchtools-4.10.1-py3-none-any.whl
| Download URL | petit_log_crunchtools-4.10.1-py3-none-any.whl |
|---|---|
| Size | 360.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
809c6c0830389ec26a018b0f0177ee009d201e60ada72118a3c7aad8b2ffb55f
|
|
BLAKE2b-256 checksum How to use checksums |
6145943ceacdae1033d82213e6d17666c14f519bfea2bc3bf61933640c293479
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 27, 2026.
Transparency log













