
piighost
English | Français



piighost replaces personal data with placeholders before the LLM sees it, then restores the real values in the reply and in tool calls. This Python library de-identifies confidential data, meaning personal data (PII) and secrets, through a reversible pseudonymization often called anonymization. LangChain, Pydantic AI, LlamaIndex and Claude Code integrations are provided, together with an OpenAI and Anthropic API connector.
This de-identification spots confidential data with pluggable detectors (regex, NER, LLM) and replaces each value with a placeholder, the token that takes its place. For example:
John Doebecomes<<PERSON:1>>john.doe@example.combecomes<<EMAIL:1>>
This placeholder stays the same from one message to the next with the conversational pipeline, which keeps the mapping between a value and its placeholder across the whole conversation. If john.doe@example.com reappears three messages later, the placeholder is still <<EMAIL:1>>, which lets the LLM follow the thread.
The LLM therefore only receives de-identified text. When it returns placeholders, for example by answering Hello <<PERSON:1>>, piighost replaces them with the real values. The user sees John Doe and never sees the de-identification.
The same mechanism protects agents that call tools. With the LangChain middleware, a tool that needs the real email address receives it in clear, while the LLM that supplies it only writes <<EMAIL:1>>.
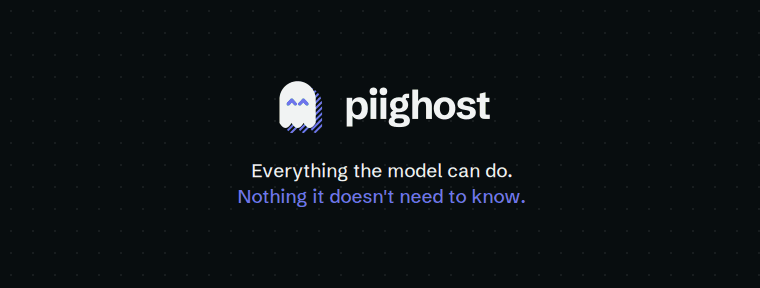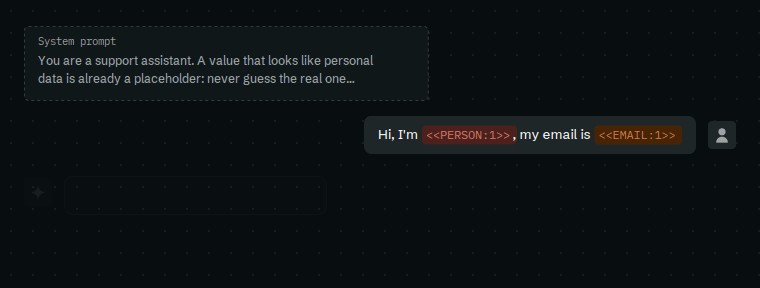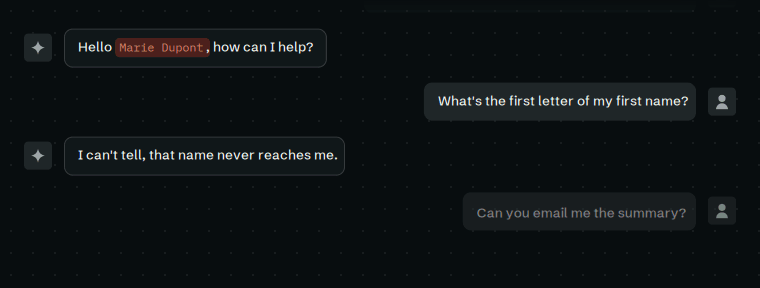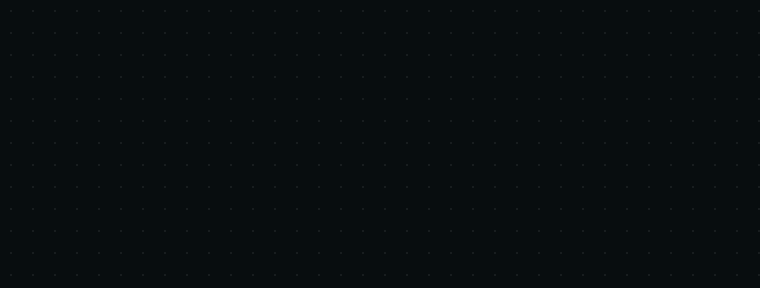
The LLM only sees placeholders. The tool receives the real address, the user gets a clear-text reply, and your agent code stays the same.
Quickstart
pip install piighost # or: uv add piighost
ExactMatchDetector de-identifies a dictionary of known values, with no model to download.
import asyncio

from piighost.components.detector import ExactMatchDetector
from piighost.pipeline import AnonymizationPipeline

detector = ExactMatchDetector({"John Doe": "PERSON", "john.doe@example.com": "EMAIL"})
pipeline = AnonymizationPipeline(detector)

result = asyncio.run(pipeline.anonymize("Write to John Doe at john.doe@example.com."))
print(result.text)  # Write to <<PERSON:1>> at <<EMAIL:1>>.
The Quickstart goes on with a real detector and a conversation.
Go further
- Start: installation, first pipeline, conversational pipeline
- Configure: a pipeline in a TOML file, pattern groups from the catalog, every config key
- Integrate: LangChain, Pydantic AI, LlamaIndex, Claude Code, a remote piighost-api
- Deploy: an API server from a catalog configuration, a production thread pipeline, several instances
- Understand: why de-identify, architecture, security, GDPR compliance, limitations, detection, measured, how it compares
- Upgrade: versions and the move to 2.0
Ecosystem
- piighost.dev: the project website, with the ecosystem and its philosophy
- piighost catalog: reviewed regex groups and ready-made pipeline configurations, pulled by reference
- piighost-api: a server hosting one pipeline behind HTTP, with OpenAI- and Anthropic-compatible proxies
- piighost-chat: an example chat interface with human-in-the-loop
- caviardage: a browser app that redacts a Word deed, with piighost running in Pyodide. Nothing of the document leaves the tab
Project
- Community: Discord to get help, report bugs and request features
- Contributing: contribution guide and bug reports
- License: MIT
If piighost is useful to you, a star on GitHub helps other developers find it.
1 maintainer

Metadata
1 maintainer
Release files for piighost 2.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| piighost-2.1.1.tar.gz | 134.5 kB | Without provenance | Details for piighost-2.1.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| piighost-2.1.1-py3-none-any.whl | Python 3 | none | any | Details for piighost-2.1.1-py3-none-any.whl |
Total release size: 317.2 kB
Release files / piighost-2.1.1.tar.gz
| Download URL | piighost-2.1.1.tar.gz |
|---|---|
| Size | 134.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fd3bff84aeccb36825fe149de698189213353805ba968b18205d7ea72c75fc45
|
|
BLAKE2b-256 checksum How to use checksums |
820b949c2c375490c808beda52cbe63508ff486c200e15f4754810ad3c813d9a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.13.1 {"installer":{"name":"uv","version":"0.13.1","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Release files / piighost-2.1.1-py3-none-any.whl
| Download URL | piighost-2.1.1-py3-none-any.whl |
|---|---|
| Size | 182.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c55f1cabc3526c2a7220e4c8ad15524c319495345a89a51ec0b0c80581068789
|
|
BLAKE2b-256 checksum How to use checksums |
938234b00b24ab4b4f678d2c4c0504ff1c87c0219adda937eb25ec0f4e51fd91
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.13.1 {"installer":{"name":"uv","version":"0.13.1","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Security for piighost 2.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














