
pipedrag
Drag files found on the command line into any app that accepts drops:
find ~/Downloads -name '*.pdf' | pipedrag
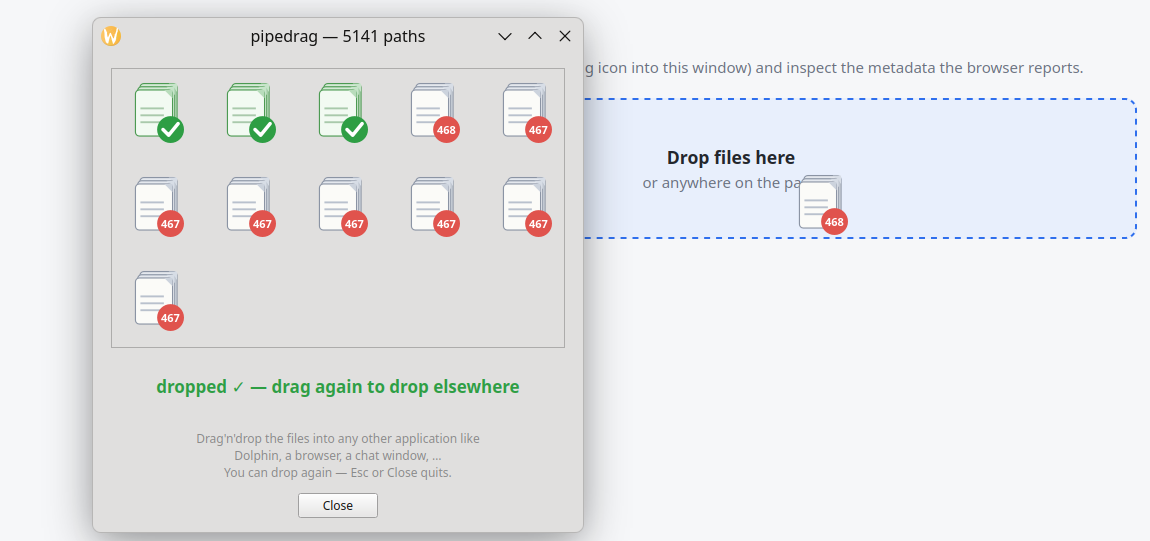
pipedrag reads file paths from stdin (newline- or NUL-separated), opens a
small window with a multi-file icon, and lets you drag it into Dolphin, a
browser, a chat window … as if you had selected the files in a file manager.
Drops can be chunked (pipedrag -n 1000), most browser uploads have some sort of limit.
Chunks already dropped are marked as "green".
$> find . -name '*.jpeg' -type f | pipedrag -n 1000
How to install a release version
Install as python image
If you have a working python/pip setup the easiest way is to install it with pip:
pip install pipedrag
Debian / Ubuntu
Debian packages can be downloaded from https://git.jtheuer.de/pipedrag/releases. Install the package as usual with:
sudo dpkg -i <filename.deb>
Development and contribution
Clone the repository and setup virtualenv locally. You can use the provided script:
make setup
Requires Python ≥ 3.10. If python3 -m venv fails on Debian/Ubuntu, install
python3-venv first.
How the drop works
- The drag speaks XDND — the same protocol Dolphin uses — via
text/uri-list. - The dragged files are registered with the FileTransfer portal, so
sandboxed targets (snap/Flatpak apps) can read them even from directories
their sandbox blocks directly — e.g. snap Firefox silently denies dot-directories
like
~/.local/share/. This is the same mechanism KDE/Dolphin uses.
Testing drag'n'drop
upload-test.html is a browser page that prints everything the browser
exposes about dropped files (metadata, mime types, filesystem handle) and
their SHA-256/SHA-384/SHA-512 checksums.
AI transparency
This project was largely coded with claude using the deepseek api. I couldn't have built a QT app so quickly and the drag'n'drop part with the portals was a lot more messy than expected.
1 maintainer

Metadata
1 maintainer
Release files for pipedrag 0.1.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| pipedrag-0.1.4.tar.gz | 23.3 kB | Without provenance | Details for pipedrag-0.1.4.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| pipedrag-0.1.4-py3-none-any.whl | Python 3 | none | any | Details for pipedrag-0.1.4-py3-none-any.whl |
Total release size: 45.8 kB
Release files / pipedrag-0.1.4.tar.gz
| Download URL | pipedrag-0.1.4.tar.gz |
|---|---|
| Size | 23.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f5e707b40c2b9a4d9045a15e3f14fcb20c49474e7b72c4b0f67db421e0e83cec
|
|
BLAKE2b-256 checksum How to use checksums |
e4b57df05491894e342a92f315fd3801fb3efdda8731765607ac767bf6f96164
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.14.4
|
Release files / pipedrag-0.1.4-py3-none-any.whl
| Download URL | pipedrag-0.1.4-py3-none-any.whl |
|---|---|
| Size | 22.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7c54637740dddddf5ab3250c2222050dbb46764f78b1d85a63e016b1d865860b
|
|
BLAKE2b-256 checksum How to use checksums |
65e64e18a0741fd8710f684242a9d6d0cec7361ed8e2c9ed02efd216337e984b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.14.4
|
Security for pipedrag 0.1.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














