
pipetree

Metadata-driven pipeline orchestration: describe what to move in declarative YAML, and a small package turns it into a runnable dependency tree.
YAML → config loader → typed model → graph builder → executor
Documentation: https://pipetree.dev. The package is the companion to the Pipeline Engineering blog series.
What it does
- One YAML block per table: a source or a SQL/PySpark file, a business key and a merge
strategy.
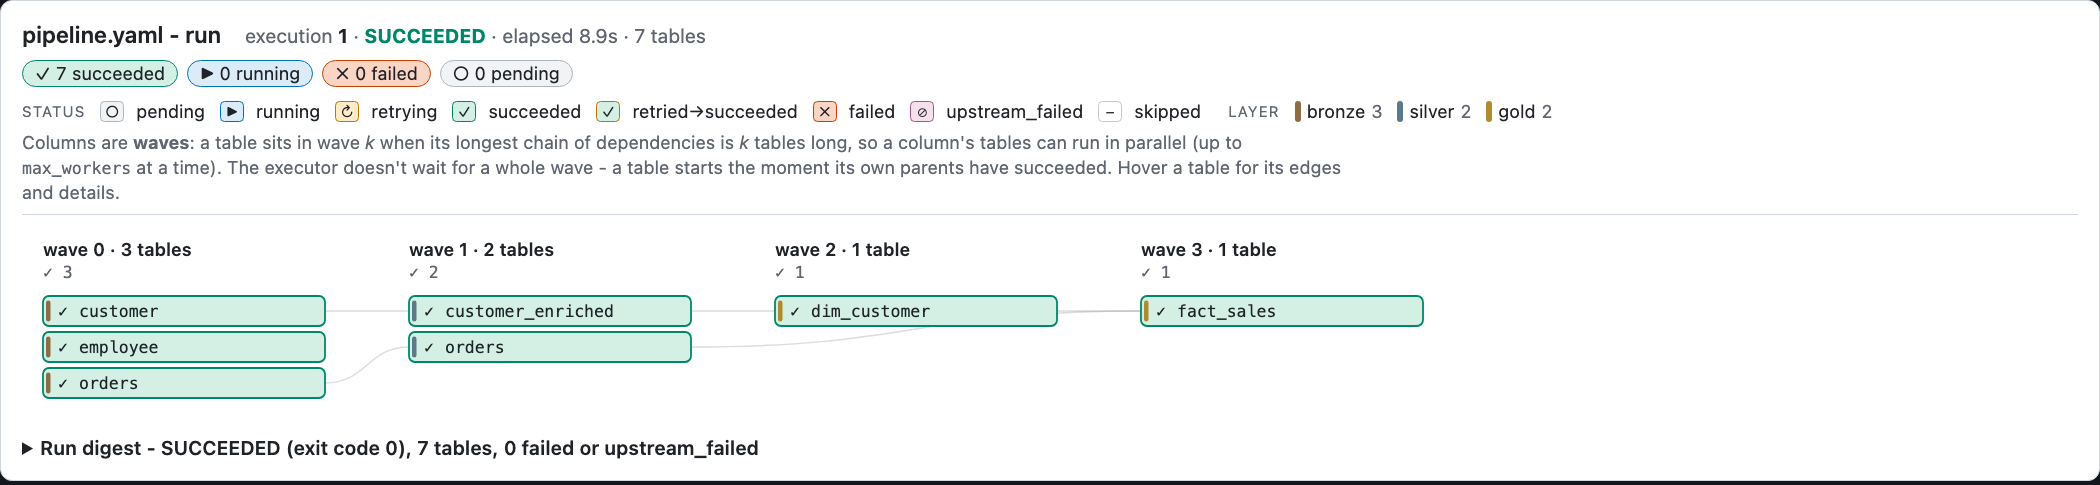
depends_on: autoreads the parents from the code. - A dependency tree that runs: a table starts the moment its parents have succeeded. Transient
errors are retried, a failed table marks its dependents
upstream_failedand the rest finishes. - Merge strategies on Delta:
replace,append,scd1andscd2, withsequence_byordering across batches, soft or hard deletes, snapshot merges for sources that deliver a full extract, unknown members and surrogate keys. - Notes for what a merge quietly changed: dropped duplicates, NULL keys, schema drift, deleted keys. In the log, the digest, the graph and the run log.
- A live picture of the run in a notebook or as an HTML file.
- Tags and partial runs:
--select,--with-dependents,--with-ancestors,--tag. - Databricks and Fabric: the same config runs on local Spark, Databricks and Fabric; secrets from Azure Key Vault without a secret, a failure email through Azure Communication Services, and a translation of scd tables to Databricks' AUTO CDC.
Installation
pip install pipetree-meta            # core: config loader, graph, executor, CLI
pip install "pipetree-meta[spark]"   # + PySpark and Delta Lake for local runs
pip install "pipetree-meta[azure]"   # + Key Vault secrets, token auth, failure email
Python 3.11 or newer. The import package and the command are pipetree. Local Spark needs a JDK
(for example brew install openjdk@17). On Databricks and Fabric install without [spark], the
runtime brings its own Spark and Delta.
Quick start
# pipeline.yaml
systems:
  crm:
    type: csv
    path: data/customer.csv
bronze:
  tables:
    customer:
      source: { system: crm, object: account }
      business_key: [accountid]
      strategy: scd1
mkdir -p data && printf 'accountid,name\n1,Contoso\n2,Fabrikam\n' > data/customer.csv   # a tiny source file
pipetree validate --config pipeline.yaml   # check the config, nothing runs
pipetree graph --config pipeline.yaml      # print the dependency tree
pipetree run --config pipeline.yaml        # run it and print a digest
The quickstart runs a seven-table example from
a clone of the repository. examples/quickstart.ipynb
is the same run as a notebook with its outputs, and
examples/with_problems/
shows what pipetree reports when the data misbehaves.
Documentation
- Install and Quickstart
- Concepts: YAML structure, the dependency tree, running, tags, notes and the run log, seeing the run
- Merge strategies: replace, append, scd1, scd2, snapshot merge, merge options
- Guides: Databricks, Fabric, notifications, AUTO CDC, custom sources
- Reference: every YAML key and every CLI option
- Architecture: the parts of the package
examples/databricks/ (a Databricks Asset Bundle) and examples/fabric/ (a notebook) run the
example pipeline against a real workspace.
Development
uv sync --all-extras --dev
uv run pytest              # full suite
uv run pytest -m "not spark"  # skip the JVM-backed integration tests
uv run ruff check . && uv run ruff format --check .
uv run pyright
See CONTRIBUTING.md.
License
MIT, see LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for pipetree-meta 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| pipetree_meta-0.1.0.tar.gz | 108.9 kB | With provenance | Details for pipetree_meta-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| pipetree_meta-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for pipetree_meta-0.1.0-py3-none-any.whl |
Total release size: 240.5 kB
Release files / pipetree_meta-0.1.0.tar.gz
| Download URL | pipetree_meta-0.1.0.tar.gz |
|---|---|
| Size | 108.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7b864982a99fc3149219fc2d097240fe7599d8f1d42eb71def8b5977d2d26cc7
|
|
BLAKE2b-256 checksum How to use checksums |
654c29d5951949054b100a9e52246a9d3860795f0a5dad75602555f64c4f0381
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / pipetree_meta-0.1.0-py3-none-any.whl
| Download URL | pipetree_meta-0.1.0-py3-none-any.whl |
|---|---|
| Size | 131.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
330f1fdd4e65414cd70c7c265d530ce616dda30e959dd0d6e41906003f1212d0
|
|
BLAKE2b-256 checksum How to use checksums |
d64703331811ad9246425ea6639362c39d0086678a8ee8926e70f52f3ac7b4a8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logSecurity for pipetree-meta 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for pipetree_meta-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














