
PriorityX


Prioritize entities and detect escalation using GLMM statistical models. Analyze event data in Python, then explore saved results in AutoViz. Example applications include IT incidents, software bugs and compliance monitoring.
Installation · AutoViz guide · Python quickstart · API reference
AutoViz
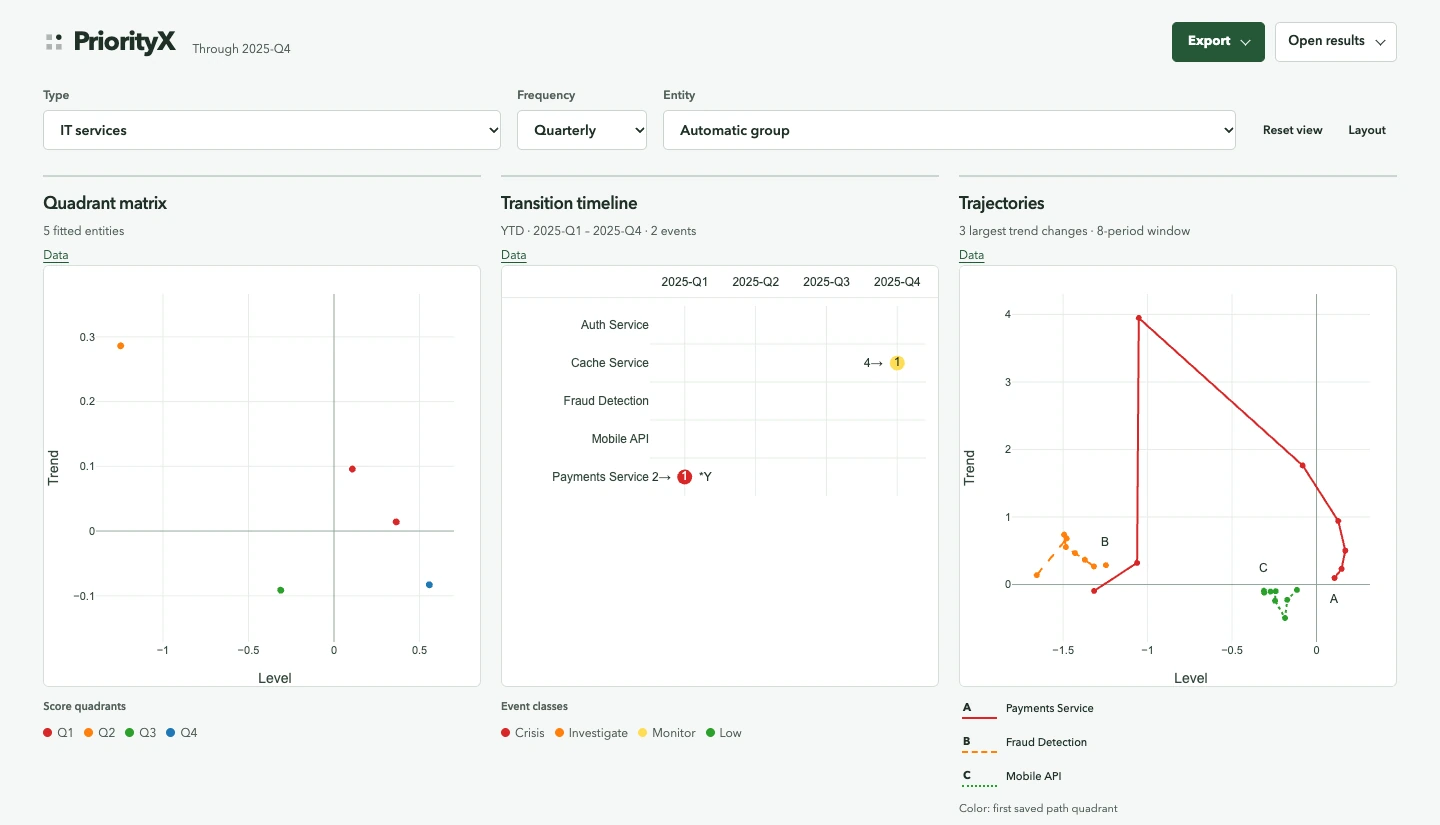
Explore a linked quadrant matrix → YTD transition timeline → trajectories in your browser. Select an entity across charts, inspect exact values, adjust chart space and save an interactive HTML view that reopens offline.
Try the IT incidents example
Save the example bundle
as incidents-quarterly.json, then run:
python -m priorityx app --bundle incidents-quarterly.json
This sample uses existing saved results from PriorityX's IT incidents example: five services with quarterly history from 2023 to 2025. It opens on Quarterly, with a 2025 YTD timeline and three automatically selected trajectories. Opening results and changing layouts do not fit models.
See the example walkthrough for what to inspect and
the sample's provenance. To open your own results, run python -m priorityx app
and choose Open results. The saved-result guide
lists the identity, period and score columns required for CSV import.
Python API
Fit a priority matrix from your event data and save a chart:
import pandas as pd
import priorityx as px

events = pd.read_csv("events.csv", parse_dates=["opened_at"])
matrix = px.fit_priority_matrix(
    events,
    entity_col="service",
    timestamp_col="opened_at",
    temporal_granularity="quarterly",
)
px.plot_priority_matrix(matrix, entity_name="Service", plot_path="matrix.png")
PriorityX also provides cumulative movement tracking, transition detection, driver analysis, custom score axes and weighted composite indices. The Python quickstart covers the analysis workflow; the API reference documents parameters and outputs.
Documentation
| Guide | What it covers |
|---|---|
| Installation | Python requirements, macOS/Linux and Windows setup, upgrades |
| AutoViz example | Open and explore the saved IT incidents sample |
| AutoViz workspace | Linked charts, selection, layout, settings and exports |
| Saved results | Data sources, identity/date columns, CSV mapping and validation |
| Python quickstart | Fit, track movement and detect transitions |
| Methodology | Statistical models and score interpretation |
| Priority classification | Quadrants and transition classes |
| Examples | IT incidents, software bugs and compliance workflows |
1 maintainer

Metadata
1 maintainer
Release files for priorityx 0.7.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| priorityx-0.7.1.tar.gz | 738.6 kB | With provenance | Details for priorityx-0.7.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| priorityx-0.7.1-py3-none-any.whl | Python 3 | none | any | Details for priorityx-0.7.1-py3-none-any.whl |
Total release size: 1.2 MB
Release files / priorityx-0.7.1.tar.gz
| Download URL | priorityx-0.7.1.tar.gz |
|---|---|
| Size | 738.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e2a723f5976bc9c87e5abcbc47871f740ed49912f67d529ee95d82773b46581c
|
|
BLAKE2b-256 checksum How to use checksums |
688007ea52c72fea760e74e72505baa50950287c334e2cbef5eaadd9f1165533
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / priorityx-0.7.1-py3-none-any.whl
| Download URL | priorityx-0.7.1-py3-none-any.whl |
|---|---|
| Size | 509.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1a698f3ac63266812aae8257353c979a01b0f27f1e0fa456ac130b6f1fdbaafe
|
|
BLAKE2b-256 checksum How to use checksums |
9cb93320dce9f486d1c4b15aff5397f453170b29ae03d49d67a82494ce91bfbf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logSecurity for priorityx 0.7.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for priorityx-0.7.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














