
pycommremover



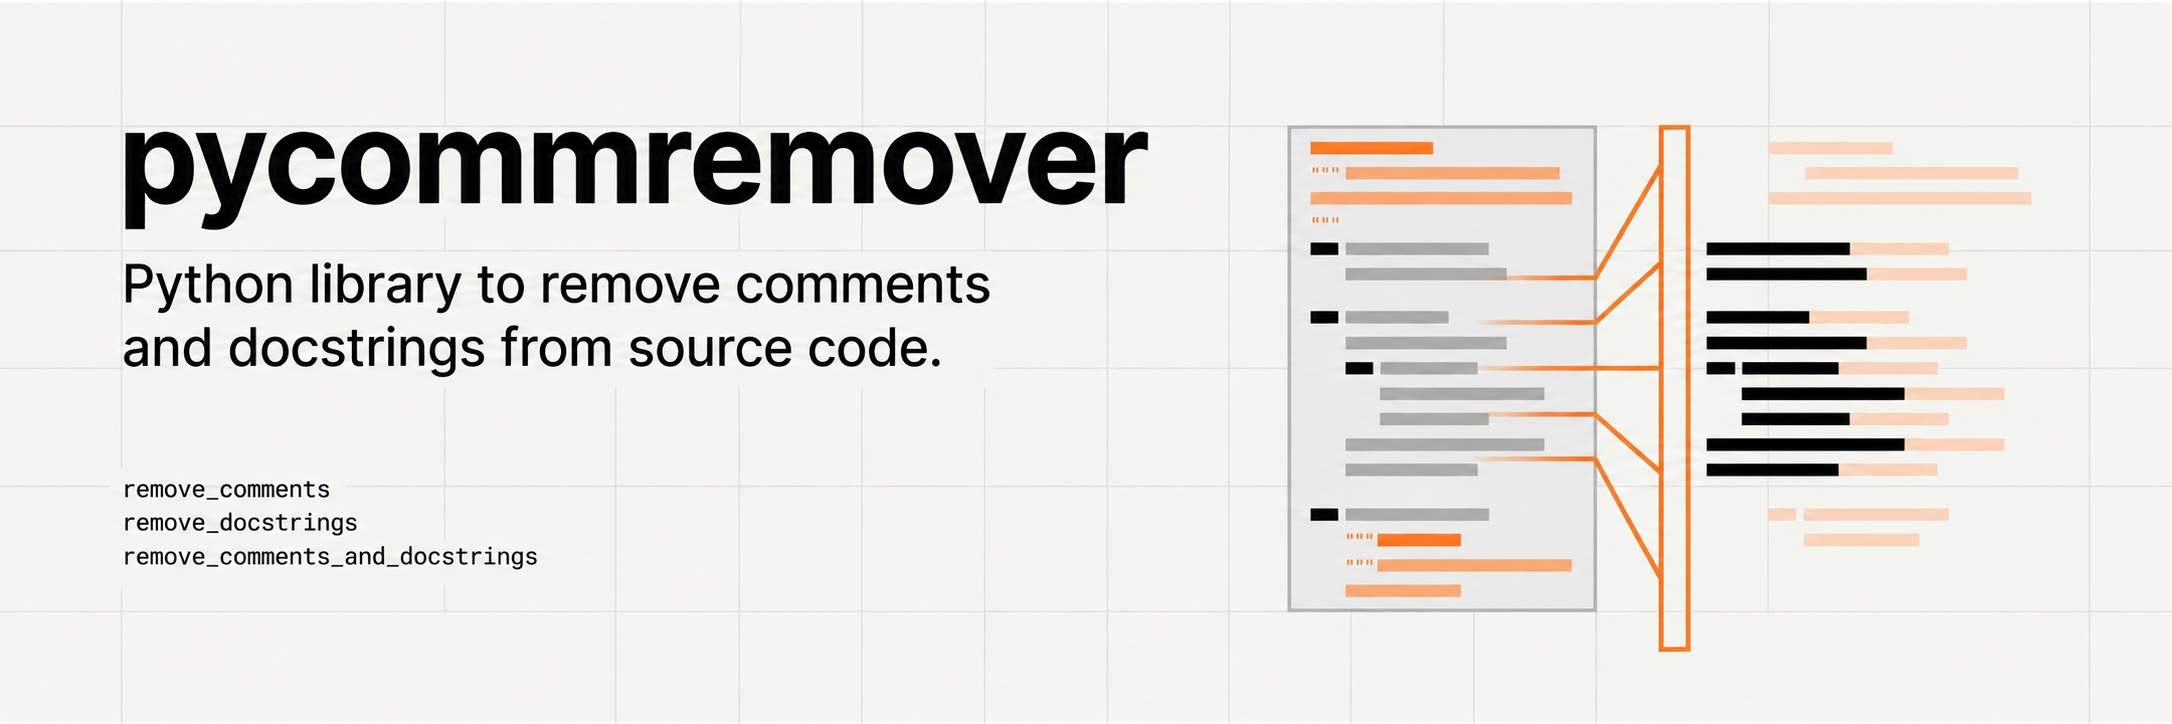
It analyses the code with the standard-library tokenize and ast modules,
so a # inside a string is never mistaken for a comment and real string
values (assignments, call arguments, f-strings) are never touched. Line
numbers of the remaining code are preserved.
Why three functions?
At the language level these are different things, so they are removed separately:
| Construct | Example | Runtime effect | Removed by |
|---|---|---|---|
| Line comment | x = 1 # note |
none (discarded by the tokenizer) | remove_comments |
| Block comment | a lone """note""" statement |
none (a discarded no-op) | remove_comments |
| Docstring | first string of a module/class/function | kept as __doc__, seen by help()/doctest |
remove_docstrings |
remove_comments is behaviour-preserving (it only deletes no-ops and
keeps docstrings). remove_docstrings changes __doc__, so it is opt-in.
remove_comments_and_docstrings does both in one pass.
When removing a string that is a block's only statement (e.g. def f(): """doc"""), a pass is inserted so the result stays valid Python.
Installation
Install with uv:
uv add pycommremover
Usage
import pycommremover

src = '''
def greet(name):
    """Return a greeting."""          # docstring: kept by remove_comments
    msg = f"Hi, {name}"  # build it   # line comment: removed
    """a block comment"""             # block comment: removed
    return msg
'''

# Line + block comments gone, docstring kept:
print(pycommremover.remove_comments(src))

# Only the docstring gone:
print(pycommremover.remove_docstrings(src))

# Everything gone:
print(pycommremover.remove_comments_and_docstrings(src))
The input must be syntactically valid Python.
Development
The dev dependency group (installed automatically by uv run) provides pytest:
uv run pytest
1 maintainer

Metadata
1 maintainer
Release files for pycommremover 0.4.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| pycommremover-0.4.1.tar.gz | 7.1 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| pycommremover-0.4.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 13.0 kB
Release files / pycommremover-0.4.1.tar.gz
| Download URL | pycommremover-0.4.1.tar.gz |
|---|---|
| Size | 7.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f30f49289d955a582e61a1fd3f2b6051b12dc8d07bb2510d17ffb147f4245dde
|
|
BLAKE2b-256 checksum How to use checksums |
1c26e649ffdefb5ebec7fdb7a4c4e82531250aa5414a52492d3513a082e229a2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 4, 2026.
Transparency logRelease files / pycommremover-0.4.1-py3-none-any.whl
| Download URL | pycommremover-0.4.1-py3-none-any.whl |
|---|---|
| Size | 5.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
29333a52ec33ebb8ca524c1ec4d2d9d66459461bedb2b2b99dd82ad64445f8bc
|
|
BLAKE2b-256 checksum How to use checksums |
e163051cdf40cfcf6cc4599b652382ef8e30d4e932079d8aa095fba439d8610c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 4, 2026.
Transparency logSecurity for pycommremover 0.4.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for pycommremover-0.4.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 4, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














