
pydeno
Run AI-generated JavaScript from Python, without trusting it.
Real V8 · supervised worker process · OS-level sandbox · your Python functions as the only way out



Quickstart · How it is secure · How it was tested · Performance · Docs · Security policy
Agents increasingly answer questions by writing code: a data transform, a chart spec, a slide
deck, a loop that calls your tools. That code is untrusted by construction. pydeno lets a Python
program run it and get the result back, behind a boundary that holds even if the code is hostile.
from pydeno import IsolatedRuntime, RuntimeConfig

with IsolatedRuntime(RuntimeConfig(timeout=2.0), sandbox="require") as rt:
    rt.bind_function("lookup", lambda sku: {"A1": 3.5}[sku])   # the only thing the guest can call
    print(rt.eval("lookup('A1') * 2"))                          # 7.0
    rt.eval("new Array(2 ** 32 - 1).fill(0)")                   # WorkerCrashed. Your process is fine.
Why pydeno
| 🧱 Contained | A V8 abort, a hang or a memory blow-up kills a disposable worker process, never yours. |
| 🔒 No ambient authority | No filesystem, network, processes, environment, Deno, process or require. Whatever the guest can do beyond computing, you bound on purpose. |
| 🧰 Real JavaScript | The engine behind Chrome and Node (deno_core + V8), so model-written code behaves like JavaScript and real libraries run. |
| ⚡ Fast | A native Rust wire codec and a pre-started spare worker: as little as ~15 ms to create a runtime and evaluate, a 2 MB result in ~18 ms. |
| 🧪 Tested like an attacker would | Assume-breach syscall sweeps against the real kernel, a verified seccomp filter, fuzzing and hostile-worker fakes, on 12 Linux distros and two CPU architectures. |
| 🔌 Tool-calling built in | bind_function and ToolBridge give the model's code your Python tools, with call budgets and errors it can branch on. |
Quickstart
pip install pydeno # or: uv pip install pydeno (Python 3.10+, macOS or Linux)
Tools the guest can call, with a total budget:
from pydeno import IsolatedRuntime, ToolBridge

bridge = ToolBridge({"get_weather": get_weather, "send_email": send_email}, max_calls=50)

with IsolatedRuntime(sandbox="require") as rt:
    bridge.attach(rt)
    rt.eval("tools.get_weather('Zurich')")
The call that exceeds max_calls never reaches your Python function; the guest gets a catchable
ToolBudgetError. A Python exception inside a tool reaches JavaScript as a real Error whose name
is the exception's class, so the model's code can branch on it. Use redact_host_errors=True if
exception text must not reach the guest.
Make the easy path the safe one (the module-level helpers then use a sandboxed worker):
import pydeno

pydeno.configure_default_runtime(isolated=True, sandbox="require")
pydeno.eval("1 + 1")
Run real libraries. Many assume browser basics a bare isolate lacks. Opt in to a small,
pure-JavaScript set (virtual-time timers, TextEncoder, btoa, Blob, EventTarget,
AbortController, structuredClone) that never defines window or document:
from pydeno import IsolatedRuntime, RuntimeConfig, WEB_POLYFILLS

rt = IsolatedRuntime(RuntimeConfig(bootstrap=WEB_POLYFILLS))
Showcase: Python and JavaScript, both sandboxed
A model that writes code wants the best language for each half of the job: Python for wrangling data, JavaScript for what only the JS ecosystem does well. Pair pydeno with Monty (Pydantic's Python sandbox) and run both without trusting either, sharing one set of host tools and one call budget:
with Monty() as pool, pool.checkout() as py:                      # the model's Python, in Monty
    analysis = py.feed_run(model_python, external_lookup={"fetch_sales": fetch_sales})

with IsolatedRuntime(RuntimeConfig(bootstrap=WEB_POLYFILLS), sandbox="require") as js:
    js.bind_function("getAnalysis", lambda: analysis)             # hand the result across
    js.bind_function("fetch_sales", fetch_sales)                  # the same tool, same budget
    svg = await js.eval_async(model_javascript)                   # the model's JS, in pydeno
1. Python half, in Monty
  [python] best region: East (1750)
  [python] refused: PermissionError: Permission denied: '/etc/passwd'
2. JavaScript half, in pydeno
  [js]     refused: Evaluation failed: ReferenceError: fetch is not defined
  [js]     sandbox: seatbelt
3. wrote sales.svg (11021 bytes); tool calls used: 2 of 5
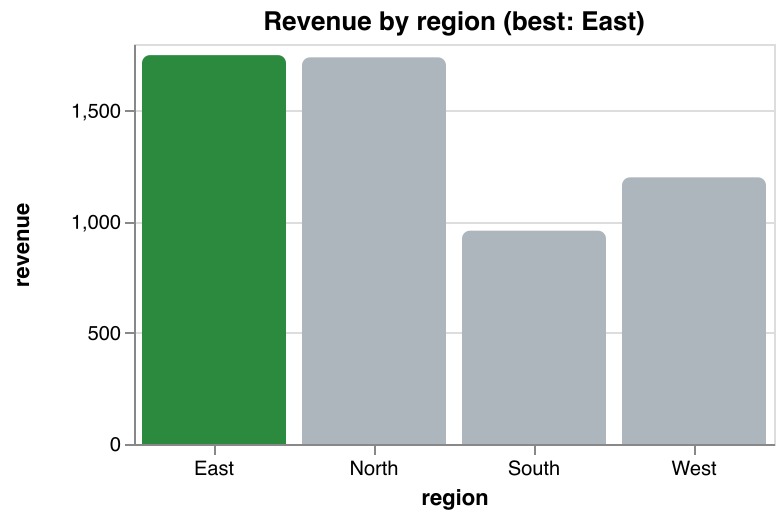
Python crunched the numbers; JavaScript drew the chart with Vega-Lite;
each sandbox refused its own attempt to reach outside, and both drew on the same five-call tool
budget. Full runnable example: examples/monty_and_pydeno.py.
How it works
flowchart LR
    app["Your Python app"] -- "eval, tools" --> parent["IsolatedRuntime<br/>(supervisor)"]
    parent <-->|"validated frames only"| worker
    subgraph worker["Worker process: sandboxed before V8 starts"]
        v8["V8 (jitless)<br/>guest JavaScript"]
    end
    v8 -. "bound functions only" .-> parent
    parent --> tools["Your tools"]
The worker is a separate process with an empty environment, its own session, no privileges, and an OS sandbox applied before the JavaScript engine exists. The parent enforces the deadline, memory and call budgets from outside and treats everything the worker sends as untrusted input.
How it is secure
Defence in depth: each layer assumes the one above it has failed. The threat model is in
SECURITY.md and the details in the isolation guide.
| Layer | What it does |
|---|---|
| Separate process | Empty environment, own session. A V8 abort, hang or out-of-memory kills the worker; the parent raises WorkerCrashed or RuntimeTimeout. |
| OS sandbox, before the engine exists | macOS: Seatbelt. Linux: Landlock, a private empty root (mount, network, IPC and UTS namespaces) and a seccomp-bpf filter that denies new processes, network, mounts, kernel interfaces, filesystem changes and signals to other processes. Syscalls newer than the reviewed range answer ENOSYS. sandbox="require" refuses to start unless every layer applied. |
| No privileges | A worker started as root drops to nobody with an empty capability set; no_new_privs is set. |
| Smaller engine surface | V8 runs --jitless (no JIT, no WebAssembly). SharedArrayBuffer, Atomics, WeakRef and FinalizationRegistry are removed: they are what timers and garbage-collection probes are built from. |
| Limits enforced from outside | Wall-clock deadline (default 60 s), CPU cap, memory ceiling (default 1 GiB), host-call budgets, an in-flight call cap and a write-stall limit. A guest that keeps calling your functions cannot hold the deadline open indefinitely. |
| The worker is untrusted | Every frame it sends goes through a strict native decoder with size, depth, node and hash-collision budgets. No pickle, no eval. A worker that sends nonsense is killed. |
| Capability tokens | A bound function is reachable only through an unguessable token, installed after the binding exists. |
| Determinism on request | clock= freezes Date/Intl; random_seed= seeds Math.random. |
What it does not promise. A V8 bug is contained to the worker, not prevented, and about 200
syscalls the engine needs stay reachable. For multi-tenant use, run one runtime per trust unit and
put the whole thing in a locked-down container or microVM (see the
deployment guidance). Libraries that need WebAssembly, a DOM or a canvas do not work.
The engine is only as current as the deno_core release it is built on; a weekly check tells
maintainers when a newer V8 becomes available.
Which runtime?
IsolatedRuntime |
Runtime (in-process) |
|
|---|---|---|
| Use it for | Anything a model or a user supplied | Code you wrote or reviewed |
| A hostile builtin can abort or hang your process | No: it kills the worker | Yes (new Array(2 ** 32 - 1).fill(0)) |
timeout= always enforced |
Yes (hard kill from outside) | Not for every builtin (e.g. sparse-array sort) |
| OS sandbox | Yes | No |
| Start-up | ~15-45 ms with the spare worker, ~70-105 ms without | microseconds |
| A host tool call | Crosses a process boundary (~70 µs per call) | ~12-17 µs (BENCHMARKS.md) |
How it was tested
The sandbox is tested the way an attacker would try it: from inside, and against the real kernel.
- Assume-breach syscall sweeps. A sandboxed process fires every syscall in the kernel's table with garbage arguments, from a fresh process each time, and records what is still reachable. Dangerous calls are fired for real (inside a container, never on a host).
- The seccomp program is verified, not trusted. A BPF interpreter in the tests runs the filter's
decision logic on any platform, and every syscall number in it is checked against the Linux
kernel's own tables (regenerated from a pinned kernel tag by
scripts/gen_syscall_tables.py). - A capability checklist. What untrusted code tries first (read or write a file, reach the
network, spawn a process, read the environment; Deno, Node and browser globals; the runtime's own
plumbing), through both
evalandeval_async, plus a check that nothing reached the host. - Hostile peers. Fake workers that stop reading, send malformed or oversized frames, flood hash tables or lie about types; fuzzing with Hypothesis; and a port of pydantic/monty's security suite (the cases an in-process runtime cannot survive are pinned as strict expected failures).
- Two codecs, tested against each other. The wire codec is native (Rust) with a readable Python reference; hundreds of tests, including generated frames, require identical results and errors.
- Real libraries, inside the sandbox. pptxgenjs, three.js (GLB export), Vega-Lite and dagre give
the same results as an unsandboxed runtime, with their bytes pinned in
vendor/libs/; about 25 more (d3, ECharts, jsPDF, Tailwind v4, Prettier, ...) were checked by hand. - Many kernels. The Linux suite runs on 12 distro images (Debian, Ubuntu, Fedora, AlmaLinux,
Amazon Linux; Python 3.10 to 3.14) on both x86_64 and aarch64, and under simulated kernels that
lack Landlock, seccomp or both, to prove the sandbox degrades honestly and
sandbox="require"fails closed. See.github/workflows/test.yml. - Zero skips. Platform-specific tests are deselected, never skipped; CI enforces a skip budget of zero so an unrun test cannot hide.
Performance
Measured on macOS arm64 (Apple M2) with a release build, on a machine that was not idle, so
ranges are shown. Reproduce with benches_py/isolated_report.py and the Criterion and
pytest-benchmark suites (BENCHMARKS.md, which also shows 0.5.0 is no slower
than 0.4.5).
Create an IsolatedRuntime and evaluate |
~15 ms with the spare worker used soon after it starts, ~30-45 ms after it has sat idle, ~70-105 ms without |
| Move a 2 MB structured result across the boundary | ~18 ms each way (native codec) |
import pydeno |
~19 ms (the isolation stack loads on first use) |
| Release extension size | 43 MB, nearly all of it V8 and its built-in Intl data |
In-process Runtime: a complete host tool call |
~12-17 µs; a bare eval ~6-10 µs |
Jitless V8 (the default for IsolatedRuntime) makes compute-heavy code roughly 1.5 to 2 times
slower than with the JIT; jitless=False trades that back for a larger attack surface.
Integrations
- FastMCP tool bridge: expose FastMCP tools to sandboxed JS via
bind_functionand an in-processfastmcp.Client - pydantic-ai "code mode" agent: the model submits one JS batch script instead of many separate tool calls, run safely with a timeout
- ToolBridge: several Python tools with a total call budget, typed errors the model's JS can branch on, and
console.logrouted back to Python - Monty + pydeno: the model's Python runs in Monty, its JavaScript in pydeno, both sandboxed, sharing one tool and one call budget; Python computes, a Vega-Lite chart is drawn in JS
- Vendored npm libraries: run real npm document-generation libraries (
pptxgenjs,pdf-lib) from their browser bundles inside the sandbox; see the guide - Arrow IPC dataframes: move 100k+ row tables into the sandbox as Arrow IPC
bytesinstead of JSON objects (5 ms vs 253 ms); see the guide
Documentation
- Security policy and threat model · the isolation guide
- Quick Start · Concepts · Guides · Use cases · API reference
- Agent skill: an Agent Skills
SKILL.mdthat teaches coding agents (Claude Code and others) to use pydeno correctly. Copyskills/pydeno/into your agent's skills directory, e.g..claude/skills/ - Benchmarks · Changelog
Status and contributing
pydeno is experimental: expect breaking changes between versions. Found a way out of the
sandbox? Please report it privately, as described in SECURITY.md. Everything else:
issues and pull requests are welcome; start with
docs/contributing/.
Licensed under the MIT License.
1 maintainer

Metadata
1 maintainer
Release files for pydeno 0.5.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| pydeno-0.5.0.tar.gz | 1.4 MB | Details |
Built distributions (wheels)
Total release size: 435.3 MB
Release files / pydeno-0.5.0.tar.gz
| Download URL | pydeno-0.5.0.tar.gz |
|---|---|
| Size | 1.4 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
20465c3f8762749d5cd26d670c8545274837d20d13bfe078f688b674ed1b0b94
|
|
BLAKE2b-256 checksum How to use checksums |
e3e608a77f74da2adb4b89bb178d6927c110acc15b133fc20a1c4190f9d588cc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-pp311-pypy311_pp73-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.5.0-pp311-pypy311_pp73-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.5 MB |
| Tags | Linux glibc 2.28+ x86-64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
a1e19a16ecc91f271662e6cf3267350d7d0742eeb99f32689b119384e8665fdd
|
|
BLAKE2b-256 checksum How to use checksums |
1cf0d07ce141a866c5ab79920b0b8fcfbae110b38869a4a0b4579bff249d193f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-pp311-pypy311_pp73-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.5.0-pp311-pypy311_pp73-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.0 MB |
| Tags | Linux glibc 2.28+ ARM64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
46b187ca67e49089c21514858e78fd9454b199e0f58b0826dfb7b18c9be0c95d
|
|
BLAKE2b-256 checksum How to use checksums |
748e81f58f1a2f15f451464bd32781a8f3de0d742766d873f32e21aa80be37d8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp314-cp314t-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.5.0-cp314-cp314t-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.6 MB |
| Tags | CPython 3.14 CPython 3.14 free-threading Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
167c76971793d5d5b550fac576a53f7f1ce0ca870daddeca90c8fc5255b7744e
|
|
BLAKE2b-256 checksum How to use checksums |
9c05791569c714b4e5665a27254e4a3bf9966c88c8d7f3dea03862e3ee88d5ed
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp314-cp314t-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.5.0-cp314-cp314t-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.0 MB |
| Tags | CPython 3.14 CPython 3.14 free-threading Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
28addfd65f96e6b7cdd69bba606e155207cb0c1a87eeb5a29d7dc5563ba66b90
|
|
BLAKE2b-256 checksum How to use checksums |
f503da34f45e444381c4736fc1f43f08226db2a2b8231e9e7fface1be37613a8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp314-cp314-win_amd64.whl
| Download URL | pydeno-0.5.0-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 18.8 MB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
3e2b290685d914bfa069ca462caa3248386263384ad3a784af22d67f1b290fd9
|
|
BLAKE2b-256 checksum How to use checksums |
41d7a3897f0f30f4e4b9d1bf020d7e542ed0a919e3b96c56e75fccc178e2a762
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp314-cp314-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.5.0-cp314-cp314-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.6 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
f2f491c626ffcc6fce7af89d4758a0e35764fe44401e48b205c4de44dc3a2ea8
|
|
BLAKE2b-256 checksum How to use checksums |
1021944169358047e94bc440e92748786f771b792cf496ed2d99a9e3ded66f69
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp314-cp314-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.5.0-cp314-cp314-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.0 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
ef7ae30ca7b252f5af6a3f41602526a3380394b989acbdf7ba595ae3ed61207c
|
|
BLAKE2b-256 checksum How to use checksums |
e09d6b5a703d2d7e2cb90afd5557a770eb9fe7d8491b15485faa711aa0ecf794
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp314-cp314-macosx_11_0_arm64.whl
| Download URL | pydeno-0.5.0-cp314-cp314-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.5 MB |
| Tags | CPython 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
a7253d0a11287b43bd74f41aa70e60acefe537d57f0a1cd7dbc3c326c175f53d
|
|
BLAKE2b-256 checksum How to use checksums |
9bb37b203261d8f1afb2e731a8a3cf7975b4c1f76488a70353bc949b67c0852e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp313-cp313-win_amd64.whl
| Download URL | pydeno-0.5.0-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 18.8 MB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
654d637d3311f2c5be0a3bc908509ad73bfeeb7b77809c2dd841d3a51545ce3a
|
|
BLAKE2b-256 checksum How to use checksums |
a3d4cdc08ac3d832bd8ffcc6760e3ec9d34db4d4bbfa15982b17aaeec99813a0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp313-cp313-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.5.0-cp313-cp313-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.6 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
c888214003e82bfe04f699f33fc33ae7166548e5862dfcea613c0bfd5c78e38e
|
|
BLAKE2b-256 checksum How to use checksums |
24578c3b1134e90cc5884be954e22d78a621ef1a9fbb220efafacf3f0434a1f0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp313-cp313-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.5.0-cp313-cp313-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.0 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
f480d524e8254fe9ee19b1a747b8cab1cdbda756e01fa8897ba9222a9f58f581
|
|
BLAKE2b-256 checksum How to use checksums |
dad0d5328899fb4d64f824624ae87bcdb644e9b608646c83f744708ff77facdf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | pydeno-0.5.0-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.5 MB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
a8470e86a0f7f0c3b9203abfc06ad979b043f2521e8ff36b890d4ac9cdf77e90
|
|
BLAKE2b-256 checksum How to use checksums |
d4a53bb37057384cf9da8da7d6a3109a06de6d2d6ac69b511b1597d028ee9a0c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp312-cp312-win_amd64.whl
| Download URL | pydeno-0.5.0-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 18.8 MB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
5ce585001af9767461323102a21278b5cb81fbee7c28f8c000c0c41c517a7b2d
|
|
BLAKE2b-256 checksum How to use checksums |
fc06b7e0ac521e301d26d0bc4fc8b7c8d350d8796e737b8c1d6d258ef640c7a2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp312-cp312-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.5.0-cp312-cp312-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.6 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
bea6aa6ef230523b0df075b2ba1fe5080ab8f7647f50cf6c542fe401763f4d83
|
|
BLAKE2b-256 checksum How to use checksums |
ef94b6ca3f329aef8863b46a0794b487abf56ee6c47fb4c9df02254dcc069dd1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp312-cp312-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.5.0-cp312-cp312-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.0 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
e959459886bbecac4cbf88420a6d3eca2ac30a90b3bb9511f7bb815634b7f7b6
|
|
BLAKE2b-256 checksum How to use checksums |
68867823bc25df0e81b893330c199c1ff041e11b825943865583fa483f7e9341
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | pydeno-0.5.0-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.5 MB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
91fb21ff62c071165df00d6326cbc58e7e8805f5e8f89e2525d0524cda59768e
|
|
BLAKE2b-256 checksum How to use checksums |
601ecee230ba8ea8a617885a60293436ff96a3869c239b12c9da912d12f10d6c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp311-cp311-win_amd64.whl
| Download URL | pydeno-0.5.0-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 18.8 MB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
c7696a4f0b0a9ad39faa9e3fd4fdb1df63d0d069ff3e5ee27161bdf9511833a4
|
|
BLAKE2b-256 checksum How to use checksums |
7ff36f4ff3ca5e6b31366bc343bc6fed3d76a50a157a6035dbc7b3756c7bc0c1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp311-cp311-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.5.0-cp311-cp311-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.6 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
905950ca1ad900c70ef549208db36f18b822ea51abd6b80c8151228644810d70
|
|
BLAKE2b-256 checksum How to use checksums |
693b81a9c12295b75d06e1058c093b941667984a703c43b861f8e424f3c02372
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp311-cp311-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.5.0-cp311-cp311-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.0 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
285e24fe0177cab98151272cc66abf130fe75d6e18d2c7d0d9caaa0ad0915ff2
|
|
BLAKE2b-256 checksum How to use checksums |
ea9307df4c0927b60dde0b9194db83933e4a083653cf01885ed93a9b1da98184
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | pydeno-0.5.0-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.5 MB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
9af0e909912afe88227e4346969460475229284c071201b276e53d9548332f45
|
|
BLAKE2b-256 checksum How to use checksums |
f38edb871b7886f0ece3c806dcaba599c104f7cfdd9c3973cc68b04197778102
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp310-cp310-win_amd64.whl
| Download URL | pydeno-0.5.0-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 18.8 MB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
74dd25b4e1882eef86e9bb9b37d4da8a96f59497acf6e117fa278f353e709e2d
|
|
BLAKE2b-256 checksum How to use checksums |
05c5ad8db84540b1e379a140b1264ded2079a50f6b47bd1c9c115cdfb464badc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp310-cp310-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.5.0-cp310-cp310-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.6 MB |
| Tags | CPython 3.10 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
a8608a615758c700ef98d2d76806f65a2f689453caafa8dfa07af0cd22617ca9
|
|
BLAKE2b-256 checksum How to use checksums |
d1b34e068c9e9045827cfe24a26e13437f7e9933693be98687c20a1de4600b89
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency logRelease files / pydeno-0.5.0-cp310-cp310-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.5.0-cp310-cp310-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.0 MB |
| Tags | CPython 3.10 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
8ca0b8df56ed2e88db5e9e8df03d86edb47cfafd3a3df196c79ed712067ce286
|
|
BLAKE2b-256 checksum How to use checksums |
5b39e1dfbc3b32ca725032d9a44b88263ae21517388a2cdffa115fd5e341dab7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 3, 2026.
Transparency log













